CVE-2026-70481
Proof-of-concept exploit for an authorization flaw in Open WebUI that lets low-privileged users edit and delete other members' channel messages via…

Proof-of-concept exploit for an authorization flaw in Open WebUI that lets low-privileged users edit and delete other members' channel messages via…

Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100

演示 Next.js 中的 Middleware 授權繞過漏洞 (CVE-2025-29927) 允許未經授權的用戶存取受保護的資訊。

The code for personally reproducing the corresponding vulnerability

Detection scanner for CVE-2026-48710 - Host-header auth bypass in Starlette/FastAPI

PoC for CVE-2025-29556 creating Security Officer accounts on ExaGrid EX10 backup appliances via a low-privilege API session, enabling privilege…

Demonstrates CVE-2023-27524 Broken Object Level Authorization (BOLA) vulnerability with vulnerable and fixed Flask API implementations for security…

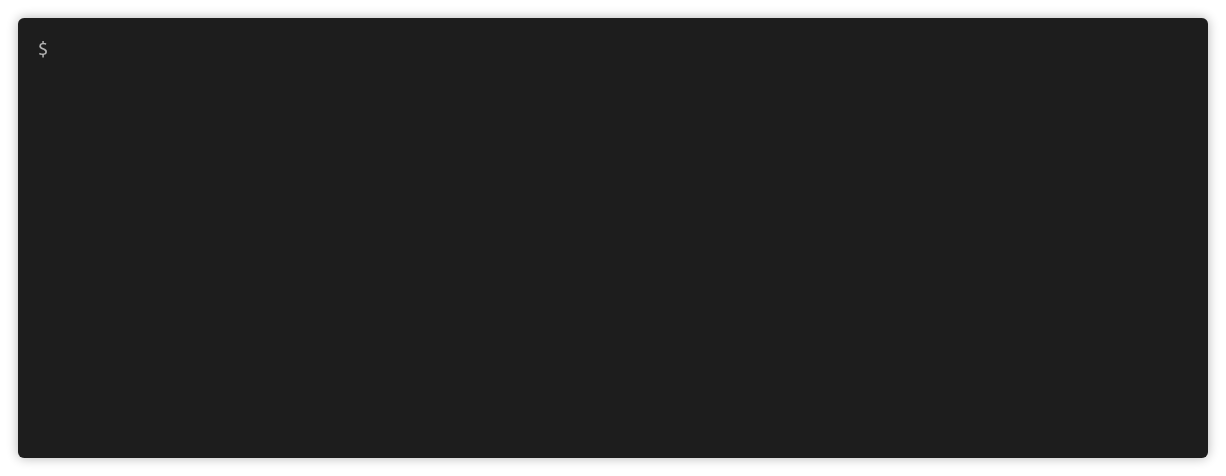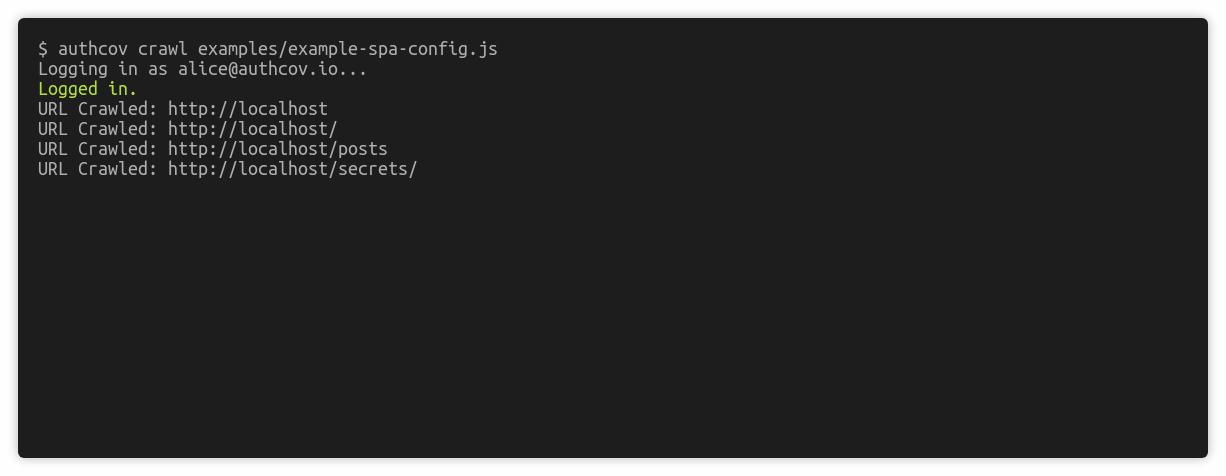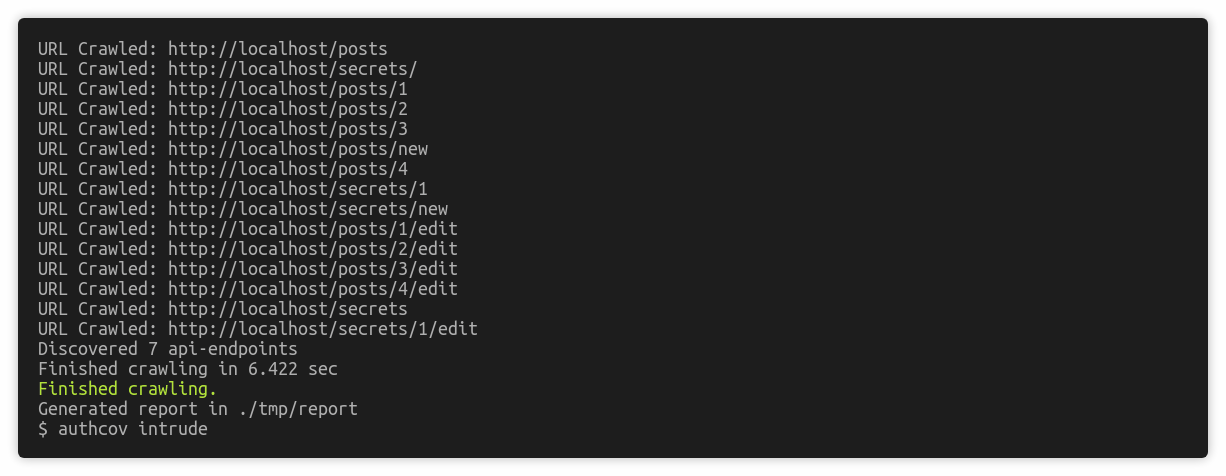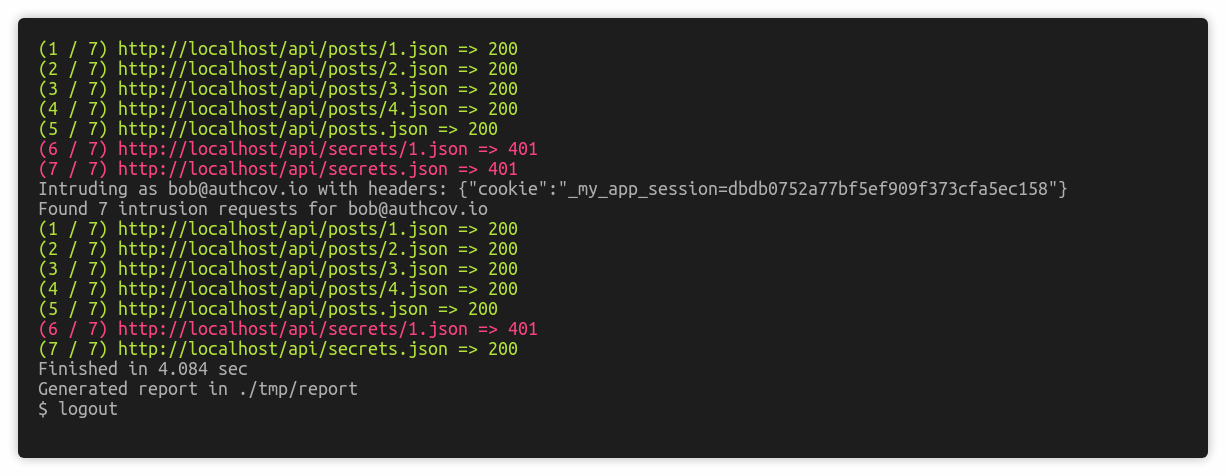
Web app authorisation coverage scanning