
CVE-2024-55591-POC
 exfil0/cve-2024-55591-poc
A comprehensive all-in-one Python-based Proof of Concept script to discover and exploit a critical authentication bypass vulnerability…
authentication-authorizationexploitationnetwork-security+6
12
exfil0/cve-2024-55591-pocA comprehensive all-in-one Python-based Proof of Concept script to discover and exploit a critical authentication bypass vulnerability…
 bishopfox/otto-support
An implementation of a vulnerable MCP server using mcp-go
 oxstussz-eng/kerberos-cve-2026-27912
PoC for CVE-2026-27912 - Windows Kerberos Elevation of Privilege (ResetNightmare). Unauthorized password reset via Kerberos flaw. For security…
 himash/cve-2018-19410-poc
Proof of concept for the vulnerability CVE-2018-19410
 cybertechajju/cve-2026-45156-poc
This repository contains the Proof of Concept (PoC) exploit script for CVE-2026-45156
 teteco/cve-2026-52217-vtex-checkout-crosstenant-idor
The VTEX Checkout Service exposes OrderForm data through the endpoints `/api/checkout/pub/orderForm/{orderFormId}` and `/attachments/*`. These…
 ethan-repo-lab4b6/cve-2022-36537
Python exploit for CVE-2022-36537, an authentication bypass in ZK Framework affecting R1Soft Server Backup Manager, allowing retrieval of web context…
 dersecure/cve-2024-33676
Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…
 az0x7/vulnerability-checklist
Curated collection of web and API vulnerability checklists covering XSS, SQLi, CSRF, IDOR, authentication bypass, file upload, and bug bounty testing…
 freerdp/freerdp
FreeRDP is a free remote desktop protocol library and clients
 kanidm/kanidm
Self-hosted identity management platform providing WebAuthn passkeys, OAuth2/OIDC SSO, SSH key distribution, RADIUS and LDAP integration for modern…
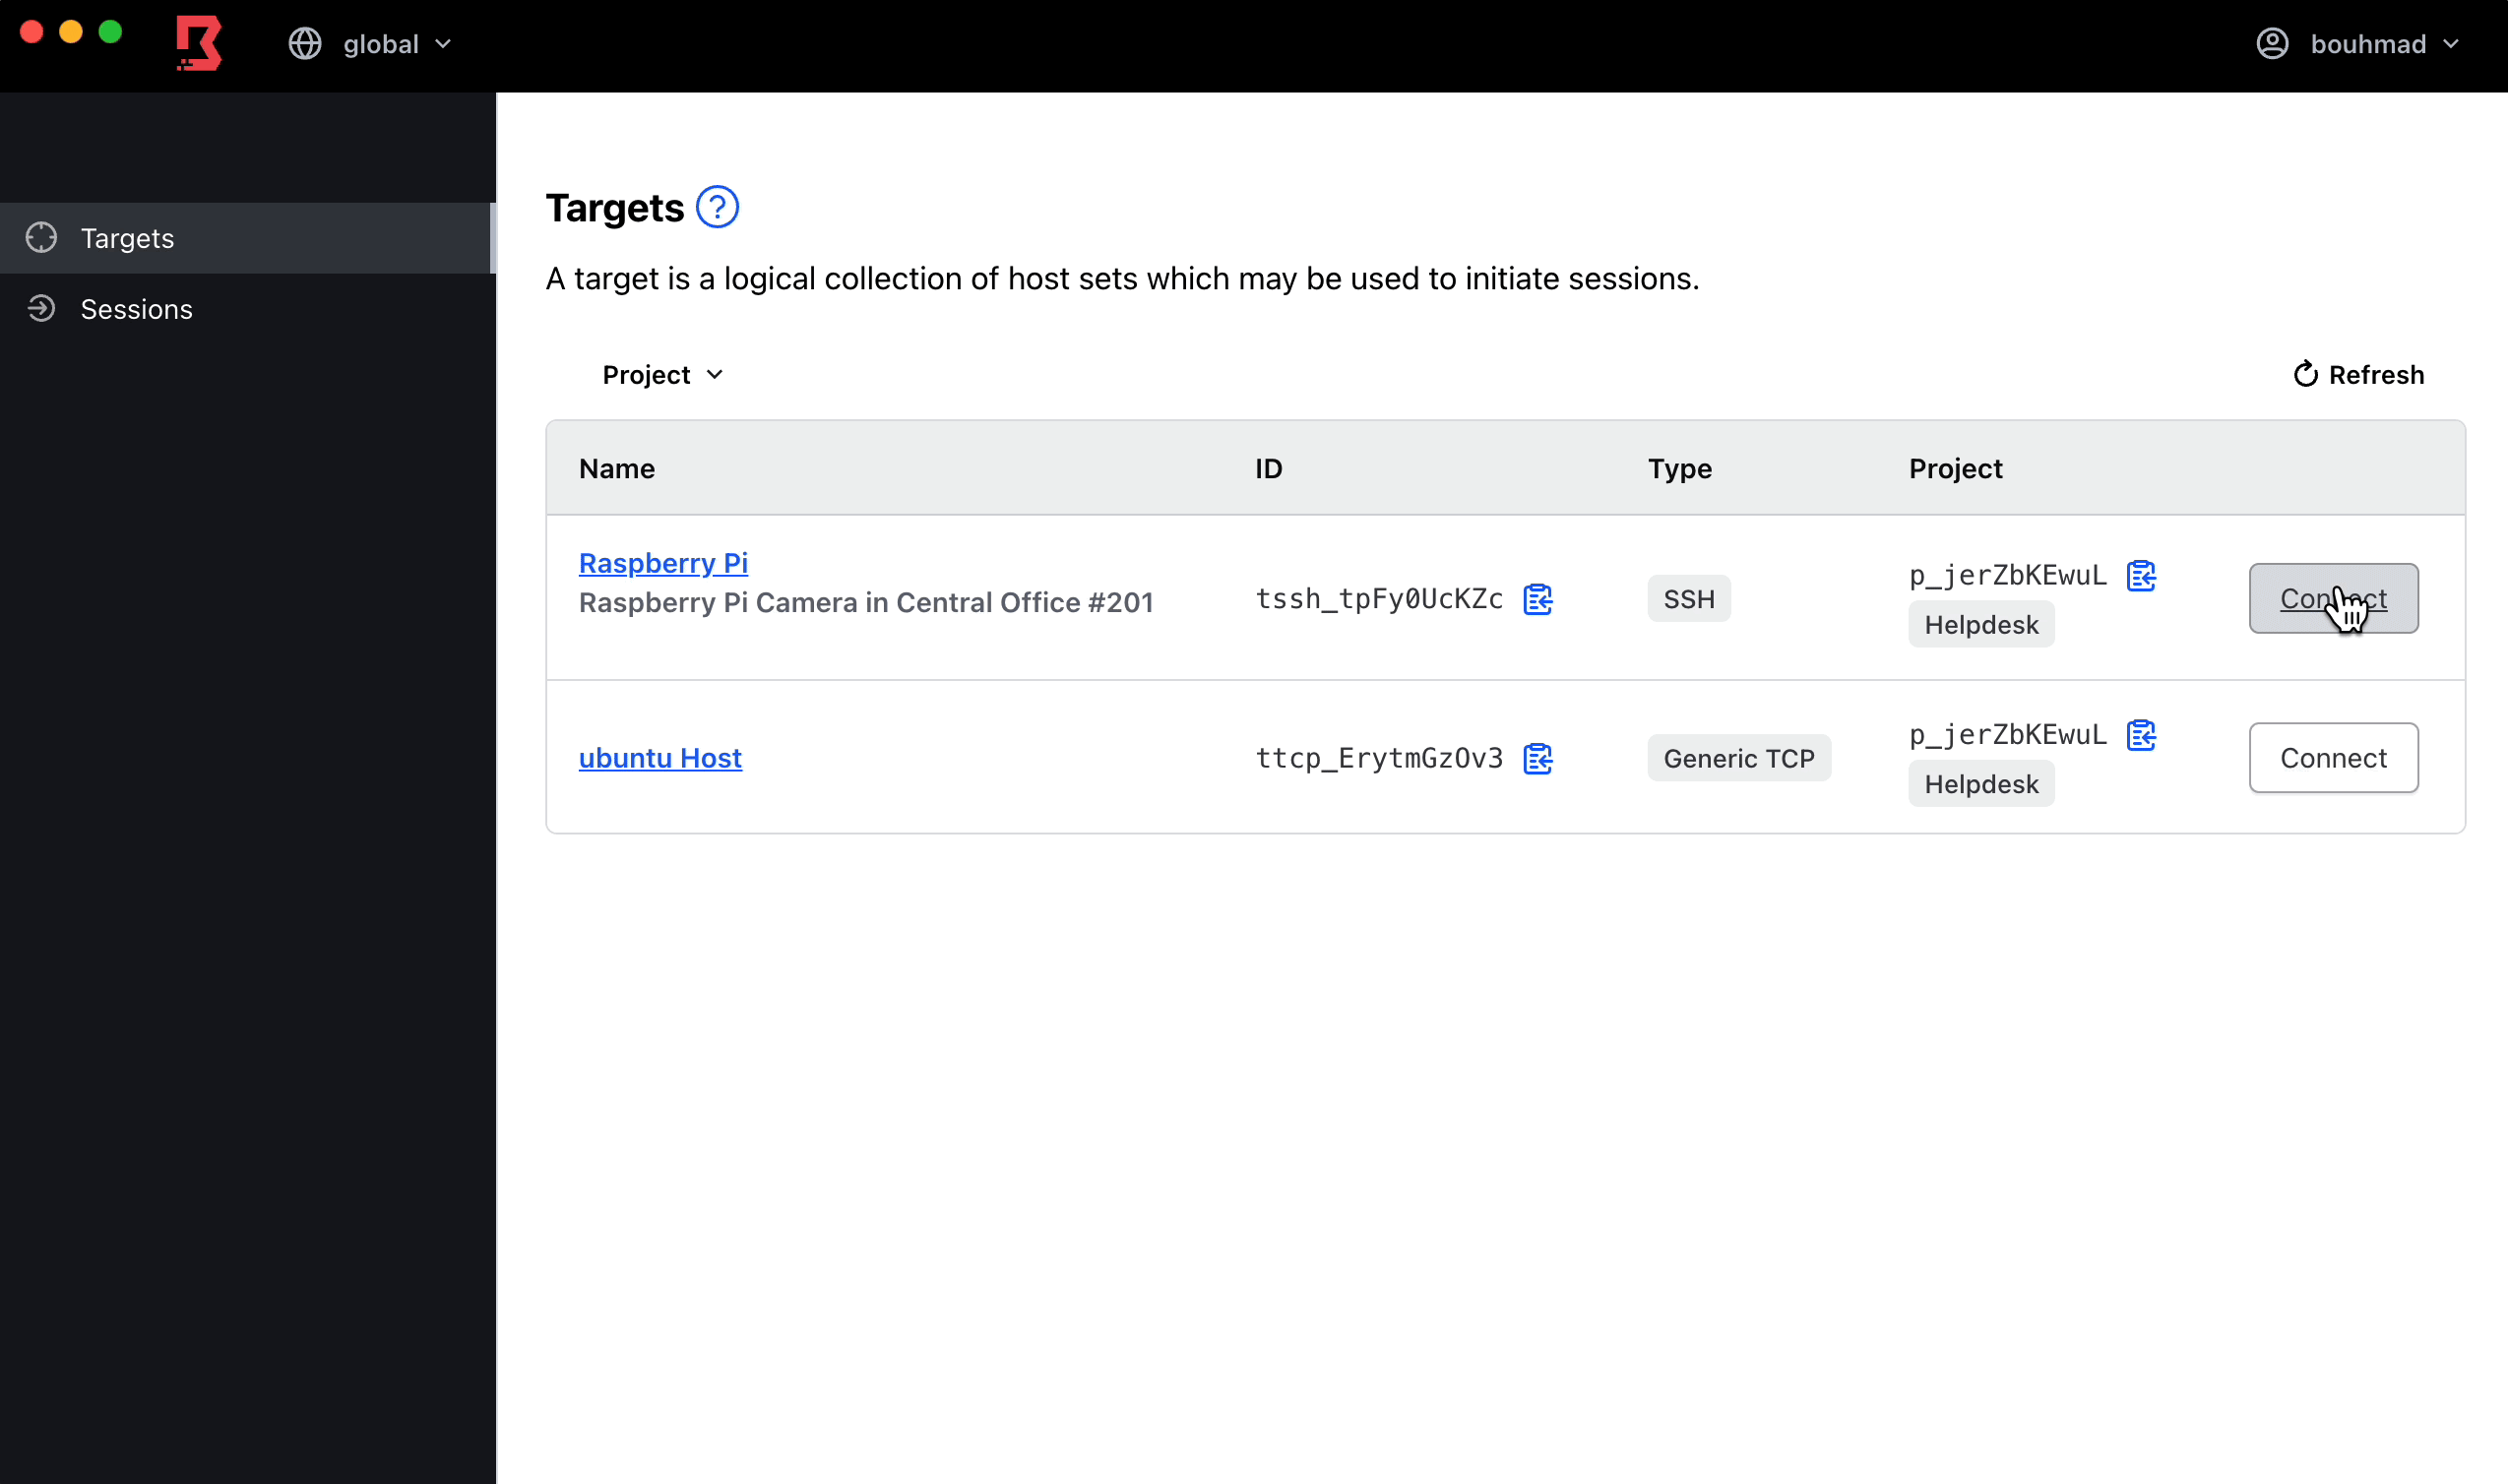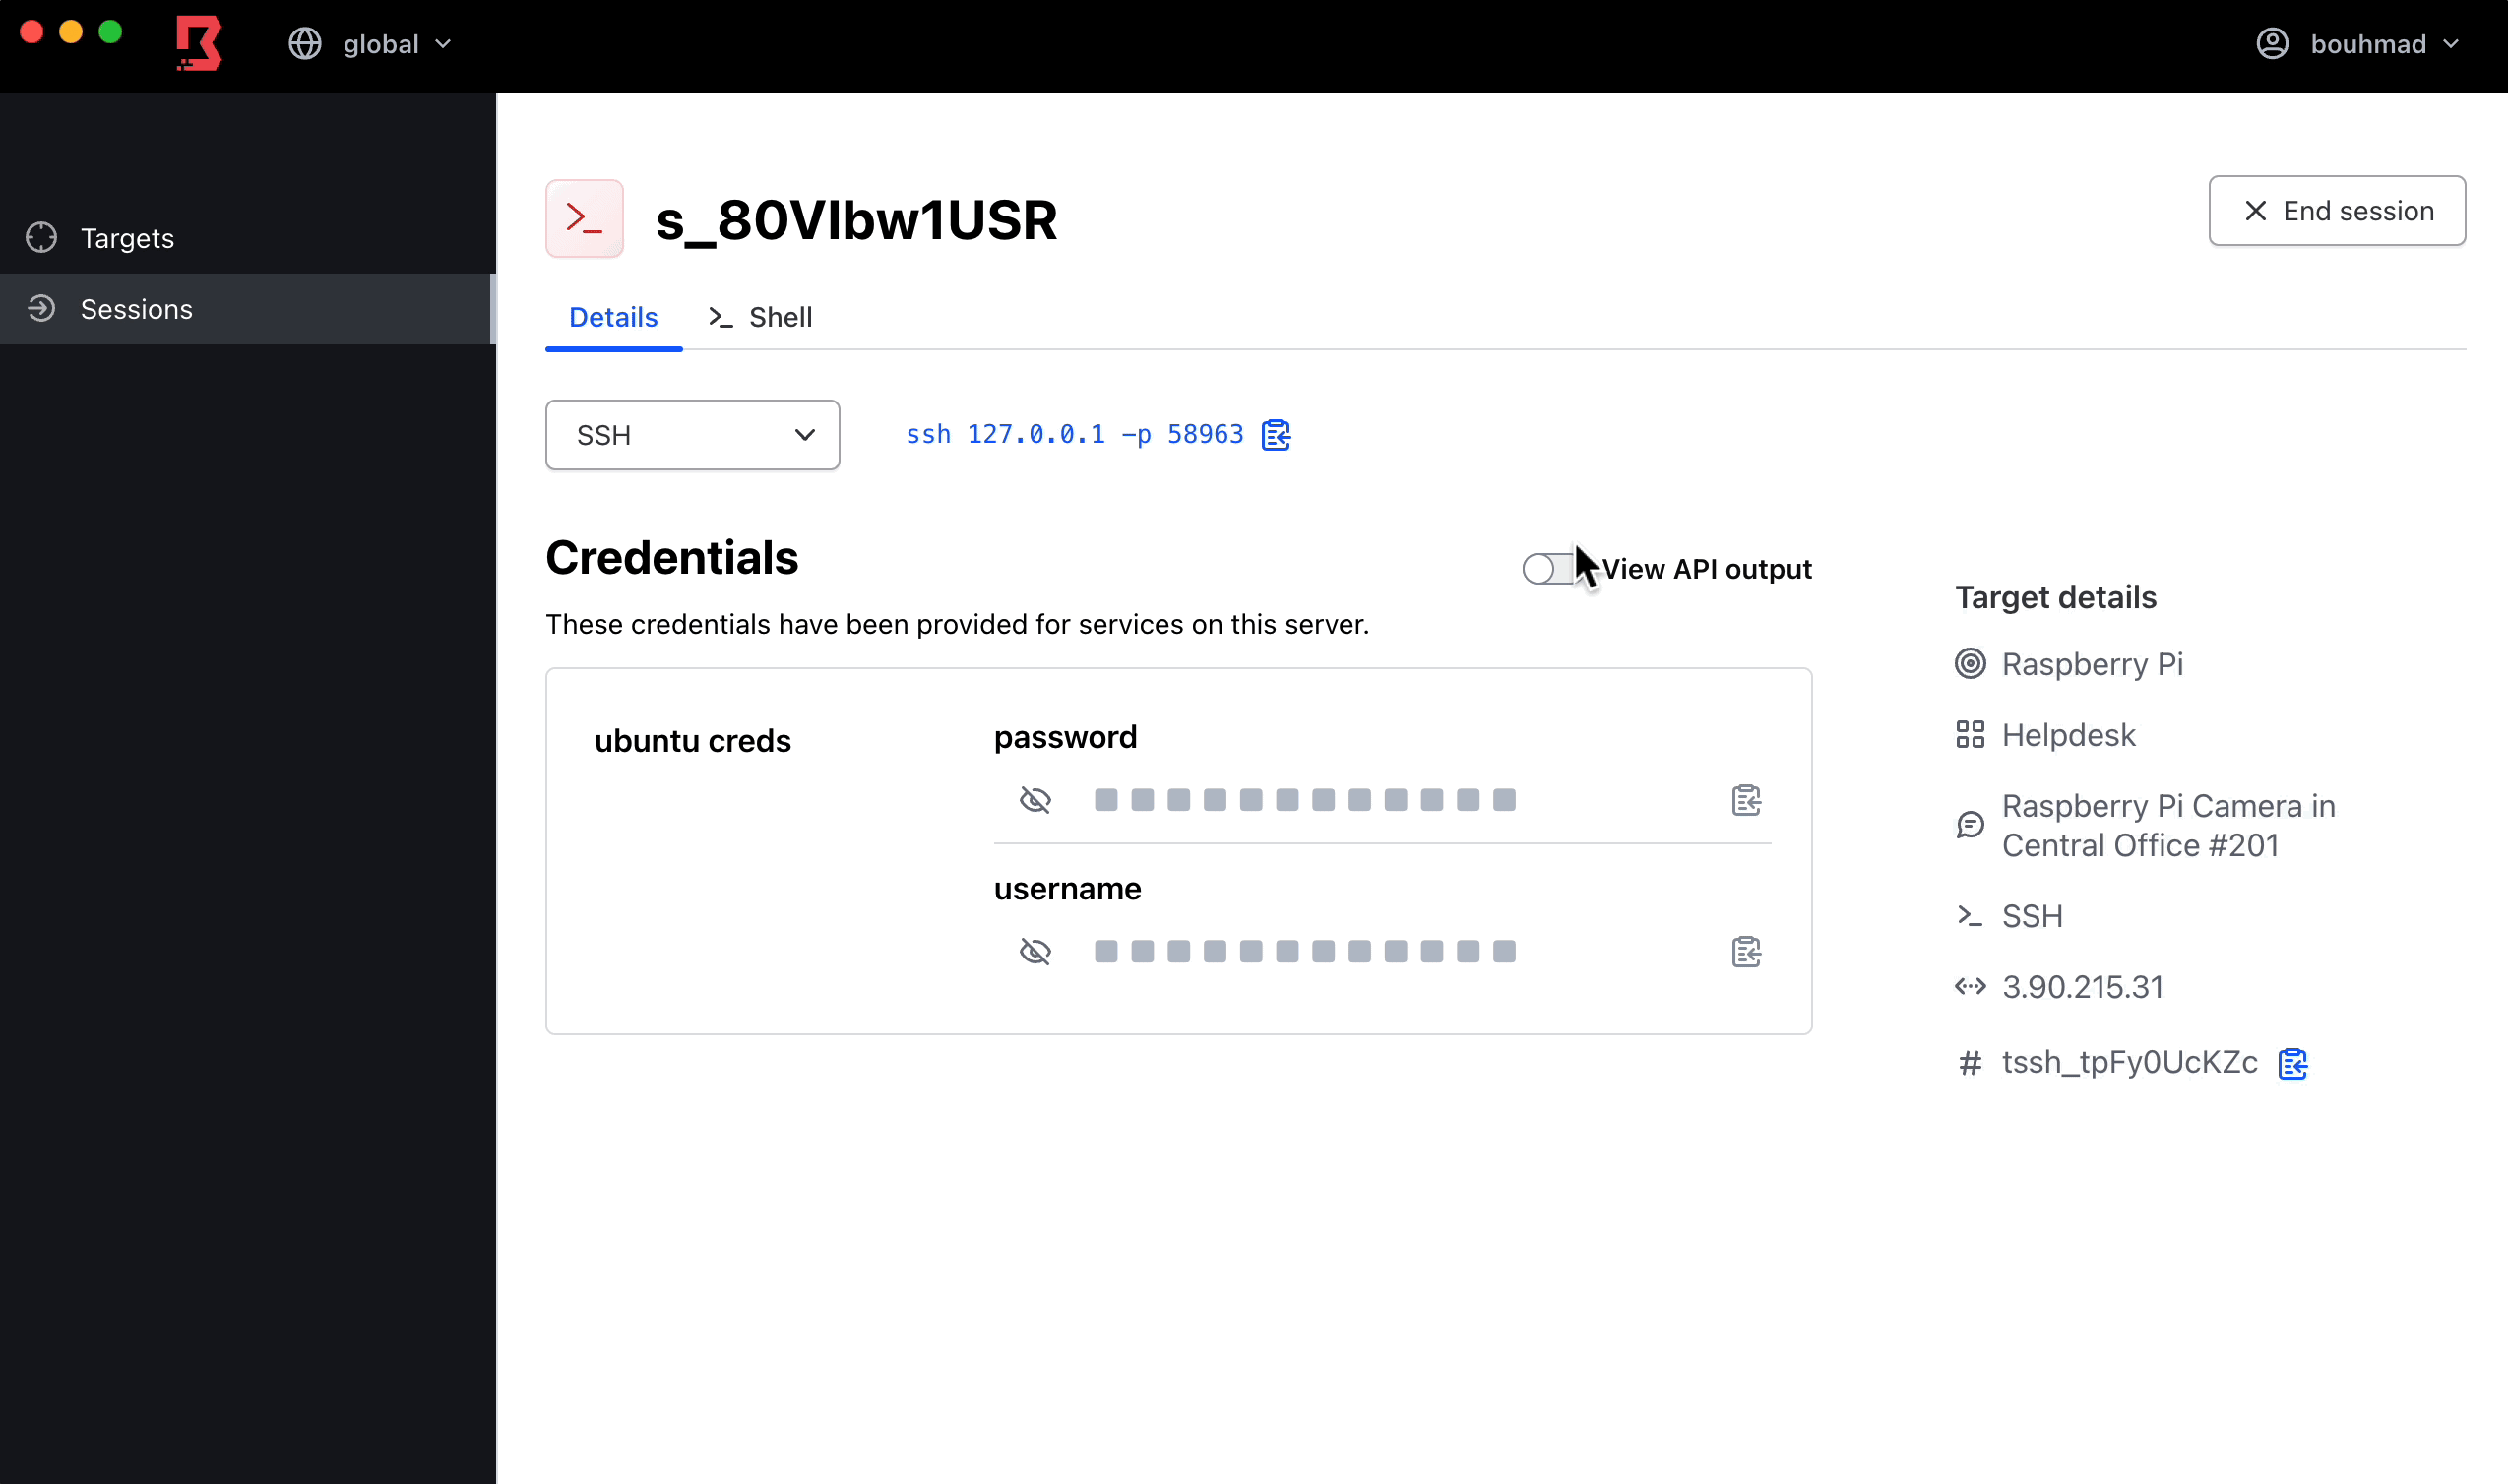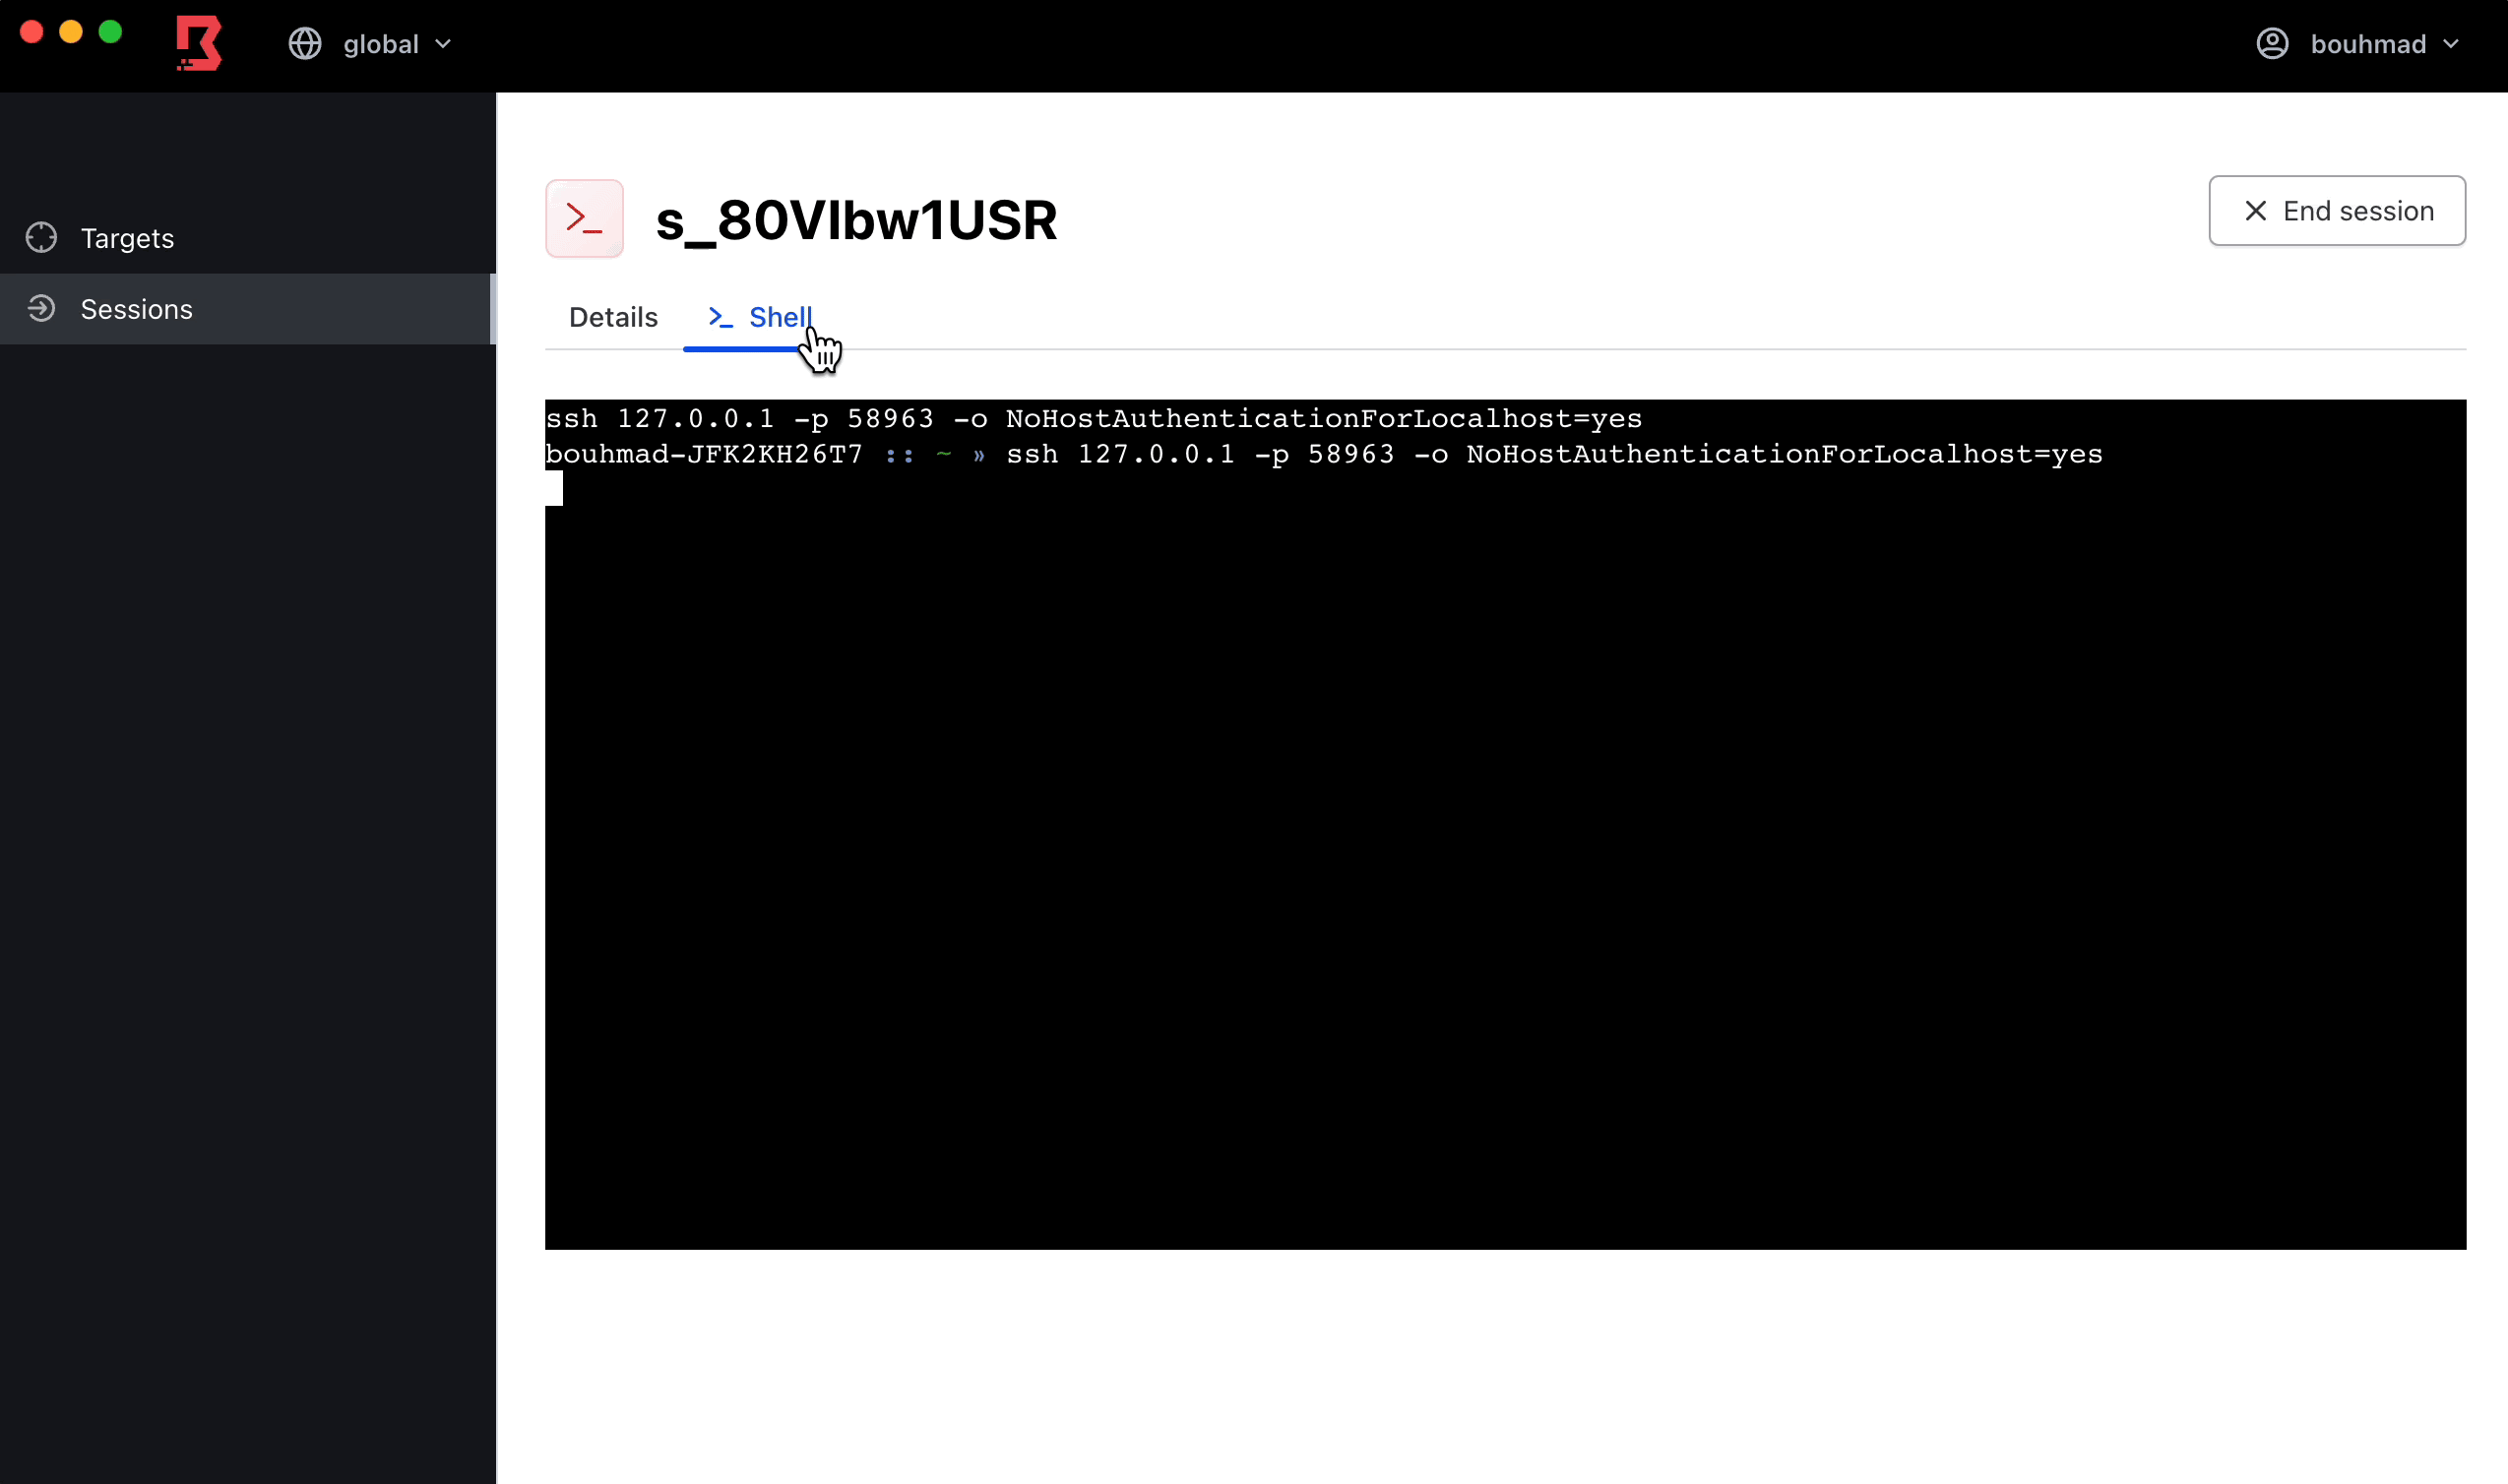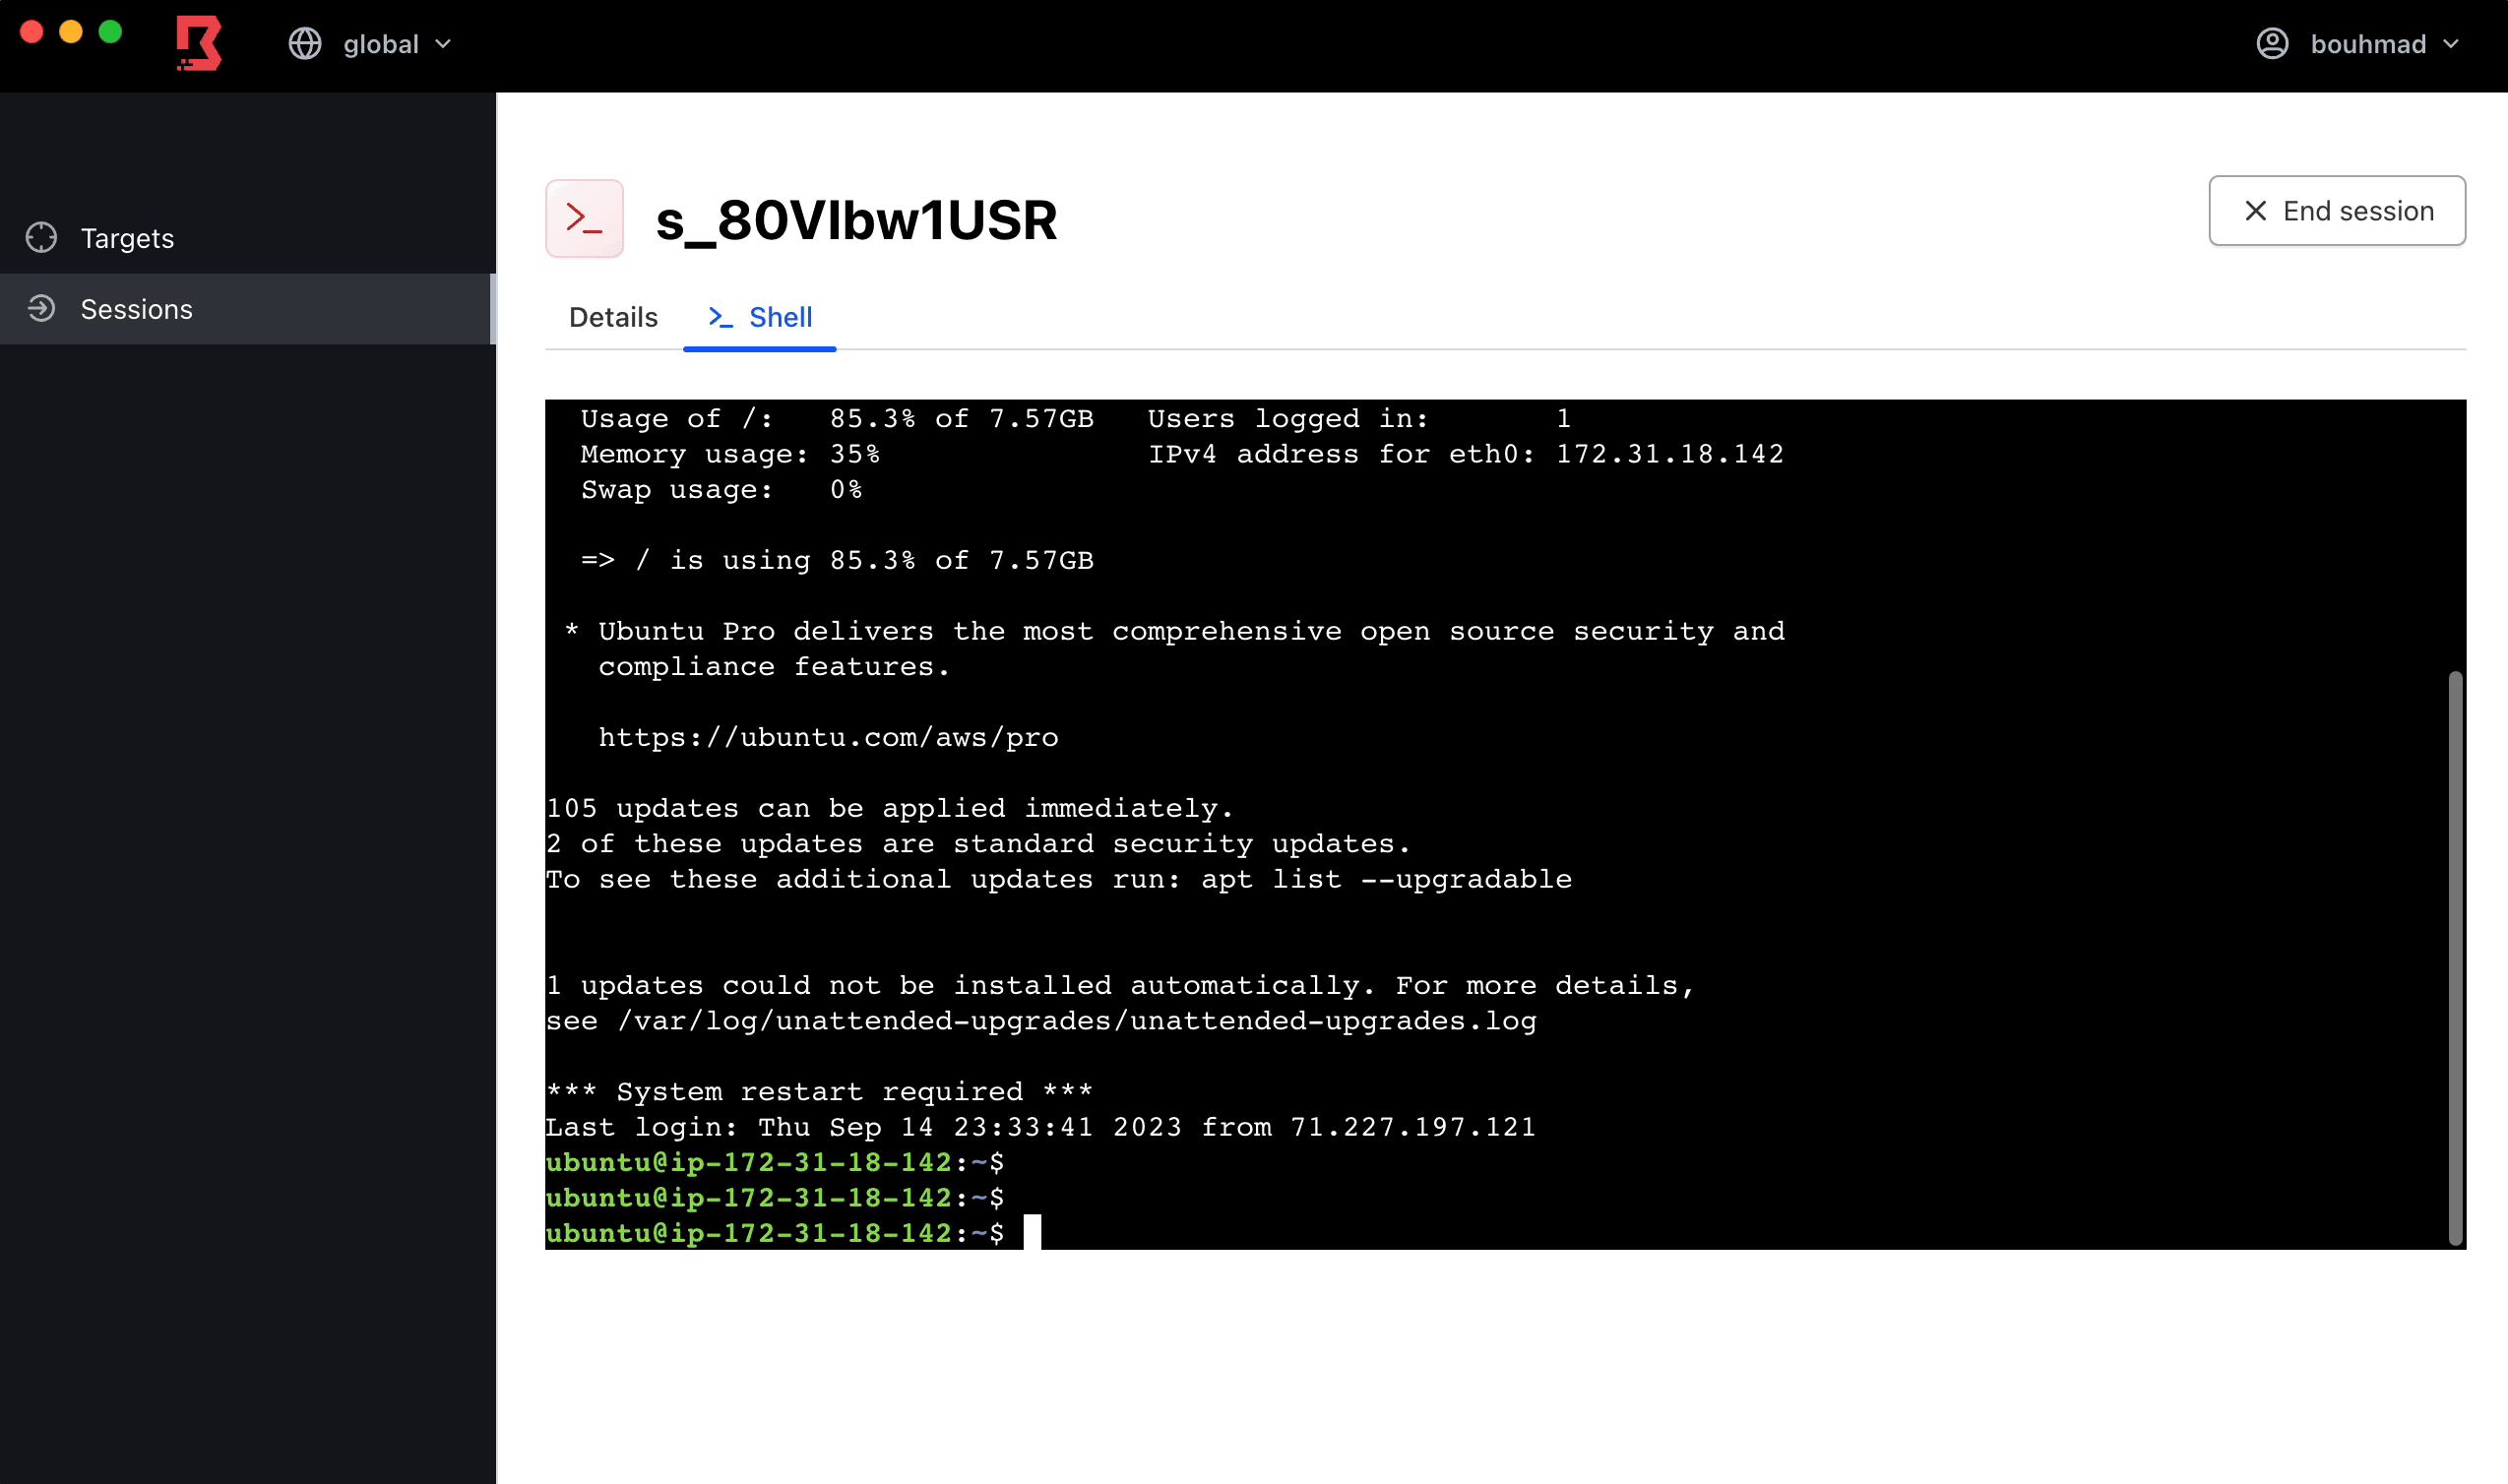 hashicorp/boundary
Boundary enables identity-based access management for dynamic infrastructure.
 spiffe/spire
Workload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…
 freeipa/freeipa
Centralizes identity, authentication, and access control for Linux/UNIX environments using LDAP, Kerberos, PKI, DNS, and Active Directory trust.
 andresriancho/enumerate-iam
Enumerate the permissions associated with AWS credential set
 hzphreak/vminjector
DLL Injection tool to unlock guest VMs
 mcw0/dahuaconsole
Dahua Console, access internal debug console and/or other researched functions in Dahua devices. Feel free to contribute in this project.
 guardicore/vmware_vcenter_cve_2020_3952
Exploit for CVE-2020-3952 in vCenter 6.7