
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
65 results
otto-support preview

otto-support

GitHubbishopfox/otto-support

An implementation of a vulnerable MCP server using mcp-go
api-securityauthentication-authorizationctf+5
196 months ago
darwis-taxii preview

darwis-taxii

GitHubcspf-founder/darwis-taxii

A high-performance TAXII (Trusted Automated eXchange of Indicator Information) server written in Rust.

api-securityauthentication-authorizationioc-management+3
118 months ago
mysql-set-role-leftover preview

mysql-set-role-leftover

GitHubabraxas/mysql-set-role-leftover

MySQL Community Server 26.7.0 - High - SET ROLE ALL EXCEPT leftover FILE - mysqld UID write
authentication-authorizationdatabase-securityexploitation+4
315 days ago
wp-secure-mcp preview

wp-secure-mcp

GitHubles-k/wp-secure-mcp

A WordPress plugin exposing an MCP server over the REST API, with the security model as the point -- closes the CVE-2026-15015 OAuth-bypass shape by…
ai-securityapi-securityauthentication-authorization+5
19 days ago
bitwarden-cipher-create-acl preview

bitwarden-cipher-create-acl

GitHubabraxas/bitwarden-cipher-create-acl

Bitwarden Server v2026.9.2 - High - IDOR - plant decryptable vault items into collections the caller cannot write
authentication-authorizationexploitationlabs-practice+4
215 days ago
ldapserver preview

ldapserver

GitHubprojectdiscovery/ldapserver

Package ldapserver implements LDAP Server
authentication-authorizationencryption-decryption-toolsidentity-access-management+2
72 years ago
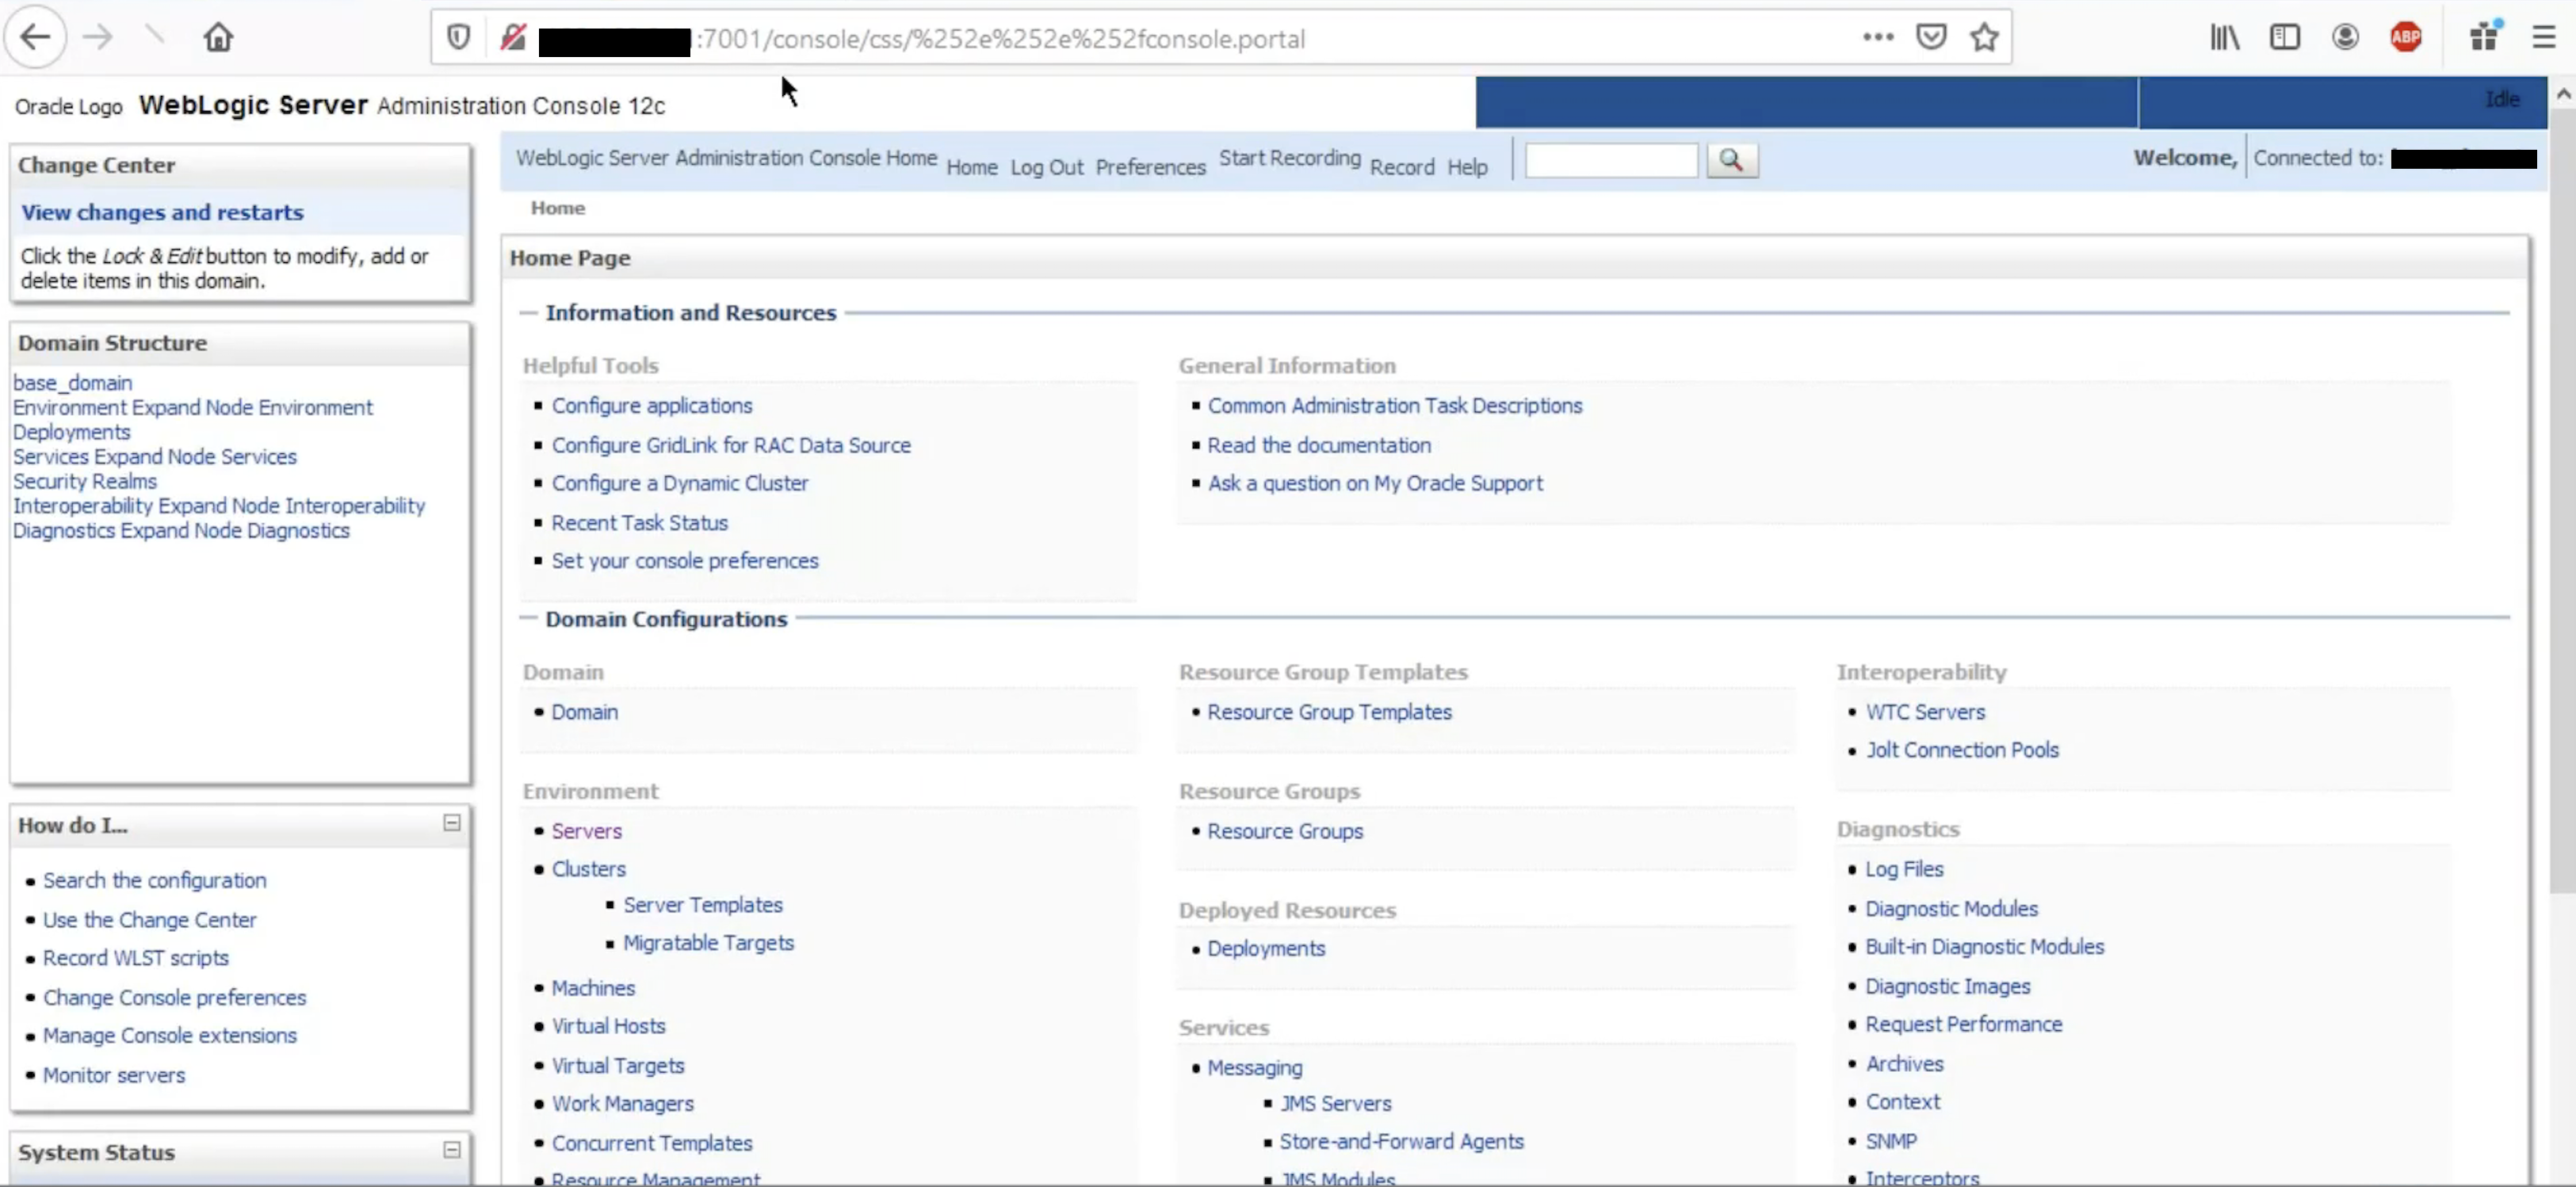
CVE-2020-14882 preview

CVE-2020-14882

GitHubmurataydemir/cve-2020-14882

[CVE-2020-14882] Oracle WebLogic Server Authentication Bypass
authentication-authorizationexploitationpenetration-testing+2
35 years ago
CVE-2022-23131 preview

CVE-2022-23131

GitHubfork-bombed/cve-2022-23131

CVE-2022-23131 Zabbix Server SAML authentication exploit
authentication-authorizationexploitationpenetration-testing+2
52 years ago
CVE-2024-38473 preview

CVE-2024-38473

GitHubabdurahmon3236/cve-2024-38473

Proof-of-concept demonstrating an encoding flaw in Apache HTTP Server mod_proxy that can bypass authentication via crafted encoded URLs.
authentication-authorizationexploitationpenetration-testing+3
32 years ago
POC-CVE-2026-56164-exploit preview

POC-CVE-2026-56164-exploit

GitHubsam00/poc-cve-2026-56164-exploit

CVE-2026-56164 is a critical missing-authentication vulnerability affecting on-premises Microsoft SharePoint Server. It allows unauthenticated,…
authentication-authorizationexploitationinformation-gathering+5
22 months ago
CVE-2026-4444-JWT-Algorithm-Confusion-via-kid-Injection preview

CVE-2026-4444-JWT-Algorithm-Confusion-via-kid-Injection

GitHubgeorge0papasotiriou/cve-2026-4444-jwt-algorithm-confusion-via-kid-injection

POC for CVE-2026-4444 demonstrating JWT algorithm confusion via untrusted kid injection, including vulnerable Node.js server and Python exploit for…
api-securityauthentication-authorizationcryptography+4
2 months ago
CVE-2026-22005-OAuth-2.0-Device-Code-Phishing-Short-Interval- preview

CVE-2026-22005-OAuth-2.0-Device-Code-Phishing-Short-Interval-

GitHubgeorge0papasotiriou/cve-2026-22005-oauth-2.0-device-code-phishing-short-interval-

Proof-of-concept for CVE-2026-22005 showing OAuth 2.0 device code phishing via too-short polling interval, with vulnerable Flask server and exploit…
authentication-authorizationeducationexploitation+4
2 months ago
CVE-2026-3456-OAuth2-PKCE-Race-Condition-Account-Takeover- preview

CVE-2026-3456-OAuth2-PKCE-Race-Condition-Account-Takeover-

GitHubgeorge0papasotiriou/cve-2026-3456-oauth2-pkce-race-condition-account-takeover-

Python PoC for CVE-2026-3456 demonstrating OAuth2 PKCE race-condition account takeover, with a vulnerable auth server and concurrent code-verifier…
api-securityauthentication-authorizationexploitation+3
2 months ago
CVE-2025-32433-PoC-Analysis preview

CVE-2025-32433-PoC-Analysis

GitHubliam-worsley/cve-2025-32433-poc-analysis

This is an analysis for CVE-2025-32433 (Erlang OTP SSH Vulnerability). I did not write any of the code, I only wrote comments describing what the…
authentication-authorizationeducationexploitation+4
2 months ago
CVE-2024-27198 preview

CVE-2024-27198

GitHubgeniuszly/cve-2024-27198

is a PoC tool that targets a vulnerability in the TeamCity server (CVE-2024-27198)
authentication-authorizationexploitationpenetration-testing+3
32 years ago
latch-plugin-openVPN-AS preview

latch-plugin-openVPN-AS

GitHubelevenpaths/latch-plugin-openvpn-as

Latch plugin for OpenVPN Access Server enabling two-factor authentication (2FA) to secure VPN connections with time-based one-time passwords (TOTP).
authenticationauthentication-authorizationcloud-security+2
112 years ago
CVE-2025-26788 preview

CVE-2025-26788

GitHubeqstlab/cve-2025-26788

Strongkey FIDO Server Authorization Bypass
authentication-authorizationexploitationpenetration-testing+2
11 year ago
CVE-2022-36537 preview

CVE-2022-36537

GitHubethan-repo-lab4b6/cve-2022-36537

Python exploit for CVE-2022-36537, an authentication bypass in ZK Framework affecting R1Soft Server Backup Manager, allowing retrieval of web context…

authentication-authorizationexploitationinformation-gathering+3
1 year ago
Previous1234Next