
Kangaroo
 monkeysec-sys/kangaroo
Authentication bypass exploit for CVE-2026-32746 targeting legacy Telnet servers, with defensive guidance and Go-based implementation for authorized…
authentication-authorizationeducationexploitation+3
2
monkeysec-sys/kangarooAuthentication bypass exploit for CVE-2026-32746 targeting legacy Telnet servers, with defensive guidance and Go-based implementation for authorized…
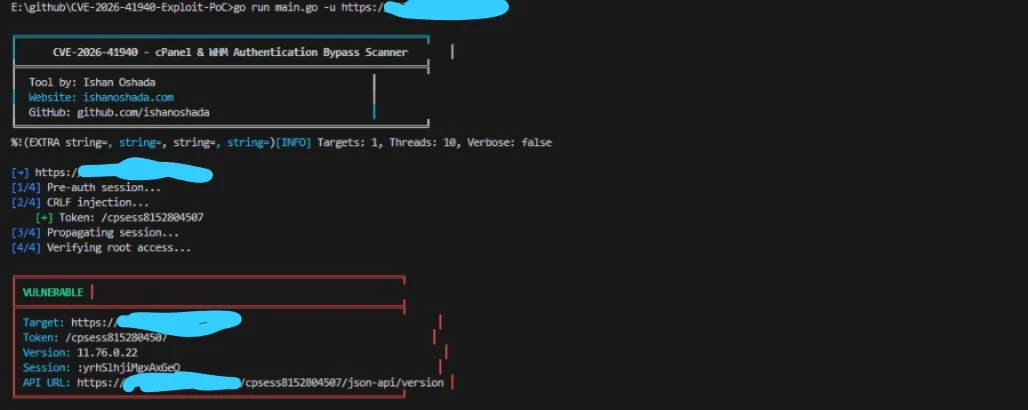 ishanoshada/cve-2026-41940-exploit-poc
Exploit PoC for CVE-2026-41940, a cPanel & WHM authentication bypass via CRLF injection. Includes mass scanning, post-exploitation actions, and an…
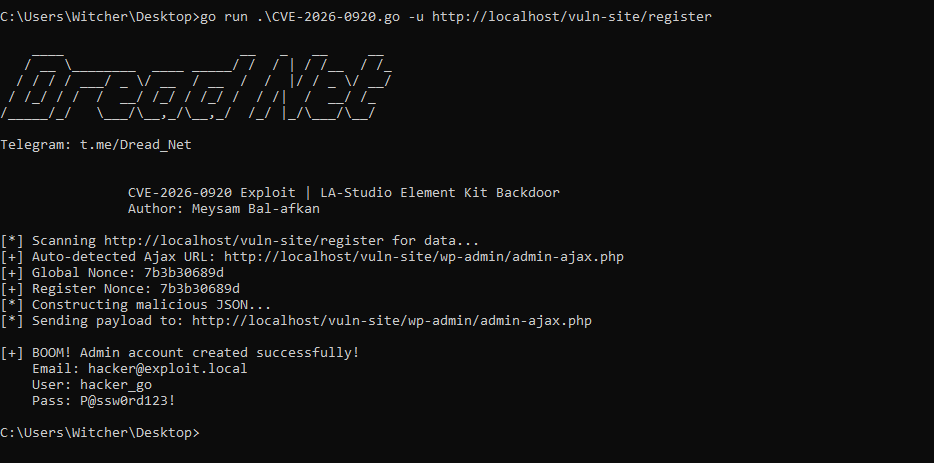 galaxy-sc/cve-2026-0920-wordpress-la-studio-exploit
Proof-of-concept exploit for CVE-2026-0920 in LA-Studio Element Kit, enabling unauthenticated privilege escalation to administrator via crafted AJAX…
 sachitrafa/yourmemory
Agentic AI memory with Ebbinghaus forgetting curve decay. +16pp better recall than Mem0 on LoCoMo.
 6lj/cve-2025-3639
login bypass vulnerability in Liferay Portal (versions 7.3.0–7.4.3.132) and Liferay DXP (various versions from 2024.Q1 to 2025.Q1.6)
 rohitberiwala/cve-2026-28372-telnetd-privilege-escalation
This Proof‑of‑Concept demonstrates a **Local Privilege Escalation** vulnerability in GNU inetutils `telnetd`. `telnetd` improperly passes…
 jumpserver/jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
 vicanso/pingap
A reverse proxy like nginx, built on pingora, simple and efficient.
 mrash/fwknop
Single Packet Authorization > Port Knocking
 umputun/reproxy
Lightweight edge HTTP(S) server and reverse proxy with automatic SSL, Docker/Consul discovery, per-route authentication, rate limiting, and…
 facebookincubator/bpfjailer
eBPF LSM based Mandatory Access Control and jailer
 ymsniper/noeyes
Secure terminal chat. E2E encrypted, zero-metadata blind-forwarder server. PyNaCl XSalsa20-Poly1305 + Ed25519 + forward secrecy. Cross-platform…
 zakipedio/bridgehead
Native C++ access to Active Directory over ADWS, no .NET, no WCF, no HTTP stack.
 eduardolat/authkeysync
🔐 Lightweight CLI utility designed to synchronize SSH public keys from remote URLs into local authorized_keys files
 fusionauth/fusionauth-samlv2
SAML v2.0 bindings in Java using JAXB
 opfour/op4
Terminal-based encrypted messenger with post-quantum cryptography, Double Ratchet protocol, and Tor anonymity. Features duress passphrase, deniable…
 ignis-sec/cve-2019-10008
ManageEngine Service Desk Plus 10.0 Privilaged account Hijacking