CVE-2026-23004-Automotive-UDS-Authentication-Bypass-via-Replay-Attack

Proof-of-concept exploit demonstrating UDS authentication bypass via challenge-response replay on automotive ECUs, with Python CAN-UDS simulator.

Proof-of-concept exploit demonstrating UDS authentication bypass via challenge-response replay on automotive ECUs, with Python CAN-UDS simulator.

Step-by-step demonstration of CVE-2022-22978 authorization bypass in Spring Security's RegexRequestMatcher, with vulnerable app setup, payload…

Proof-of-concept exploit for CVE-2020-1764 authentication bypass in Kiali 0.4.0–1.15.0, enabling unauthorized API access via crafted JWT tokens.

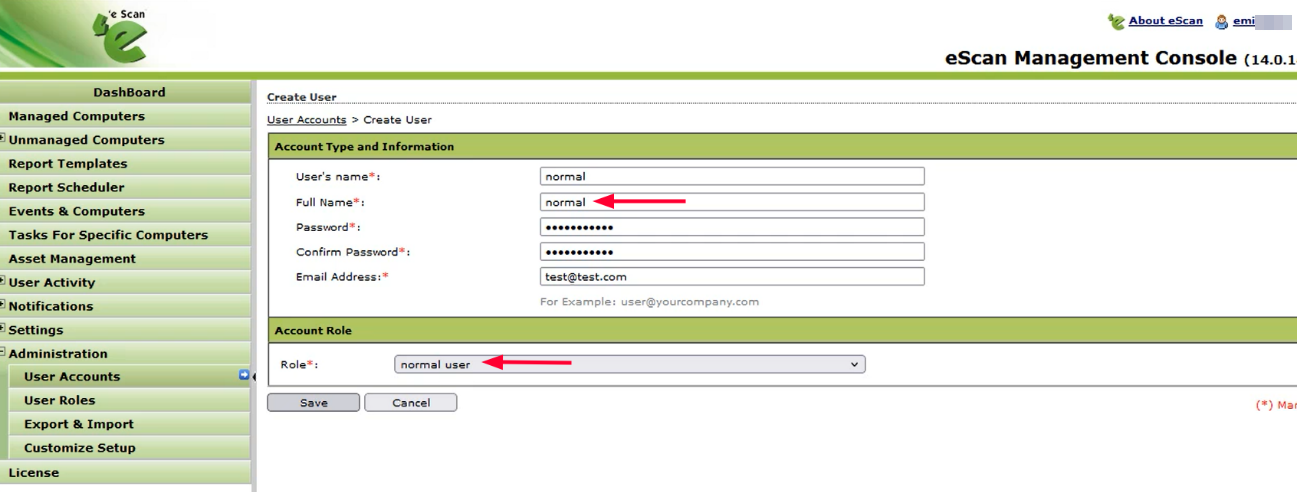
eScan Management Console version 14.0.1400.2281 contains privilege escalation via `GetUserCurrentPwd` function lets attackers retrieve any user's…

TeamCity CVE-2023-42793 exploit written in Rust

A security-hardened fork of the abandoned "PostGallery" WordPress plugin. Fixes critical Arbitrary File Upload (CVE-2025-13543) and Guest Access…

A secure, zero-trust database management tool for WordPress. Fixes critical SSRF vulnerabilities (CVE-2021-21311) by enforcing local connections only.

Unauthenticated Remote Code Execution through authentication bypass and command injection in Cacti < 1.2.23 and < 1.3.0

Proof-of-concept demonstrating authorization bypass in Spring Security's RegexRequestMatcher (CVE-2022-22978) using CRLF injection, with analysis and…

https://medium.com/@mnqazi/cve-2023-4696-account-takeover-due-to-improper-handling-of-jwt-tokens-in-memos-v0-13-2-13104e1412f3

Repository for CVE-2023-4800 vulnerability.

Infisical is the open-source platform for secrets, certificates, and privileged access management.

Provides open-source SSO and identity provider functionality with SAML, OAuth2/OIDC, LDAP, and RADIUS support for centralized authentication,…

WireGuard-based zero-trust access platform providing secure, peer-to-peer remote access with granular policy controls, SSO authentication, and audit…

Exploit for Keycloak CVE-2026-18963 enabling unauthenticated account takeover via reset-credentials bypass. Includes safe detection, non-destructive…

POC of CVE-2022-36537

CVE-2026-27771 - Gitea/Forgejo Container Registry Auth Bypass Exploit PoC - Pull private container images without authentication

PoC exploit for CVE-2026-2991 — authentication bypass in KiviCare WordPress plugin (≤4.1.2) allowing unauthenticated patient account takeover and…