
autogpt-CVE-2026-30950-poc
 zeropathai/autogpt-cve-2026-30950-poc
POC for CVE-2026-30950 which allows session hijacking in AutoGpt
authentication-authorizationexploitationpenetration-testing+3
zeropathai/autogpt-cve-2026-30950-pocPOC for CVE-2026-30950 which allows session hijacking in AutoGpt
 nxploited/cve-2025-4796
Eventin <= 4.0.34 - Authenticated (Contributor+) Privilege Escalation via User Email Change/Account Takeover
 randomrobbiebf/freemius-exploit
Freemius Library < 2.2.4 - Subscriber+ Arbitrary Option Update
 squ1dw3rm/cve-2023-52268
Authentication Bypass for FreeScout End-User Portal
 mnqazi/cve-2023-4696
https://medium.com/@mnqazi/cve-2023-4696-account-takeover-due-to-improper-handling-of-jwt-tokens-in-memos-v0-13-2-13104e1412f3
 focused.hunts/the.vault
Privacy-first password manager with local storage and bring-your-own-cloud sync across Google Drive, Microsoft OneDrive, and Dropbox. Your…
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 learner202649/cve-2026-47101-poc
The code for personally reproducing the corresponding vulnerability
 0xsu3ks/cve-2025-29556
PoC for CVE-2025-29556 creating Security Officer accounts on ExaGrid EX10 backup appliances via a low-privilege API session, enabling privilege…
 nccgroup/autorepeater
Automated HTTP Request Repeating With Burp Suite
 qianlijaingshan/milvus-auth-audit
Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100
 foxer131/cve-2026-70481
Proof-of-concept exploit for an authorization flaw in Open WebUI that lets low-privileged users edit and delete other members' channel messages via…
 lstudlo/nextjs-cve-demo
演示 Next.js 中的 Middleware 授權繞過漏洞 (CVE-2025-29927) 允許未經授權的用戶存取受保護的資訊。
 rachidafaf/bola-cve-2023-27524
Demonstrates CVE-2023-27524 Broken Object Level Authorization (BOLA) vulnerability with vulnerable and fixed Flask API implementations for security…
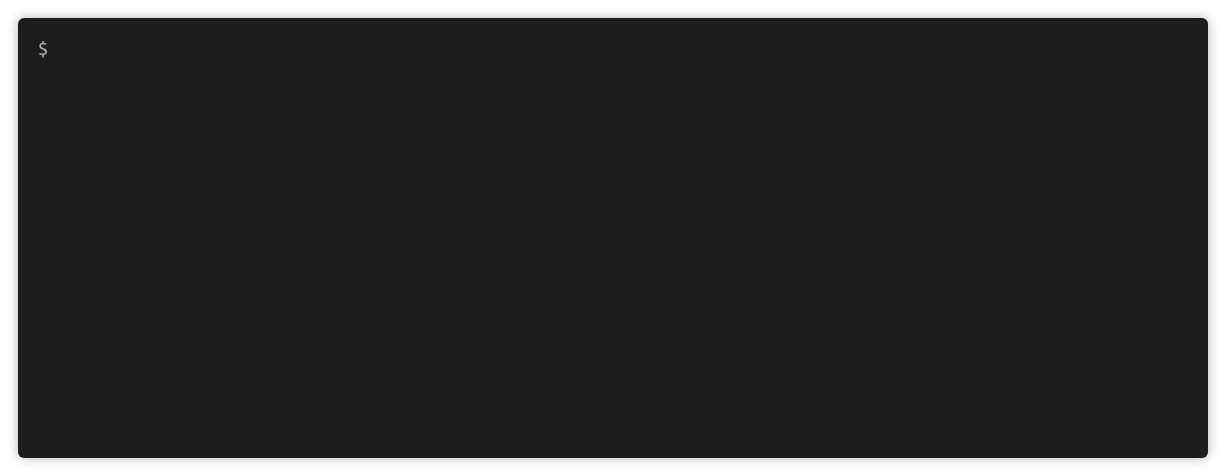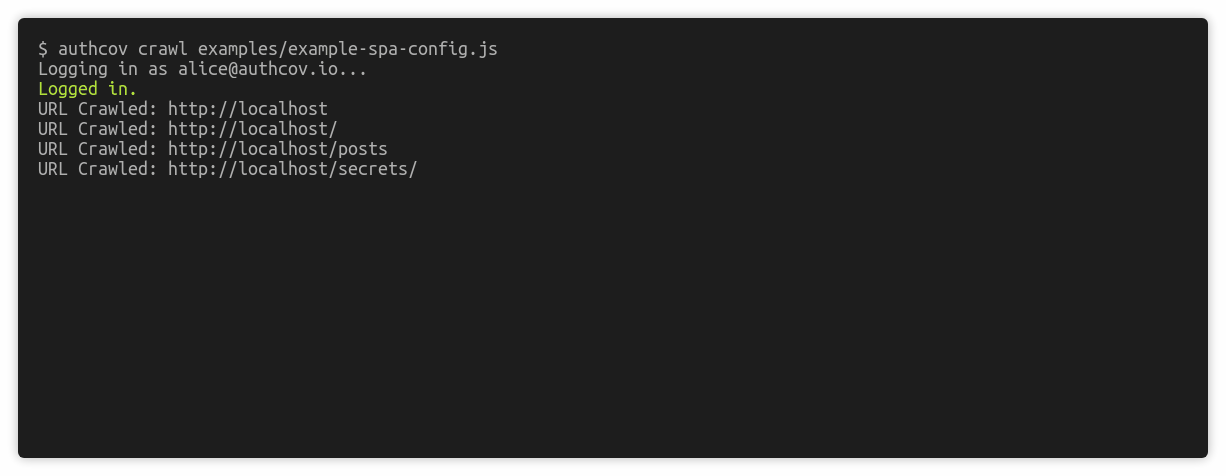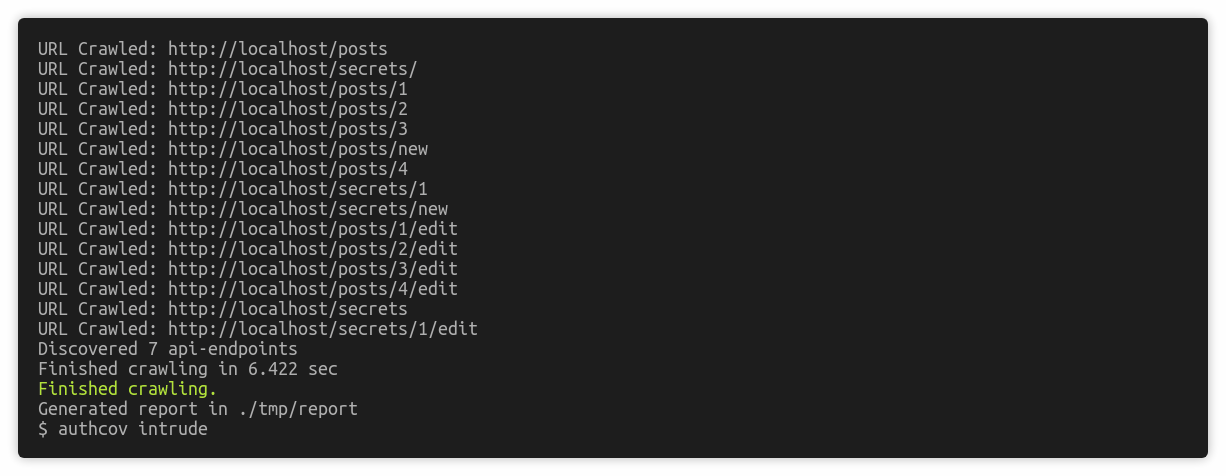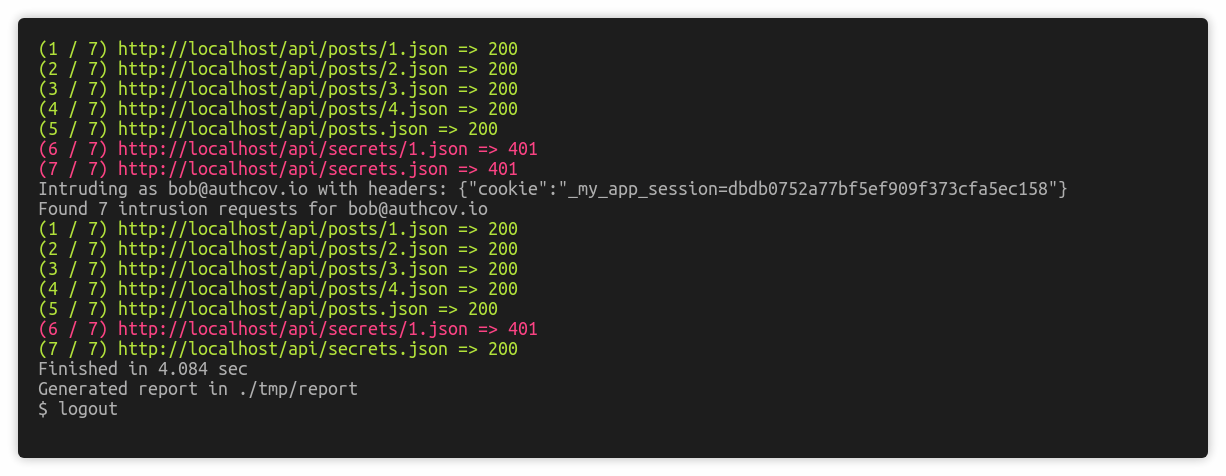 authcov/authcov
Web app authorisation coverage scanning
 0xcyp1337/cve-2026-82329
Mass exploit for CVE-2026-82329, an unauthenticated authentication bypass in JFrog Artifactory. Supports single-target and batch scanning with…
 nccgroup/sshession
The SSH Multiplex Backdoor Tool
 geniuszly/cve-2024-27198
is a PoC tool that targets a vulnerability in the TeamCity server (CVE-2024-27198)