
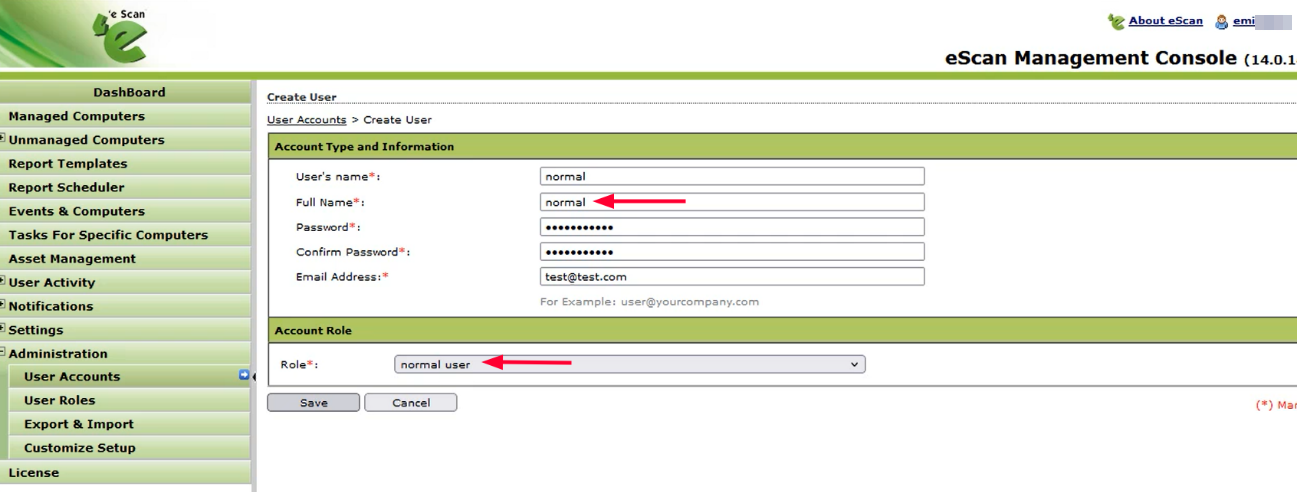
CVE-2023-33730
 sahiloj/cve-2023-33730
eScan Management Console version 14.0.1400.2281 contains privilege escalation via `GetUserCurrentPwd` function lets attackers retrieve any user's…
authentication-authorizationeducationexploitation+8
2
sahiloj/cve-2023-33730eScan Management Console version 14.0.1400.2281 contains privilege escalation via `GetUserCurrentPwd` function lets attackers retrieve any user's…
 sardine-web/automated-scanner-cve-2026-41940
Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection
 cybertechajju/cve-2026-45156-poc
This repository contains the Proof of Concept (PoC) exploit script for CVE-2026-45156
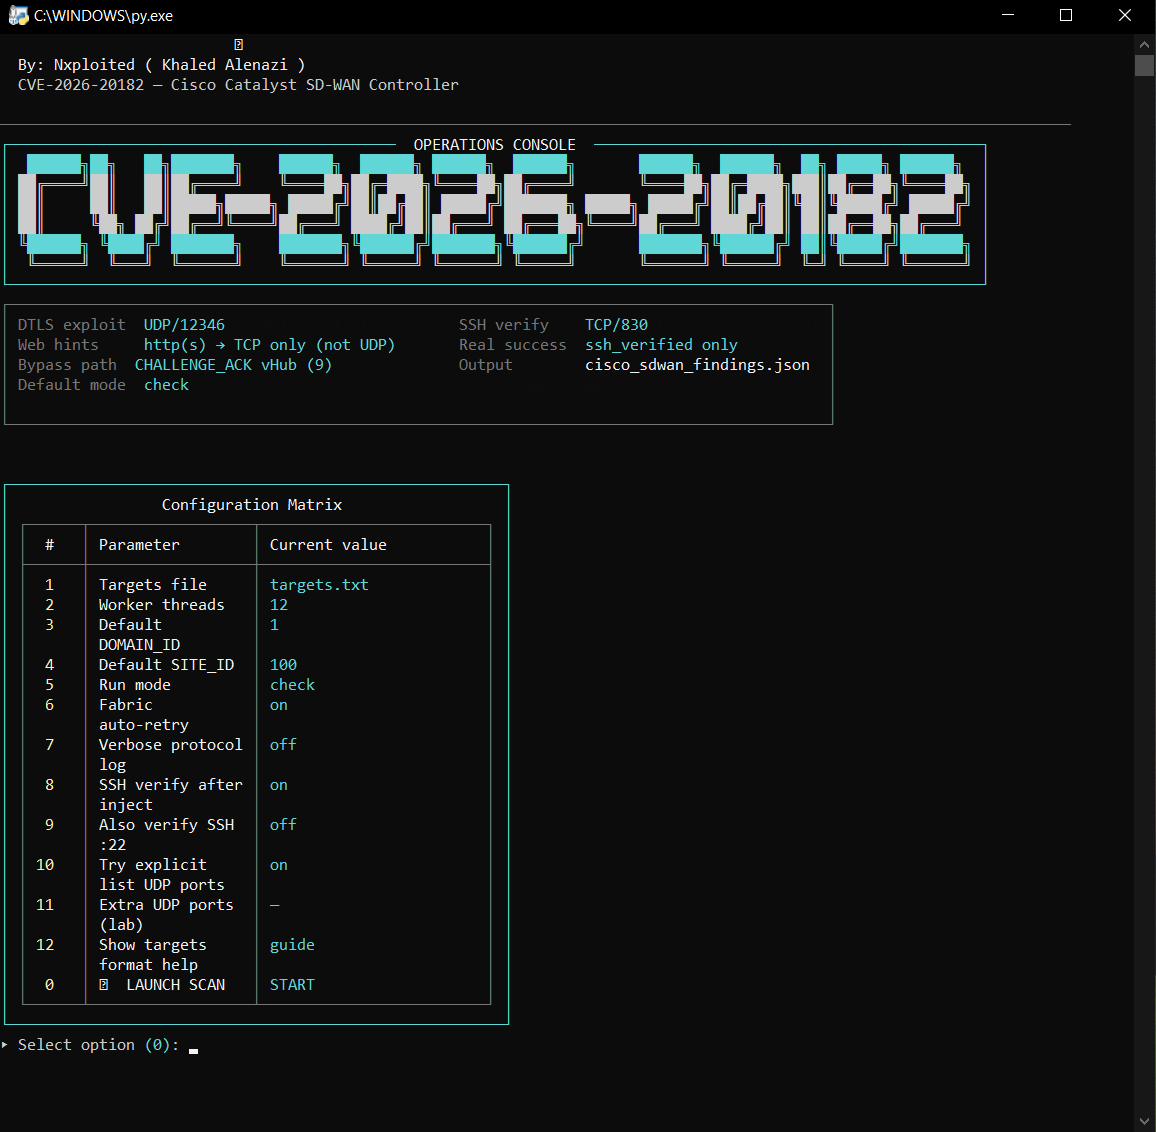 nxploited/cve-2026-20182
Cisco Catalyst SD-WAN Peering Authentication Bypass
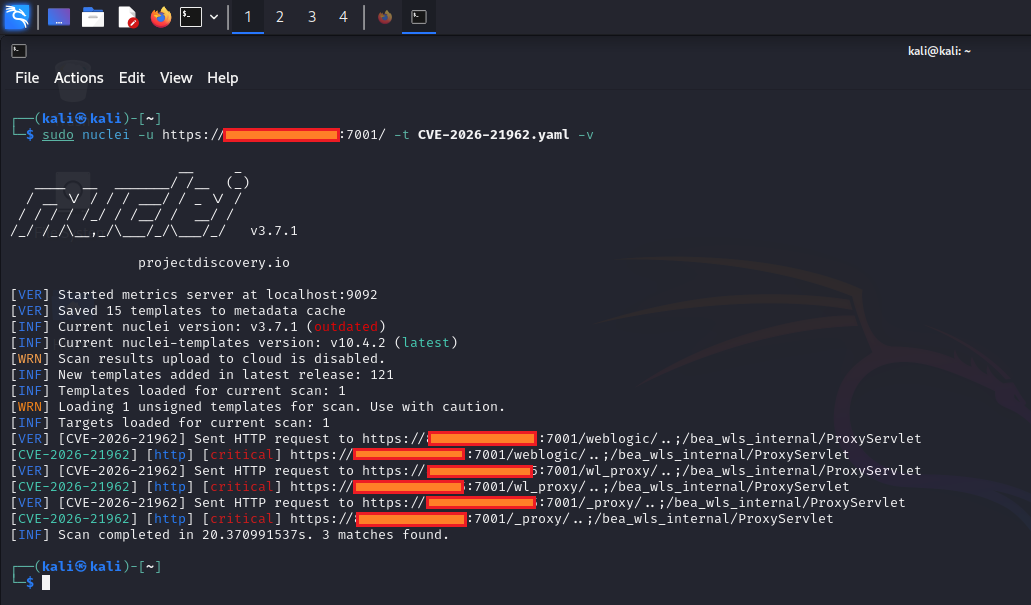 0xblackash/cve-2026-21962
CVE-2026-21962
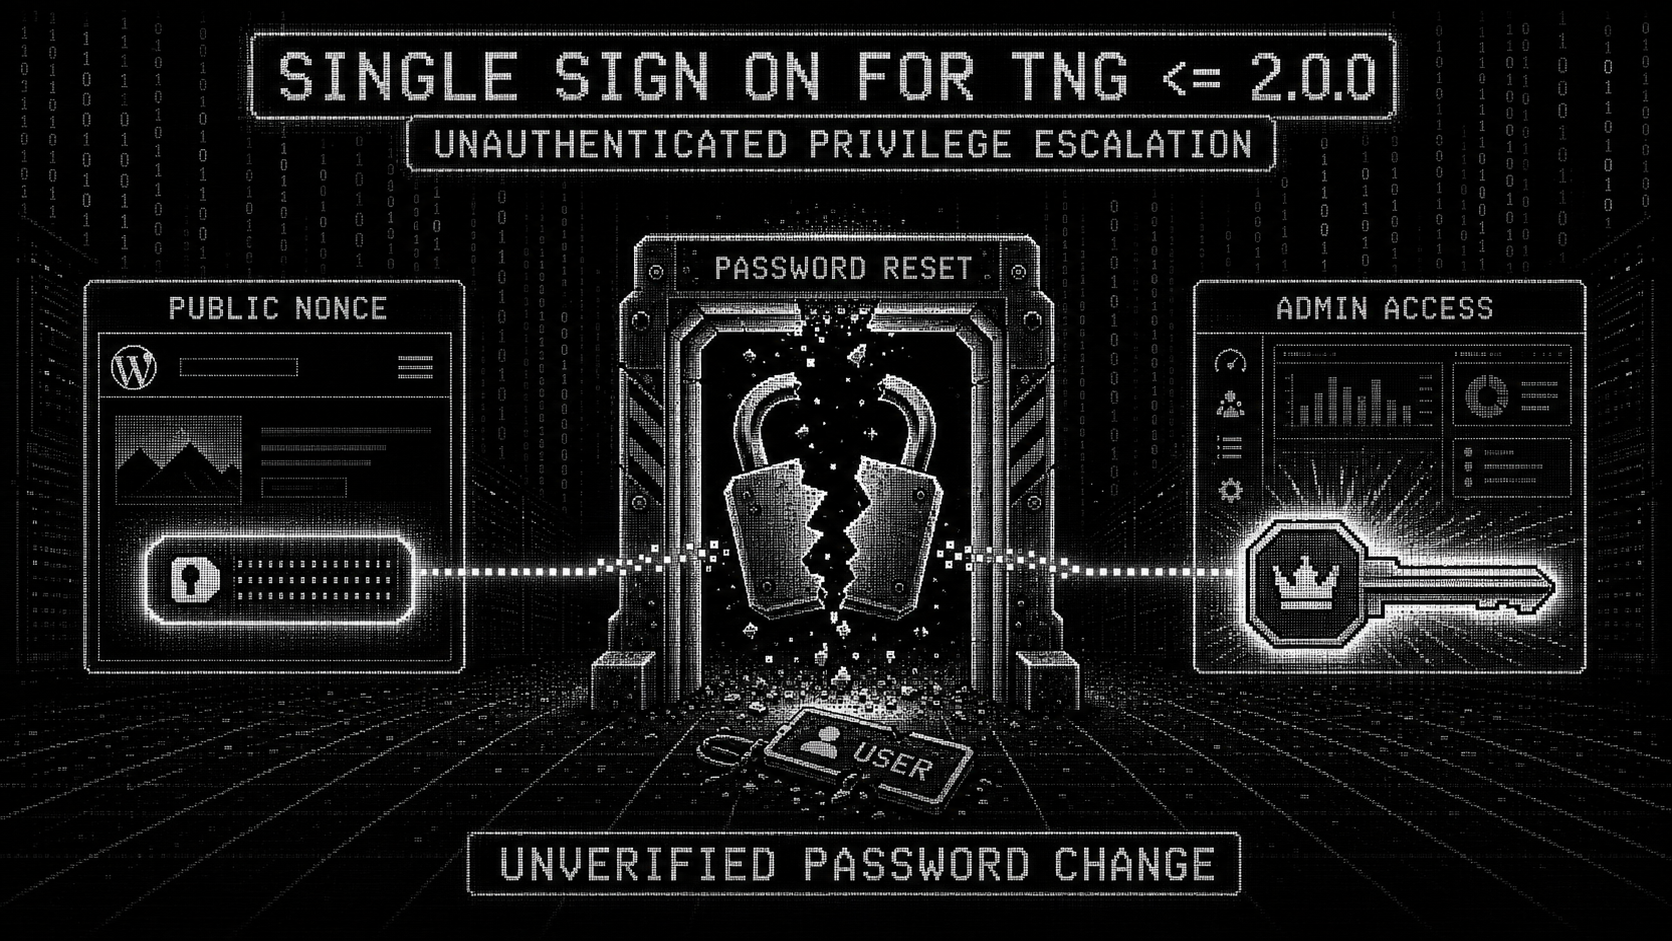 instructor-admin/cve-2026-15964-poc
PoC & checker for CVE-2026-15964 - unauthenticated password change in the WordPress plugin Single Sign On For TNG <= 2.0.0 (CVSS 9.8)
 mr-zapi/cve-2024-54085
Just poc for CVE 2024-54085
 abraxas/pfsense-api-fleet-jwt
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - IDOR - one controller JWT is a fleet token
 abraxas/pfsense-api-export-key-get
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - GET export-key private keys
 sneden/zeroheight-account-verification-bypass-cve-2025-65925
Independent security finding – Zeroheight account creation bypass via missing verification enforcement (patched June 2025)
 anach-ai/cve-2026-41940
CVE-2026-41940 — cPanel/WHM Auth Bypass By Dr.Anach, CRLF injection in `cpsrvd` Basic auth handler → unauthenticated WHM API access → RCE as root.…
 ex-cal1bur/cve-2026-44595
# CVE-2026-44595 YAMCS Unauthorized User Enumeration via IAM API
 gmh5225/jataayu
LLM-backed AI agent security — inbound injection detection + outbound privacy protection
 elevenpaths/latch-plugin-openvpn-as
Latch plugin for OpenVPN Access Server enabling two-factor authentication (2FA) to secure VPN connections with time-based one-time passwords (TOTP).
 nxploited/cve-2025-9209
RestroPress – Online Food Ordering System 3.0.0 - 3.1.9.2 - Unauthenticated Information Exposure to Authentication Bypass via Forged JWT
 randomrobbiebf/cve-2024-9821
Bot for Telegram on WooCommerce <= 1.2.4 - Authenticated (Subscriber+) Telegram Bot Token Disclosure to Authentication Bypass
 jenderal92/owa-valid-login-checker
Owa Valid Login Checker
 trqt/cve-2024-48322
Exploit for CVE-2024-48322 targeting RunCodes instances. Retrieves user passwords via email inbox after authentication bypass, requiring only any…