

agentsh
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
ai-securityauthentication-authorizationcloud-security+7
40417h 12m ago
canyonroad/agentshExecution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
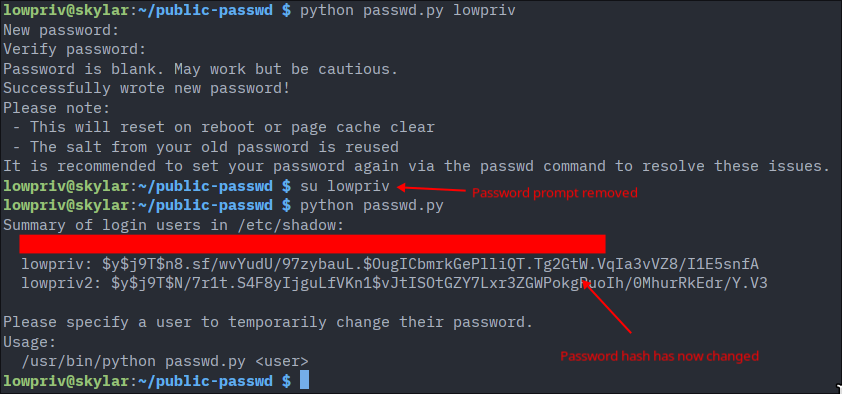 st4rburn/public-passwd
Use CVE-2026-46333 and CVE-2026-31431 to change any user's password.
 xitexploiter96-dot/cve-2025-23419
Python-based TLS session reuse exploit tester that checks for authentication bypass vulnerabilities in misconfigured servers requiring client…
 0xpthree/next.js_cve-2025-29927
Reproduces CVE-2025-29927 middleware authorization bypass in Next.js 14.2.24 and demonstrates exploitation with curl to bypass authentication and…
 hotblac/cve-2022-31692
Demonstrates CVE-2022-31692 Spring Security authorization bypass with a minimal Java exploit, enabling security researchers to test and understand…
 otterhacker/labs4u2self
Deployable AWS-hosted Active Directory pentest lab with domain controller and vulnerable MSSQL; practice S4U2Self abuse, SQL brute force, and RCE.
 bhdresh/cve-2021-33766
ProxyToken (CVE-2021-33766) : An Authentication Bypass in Microsoft Exchange Server POC exploit
 soledad208/cve-2018-10933
CVE-2018-10933 very simple POC
 likekabin/cve-2018-10933_ssh
Python exploit for CVE-2018-10933 that bypasses libssh server authentication and spawns an unauthenticated shell on vulnerable SSH servers.