macOS-enterprise-privileges

This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…

This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…

Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…

Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software

This publication is a collection of various common attack scenarios on Microsoft Entra ID (formerly known as Azure Active Directory) and how they can…

A reverse proxy that provides authentication with Google, Azure, OpenID Connect and many more identity providers.

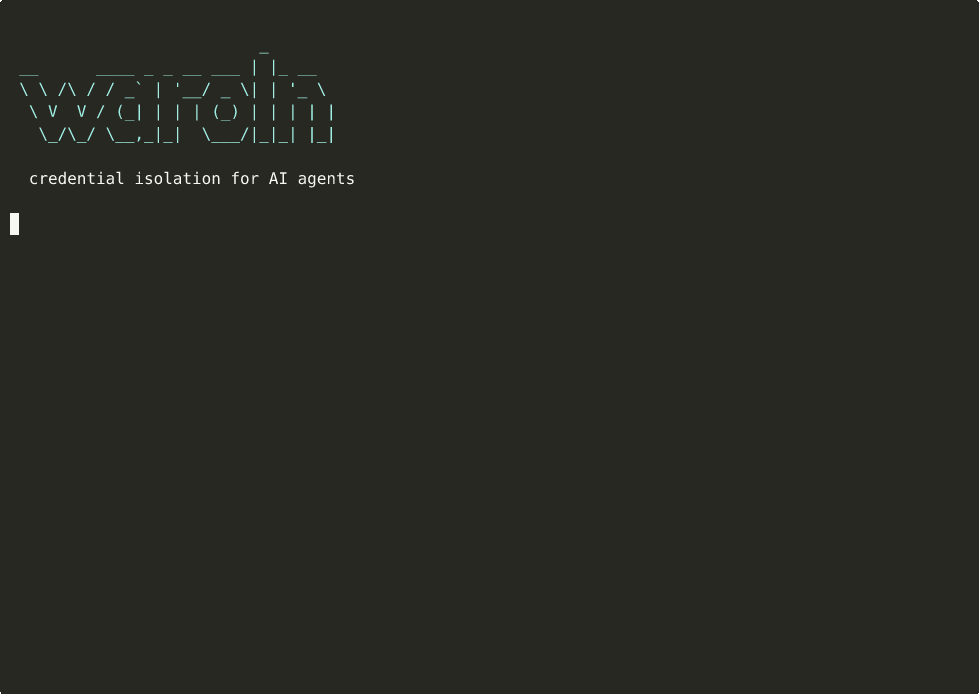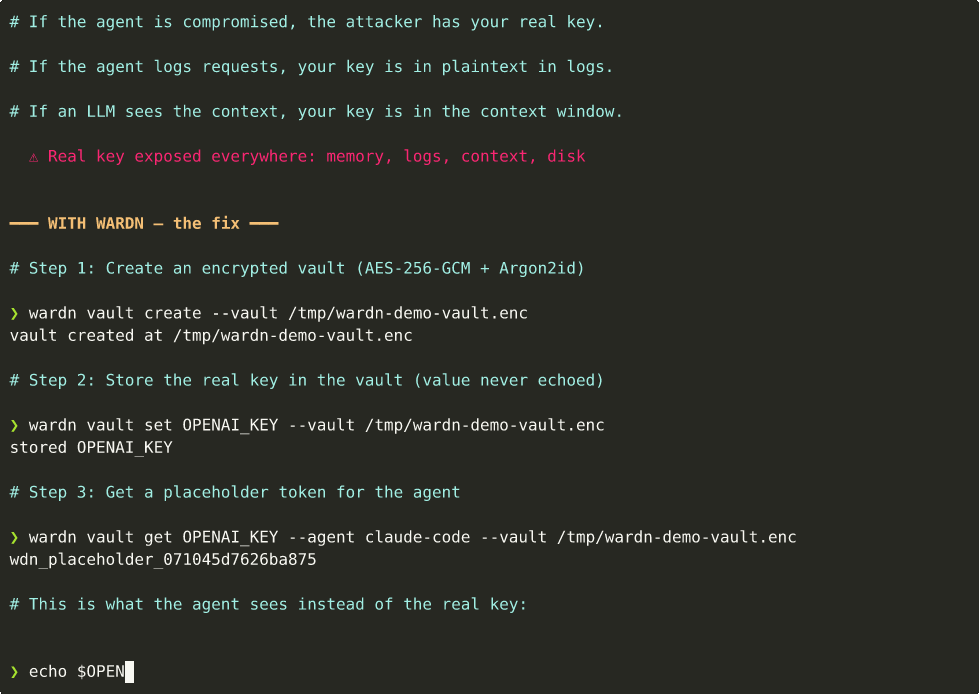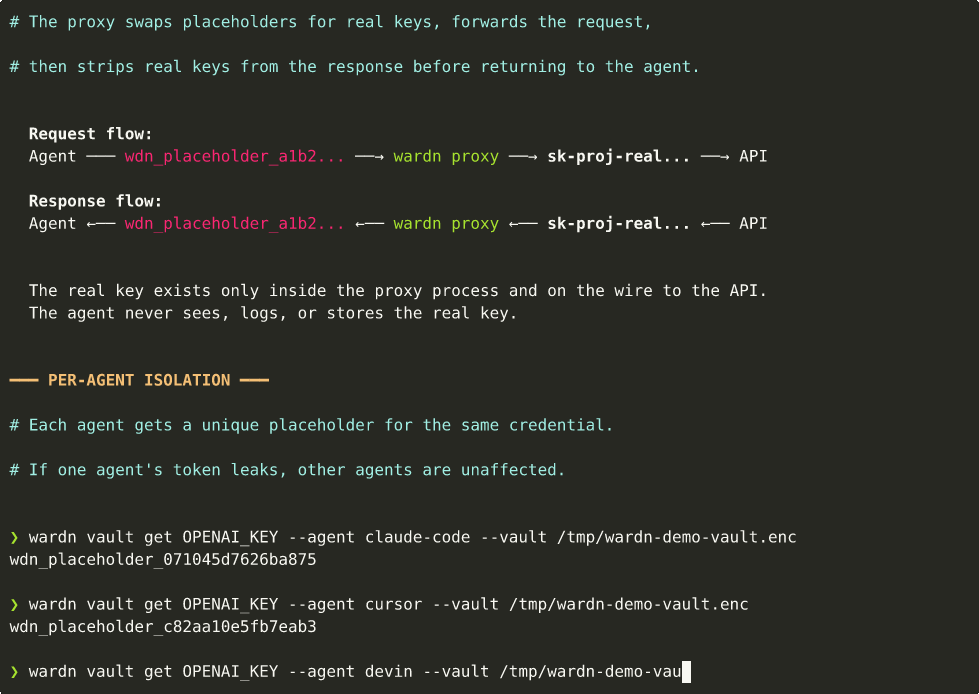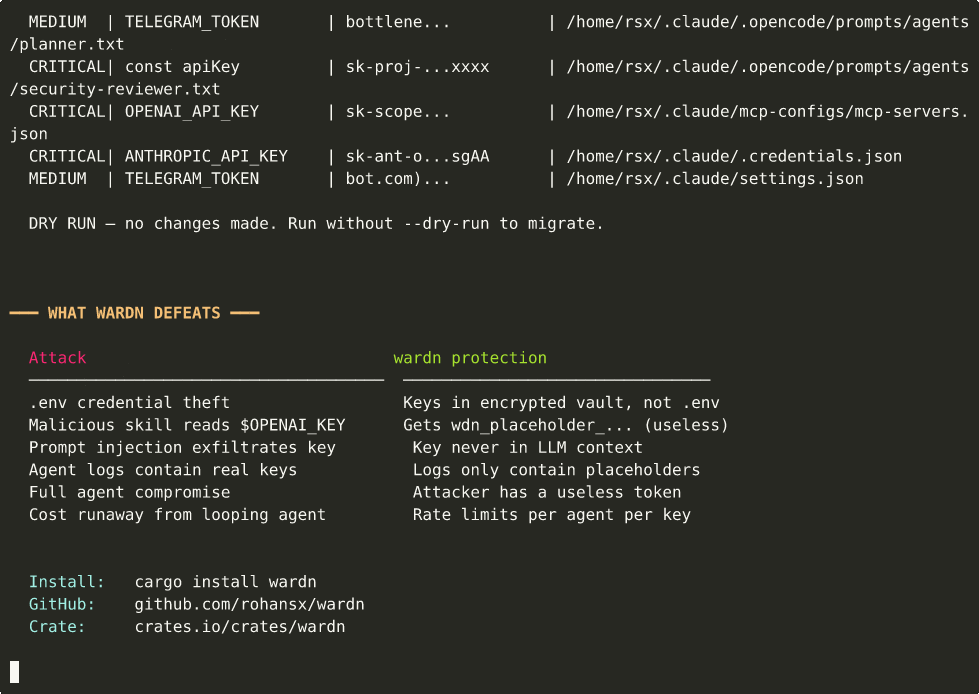
credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.

Sanitized report and local proof-of-concept script for CVE-2026-102975, a MediaWiki RevisionDelete API authorization bypass allowing suppression…

Sanitized report and local proof-of-concept script demonstrating the MediaWiki action=emailuser API EmailUserAuthorizeSend hook bypass…

A new open-source tool to quickly audit SAP permissions.

Cyrus SASL API implementation providing client- and server-side authentication and authorization services via pluggable SASL mechanisms per RFC 4422.

Python PoC for CVE-2026-21010 that replays captured SIP digest Authorization headers to bypass nonce uniqueness/expiration and make unauthorized VoIP…

Gitea Docker Image Authentication Bypass

Authentication bypass exploit for CVE-2026-32746 targeting legacy Telnet servers, with defensive guidance and Go-based implementation for authorized…

Pre-auth RCE exploit for Craft CMS in Go. Grabs session/CSRF token, poisons PHP session, triggers deserialization for command execution or reverse…

Single Packet Authorization > Port Knocking

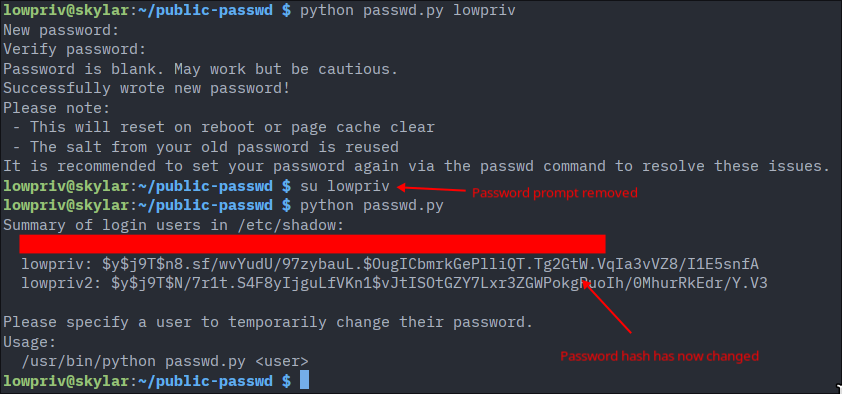
Use CVE-2026-46333 and CVE-2026-31431 to change any user's password.

Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.

A framework for creating smart cards (ICC-based cards with contacts).