carbon-identity-framework

Core framework for identity and access management, providing authentication, authorization, and identity governance capabilities for enterprise…

Core framework for identity and access management, providing authentication, authorization, and identity governance capabilities for enterprise…

The Symfony PHP framework

Secure, private AI agent operating system with local encrypted storage, OAuth/SSO authentication, policy-based access control, and extensible…

A flexible, composable authorization framework for Kit (inspired by Action Policy)

credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.

An open-source framework for verifiably private AI inference

Open-source services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, JAX-WS, and JAX-RS APIs.

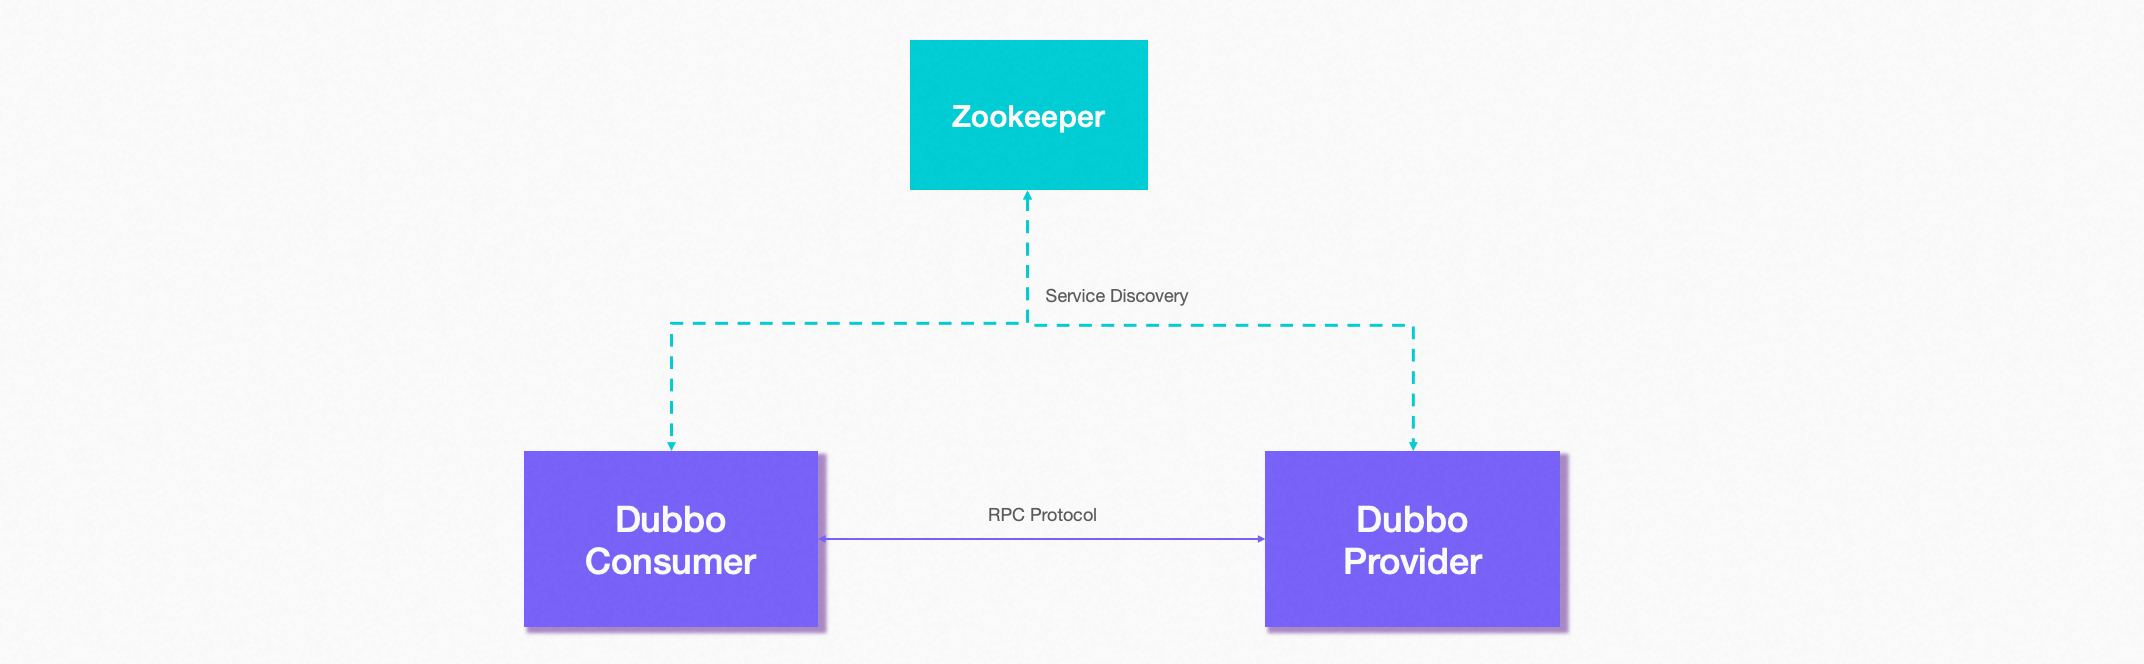
High-performance Java RPC and microservices framework with service discovery, traffic management, observability, and built-in security for building…

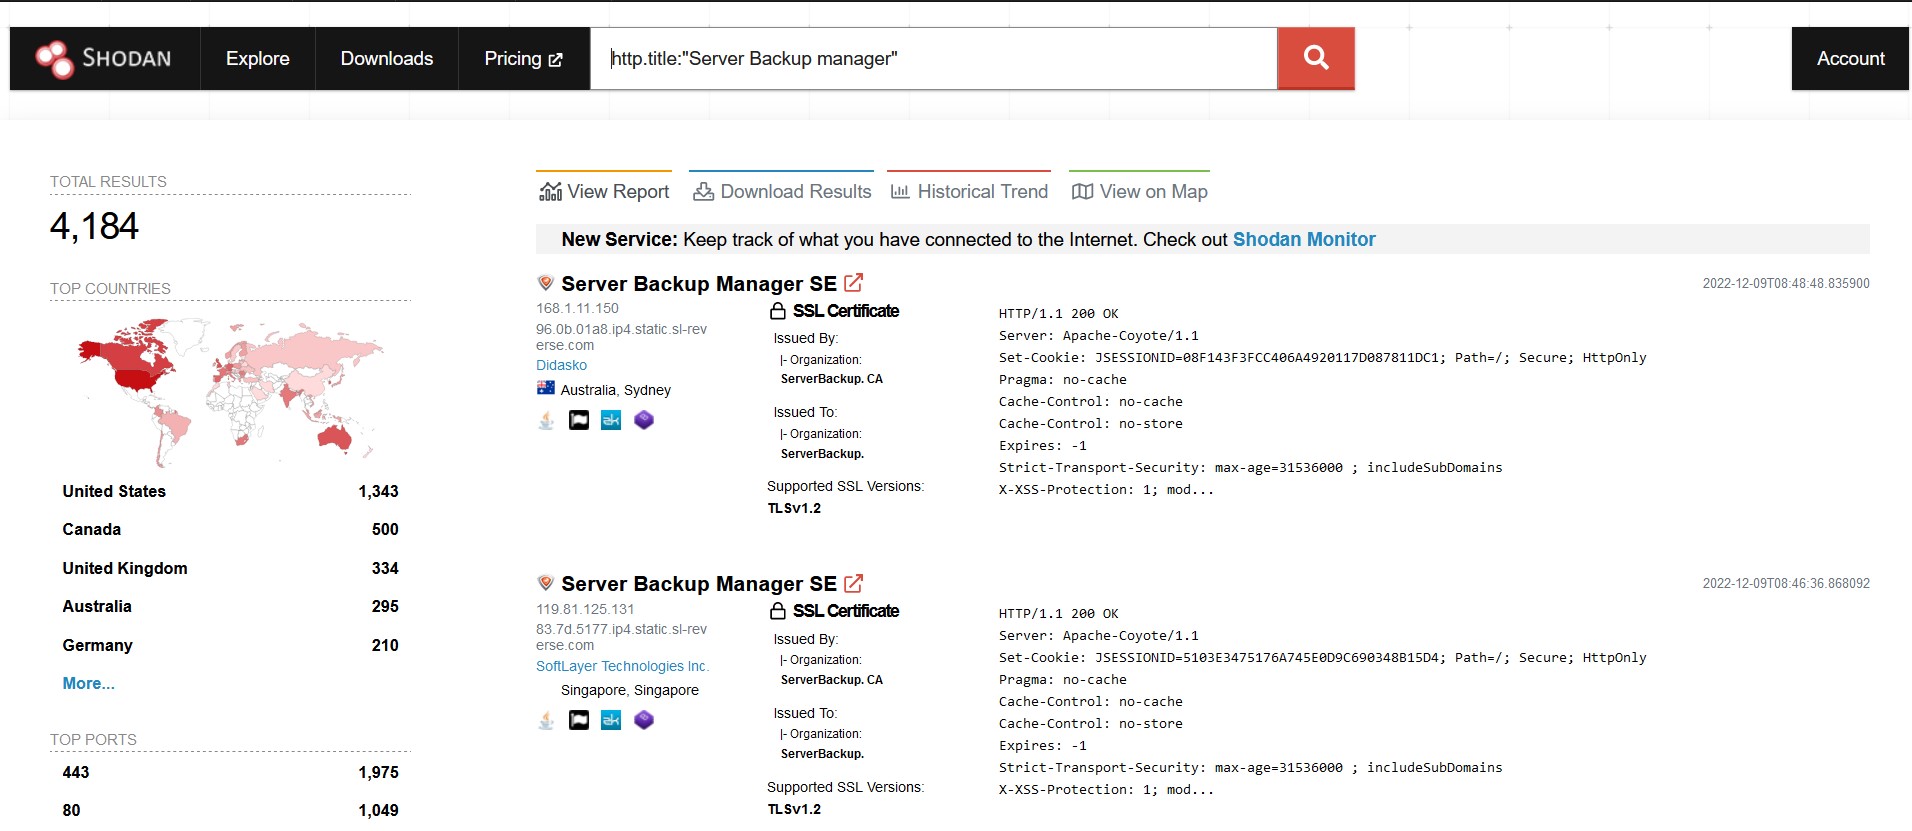
Python exploit for CVE-2022-36537, an authentication bypass in ZK Framework affecting R1Soft Server Backup Manager, allowing retrieval of web context…

Web services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, WS-Trust, and JAX-WS/JAX-RS APIs.

Java security framework providing authentication, authorization, cryptography, and session management APIs to secure any application from mobile to…

POC of CVE-2022-36537

CVE-2025-29927 is a critical security vulnerability affecting Next.js, a popular React framework for building full-stack web applications. This flaw…

CVE-2025-29927 - Critical Security Vulnerability in Next.js

Proof-of-concept demonstrating authorization bypass in Spring Security's RegexRequestMatcher (CVE-2022-22978) using CRLF injection, with analysis and…

PoC of CVE-2022-22978 vulnerability in Spring Security framework

Step-by-step demonstration of CVE-2022-22978 authorization bypass in Spring Security's RegexRequestMatcher, with vulnerable app setup, payload…