macOS-enterprise-privileges

This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…

This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…

Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…

👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…

cPanel & WHM - Authentication Bypass via Session-File CRLF Injection

SCCMSecrets.py aims at exploiting SCCM policies distribution for credentials harvesting, initial access and lateral movement.

Exploit for CVE-2026-55040 in Microsoft SharePoint, forging JWT tokens via algorithm none, weak HS256 secrets, and RS256 substitution to impersonate…

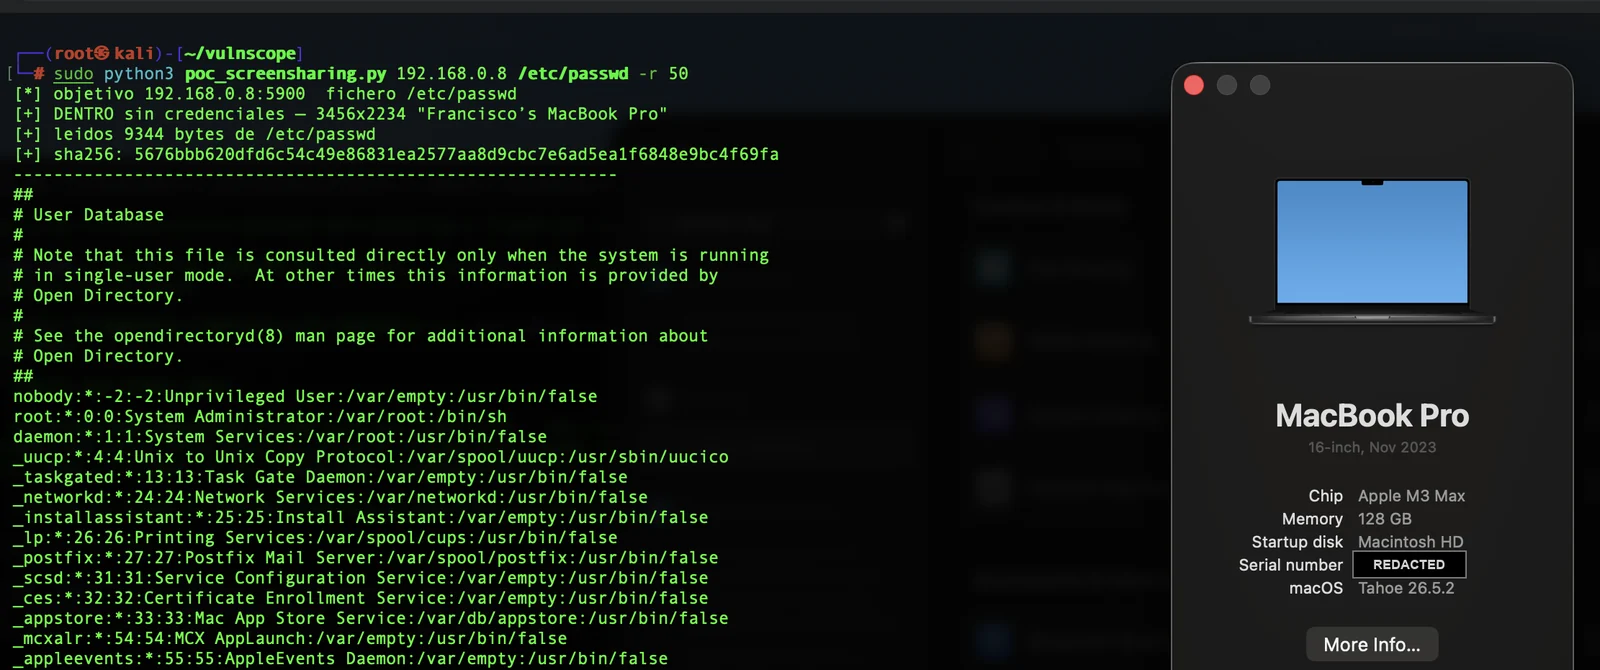
Read-only PoC for CVE-2026-65400 — macOS Screen Sharing (screensharingd) pre-auth SRP bypass giving root file read. Patched in macOS 26.6.1 / 15.7.9…

POC tool for ResetNightmare (CVE-2026-27912)

Exploit PoC for WordPress Burst Statistics authentication bypass allowing unauthenticated admin impersonation via crafted Authorization header.

Exploit PoC for unauthenticated doctor/receptionist account creation in the KiviCare WordPress plugin via improper privilege management, providing…

PoC for CVE-2026-27912 - Windows Kerberos Elevation of Privilege (ResetNightmare). Unauthorized password reset via Kerberos flaw. For security…

C# tool for enumerating and exploiting misconfigurations in Active Directory Certificate Services (AD CS), enabling certificate template abuse,…

CVE-2026-56164 is a critical missing-authentication vulnerability affecting on-premises Microsoft SharePoint Server. It allows unauthenticated,…

Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…

Silent;Call — Pre-authentication remote root on Cisco CUCM 15.x (CVSS 10.0)

Python proof-of-concept for LDAP anonymous bind privilege escalation, simulating insecure ACLs to create admin users via unauthenticated LDAP binds.

A flaw in Gitea Open Source Git Server’s approval‑gate logic allows a pull request that originates from a permanent fork to merge without satisfying…

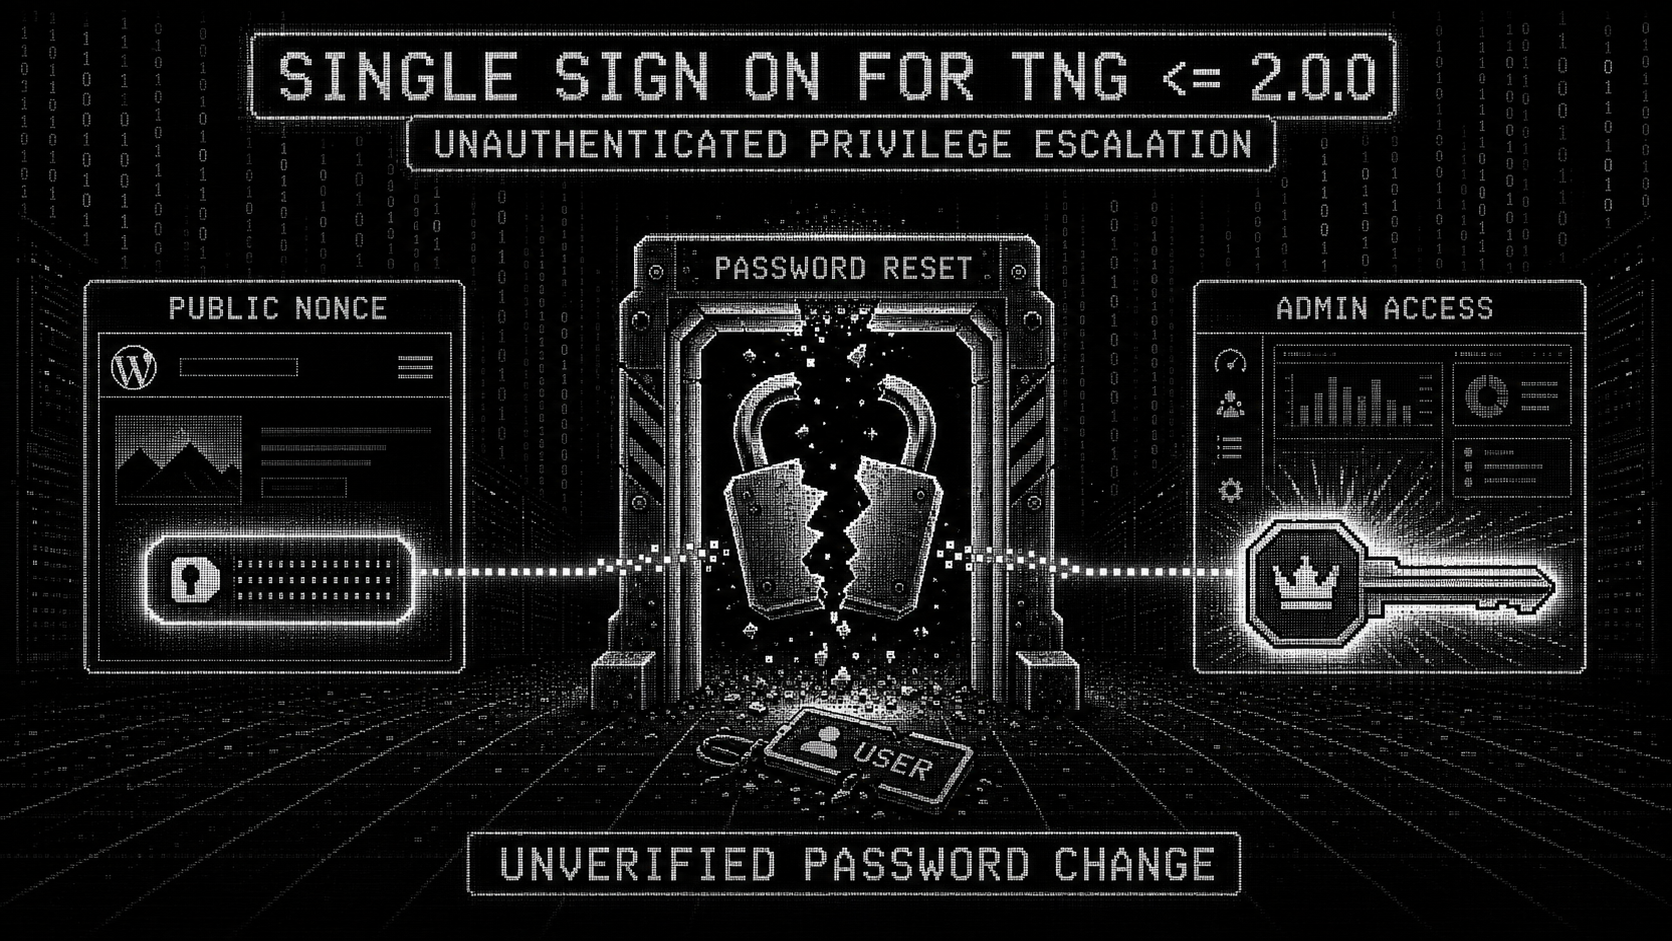
PoC & checker for CVE-2026-15964 - unauthenticated password change in the WordPress plugin Single Sign On For TNG <= 2.0.0 (CVSS 9.8)