

OpenShell
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
ai-securityauthentication-authorizationcloud-security+7
12.4k
nvidia/openshellSandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 tc4dy/cve-2026-54121-poc-exploit
👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…
 openvpn/openvpn
Secure tunneling daemon implementing VPN protocols with TLS encryption, certificate authentication, and routing/firewall configuration for private…
 juanfont/headscale
An open source, self-hosted implementation of the Tailscale control server
 opfour/op4
Terminal-based encrypted messenger with post-quantum cryptography, Double Ratchet protocol, and Tor anonymity. Features duress passphrase, deniable…
 xrzmodz444/cve-2026-41940-poc-linux
Proof-of-concept exploit for CVE-2026-41940, an authentication bypass in cPanel/WHM. Supports custom payloads and verbose logging, compatible with…
 umputun/reproxy
Lightweight edge HTTP(S) server and reverse proxy with automatic SSL, Docker/Consul discovery, per-route authentication, rate limiting, and…
 focused.hunts/the.vault
Privacy-first password manager with local storage and bring-your-own-cloud sync across Google Drive, Microsoft OneDrive, and Dropbox. Your…
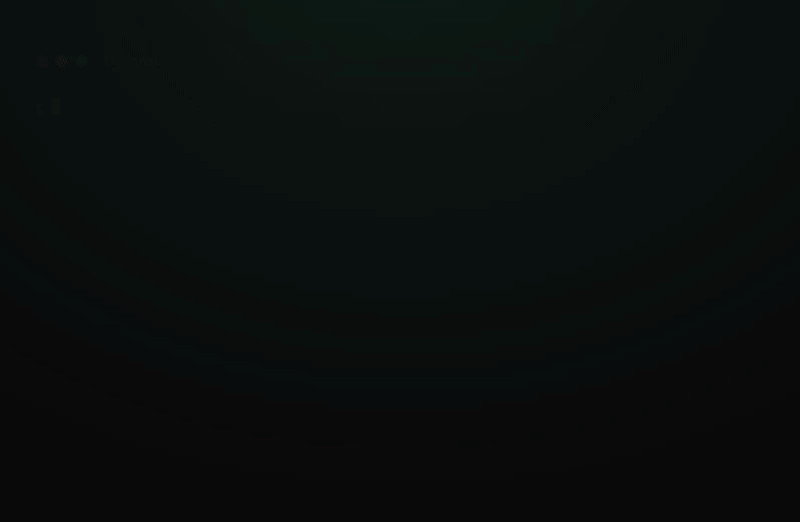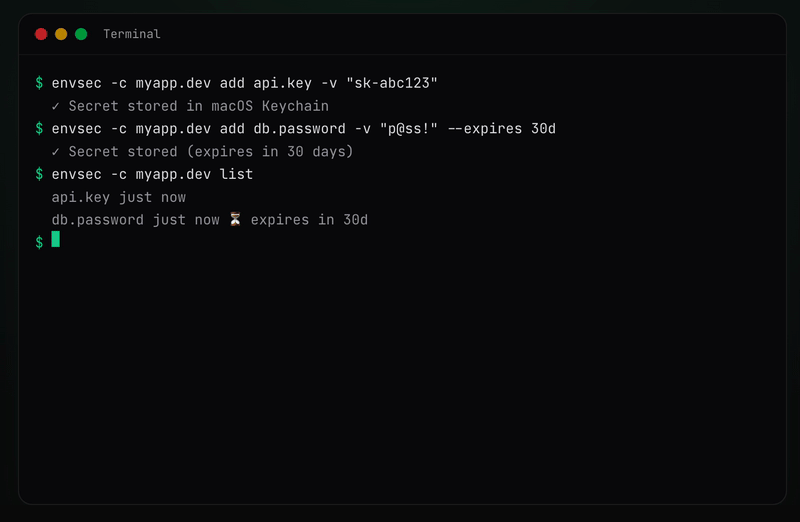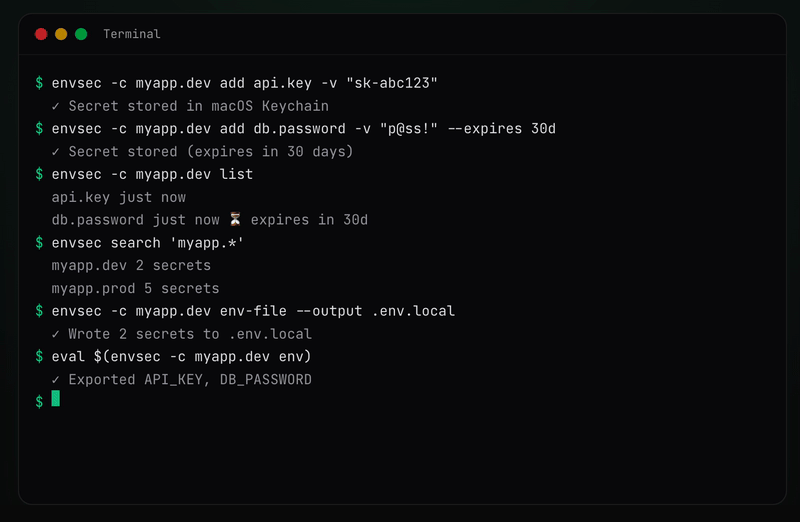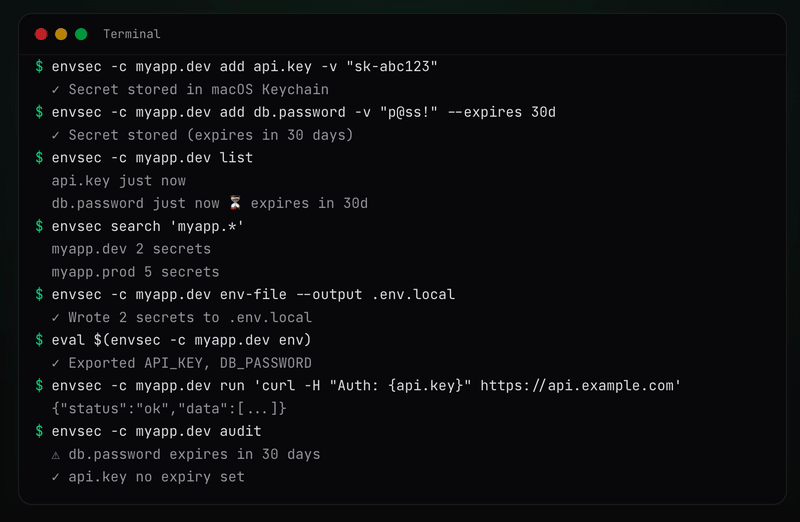 davidnussio/envsec
Secure CLI tool for managing environment secrets using native OS credential stores (macOS Keychain, Linux Secret Service, Windows Credential Manager)
 semperis-community/resetnightmare
POC tool for ResetNightmare (CVE-2026-27912)
 oxstussz-eng/kerberos-cve-2026-27912
PoC for CVE-2026-27912 - Windows Kerberos Elevation of Privilege (ResetNightmare). Unauthorized password reset via Kerberos flaw. For security…
 sfewer-r7/cve-2026-55040
Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…
 monkeysec-sys/kangaroo
Authentication bypass exploit for CVE-2026-32746 targeting legacy Telnet servers, with defensive guidance and Go-based implementation for authorized…
 scipag/hardeningkitty
HardeningKitty - Checks and hardens your Windows configuration
 cosignet/sdk
Thin TypeScript + zero-dep Python client and recipes to gate high-risk actions behind a payload-bound passkey approval.
 johanneslks/cve-2026-50338
Proof-of-concept exploit for CVE-2026-50338: cross-issuer authentication bypass in Spring Cloud Azure B2C resource servers. Demonstrates token…
 sachitrafa/yourmemory
Agentic AI memory with Ebbinghaus forgetting curve decay. +16pp better recall than Mem0 on LoCoMo.
 mrash/fwknop
Single Packet Authorization > Port Knocking