

OpenAM
 openidentityplatform/openam
Open-source access management platform offering single sign-on, adaptive authentication, authorization, and federation for secure access to web,…
api-securityauthentication-authorizationcloud-security+3
894
openidentityplatform/openamOpen-source access management platform offering single sign-on, adaptive authentication, authorization, and federation for secure access to web,…
 opennhp/opennhp
A lightweight, cryptography-powered, open-source toolkit built to enforce Zero Trust security for infrastructure, applications, and data in the…
 lore-hex/quill-router
TrustedRouter.com repo for secure LLM proxying
 scopeblind/scopeblind-gateway
Ed25519 signed receipts + Cedar policies for AI agents. Finance mandate gate (Legate), proof packs, 3 IETF Internet-Drafts. npx protect-mcp
 agentrust-io/cmcp
cMCP: Confidential MCP Gateway. Hardware-attested policy enforcement for MCP tool calls.
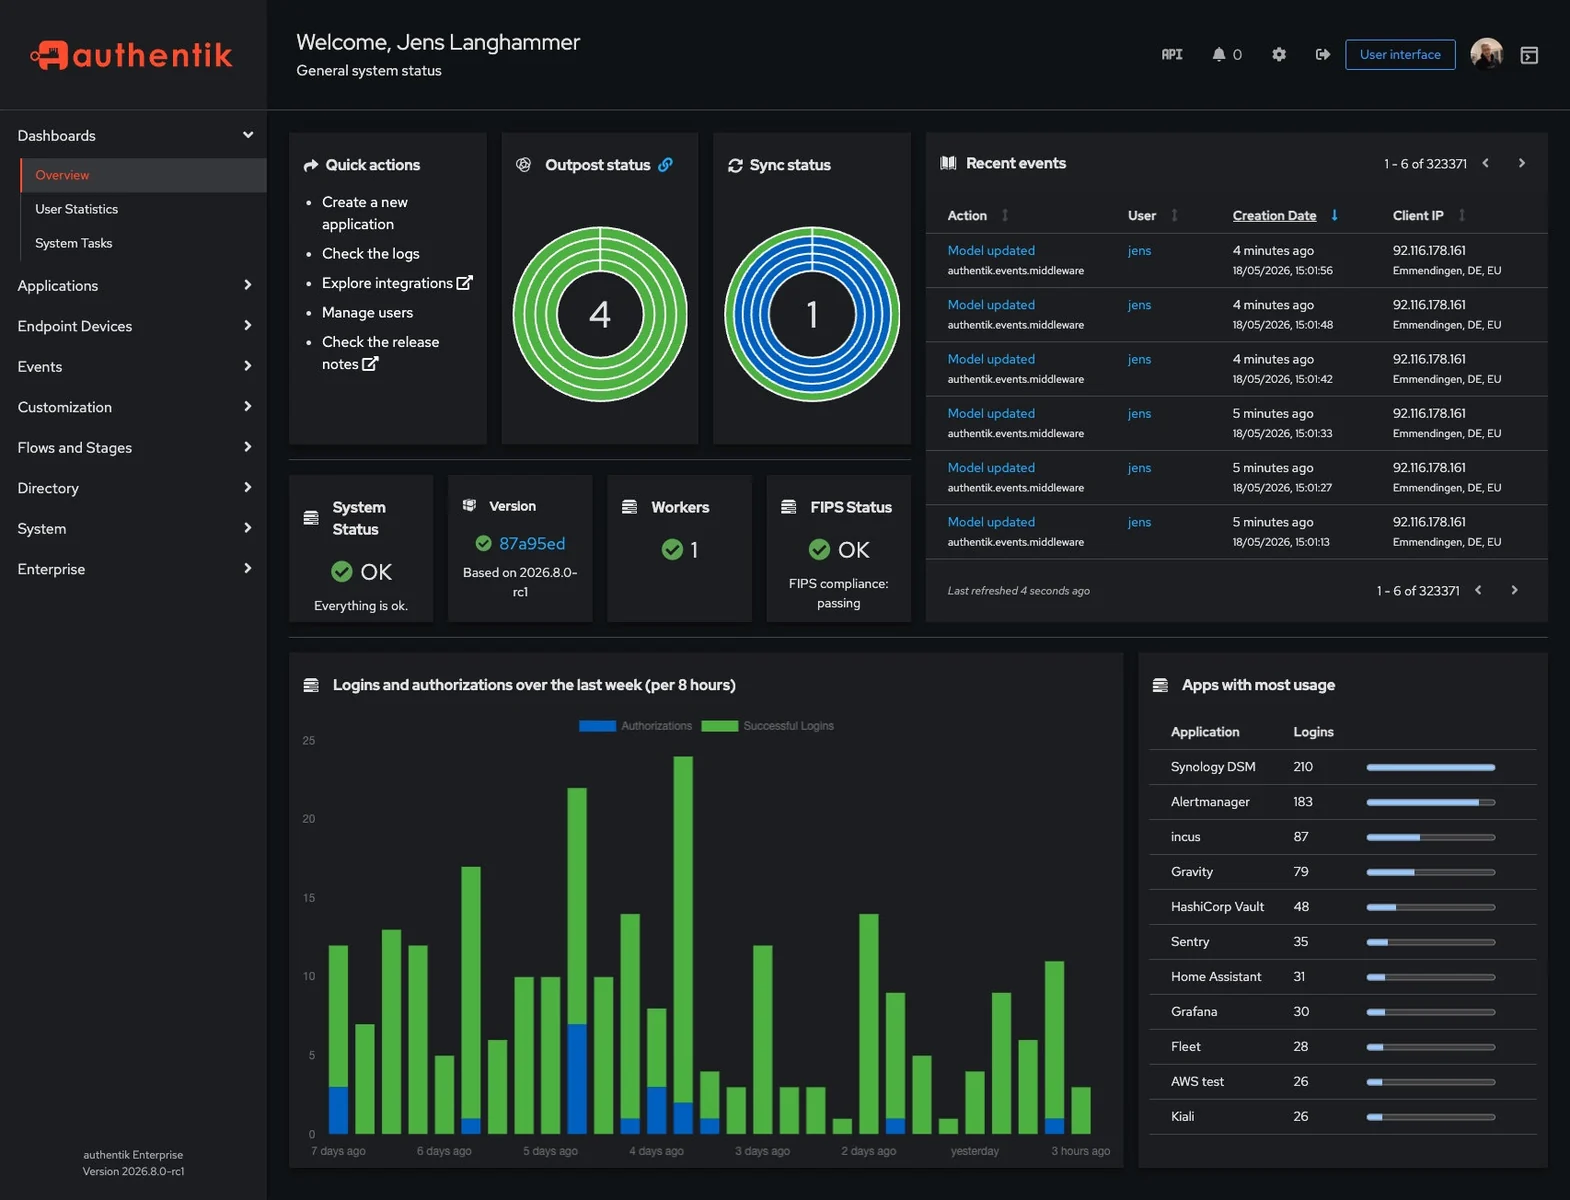 goauthentik/authentik
Provides open-source SSO and identity provider functionality with SAML, OAuth2/OIDC, LDAP, and RADIUS support for centralized authentication,…
 firezone/firezone
WireGuard-based zero-trust access platform providing secure, peer-to-peer remote access with granular policy controls, SSO authentication, and audit…
 infisical/infisical
Infisical is the open-source platform for secrets, certificates, and privileged access management.
 vicanso/pingap
A reverse proxy like nginx, built on pingora, simple and efficient.
 scille/parsec-cloud
Open source Dropbox-like file sharing with full client encryption !
 openziti/ziti
Zero-trust networking platform that makes services invisible with cryptographic identity, policy-based access, and end-to-end encryption. Replaces…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 wso2/carbon-identity-framework
Core framework for identity and access management, providing authentication, authorization, and identity governance capabilities for enterprise…
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 kontext-security/kontext-cli
Secure agents in seconds with permissions enforced at runtime.
 adarsh14734/aegis-releases
Sandbox and MCP proxy that blocks AI coding agents from reading SSH keys, AWS credentials, and .env files, with deny-by-default policy and…
 rocketchat/rocket.chat
The Secure CommsOS™ for mission-critical operations