

OpenShell
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
ai-securityauthentication-authorizationcloud-security+7
18.4k
nvidia/openshellSandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
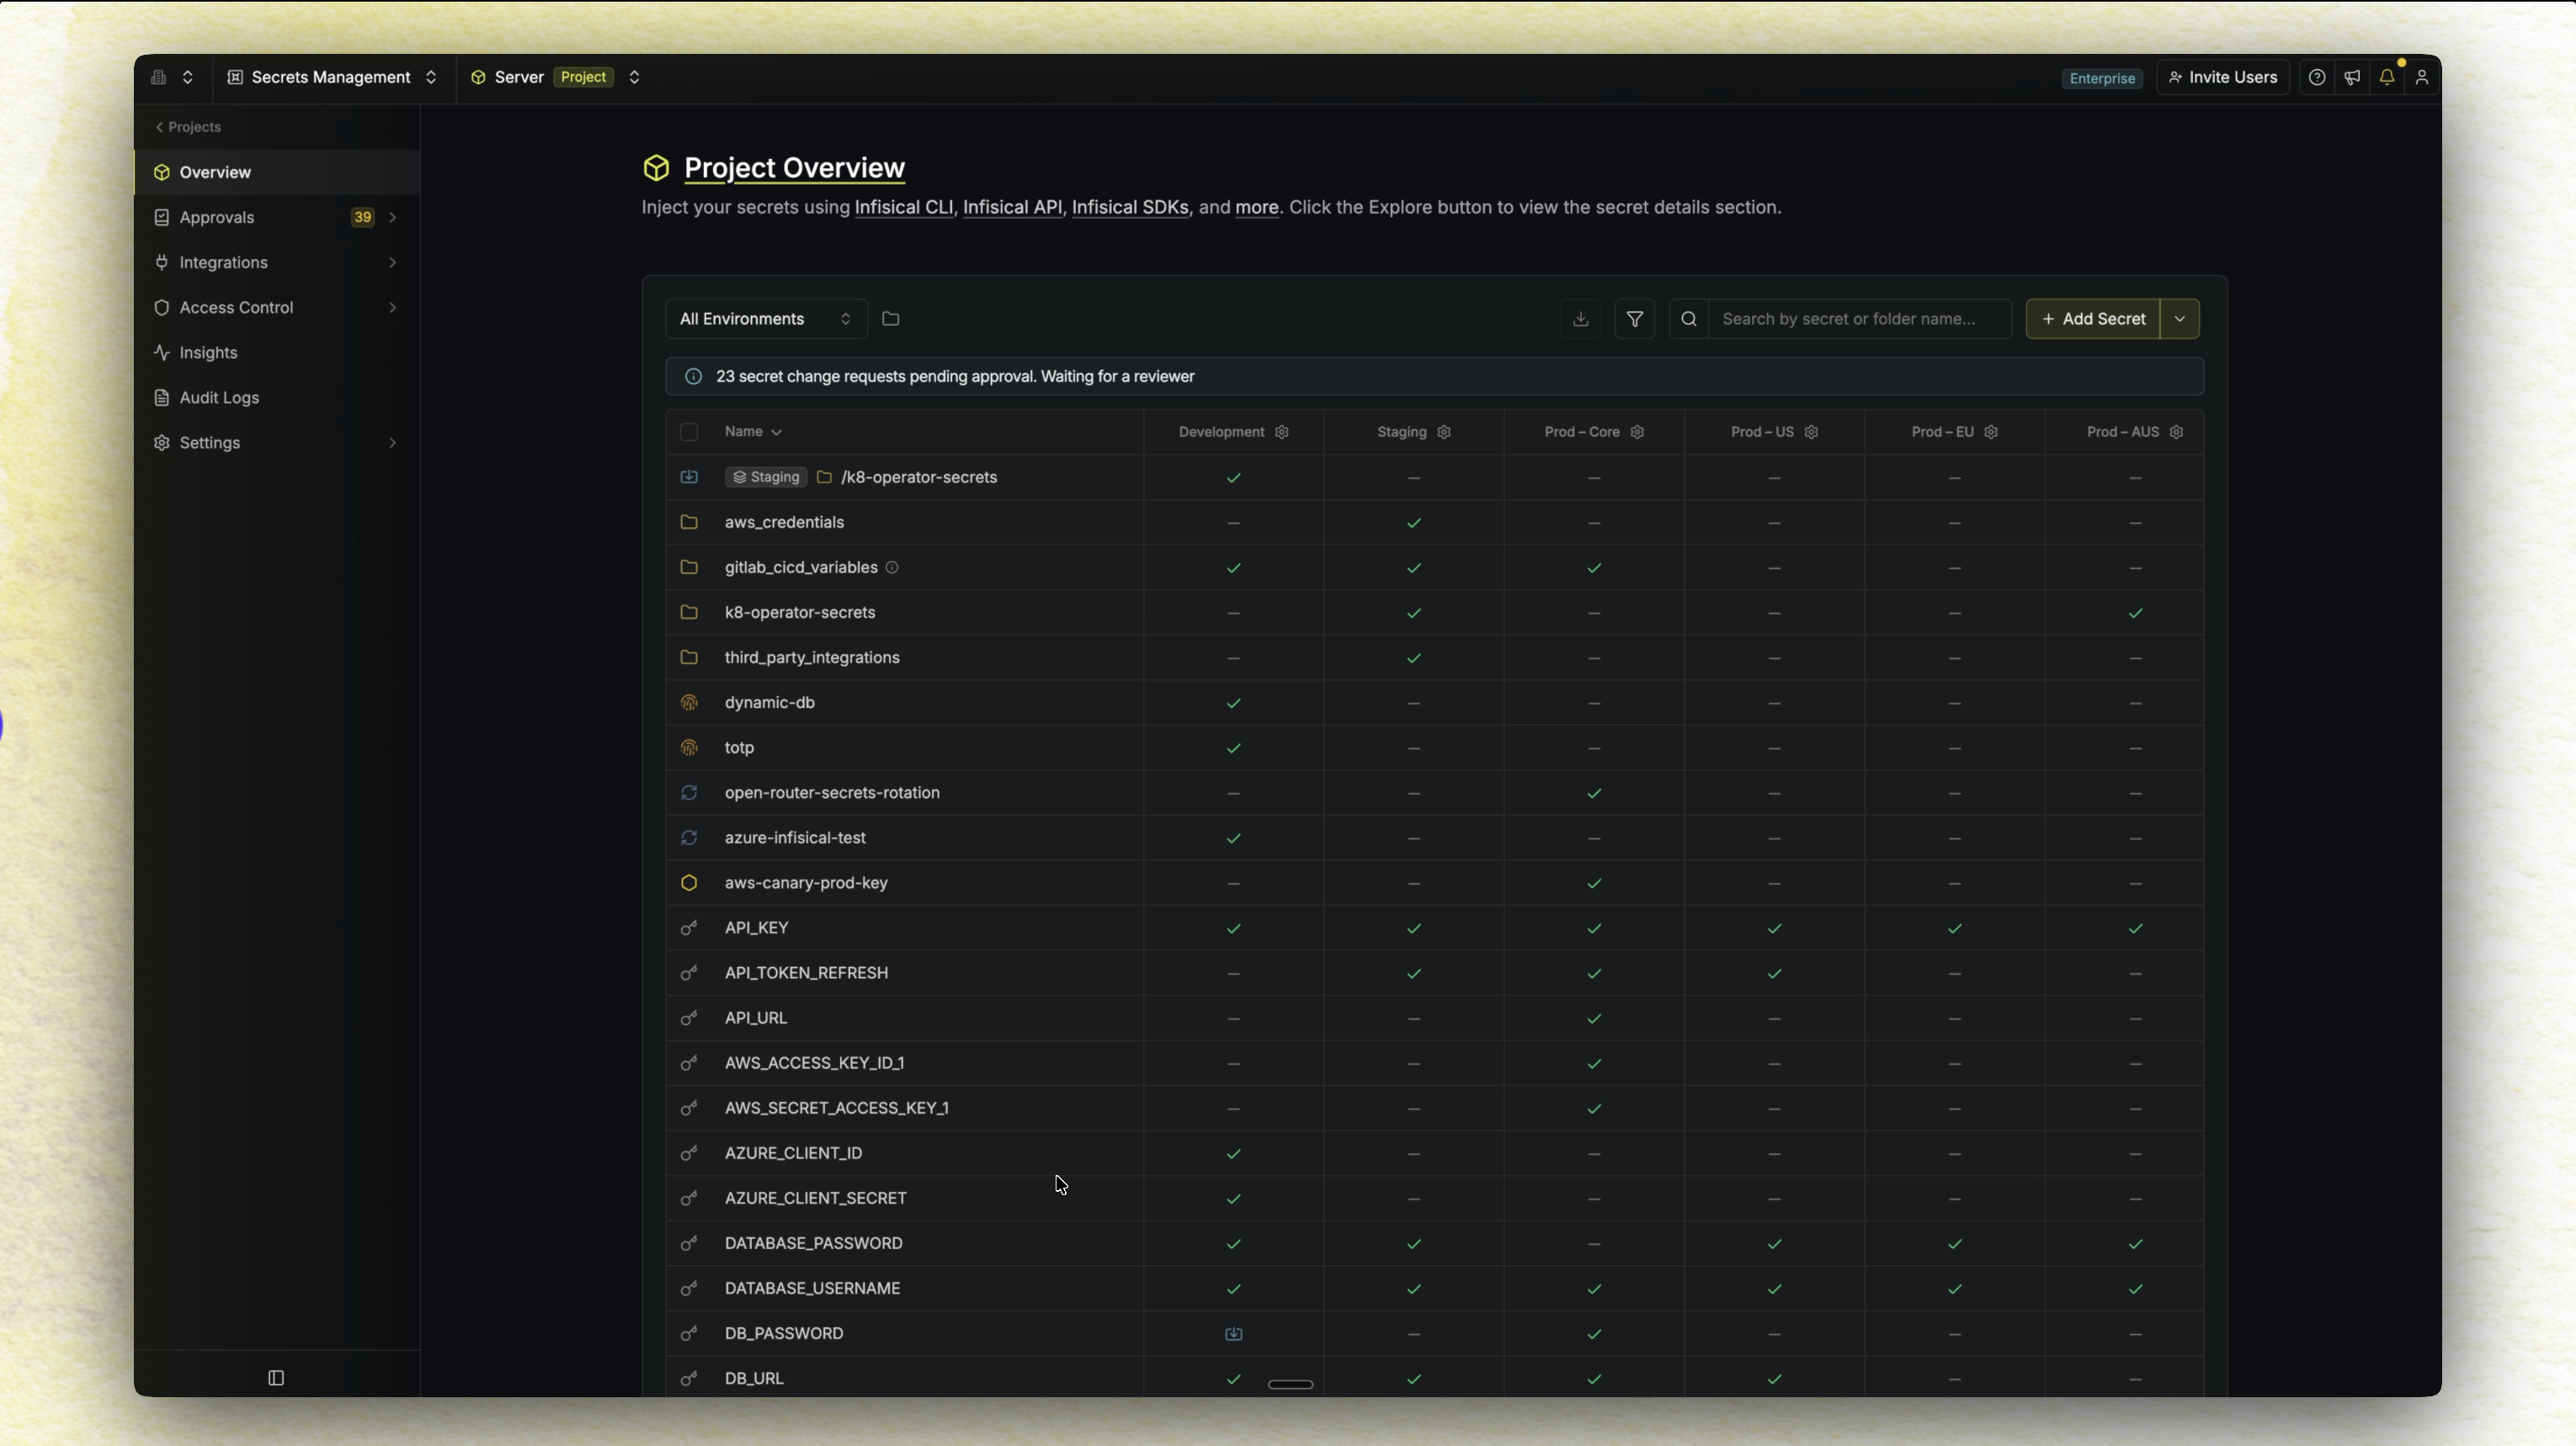 infisical/infisical
Infisical is the open-source platform for secrets, certificates, and privileged access management.
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 tuskira/ai-agent-gateway
Open-source gateway that secures, governs, and observes AI agents' MCP tool calls and LLM traffic, with API-key authentication and an admin console…
 infisical/agent-vault
A HTTP credential proxy and vault for AI agents like Claude Code, OpenClaw, Hermes, custom agents + harnesses, and more.
 zentinelproxy/zentinel
A security-first reverse proxy built to guard the free web.
 scopeblind/scopeblind-gateway
Fail-closed Cedar policy gate plus signed receipts for AI agent tool calls. npx protect-mcp
 onecli/onecli
Open-source sandboxed agent harness for teams. Giving every employee a secured personal agent.
 kontext-security/kontext-cli
Runtime security for AI agents: discover agents, map their permissions, and enforce what they can do.
 peach-research-lab/authorizationbench
The first benchmark to evaluate how well do LLM agents act in alignment with their assigned authorization scope.
 zhengxr930/apex_official
Defender framework for LLM agent security that compiles task contracts, validates capability manifests, and checks effects via PLANT/WRAP proof…
 philippeabraxas-jpg/tbp-network
Theory and implemantation of the TBP protocol to secure networked AI in small to open web networks
 tech4242/aquaman
🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…
 philippeabraxas-jpg/responsible-alliance-protocol
Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…
 commonguy25/authproof-sdk
Cryptographically signed delegation receipts for AI agents. Define exactly what an AI can and can't do — signed, verifiable, tamper-proof.
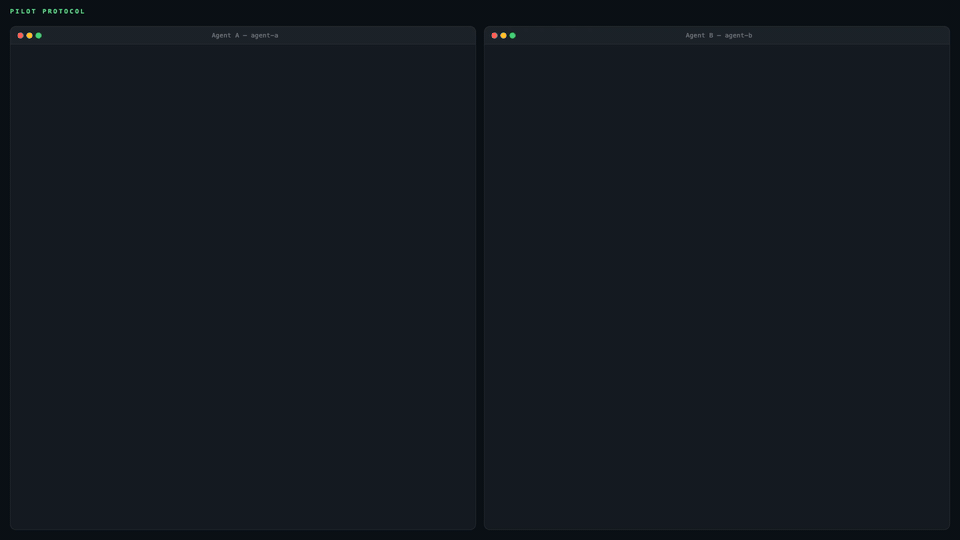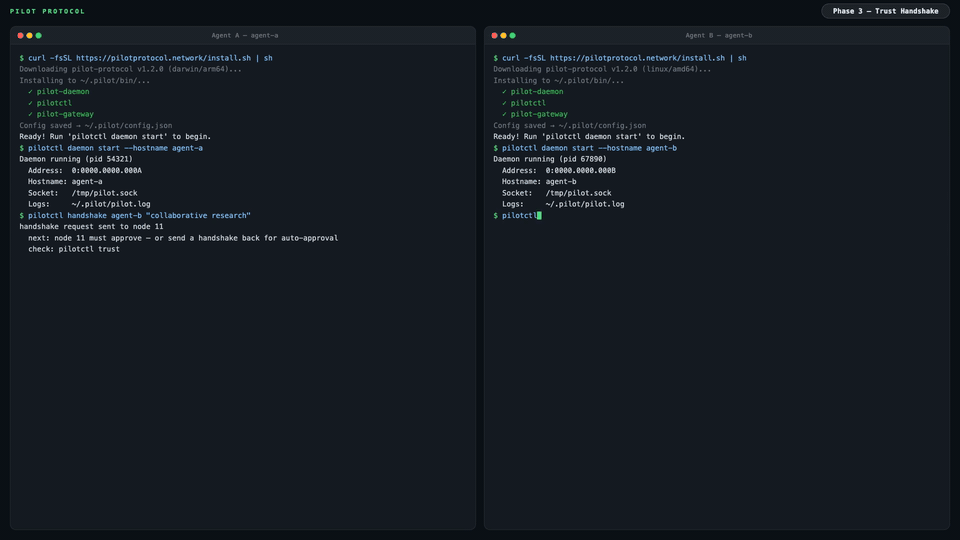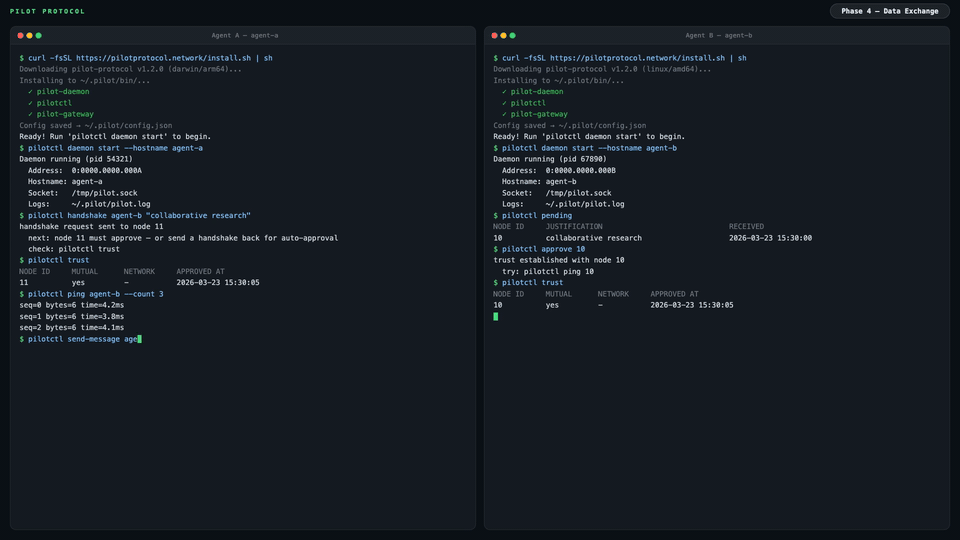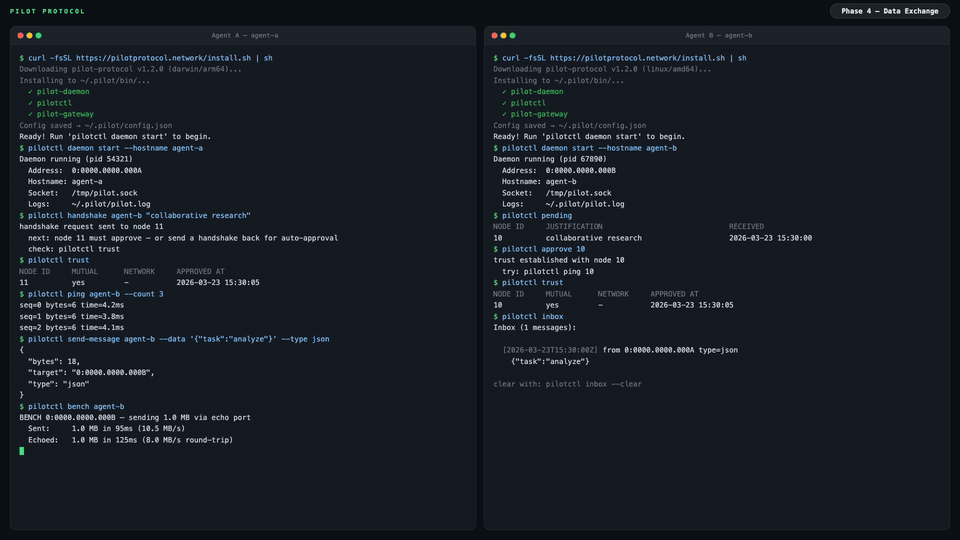 pilot-protocol/pilotprotocol
Overlay network protocol giving AI agents permanent addresses, authenticated encrypted tunnels, and a trust model over UDP. Includes NAT traversal,…
 farenhytee/database-sentinel
Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…
 les-k/wp-secure-mcp
A WordPress plugin exposing an MCP server over the REST API, with the security model as the point -- closes the CVE-2026-15015 OAuth-bypass shape by…