cve-2026-32699-facturascripts-nick-bypass

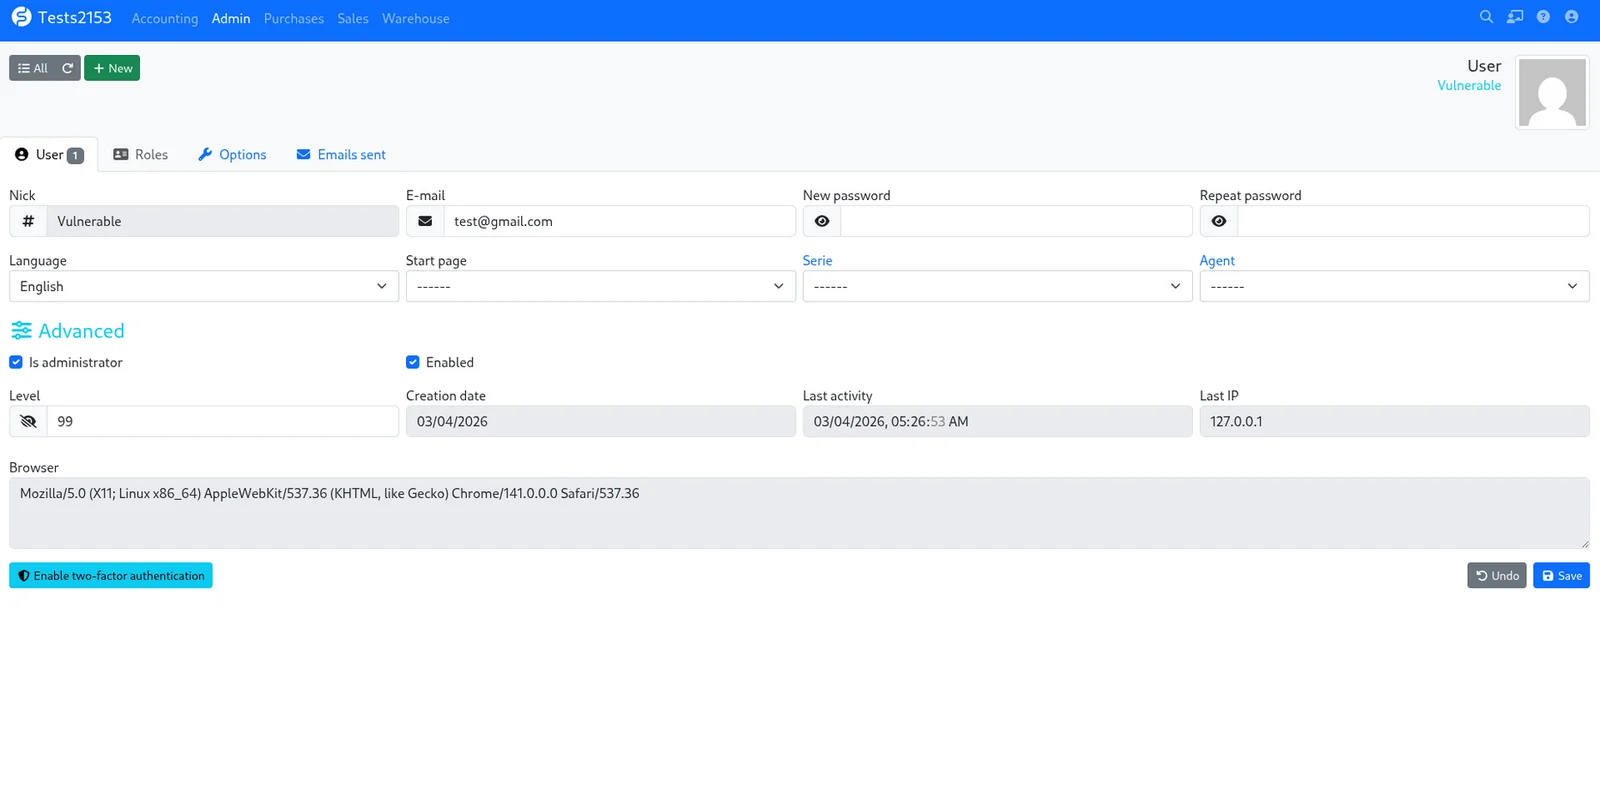
Broken Access Control in FacturaScripts EditUser controller allows authenticated users to rename any account (including admin) by modifying the…

Broken Access Control in FacturaScripts EditUser controller allows authenticated users to rename any account (including admin) by modifying the…

While Fortinet's January 27, 2026 mitigation for **CVE-2026-24858** focuses on blocking specific accounts like `[email protected]`, it fails to…

Runtime security gateway for AI agents: cryptographically attests tool calls, enforces policies, sandboxes execution, and logs tamper-evident audit…

Feature toggle framework for Java enabling runtime feature activation, role-based access, AOP-driven toggling, monitoring, audit trails, and a web…

Feature toggle framework for Java enabling runtime feature activation, role-based access, AOP-driven toggling, monitoring, audit trails, and a web…