
kanidm
 kanidm/kanidm
Self-hosted identity management platform providing WebAuthn passkeys, OAuth2/OIDC SSO, SSH key distribution, RADIUS and LDAP integration for modern…
authenticationauthentication-authorizationidentity-access-management+2
5.4k
kanidm/kanidmSelf-hosted identity management platform providing WebAuthn passkeys, OAuth2/OIDC SSO, SSH key distribution, RADIUS and LDAP integration for modern…
 freeipa/freeipa
Centralizes identity, authentication, and access control for Linux/UNIX environments using LDAP, Kerberos, PKI, DNS, and Active Directory trust.
 al1ex/shiro-basic
This is a simple Shiro-basic project .Just for pentest env
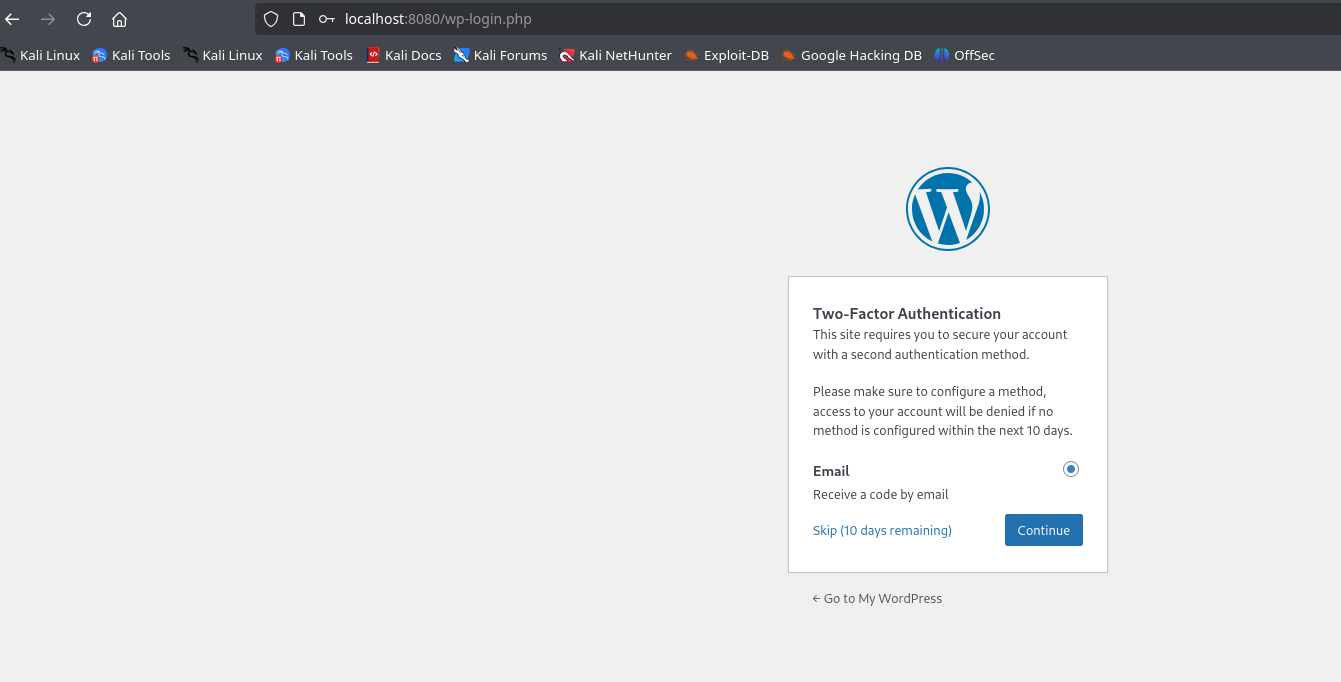 maalfer/cve-2024-10924-poc
Bypass del MFA en WordPress con el plugin Really Simple Security instalado entre las versiones 9.0.0 – 9.1.1.1.
 m3ssap0/wordpress-really-simple-security-authn-bypass-exploit
Python exploit for CVE-2024-10924 authentication bypass in Really Simple Security < 9.1.2. Enables unauthenticated login as any existing WordPress…
 maleeshaudan/wordpress-cve-2024-10924--exploit
WordPress CVE-2024-10924 Exploit for Really Simple Security plugin
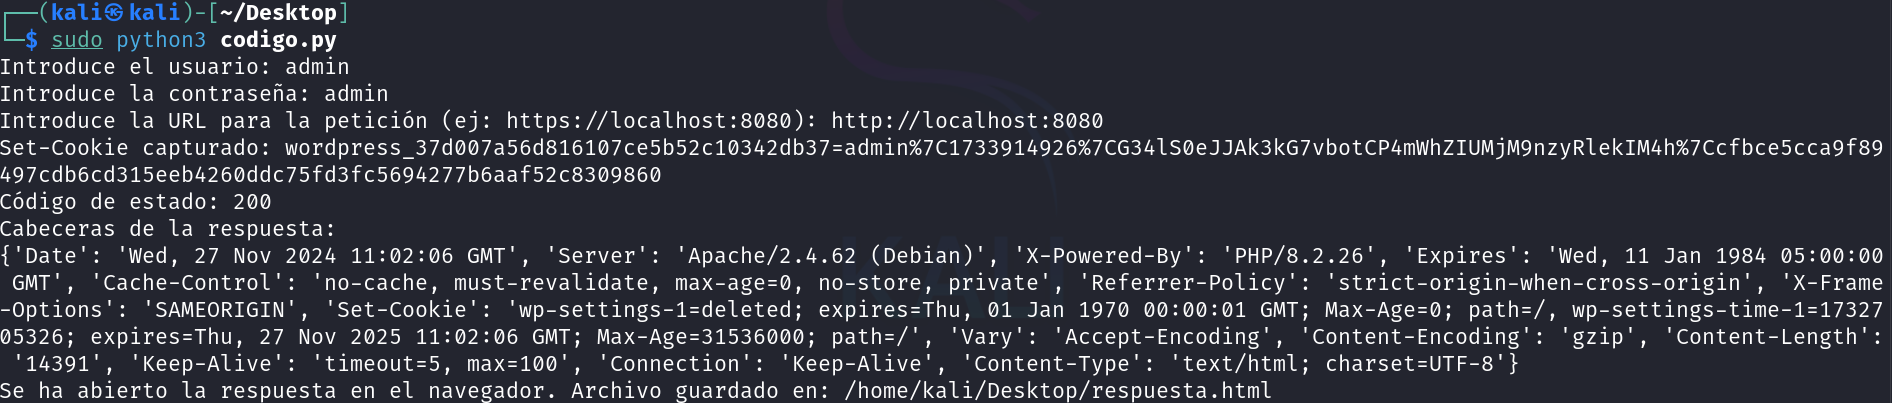 hunt3r850/cve-2024-10924-poc
Proof-of-concept exploit for CVE-2024-10924, an authentication bypass vulnerability in the Really Simple Security WordPress plugin, enabling MFA…
 nxploited/cve-2024-10924-exploit
Really Simple Security (Free, Pro, and Pro Multisite) 9.0.0 - 9.1.1.1 - Authentication Bypass
 sariamubeen/cve-2024-10924
Python exploit for CVE-2024-10924 that bypasses Two-Factor Authentication in the Really Simple SSL WordPress plugin, enabling unauthorized…
 murataydemir/cve-2020-6287
[CVE-2020-6287] SAP NetWeaver AS JAVA (LM Configuration Wizard) Authentication Bypass (Create Simple & Administrator Java User)
 nxploited/cve-2025-49901
WordPress Simple Link Directory Plugin < 14.8.1 is vulnerable to a high priority Broken Authentication
 yen223/hotpot
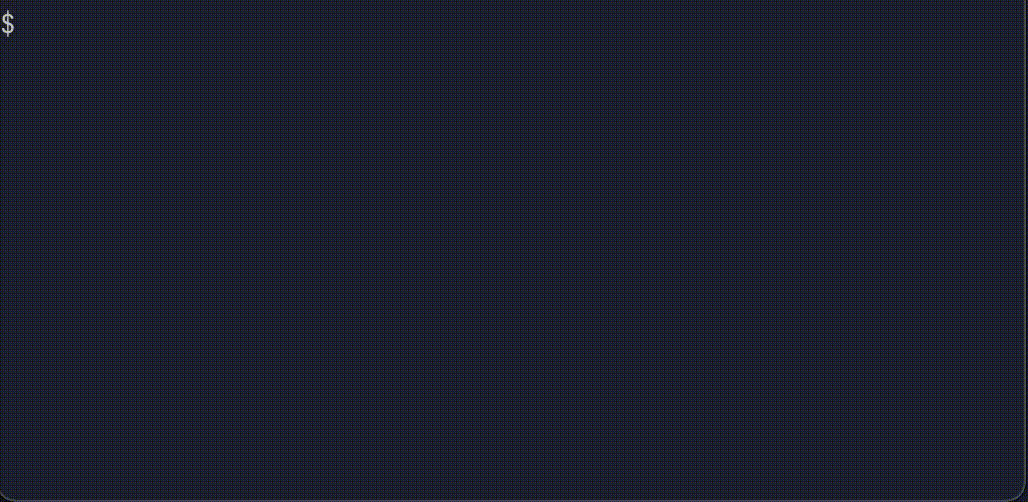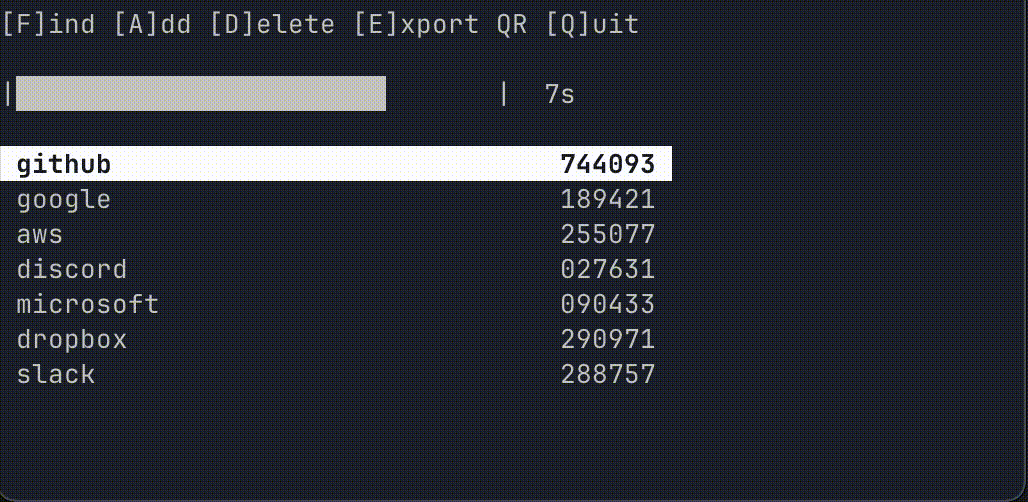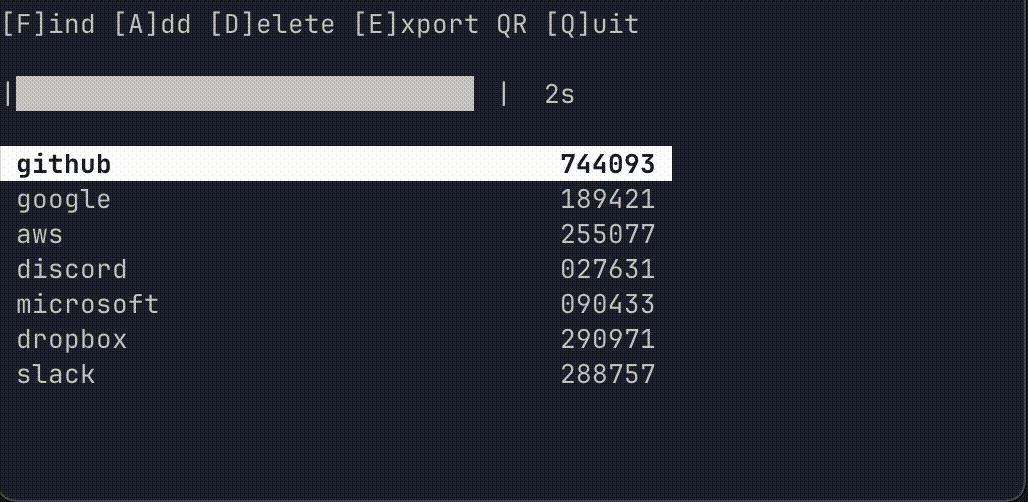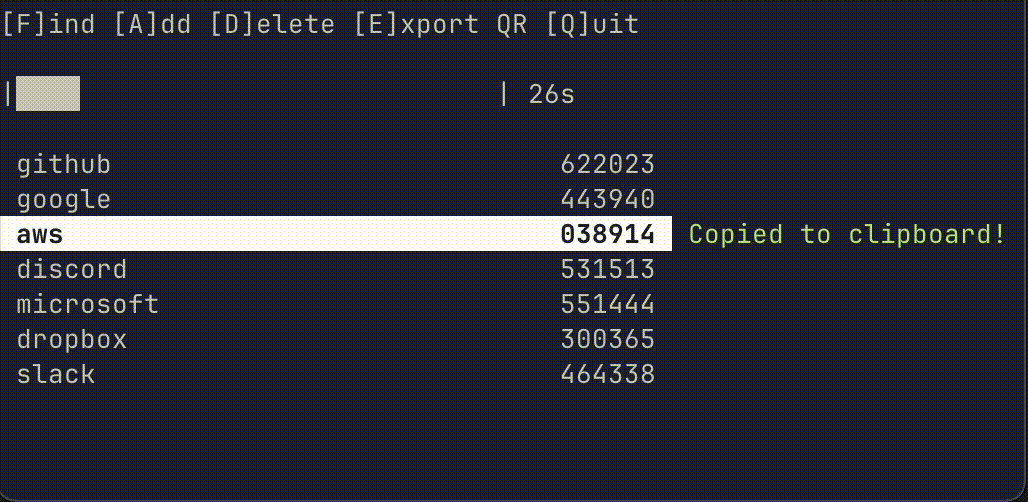
A simple and secure command-line tool for managing TOTP-based two-factor authentication codes.
 h8su/wordpress-cve-2024-10924-exploit
A Proof-of-Concept (PoC) exploit for CVE-2024-10924, a vulnerability in the Really Simple SSL WordPress plugin that allows bypassing two-factor…
 kazuya256/next-js-auth-bypass
🔓 Next.js Auth Bypass Demo - Educational application demonstrating CVE-2025-29927 middleware authentication bypass vulnerability . ⚠️ For…
 blipzip/cve-2022-31692
A project demonstrating an app that is vulnerable to Spring Security authorization bypass CVE-2022-31692
 alash3al/wp-allowed-hosts
a plugin that protects your wp site from the CVE-2017-8295 vulnerability
 soledad208/cve-2018-10933
CVE-2018-10933 very simple POC
 izxci/cve-2026-7459
Exploit for CVE-2026-7459 targeting Simple History plugin missing authorization vulnerability, enabling unauthenticated account takeover in WordPress…