
KeycloakESC
 secfathy/keycloakesc
Reproducible Docker lab + PoC: Keycloak manage-users -> realm-admin escalation via composite roles (CVE-2026-94000 variant). Validated on 26.8.1.
authentication-authorizationexploitationidentity-access-management+5
secfathy/keycloakescReproducible Docker lab + PoC: Keycloak manage-users -> realm-admin escalation via composite roles (CVE-2026-94000 variant). Validated on 26.8.1.
 abraxas/keycloak-manage-users-composite
Keycloak 26.8.1 Medium 6.6 Remote authenticated auth leftover. A help-desk admin with manage-users can pin a pre-built composite of manage-realm onto…
 ritwick7/sudostamp
Approve sudo on a Linux workstation with a fingerprint on your Android phone. LAN only; the ECDSA key never leaves the phone's TEE and speaks the…
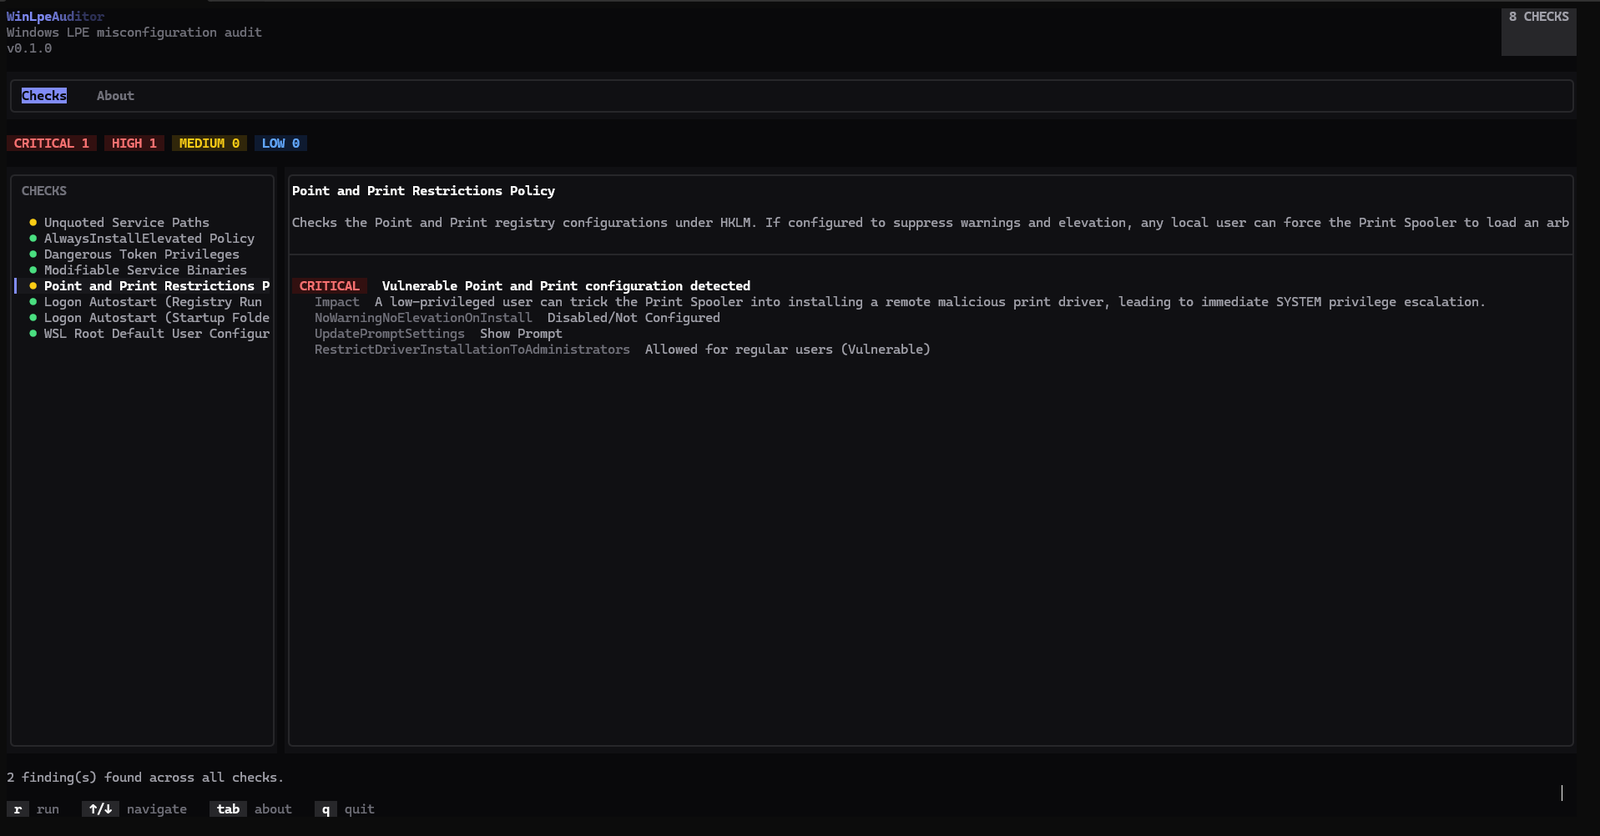 0xby7eme/windows-lpe-auditor
A small Windows local-privilege-escalation (LPE) misconfiguration auditor with a terminal UI, built with C++20 and FTXUI
 abraxas/superset-g3-v0-import-sql-plant
Proof-of-concept lab for an Apache Superset 6.1.0 authorization flaw where a Gamma dashboard editor plants dataset SQL via unversioned v0 dashboard…
 abraxas/openmeetings-soap-user-rights
Apache OpenMeetings 9.1.0 - High - Remote - Privilege leftover - SOAP POST /user copies UserDTO.rights including ADMIN
 abraxas/openmeetings-stale-install-admin
Apache OpenMeetings 9.1.0 - High - Remote - Privilege leftover - stale /install wizard inserts second ADMIN
 abraxas/pfsense-ldap-name-collision
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Privilege leftover - LDAP admin name
 abraxas/opnsense-uidfield-system-uid0
OPNsense 26.7.6 - High - Remote - Privilege leftover - UidField uid 0
 abraxas/nextcloud-ldap-put-isadmin
Nextcloud 35.0.0 — delegated Users admin can PUT-edit an LDAP-promoted admin that PATCH correctly refuses
 abraxas/nextcloud-webhook-tokenneeded
Nextcloud 35.0.0 — delegated Webhooks admin can mint a 1h admin app password via webhook update tokenNeeded
 abraxas/mysql-set-role-leftover
MySQL Community Server 26.7.0 - High - SET ROLE ALL EXCEPT leftover FILE - mysqld UID write
 abraxas/sqlite-fj-using-auth
SQLite 3.53.4 - High - Local - Privilege leftover - FULL JOIN USING skips sqlite3AuthRead
 abraxas/grafana-signup-invite-join
Grafana OSS 13.2.3 - High - Remote - Invite join - SignUpStep2 joins pending org invites without the code
 facebookincubator/bpfjailer
eBPF LSM based Mandatory Access Control and jailer
 hakaioffsec/cve-2026-16764
Python exploit for CVE-2026-16764, a privilege escalation in OWASP DefectDojo where an is_staff REST API bypass lets a low-privileged user gain…
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
 0xgh057r3c0n/cve-2026-41940
cPanel & WHM - Authentication Bypass via Session-File CRLF Injection