

work1-secure-api
 ght657/work1-secure-api
HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
api-securityauthentication-authorizationdevsecops+7
ght657/work1-secure-apiHDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
 peach-research-lab/authorizationbench
[🎖️ Honorable Mention in HAIPS @COLM'26] The first benchmark to evaluate how well do LLM agents act in alignment with their assigned authorization…
 edtrackai/nextjs-supabase-stripe-security-checker
Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…
 abraxas/opnsense-uidfield-system-uid0
OPNsense 26.7.6 - High - Remote - Privilege leftover - UidField uid 0
 zentinelproxy/zentinel
A security-first reverse proxy built to guard the free web.
 abraxas/gitea-public-only-pat-org
Proof-of-concept lab for a Gitea authorization bypass where a public-only PAT with write:organization creates a private organization via POST…
 abraxas/sqlite-fj-using-auth
SQLite 3.53.4 - High - Local - Privilege leftover - FULL JOIN USING skips sqlite3AuthRead
 abraxas/proftpd-sftp-copy-file-write
ProFTPD 1.3.9d - High - Remote - Privilege leftover / File write - SFTP copy-file skips dest WRITE
 zhengxr930/apex_official
Defender framework for LLM agent security that compiles task contracts, validates capability manifests, and checks effects via PLANT/WRAP proof…
 7acini/cve-2026-102261
Non-destructive Go verifier that checks whether a Camaleon CMS instance applies the authorization fix for CVE-2026-102261 in the media crop endpoint.
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 sag-asab/cve-2026-19598
Custom Content Types and Fields plugin for WordPress
 huzjie/aegisagent
Runtime security gateway for AI agents: cryptographically attests tool calls, enforces policies, sandboxes execution, and logs tamper-evident audit…
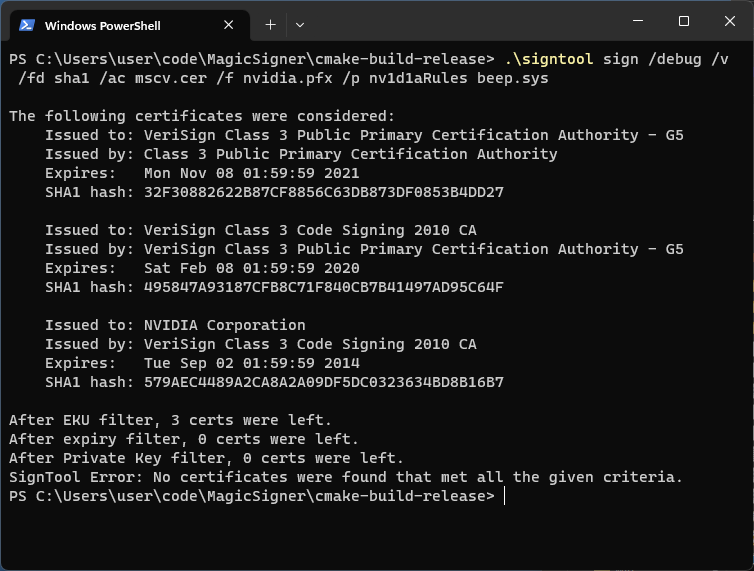 namazso/magicsigner
Signtool for expired certificates
 eastarctica/cve-2026-43813
CVE-2026-43813: CloudAttestation enforceEnvironment bypass
 mr-zapi/cve-2024-54085
Just poc for CVE 2024-54085
 razureink/cve-2026-41940-cpanel_authbypass_reproduction
CVE Reproduction: cve-2026-41940-cpanel_authbypass_reproduction
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.