

work1-secure-api
 ght657/work1-secure-api
HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
api-securityauthentication-authorizationdevsecops+7
ght657/work1-secure-apiHDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
 xhyumiracle/sudp
Secret-Use Delegation Protocol — protocol-level secret use for agentic systems
 saml-toolkits/ruby-saml
Ruby library implementing the SAML Service Provider side of SSO, handling authn requests, response validation, XML signature checks, and IdP metadata…
 andresriancho/enumerate-iam
Enumerate the permissions associated with AWS credential set
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
 philippeabraxas-jpg/tbp-network
Theory and implemantation of the TBP protocol to secure networked AI in small to open web networks
 isaca0315/cve-2026-65013-bola-idor
Reproducible BOLA/IDOR PoC against Onlook's tRPC API (CVE-2026-65013), with a 12-step exploit chain, vulnerable and patched Docker targets, and…
 rosemary1337/cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940, an unauthenticated authentication bypass in cPanel/WHM using CRLF injection to leak security tokens and…
 aksalsalimi/cve-2026-26418
Documentation of CVE-2026-26418, a missing authentication and authorization vulnerability in TCS Cognix Recon Client v3.0 Web API, including affected…
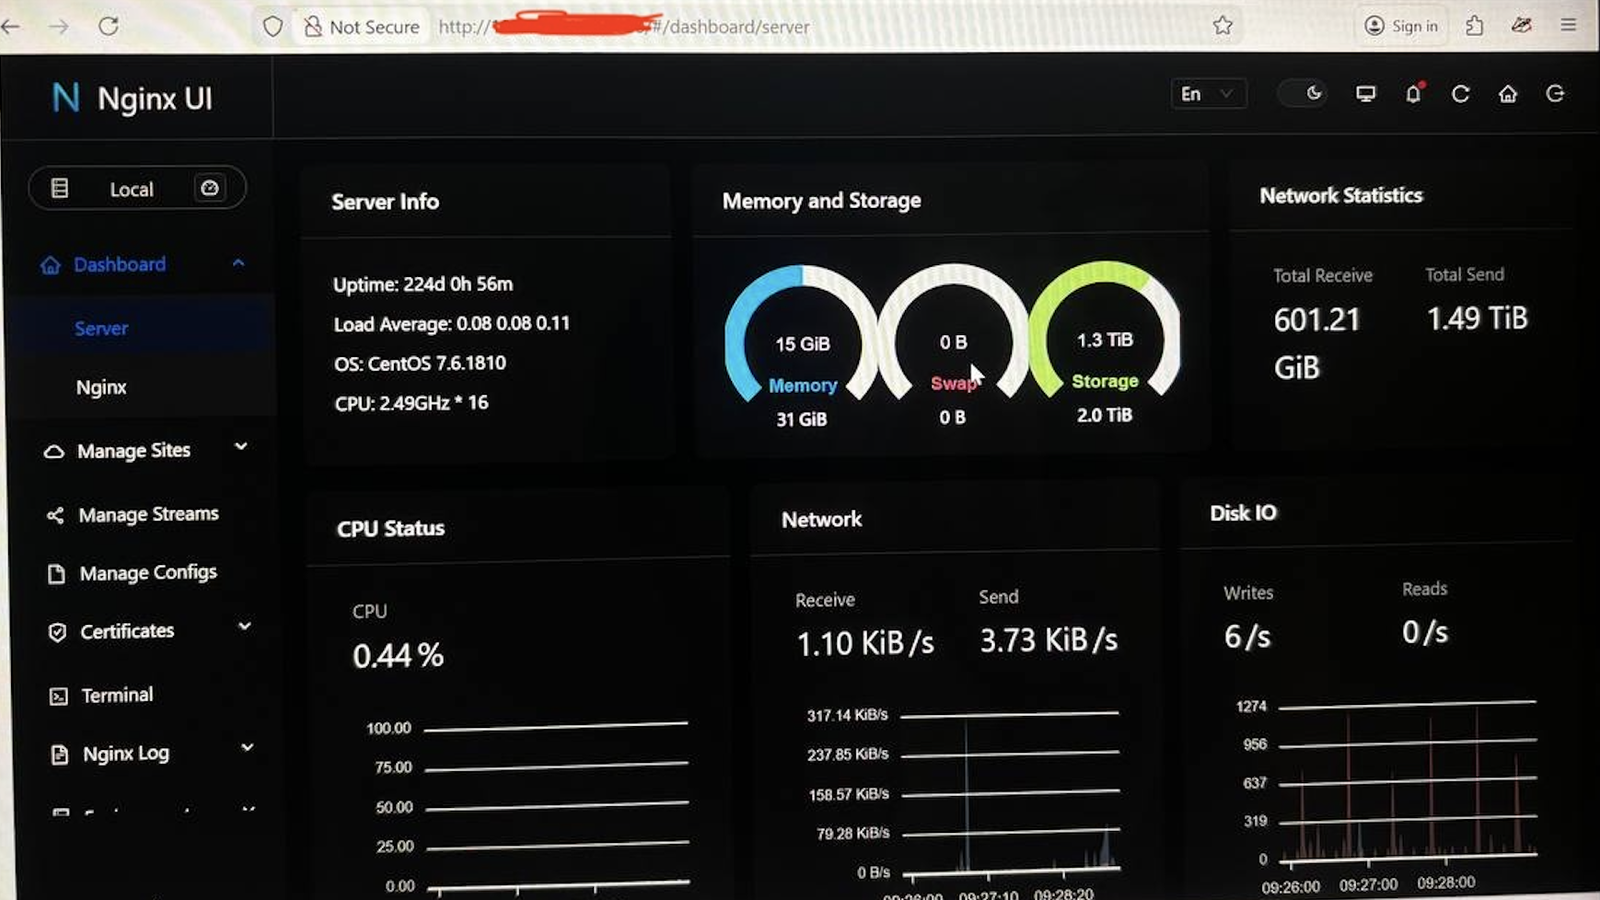 skynoxk/cve-2026-27944
Automated exploit for CVE-2026-27944 in Nginx UI: downloads and decrypts backups, extracts secrets, and creates rogue admin accounts for full…
 simoesctt/sctt-2026-33-0004-forticloud-sso-identity-singularity
While Fortinet's January 27, 2026 mitigation for **CVE-2026-24858** focuses on blocking specific accounts like `[email protected]`, it fails to…
 rohitberiwala/cve-2026-28372-telnetd-privilege-escalation
This Proof‑of‑Concept demonstrates a **Local Privilege Escalation** vulnerability in GNU inetutils `telnetd`. `telnetd` improperly passes…
 immersive-labs-sec/cve-2021-32648
Proof-of-concept exploit for OctoberCMS authentication bypass (CVE-2021-32648), demonstrating unauthorized access and providing a working PoC for…
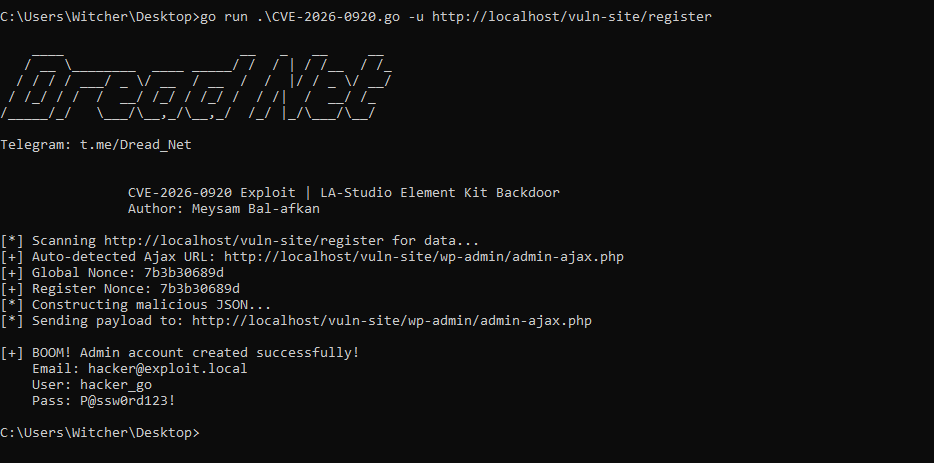 galaxy-sc/cve-2026-0920-wordpress-la-studio-exploit
Proof-of-concept exploit for CVE-2026-0920 in LA-Studio Element Kit, enabling unauthenticated privilege escalation to administrator via crafted AJAX…
 zedxod/cve-2026-41940-poc
Proof-of-concept exploit for CVE-2026-41940, demonstrating authentication bypass in cPanel/WHM via CRLF injection and session poisoning to gain…
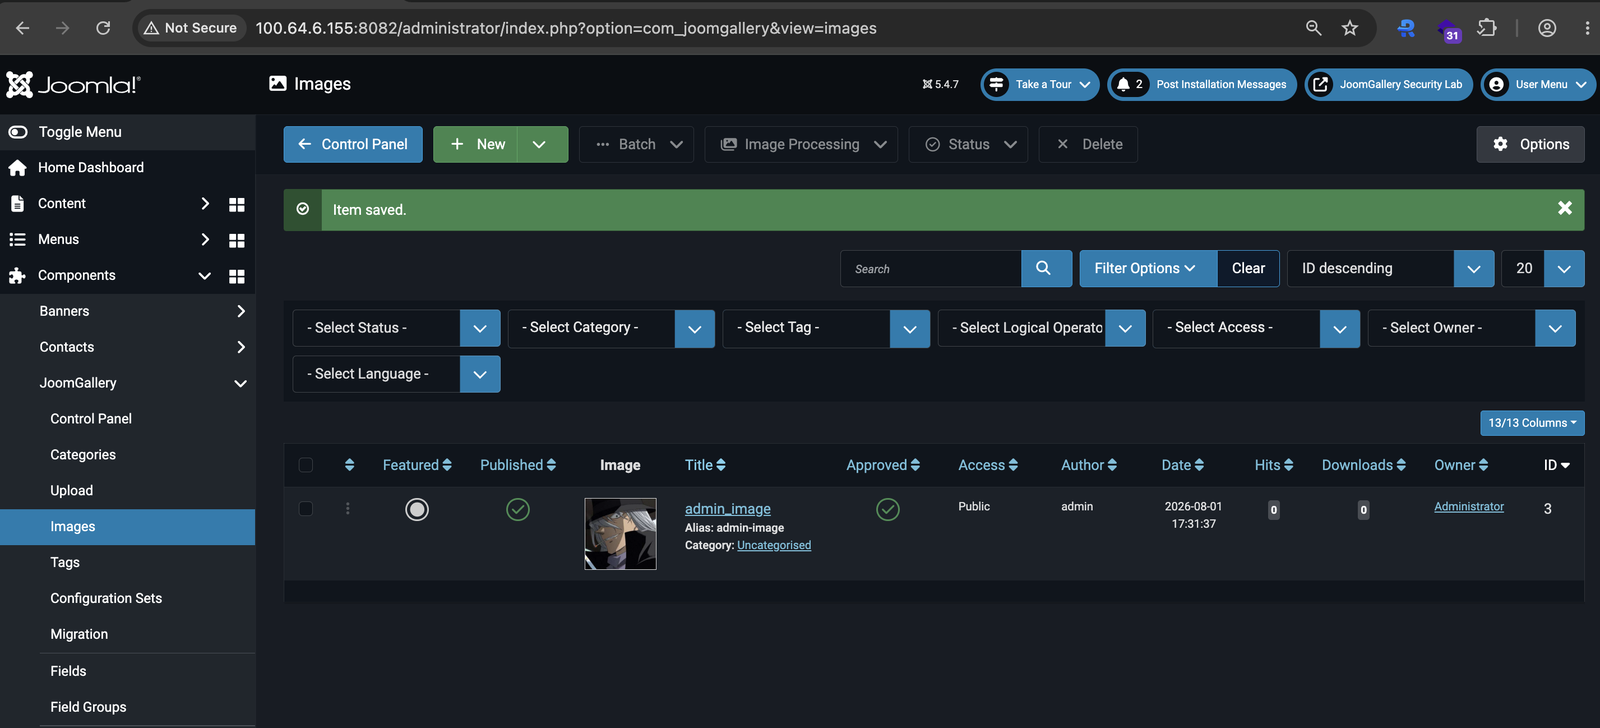 toanln-cov/cve-2026-66917
IDOR + Stored XSS via Broken Object-Level Authorization in JoomGallery
 nastar-id/cve-2026-18315-poc
Proof-of-concept for CVE-2026-18315 (TrueBooker WordPress Plugin): Unauthenticated Authorization Bypass Through User-Controlled Key to Account…
 kanidm/kanidm
Self-hosted identity management platform providing WebAuthn passkeys, OAuth2/OIDC SSO, SSH key distribution, RADIUS and LDAP integration for modern…