Responsible-Alliance-Protocol

Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…

Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…

cPanel & WHM - Authentication Bypass via Session-File CRLF Injection

PoC for CVE-2026-27912 - Windows Kerberos Elevation of Privilege (ResetNightmare). Unauthorized password reset via Kerberos flaw. For security…

Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…

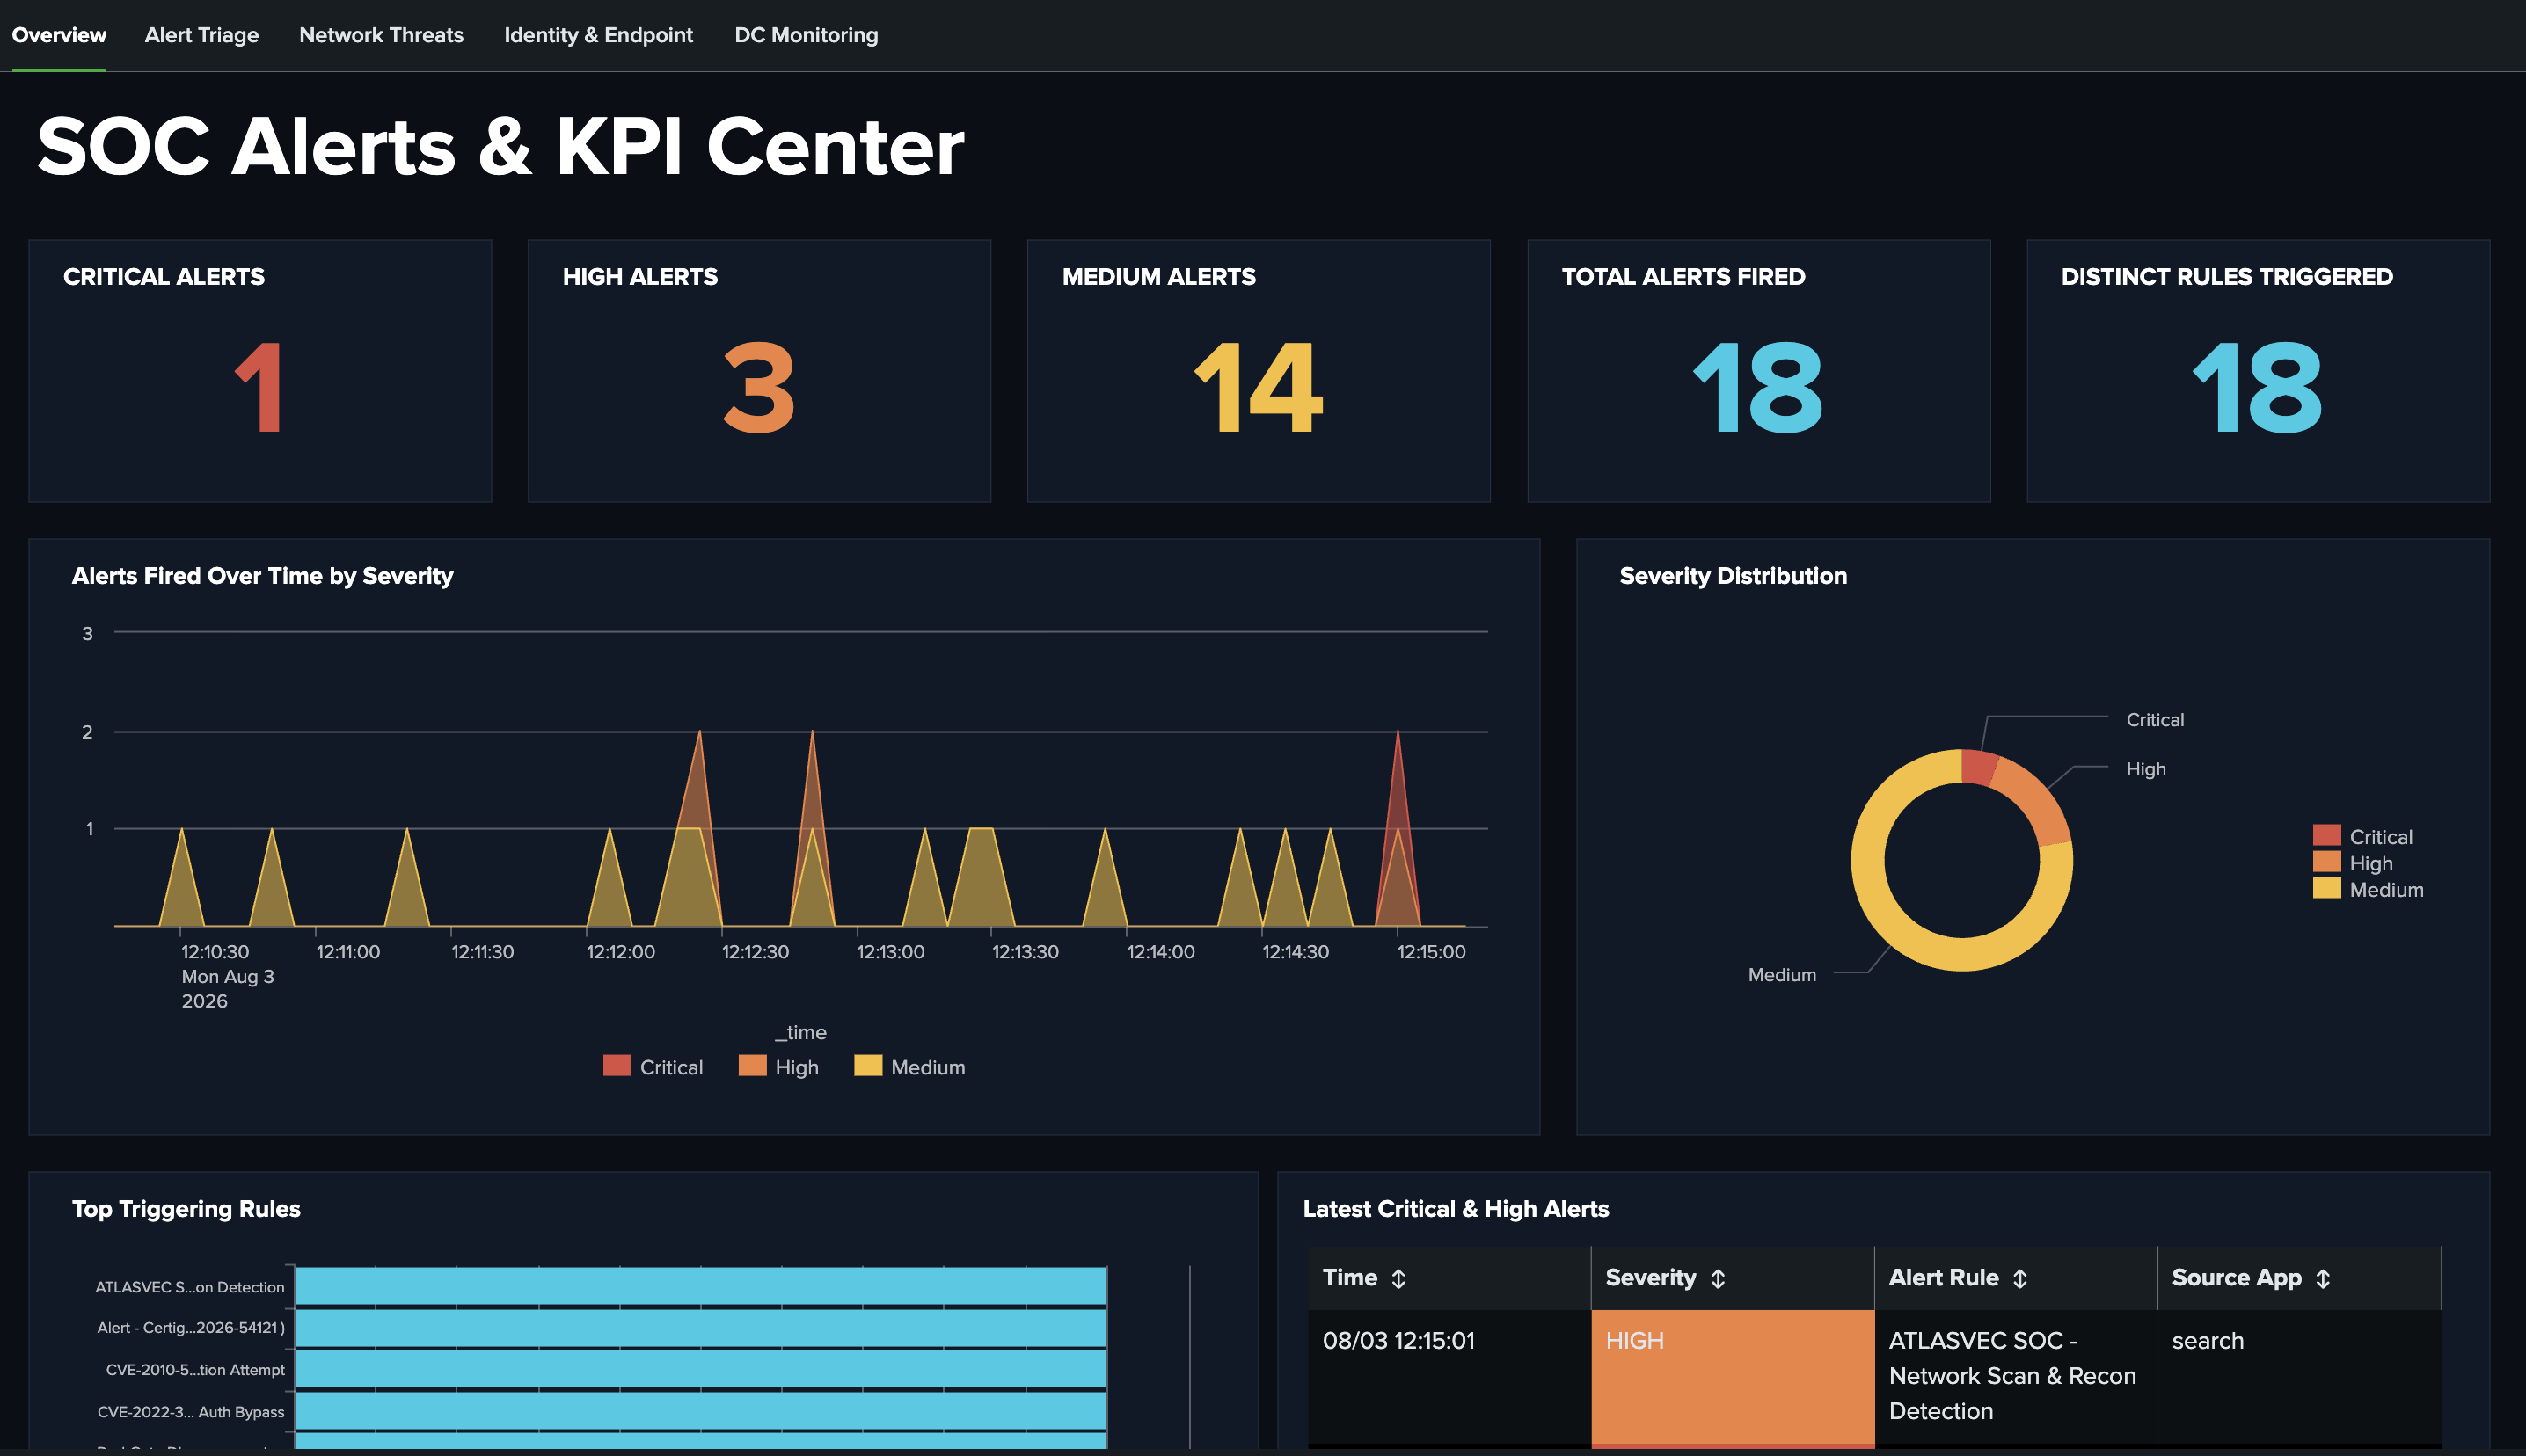
Splunk detection writeup for CVE-2026-54121 (CertiGhost): AD CS certificate chase abuse leading to full domain compromise. Lab-validated detection,…

Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…

Shadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.

CVE-2026-43813: CloudAttestation enforceEnvironment bypass

SAML Single Sign On <= 5.4.4 - Unauthenticated Authentication Bypass via SAMLResponse Parameter

👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…

Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.

Detailed technical analysis of CVE-2026-47777, a high-severity authorization bypass in Mastodon's Featured Collections federation pipeline, including…

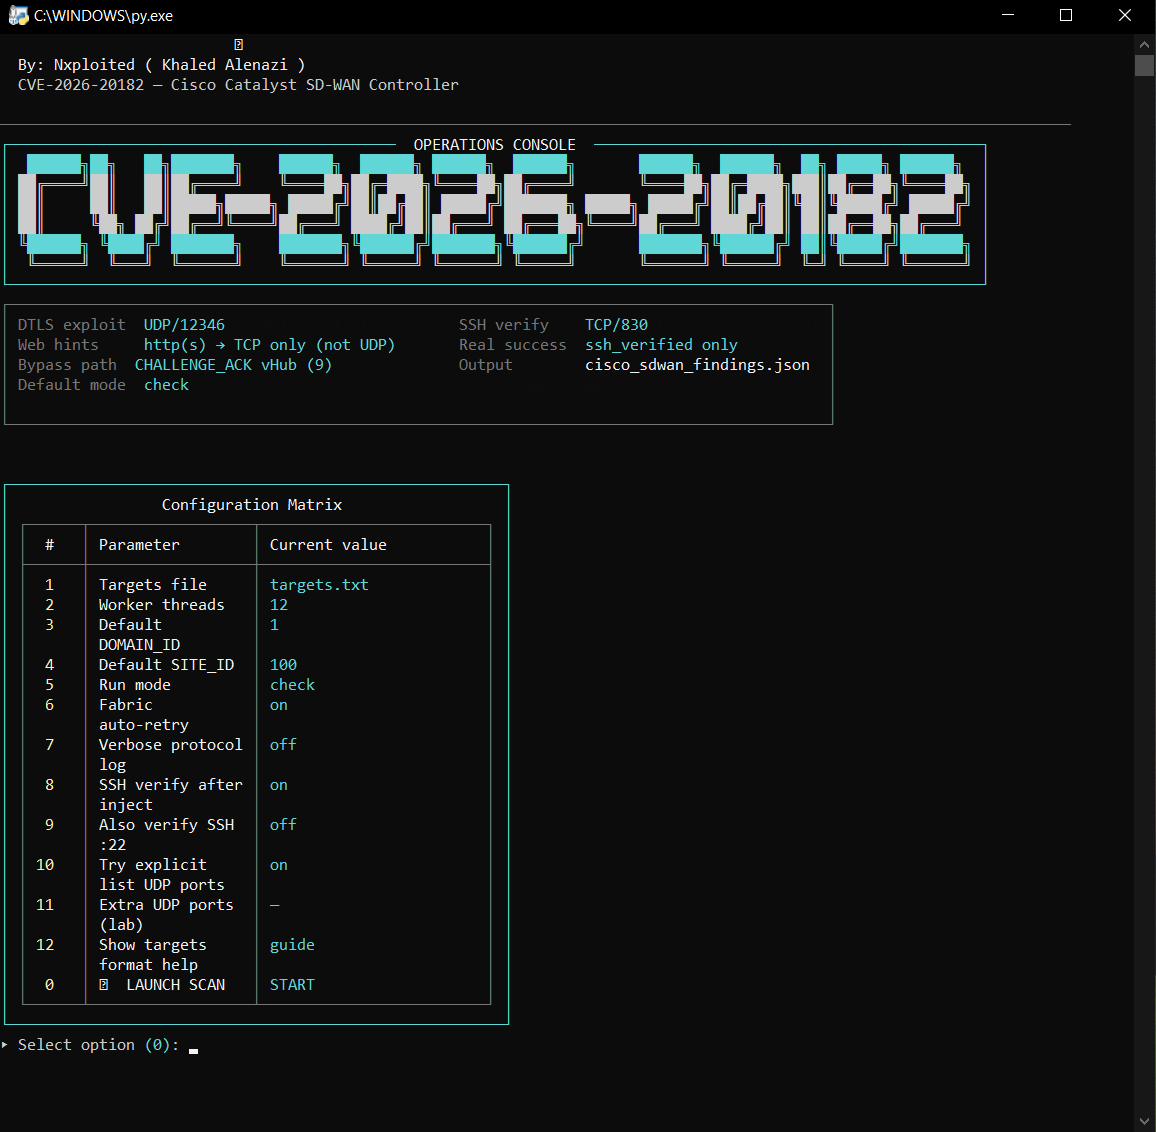
Cisco Catalyst SD-WAN Peering Authentication Bypass

Python script to detect CVE-2023-3128 authentication bypass in Grafana via Azure AD email claim validation. Checks Azure AD SSO configuration and…

This repository consists of the python exploit for CVE-2022-1388 (F5's BIG-IP Authentication Bypass to RCE)

Fix without disabling Print Spooler

WP Maps Pro <= 6.1.0 - Unauthenticated Privilege Escalation via Administrator Account Creation to wpgmp_temp_access_ajax AJAX Action

WordPress Simple Link Directory Plugin < 14.8.1 is vulnerable to a high priority Broken Authentication