
vaultwarden
 dani-garcia/vaultwarden
Unofficial Bitwarden compatible server written in Rust, formerly known as bitwarden_rs
authenticationauthentication-authorizationcontainer-security+5
69.9k
dani-garcia/vaultwardenUnofficial Bitwarden compatible server written in Rust, formerly known as bitwarden_rs
 az0x7/vulnerability-checklist
Curated collection of web and API vulnerability checklists covering XSS, SQLi, CSRF, IDOR, authentication bypass, file upload, and bug bounty testing…
 ght657/work1-secure-api
HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
 abraxas/ats-realip-plugin-acl
Apache Traffic Server 10.2.0 - High - Remote - Privilege leftover - realip PLUGIN ACL fail-open
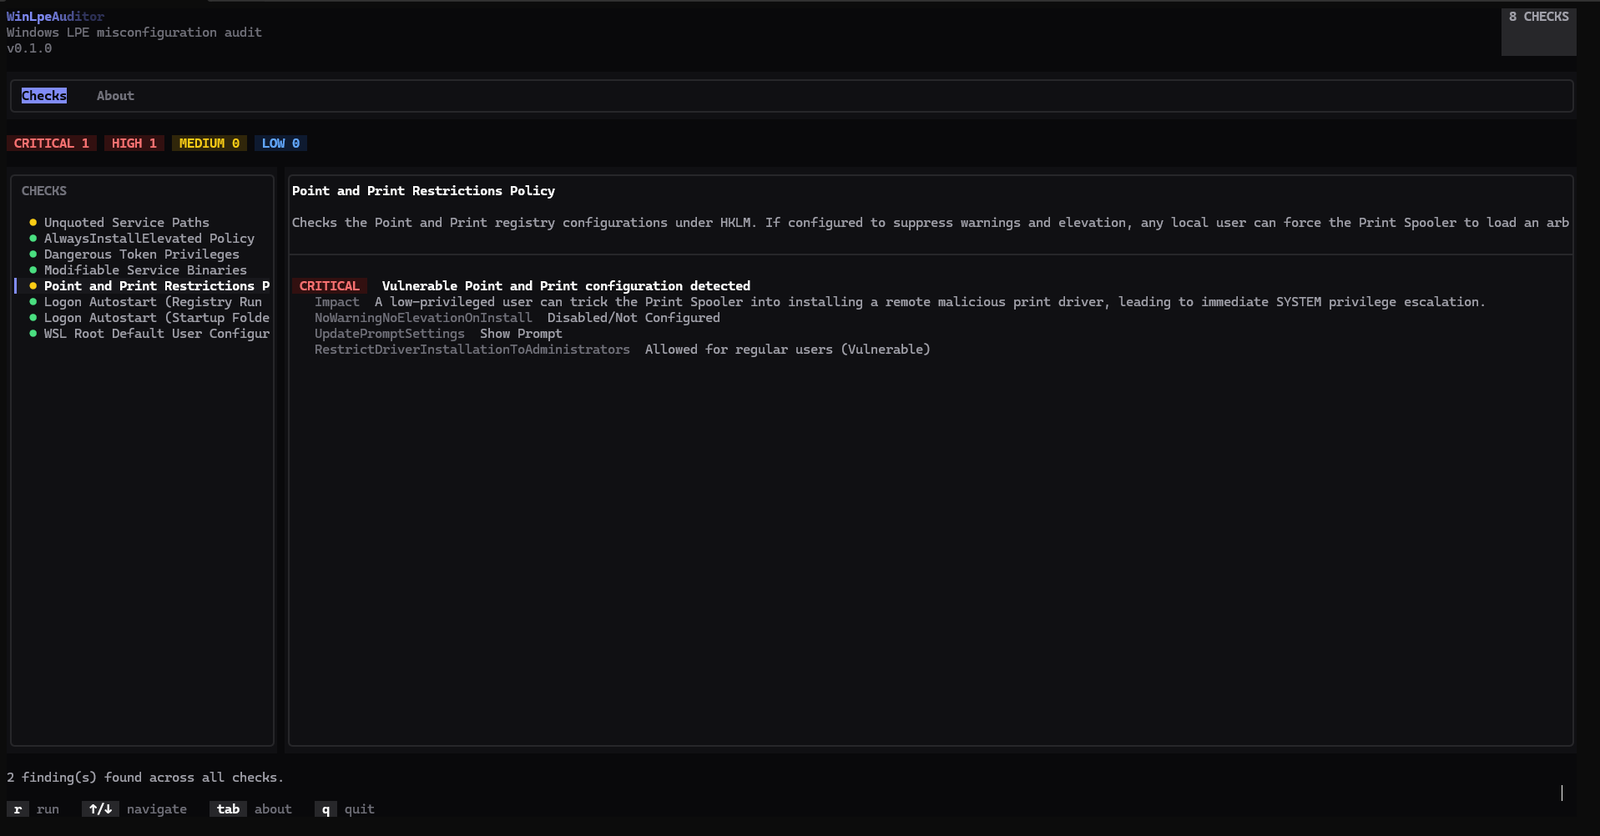 0xby7eme/windows-lpe-auditor
A small Windows local-privilege-escalation (LPE) misconfiguration auditor with a terminal UI, built with C++20 and FTXUI
 xhyumiracle/sudp
Secret-Use Delegation Protocol — protocol-level secret use for agentic systems
 edtrackai/nextjs-supabase-stripe-security-checker
Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…
 oscerd/cve-2026-80343
Runnable proof-of-concept for CVE-2026-80343, a camel-netty-http security-constraint case-sensitivity bypass, with Spring Boot and Quarkus…
 abraxas/pfsense-api-export-key-get
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - GET export-key private keys
 abraxas/pfsense-api-fleet-jwt
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - IDOR - one controller JWT is a fleet token
 zentinelproxy/zentinel
A security-first reverse proxy built to guard the free web.
 abraxas/sqlite-fj-using-auth
SQLite 3.53.4 - High - Local - Privilege leftover - FULL JOIN USING skips sqlite3AuthRead
 abraxas/forgejo-keys-idor
Forgejo 16.0.5 - High - Remote - IDOR - GET /api/v1/user/keys/{id} returns other users SSH and deploy keys
 zhengxr930/apex_official
Defender framework for LLM agent security that compiles task contracts, validates capability manifests, and checks effects via PLANT/WRAP proof…
 facebookincubator/bpfjailer
eBPF LSM based Mandatory Access Control and jailer
 andresriancho/enumerate-iam
Enumerate the permissions associated with AWS credential set
 7acini/cve-2026-102261
Non-destructive Go verifier that checks whether a Camaleon CMS instance applies the authorization fix for CVE-2026-102261 in the media crop endpoint.
 gmh5225/jataayu
LLM-backed AI agent security — inbound injection detection + outbound privacy protection