

OpenShell
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
ai-securityauthentication-authorizationcloud-security+7
21.0k
nvidia/openshellSandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 haidang-infosec/phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…
 openziti/ziti
Zero-trust networking platform that makes services invisible with cryptographic identity, policy-based access, and end-to-end encryption. Replaces…
 tuskira/ai-agent-gateway
Open-source gateway that secures, governs, and observes AI agents' MCP tool calls and LLM traffic, with API-key authentication and an admin console…
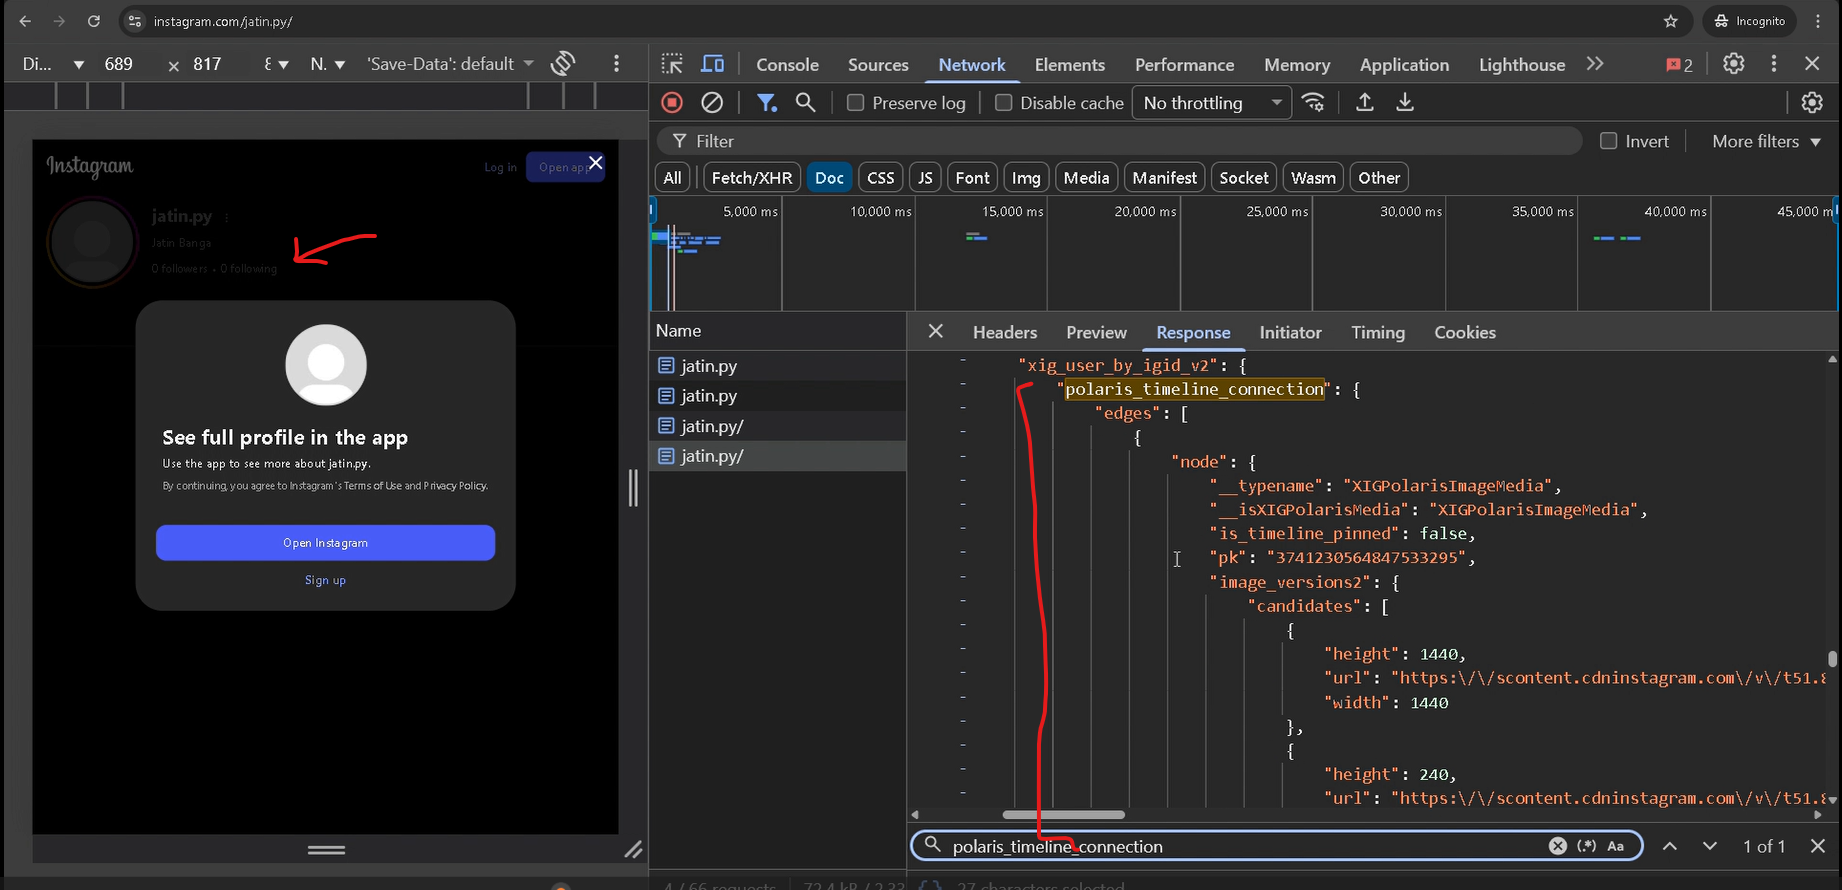 jatin-dot-py/instagram-private-bypass
This repository discloses a server-side authorization bypass in Instagram, which allowed unauthenticated access to private timelines; it seems likely…
 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
 the-infra-company/kcatcher
Catch what's lurking in your Kafka clusters.
 bp2008/dahualoginbypass
Chrome extension that uses vulnerabilities CVE-2021-33044 and CVE-2021-33045 to log in to Dahua cameras without authentication.
 strongswan/strongswan
strongSwan - IPsec-based VPN
 zhengxr930/apex_official
Defender framework for LLM agent security that compiles task contracts, validates capability manifests, and checks effects via PLANT/WRAP proof…
 zentinelproxy/zentinel
A security-first reverse proxy built to guard the free web.
 quarkslab/android-hardware-attestation-demo
An Android HW Attestation demo
 horizon3ai/vcenter_saml_login
A tool to extract the IdP cert from vCenter backups and log in as Administrator
 firezone/firezone
WireGuard-based zero-trust access platform providing secure, peer-to-peer remote access with granular policy controls, SSO authentication, and audit…
 andresriancho/enumerate-iam
Enumerate the permissions associated with AWS credential set
 hughink/cve-2022-40684
PoC and exploit for CVE-2022-40684, an authentication bypass in Fortinet FortiOS, FortiProxy, and FortiSwitchManager management interfaces, enabling…
 exfil0/cve-2024-55591-poc
A comprehensive all-in-one Python-based Proof of Concept script to discover and exploit a critical authentication bypass vulnerability…
 xthalach/cve-2024-11318
This repository details an IDOR vulnerability in AbsysNet 2.3.1, which allows a remote attacker to brute-force session IDs via the /cgi-bin/ocap/…