CVE-2022-40684
PoC and exploit for CVE-2022-40684, an authentication bypass in Fortinet FortiOS, FortiProxy, and FortiSwitchManager management interfaces, enabling…

PoC and exploit for CVE-2022-40684, an authentication bypass in Fortinet FortiOS, FortiProxy, and FortiSwitchManager management interfaces, enabling…

A HTTP credential proxy and vault for AI agents like Claude Code, OpenClaw, Hermes, custom agents + harnesses, and more.

Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100

Native C++ access to Active Directory over ADWS, no .NET, no WCF, no HTTP stack.

Centralized configuration server for distributed systems with HTTP API, encryption/decryption of properties, and support for Git, Vault, JDBC, and…

Squid Web Proxy Cache - Source Code

Python exploit for CVE-2026-41940, a critical CRLF injection in cPanel/WHM cpsrvd that bypasses authentication and 2FA, granting root-level access…

Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.

演示 Next.js 中的 Middleware 授權繞過漏洞 (CVE-2025-29927) 允許未經授權的用戶存取受保護的資訊。

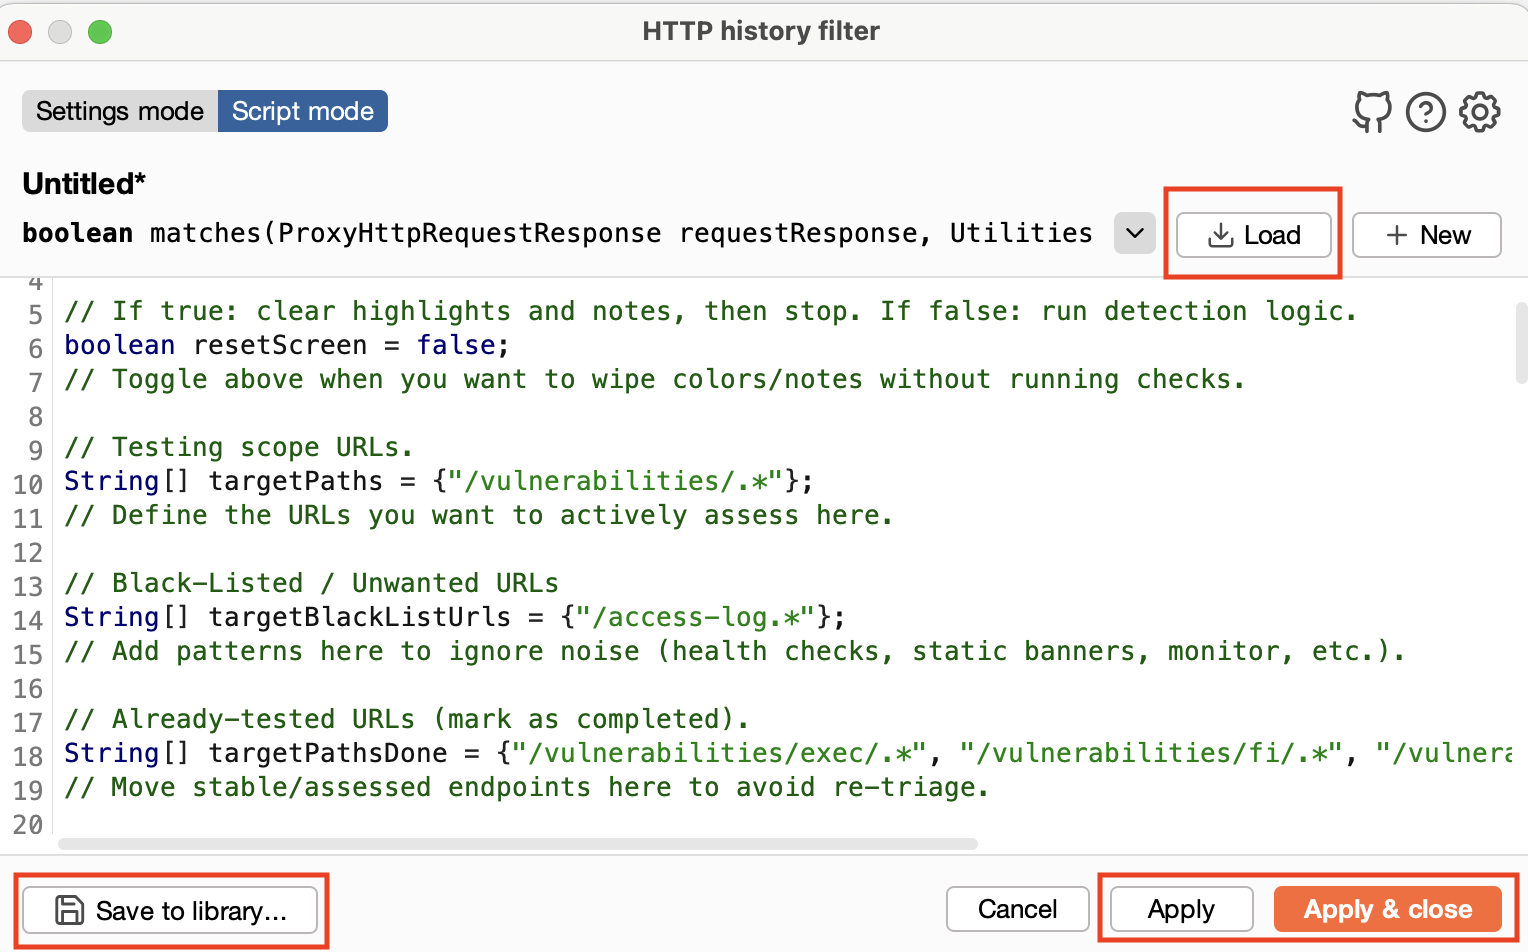
Automated HTTP Request Repeating With Burp Suite

A Burp Suite extension for identifying injection flaws (LFI, RCE, SQLi), authentication/authorization issues, and HTTP 403 access violations. It…

Centralized configuration server for distributed systems with HTTP API, Git-backed storage, property encryption/decryption, and integration with…

Demonstrates an authentication bypass in FortiWeb (CVE-2025-52970) chained with SQL injection to upload a webshell and achieve remote code execution…

Proof-of-concept exploit for CVE-2026-41940, an authentication bypass chain in WHM/cPanel. Multi-threaded scanner that changes root password on…

Silent;Call — Pre-authentication remote root on Cisco CUCM 15.x (CVSS 10.0)

Automated HTTP Request Repeating With Burp Suite

Lab + writeup for CVE-2026-28699: Gitea OAuth2 scope enforcement bypass via HTTP Basic auth

Analysis of two authentication bypass techniques for Apache Shiro (CVE-2020-17523) with a reproducible exploit environment and detailed root cause…