
CVE-2022-1388
 omnigodz/cve-2022-1388
This repository consists of the python exploit for CVE-2022-1388 (F5's BIG-IP Authentication Bypass to RCE)
authentication-authorizationexploitationpenetration-testing+2
omnigodz/cve-2022-1388This repository consists of the python exploit for CVE-2022-1388 (F5's BIG-IP Authentication Bypass to RCE)
 openziti/ziti
Zero-trust networking platform that makes services invisible with cryptographic identity, policy-based access, and end-to-end encryption. Replaces…
 opennhp/opennhp
A lightweight, cryptography-powered, open-source toolkit built to enforce Zero Trust security for infrastructure, applications, and data in the…
 goauthentik/authentik
Provides open-source SSO and identity provider functionality with SAML, OAuth2/OIDC, LDAP, and RADIUS support for centralized authentication,…
 the-infra-company/kcatcher
Catch what's lurking in your Kafka clusters.
 authelia/authelia
The Single Sign-On Multi-Factor portal for web apps. OpenID Certified™ and Post-Quantum Cryptography Ready.
 keycloak/keycloak
Open Source Identity and Access Management For Modern Applications and Services
 dbeaver/dbeaver
Free universal database tool and SQL client
 zitadel/zitadel
Open-source identity and access management platform providing SSO, MFA, passkeys, OIDC, SAML, SCIM, and multi-tenant access control for developers…
 horizon3ai/vcenter_saml_login
A tool to extract the IdP cert from vCenter backups and log in as Administrator
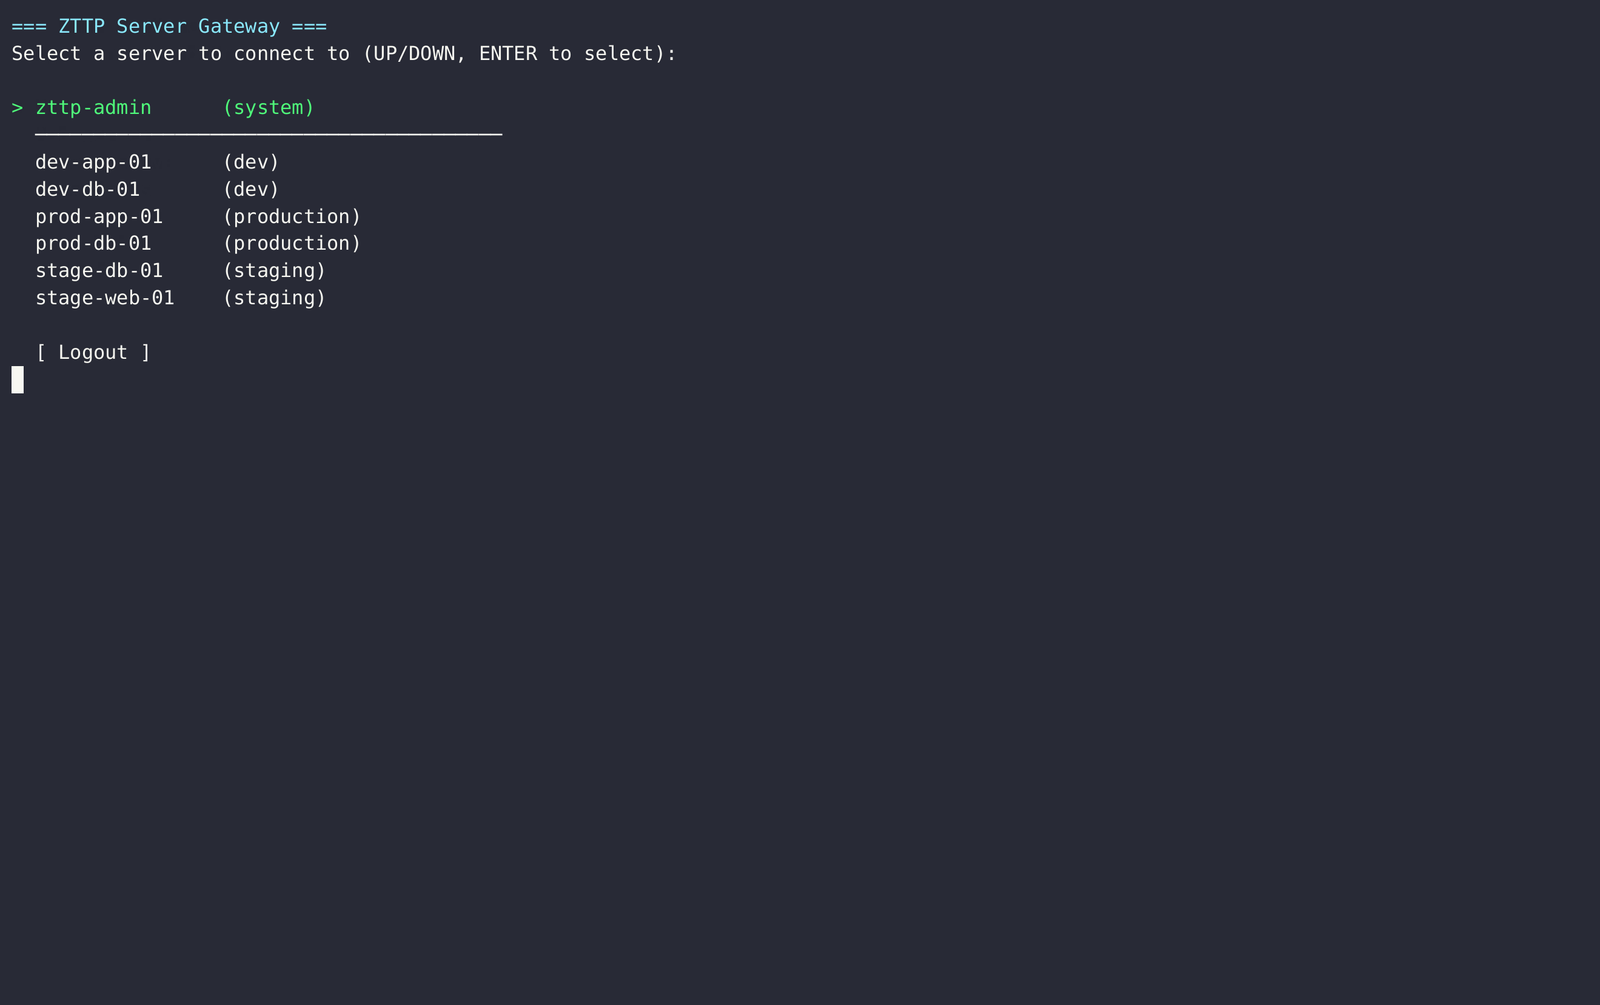
 nihal799/zttp
Zero-trust SSH bastion proxy with Vault-backed key management, RBAC policy enforcement, full session recording, and admin TUI for auditable access to…
 freerdp/freerdp
FreeRDP is a free remote desktop protocol library and clients
 nearai/ironclaw
Secure, private AI agent operating system with local encrypted storage, OAuth/SSO authentication, policy-based access control, and extensible…
 ory/oathkeeper
A cloud native Identity & Access Proxy / API (IAP) and Access Control Decision API that authenticates, authorizes, and mutates incoming HTTP(s)…
 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
 openvpn/openvpn
Secure tunneling daemon implementing VPN protocols with TLS encryption, certificate authentication, and routing/firewall configuration for private…
 themehackers/cve-2025-29972
CVE-2025-29927 is a critical security vulnerability affecting Next.js, a popular React framework for building full-stack web applications. This flaw…
 xthalach/cve-2024-11318
This repository details an IDOR vulnerability in AbsysNet 2.3.1, which allows a remote attacker to brute-force session IDs via the /cgi-bin/ocap/…