
CVE-2024-29849
 sinsinology/cve-2024-29849
Veeam Backup Enterprise Manager Authentication Bypass (CVE-2024-29849)
authentication-authorizationexploitationpenetration-testing+3
sinsinology/cve-2024-29849Veeam Backup Enterprise Manager Authentication Bypass (CVE-2024-29849)
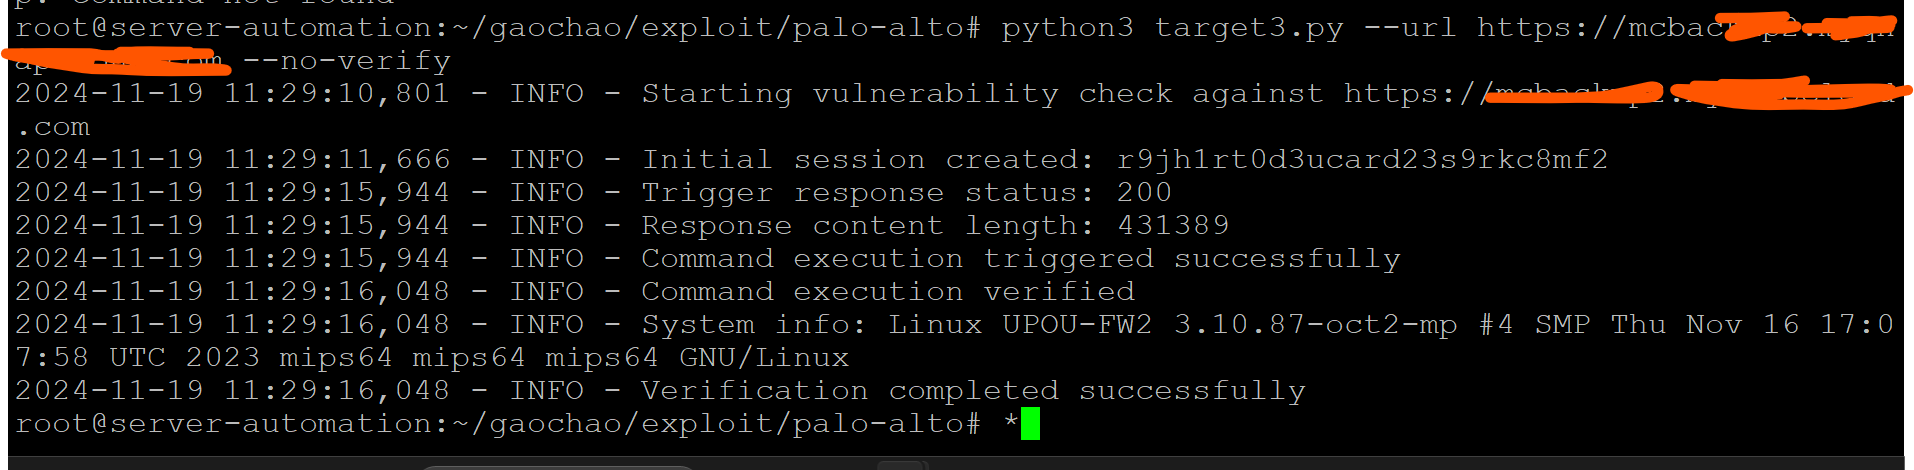 sachinart/cve-2024-0012-poc
CVE-2024-0012 PAN-OS: Authentication Bypass in the Management Web Interface (PAN-SA-2024-0015) RCE POC
 orangejuicehu/cve-2024-41958-poc
This is a small proof of concept for CVE-2024-41958
 geniuszly/cve-2024-27198
is a PoC tool that targets a vulnerability in the TeamCity server (CVE-2024-27198)
 synacktiv/cve-2024-45409
Ruby-SAML / GitLab Authentication Bypass (CVE-2024-45409) exploit
 watchtowrlabs/watchtowr-vs-progress-moveit_cve-2024-5806
Exploit for the CVE-2024-5806
 sariamubeen/cve-2024-10924
Python exploit for CVE-2024-10924 that bypasses Two-Factor Authentication in the Really Simple SSL WordPress plugin, enabling unauthorized…
 tam-k592/cve-2024-52316
CVE-2024-52316 - Apache Tomcat Authentication Bypass Vulnerability
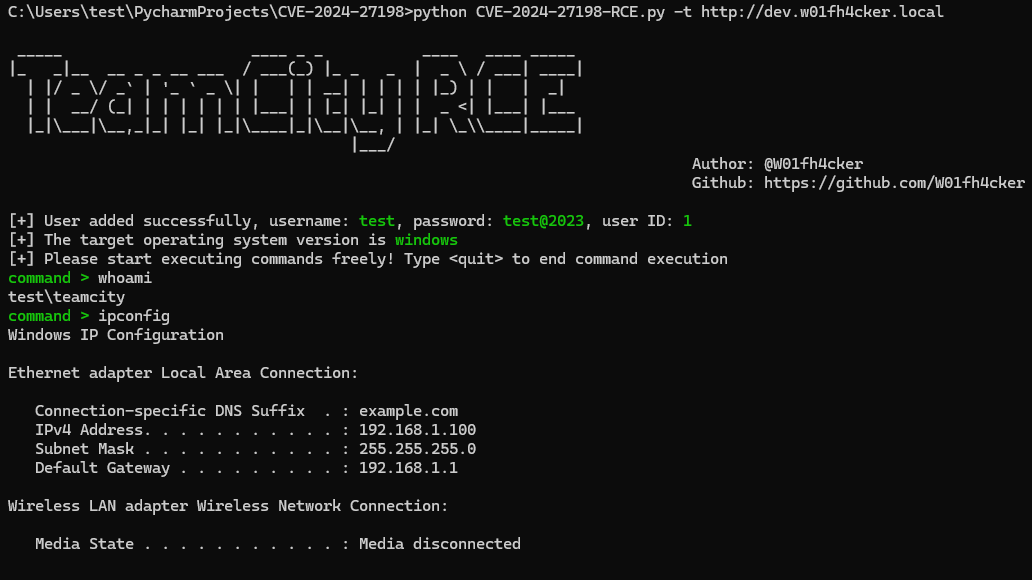 passwa11/cve-2024-27198-rce
Exploit for JetBrains TeamCity authentication bypass (CVE-2024-27198/27199) enabling remote code execution. Includes dork queries for asset discovery…
 rampantspark/cve-2024-27198
A PoC for CVE-2024-27198 written in Go
 thetrueartist/abo.cms-exploit-unauthenticated-login-bypass-cve-2024-25227
SQL injection exploit for ABO.CMS 5.8 that bypasses authentication via the tb_login parameter, granting unauthenticated admin panel access. Includes…
 razureink/cve-2024-0012_9474-panos_authbypass_reproduction
CVE Reproduction: cve-2024-0012_9474-panos_authbypass_reproduction
 horizon3ai/cve-2024-1403
Progress OpenEdge Authentication Bypass
 masa42/cve-2024-38821-poc
Proof-of-concept exploit for CVE-2024-38821, demonstrating authentication bypass in Spring Framework via path traversal to access restricted…
 absholi7ly/poc-cve-2024-32962-xml-crypto
Simulates an attack exploiting CVE-2024-32962 to forge SAML messages and gain unauthorized permissions, demonstrating the vulnerability's impact.
 gr-1m/cve-2024-0012-poc
CVE-2024-0012是Palo Alto Networks PAN-OS软件中的一个身份验证绕过漏洞。该漏洞允许未经身份验证的攻击者通过网络访问管理Web界面,获取PAN-OS管理员权限,从而执行管理操作、篡改配置,或利用其他需要身份验证的特权提升漏洞(如CVE-2024-9474)
 yoryio/cve-2024-27198
Exploit for CVE-2024-27198 - TeamCity Server
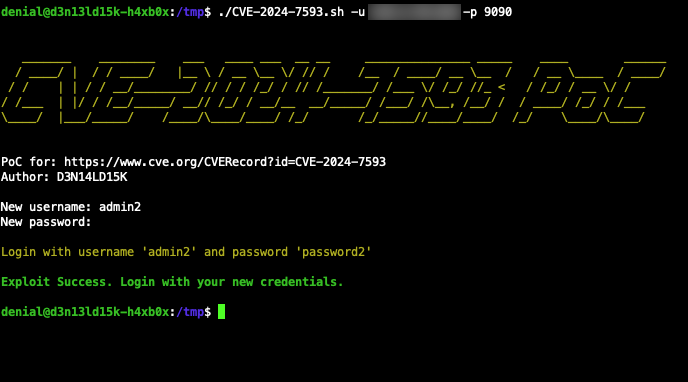 d3n14ld15k/cve-2024-7593_poc_exploit
CVE-2024-7593 Ivanti Virtual Traffic Manager 22.2R1 / 22.7R2 Admin Panel Authentication Bypass PoC [EXPLOIT]