
ironclaw
 nearai/ironclaw
Secure, private AI agent operating system with local encrypted storage, OAuth/SSO authentication, policy-based access control, and extensible…
ai-securityauthentication-authorizationcloud-security+6
12.6k
nearai/ironclawSecure, private AI agent operating system with local encrypted storage, OAuth/SSO authentication, policy-based access control, and extensible…
 themehackers/cve-2025-29972
CVE-2025-29927 is a critical security vulnerability affecting Next.js, a popular React framework for building full-stack web applications. This flaw…
 openpcc/openpcc
An open-source framework for verifiably private AI inference
 better-auth/better-auth
The most comprehensive authentication framework
 symfony/symfony
The Symfony PHP framework
 tomasz-lisowski/swicc
A framework for creating smart cards (ICC-based cards with contacts).
 wso2/carbon-identity-framework
Core framework for identity and access management, providing authentication, authorization, and identity governance capabilities for enterprise…
 secureworks/whiskeysamlandfriends
Python-based framework for generating Golden SAML tokens, Kerberos tickets, and Azure Access Tokens to exploit federated identity systems and…
 tc4dy/cve-2026-54121-poc-exploit
👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…

 kit-lang/packages/kit-policy
A flexible, composable authorization framework for Kit (inspired by Action Policy)
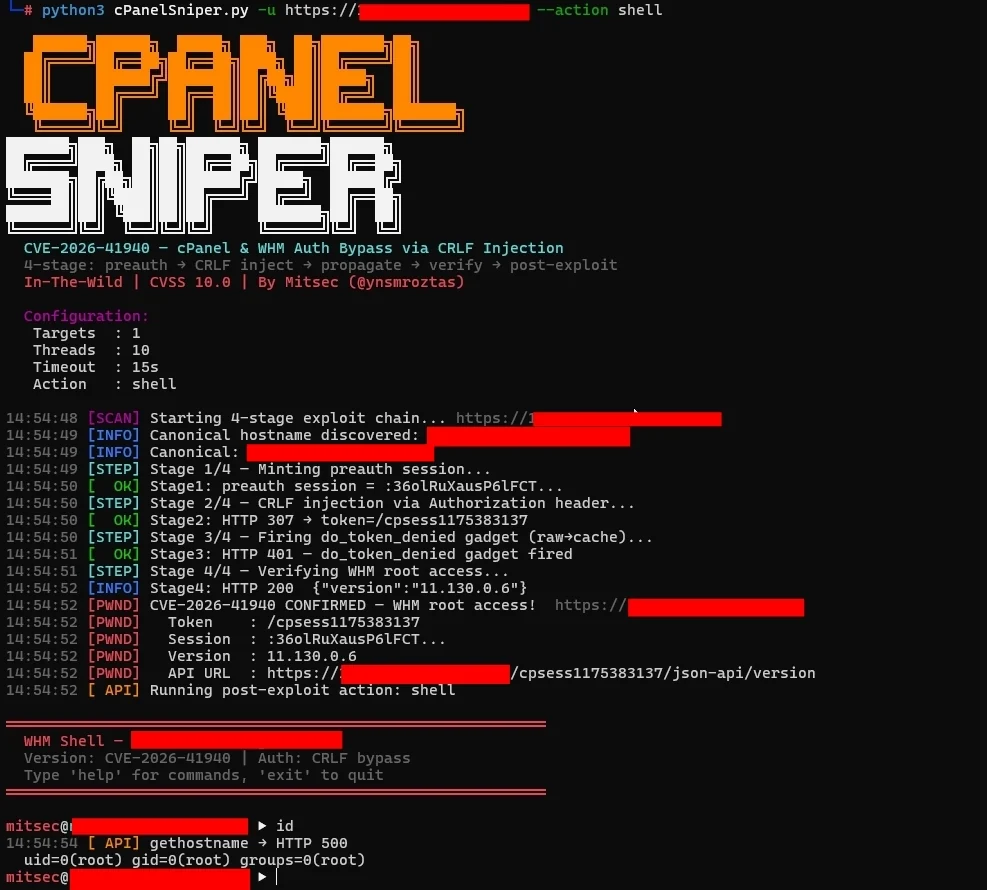 44pie/cpsniper
cPanelSniper STABLE - CVE-2026-41940 optimized for 10M+ targets
 raghvendra1207/cve-2022-22978
Proof-of-concept demonstrating authorization bypass in Spring Security's RegexRequestMatcher (CVE-2022-22978) using CRLF injection, with analysis and…
 shoucheng3/asf__cxf_cve-2016-6812_3-0-11
Open-source services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, JAX-WS, and JAX-RS APIs.
 malwareman007/cve-2022-36537
POC of CVE-2022-36537
 shoucheng3/ff4j__ff4j_cve-2022-44262_1-8-13
Feature toggle framework for Java enabling runtime feature activation, role-based access, AOP-driven toggling, monitoring, audit trails, and a web…
 shoucheng3/ff4j__ff4j_cve-2022-44262_1_8_13_fixed
Feature toggle framework for Java enabling runtime feature activation, role-based access, AOP-driven toggling, monitoring, audit trails, and a web…
 shoucheng3/apache__shiro_cve-2023-34478_1-11-0
Java security framework providing authentication, authorization, cryptography, and session management APIs to secure any application from mobile to…
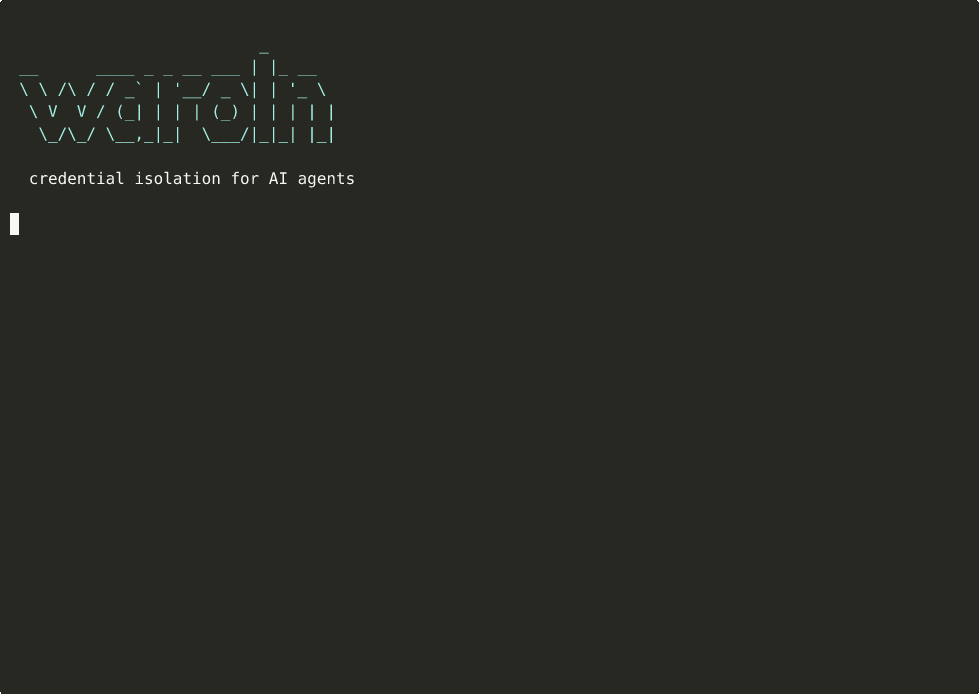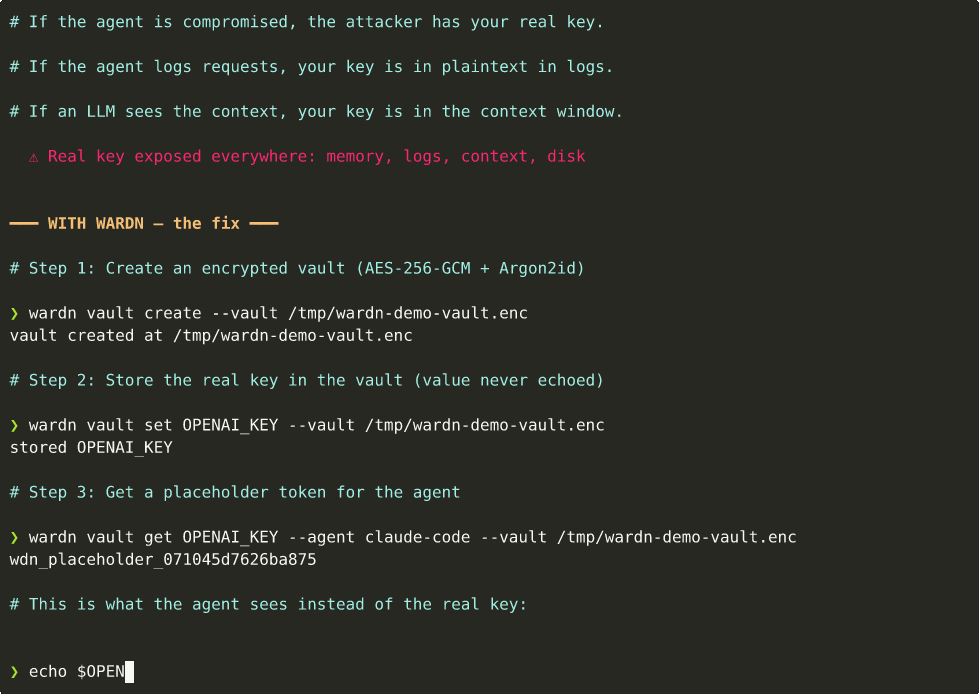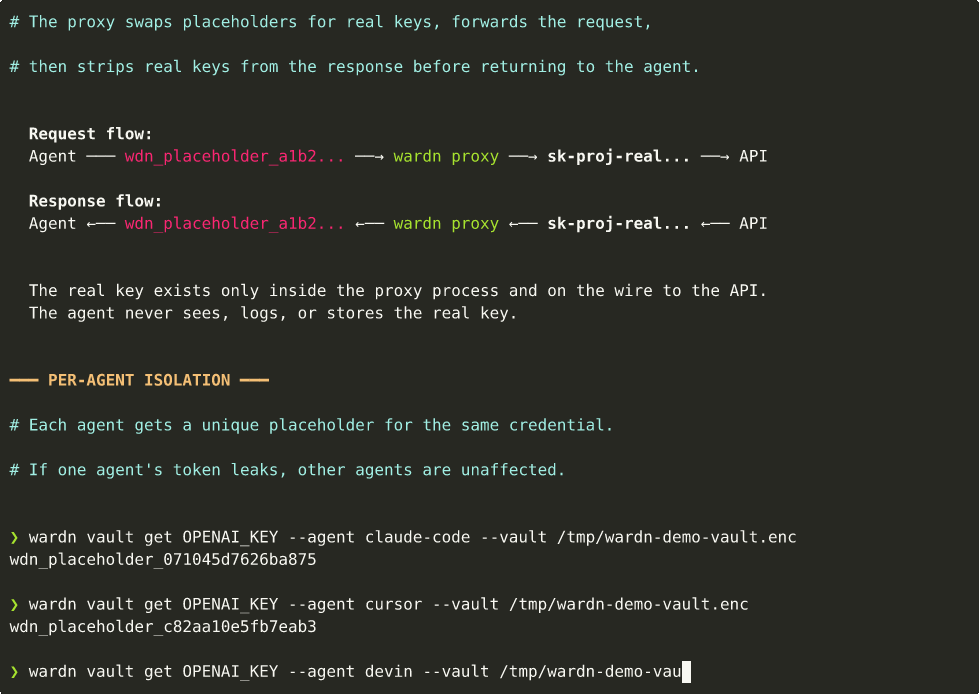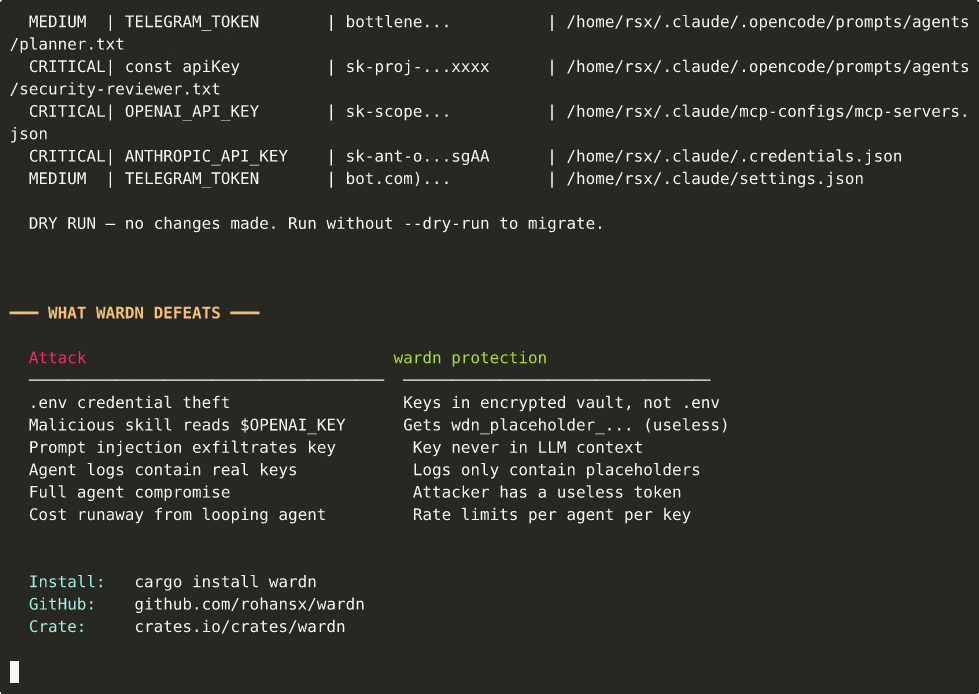 rohansx/wardn
credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.