
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
178 results
MFASweep preview

MFASweep

GitHubdafthack/mfasweep

A tool for checking if MFA is enabled on multiple Microsoft Services
authenticationcloud-securitypenetration-testing+2
1.7k5 months ago
CVE-2025-50154 preview

CVE-2025-50154

GitHubzenzue/cve-2025-50154

PowerShell toolkit to audit, harden, and hunt for insecure NTLM/SMB usage, addressing CVE-2025-50154 credential leak risks with event log analysis…
authenticationconfiguration-auditingdefensive-tools+7
31 year ago
CVE-2026-25253 preview

CVE-2026-25253

GitHubkajzingerakos/cve-2026-25253

Proof-of-concept exploit for CVE-2026-25253, demonstrating one-click remote code execution in OpenClaw via authentication token theft and cross-site…

authenticationexploitationred-teaming+3
15 months ago
lsawhisper-bof preview

lsawhisper-bof

GitHubdazzyddos/lsawhisper-bof

A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
authenticationcommand-and-controlexploitation+4
2967 months ago
Potato preview

Potato

GitHubfoxglovesec/potato

Windows local privilege escalation exploit using NBNS spoofing, fake WPAD proxy, and HTTP-to-SMB NTLM relay to gain NT AUTHORITY\SYSTEM access.

authenticationexploitationlateral-movement+5
7435 years ago
mimikatz-missing-manual preview

mimikatz-missing-manual

GitHubdarkoperator/mimikatz-missing-manual

Comprehensive self-paced manual on Windows identity, Kerberos, and PKI internals, covering credential dumping, ticket forgery, domain persistence,…
authenticationcryptographyeducation+6
4658 months ago
windows-coerced-authentication-methods preview

windows-coerced-authentication-methods

GitHubp0dalirius/windows-coerced-authentication-methods

A list of methods to coerce a windows machine to authenticate to an attacker-controlled machine through a Remote Procedure Call (RPC) with various…
authenticationcurated-resourcesexploitation+3
60520 days ago
KRBUACBypass preview

KRBUACBypass

GitHubwh0amitz/krbuacbypass

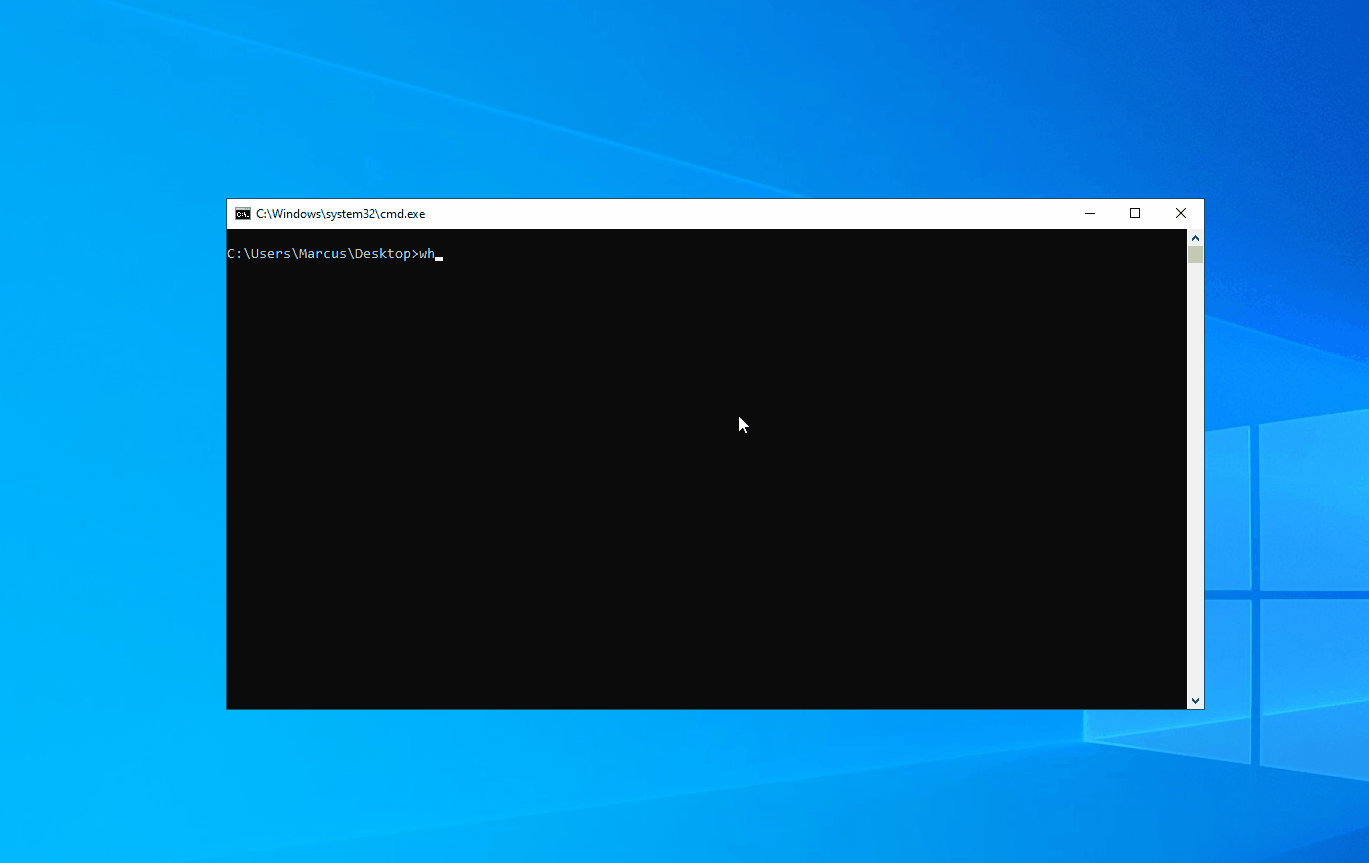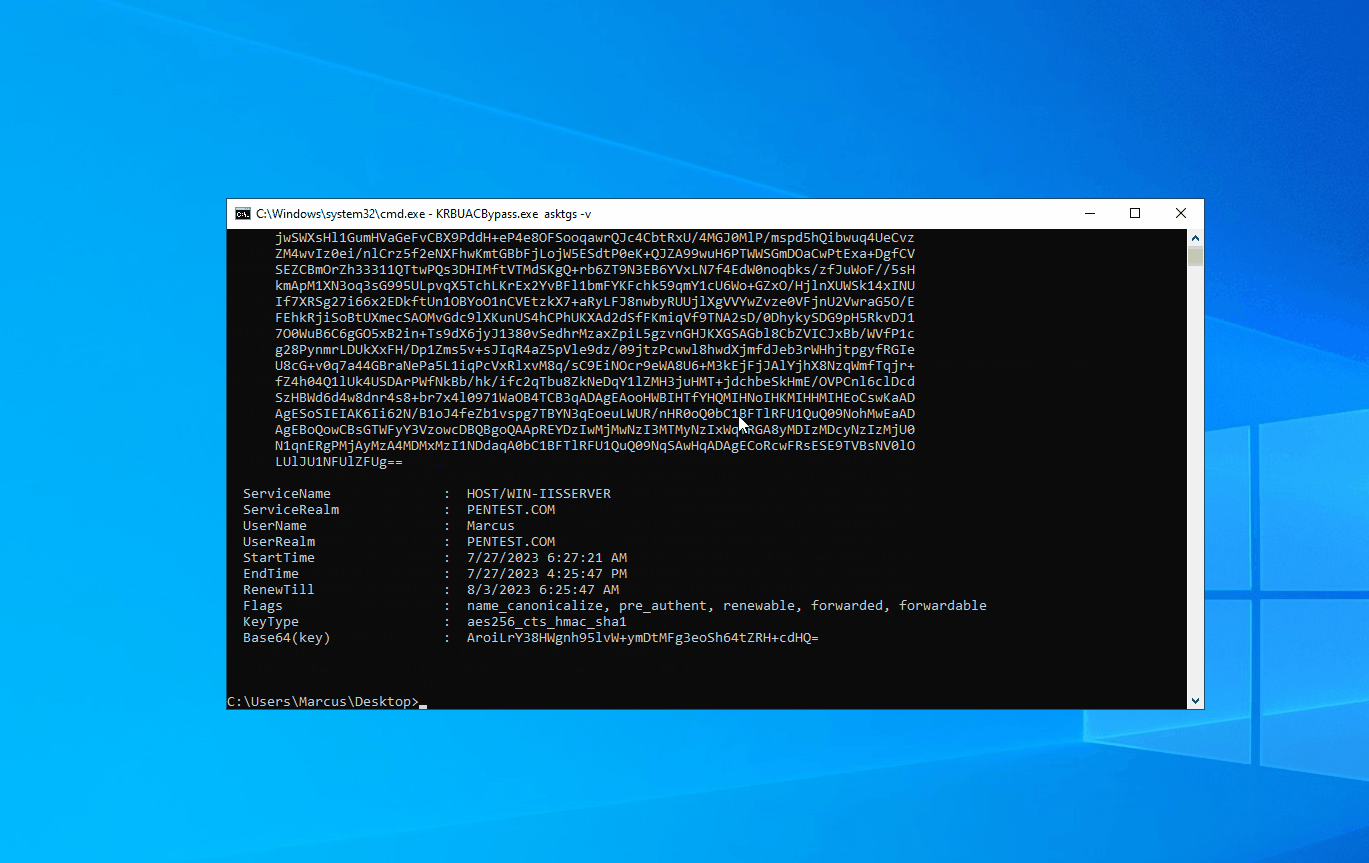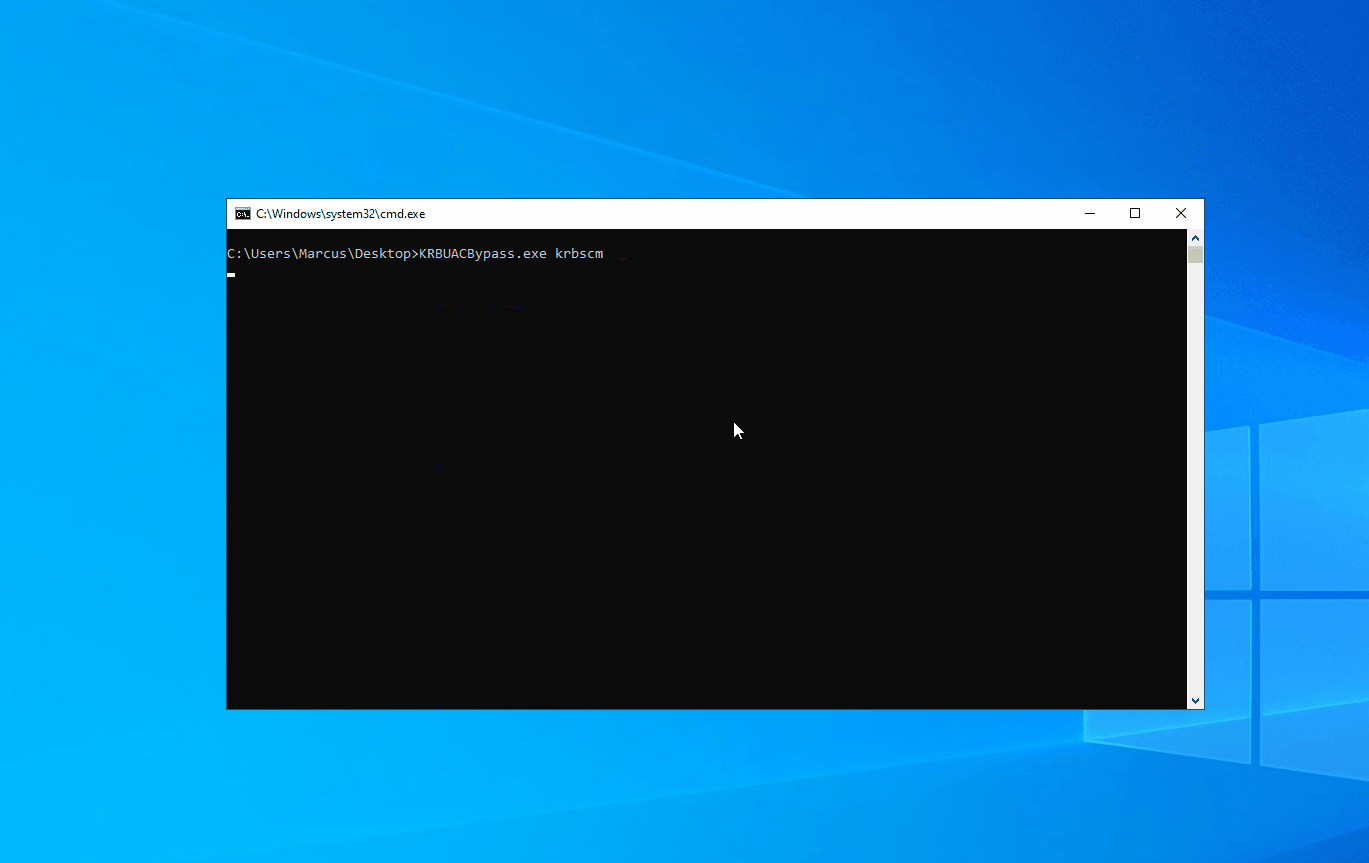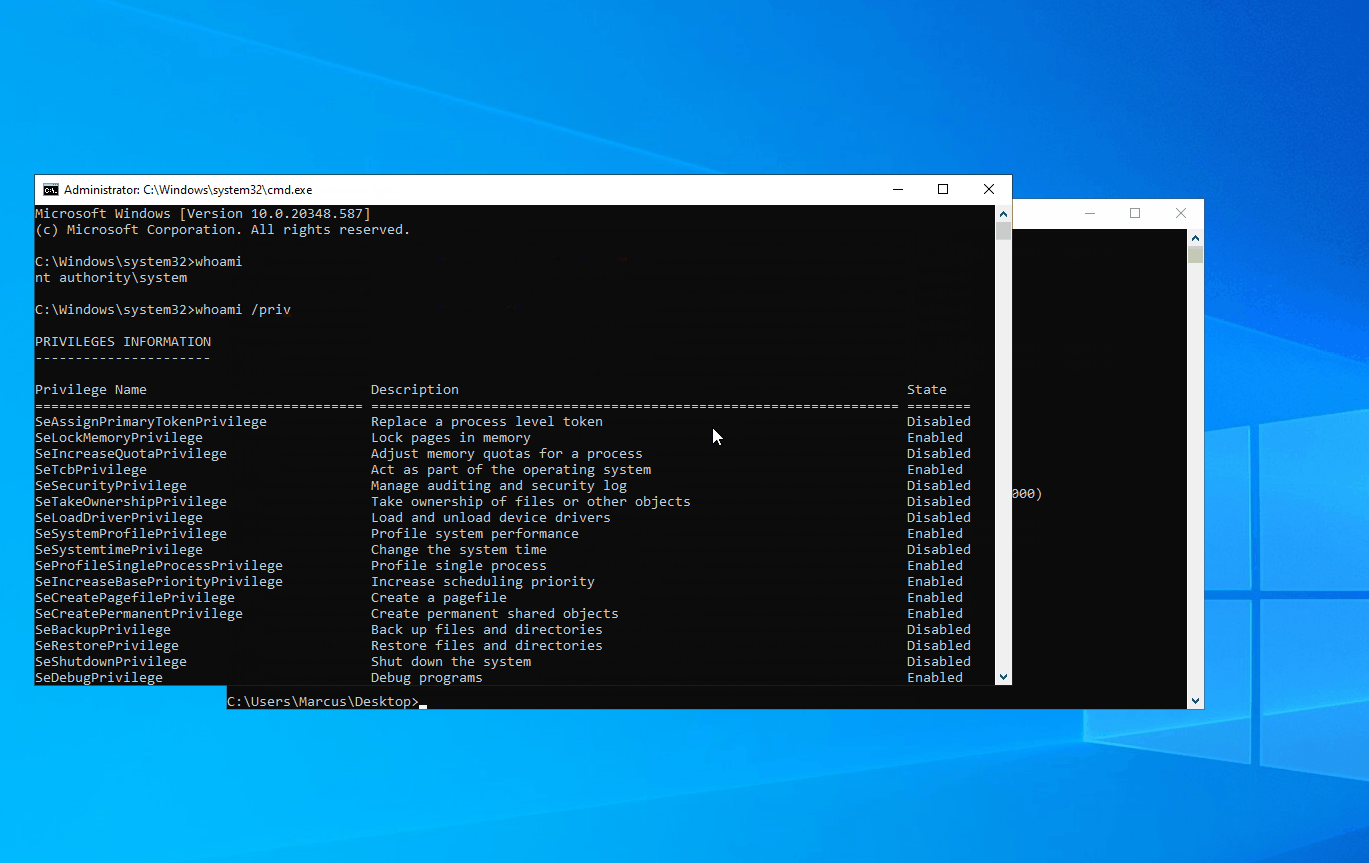
Abuses Kerberos tickets to bypass Windows UAC and gain SYSTEM privileges by injecting a fake MachineID into service tickets, leveraging the tgtdeleg…

authenticationexploitationpenetration-testing+2
5113 years ago
PetitPotam preview

PetitPotam

GitHubtopotam/petitpotam

PoC tool to coerce Windows hosts to authenticate to other machines via MS-EFSRPC EfsRpcOpenFileRaw or other functions.

authenticationexploitationpenetration-testing+1
2.3k2 years ago
Coercer preview

Coercer

GitHubp0dalirius/coercer

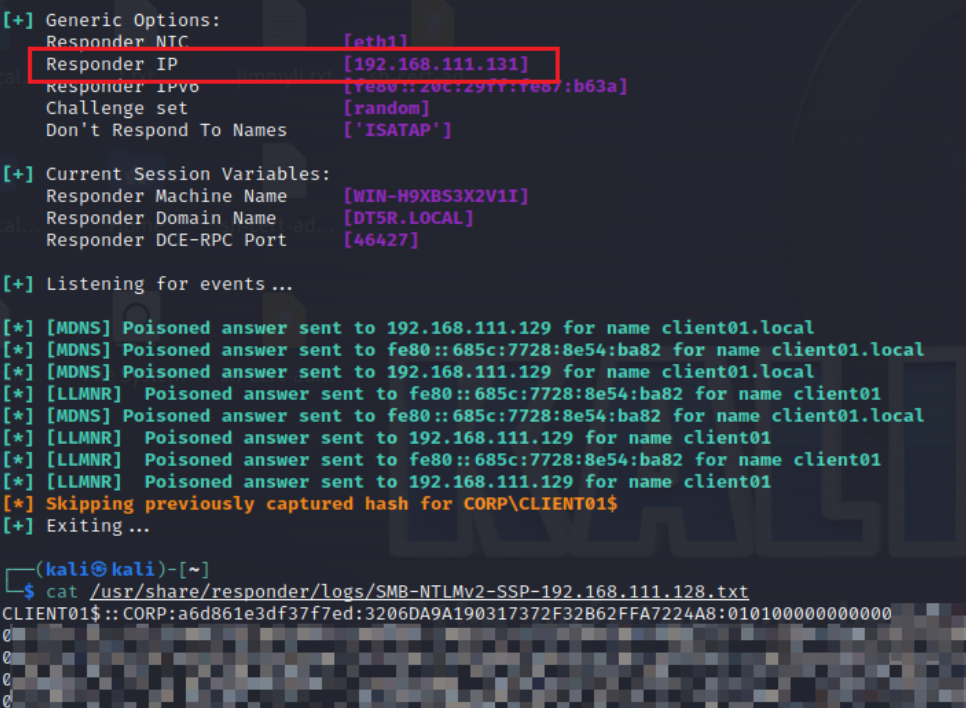
A python script to automatically coerce a Windows server to authenticate on an arbitrary machine through 12 methods.
authenticationexploitationfuzzing+3
2.3k5 months ago
CVE-2024-40586-Windows-Coerced-Authentication-in-FortiClient preview

CVE-2024-40586-Windows-Coerced-Authentication-in-FortiClient

GitHubhagrid29/cve-2024-40586-windows-coerced-authentication-in-forticlient

Exploit for CVE-2024-40586: coerces Windows hosts to authenticate via a vulnerable FortiClient named pipe, enabling privilege escalation to SYSTEM or…

authenticationexploitationlateral-movement+4
11 year ago
CVE-2022-30216 preview

CVE-2022-30216

GitHubcorelight/cve-2022-30216

Zeek package detecting CVE-2022-30216 NTLM relay attacks against Windows Server. Raises notices for exploit attempts and successful exploitation via…
authenticationexploitationintrusion-detection+2
3 years ago
imposter preview

imposter

GitHubbugch3ck/imposter

Proof of concept for CVE-2015-0006. Fixed in MS15-005 https://docs.microsoft.com/en-us/security-updates/SecurityBulletins/2015/ms15-005 .

authenticationexploitationnetwork-security+3
212 years ago
mimikatz preview

mimikatz

GitHubgentilkiwi/mimikatz

A little tool to play with Windows security

authenticationexploitationexploit-frameworks+10
21.9k5 months ago
lsarelayx preview

lsarelayx

GitHubccob/lsarelayx

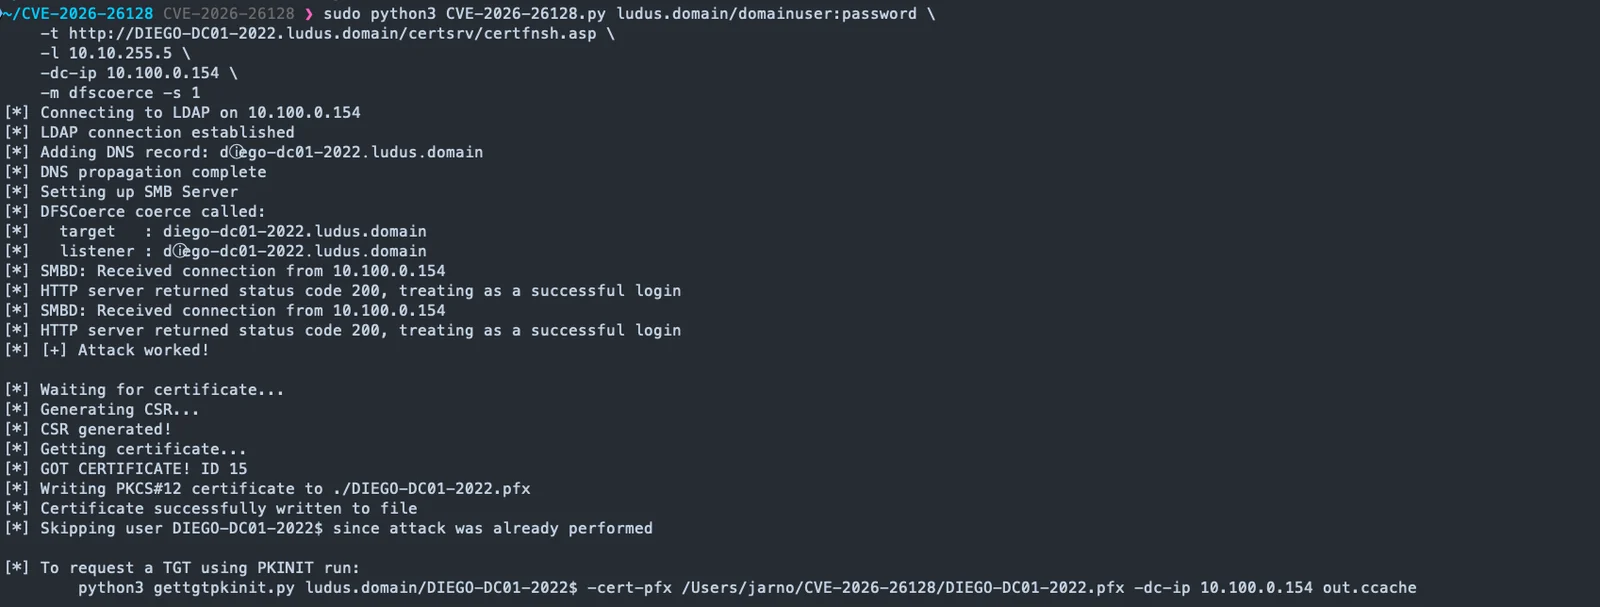
System-wide NTLM relay tool that hooks Windows authentication APIs to relay incoming NTLM connections, downgrade Kerberos, and dump NetNTLM hashes…
authenticationexploitationpassword-attacks+2
5864 years ago
CVE-2026-26128 preview

CVE-2026-26128

GitHubjarnovandenbrink/cve-2026-26128

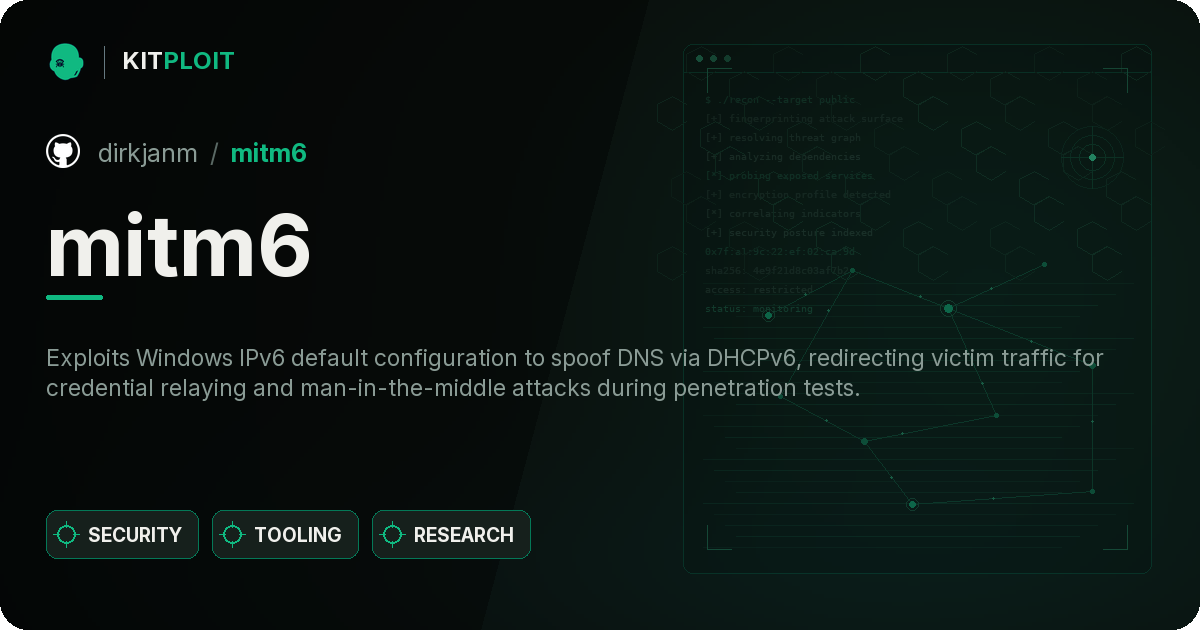
Exploits Kerberos reflection via Unicode normalization in Windows Active Directory to relay authentication to ADCS and MSSQL, enabling…
authenticationexploitationpenetration-testing+2
635 months ago
mitm6 preview

mitm6

GitHubdirkjanm/mitm6

Exploits Windows IPv6 default configuration to spoof DNS via DHCPv6, redirecting victim traffic for credential relaying and man-in-the-middle attacks…
authenticationdns-analysisinformation-gathering+3
1.9k4 years ago
DavRelayUp preview

DavRelayUp

GitHubdec0ne/davrelayup

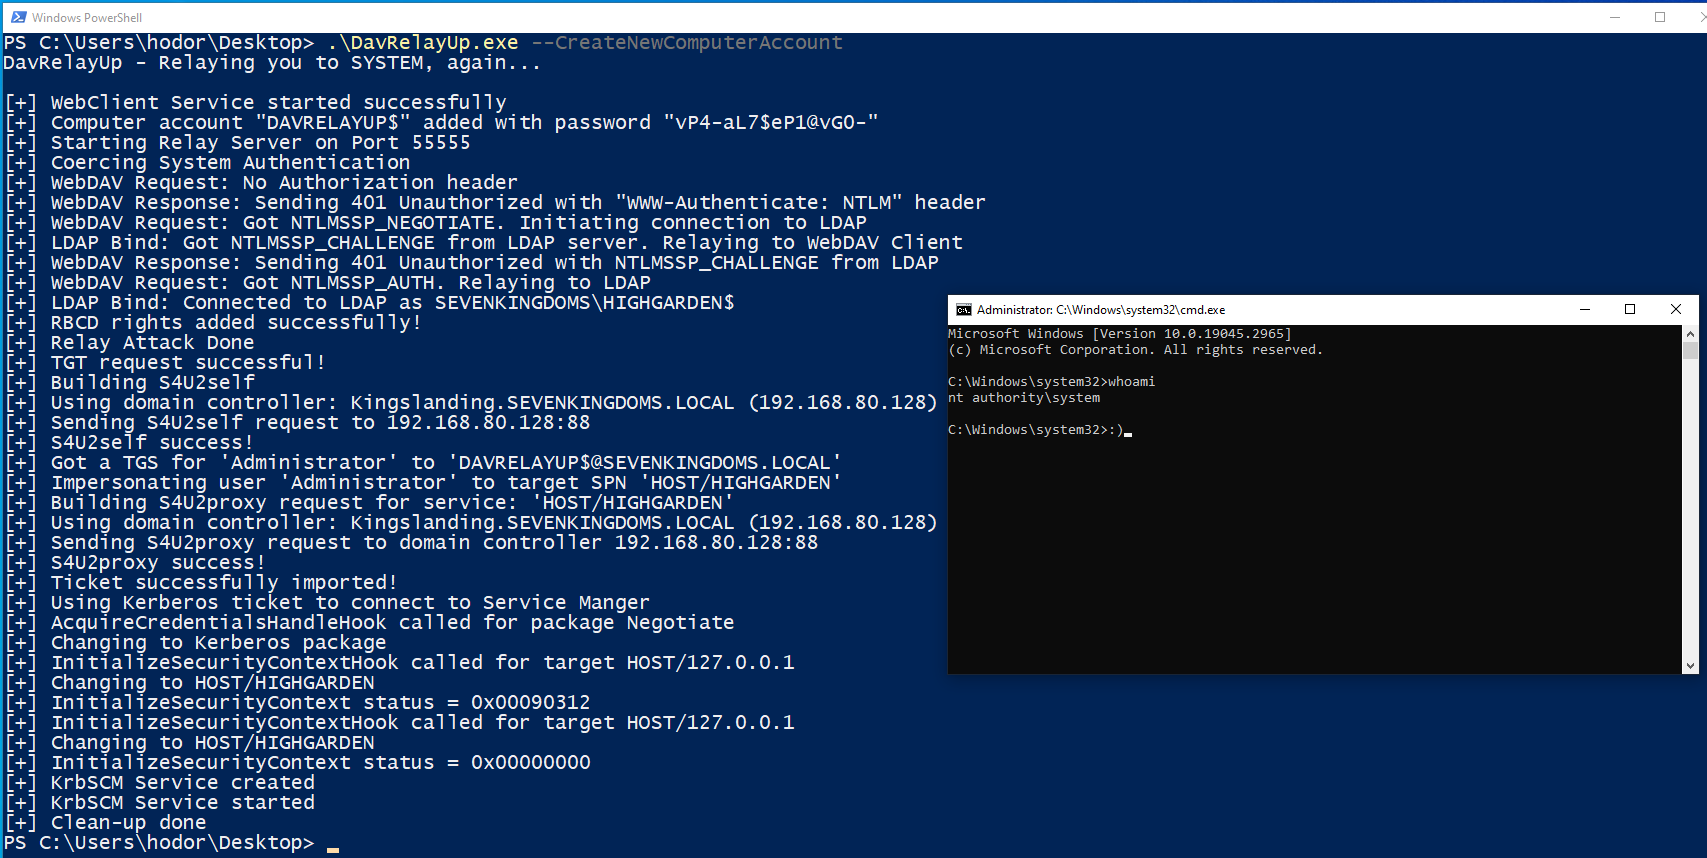
Automates local privilege escalation to SYSTEM on domain-joined Windows workstations by relaying NTLM authentication from WebDAV to LDAP, leveraging…

authenticationexploitationlateral-movement+2
5783 years ago
Previous12…10Next