
awesome-privacy
 lissy93/awesome-privacy
🦄 A curated list of privacy & security-focused software and services
authenticationcurated-resourceseducation+6
9.9k4 days ago
lissy93/awesome-privacy🦄 A curated list of privacy & security-focused software and services
 p0dalirius/windows-coerced-authentication-methods
A list of methods to coerce a windows machine to authenticate to an attacker-controlled machine through a Remote Procedure Call (RPC) with various…
 tailscale/tailscale
The easiest, most secure way to use WireGuard and 2FA.
 better-auth/better-auth
The most comprehensive authentication framework
 login-securite/donpapi
Automated remote credential dumper for Windows environments, extracting DPAPI secrets, browser credentials, certificates, and configuration files…
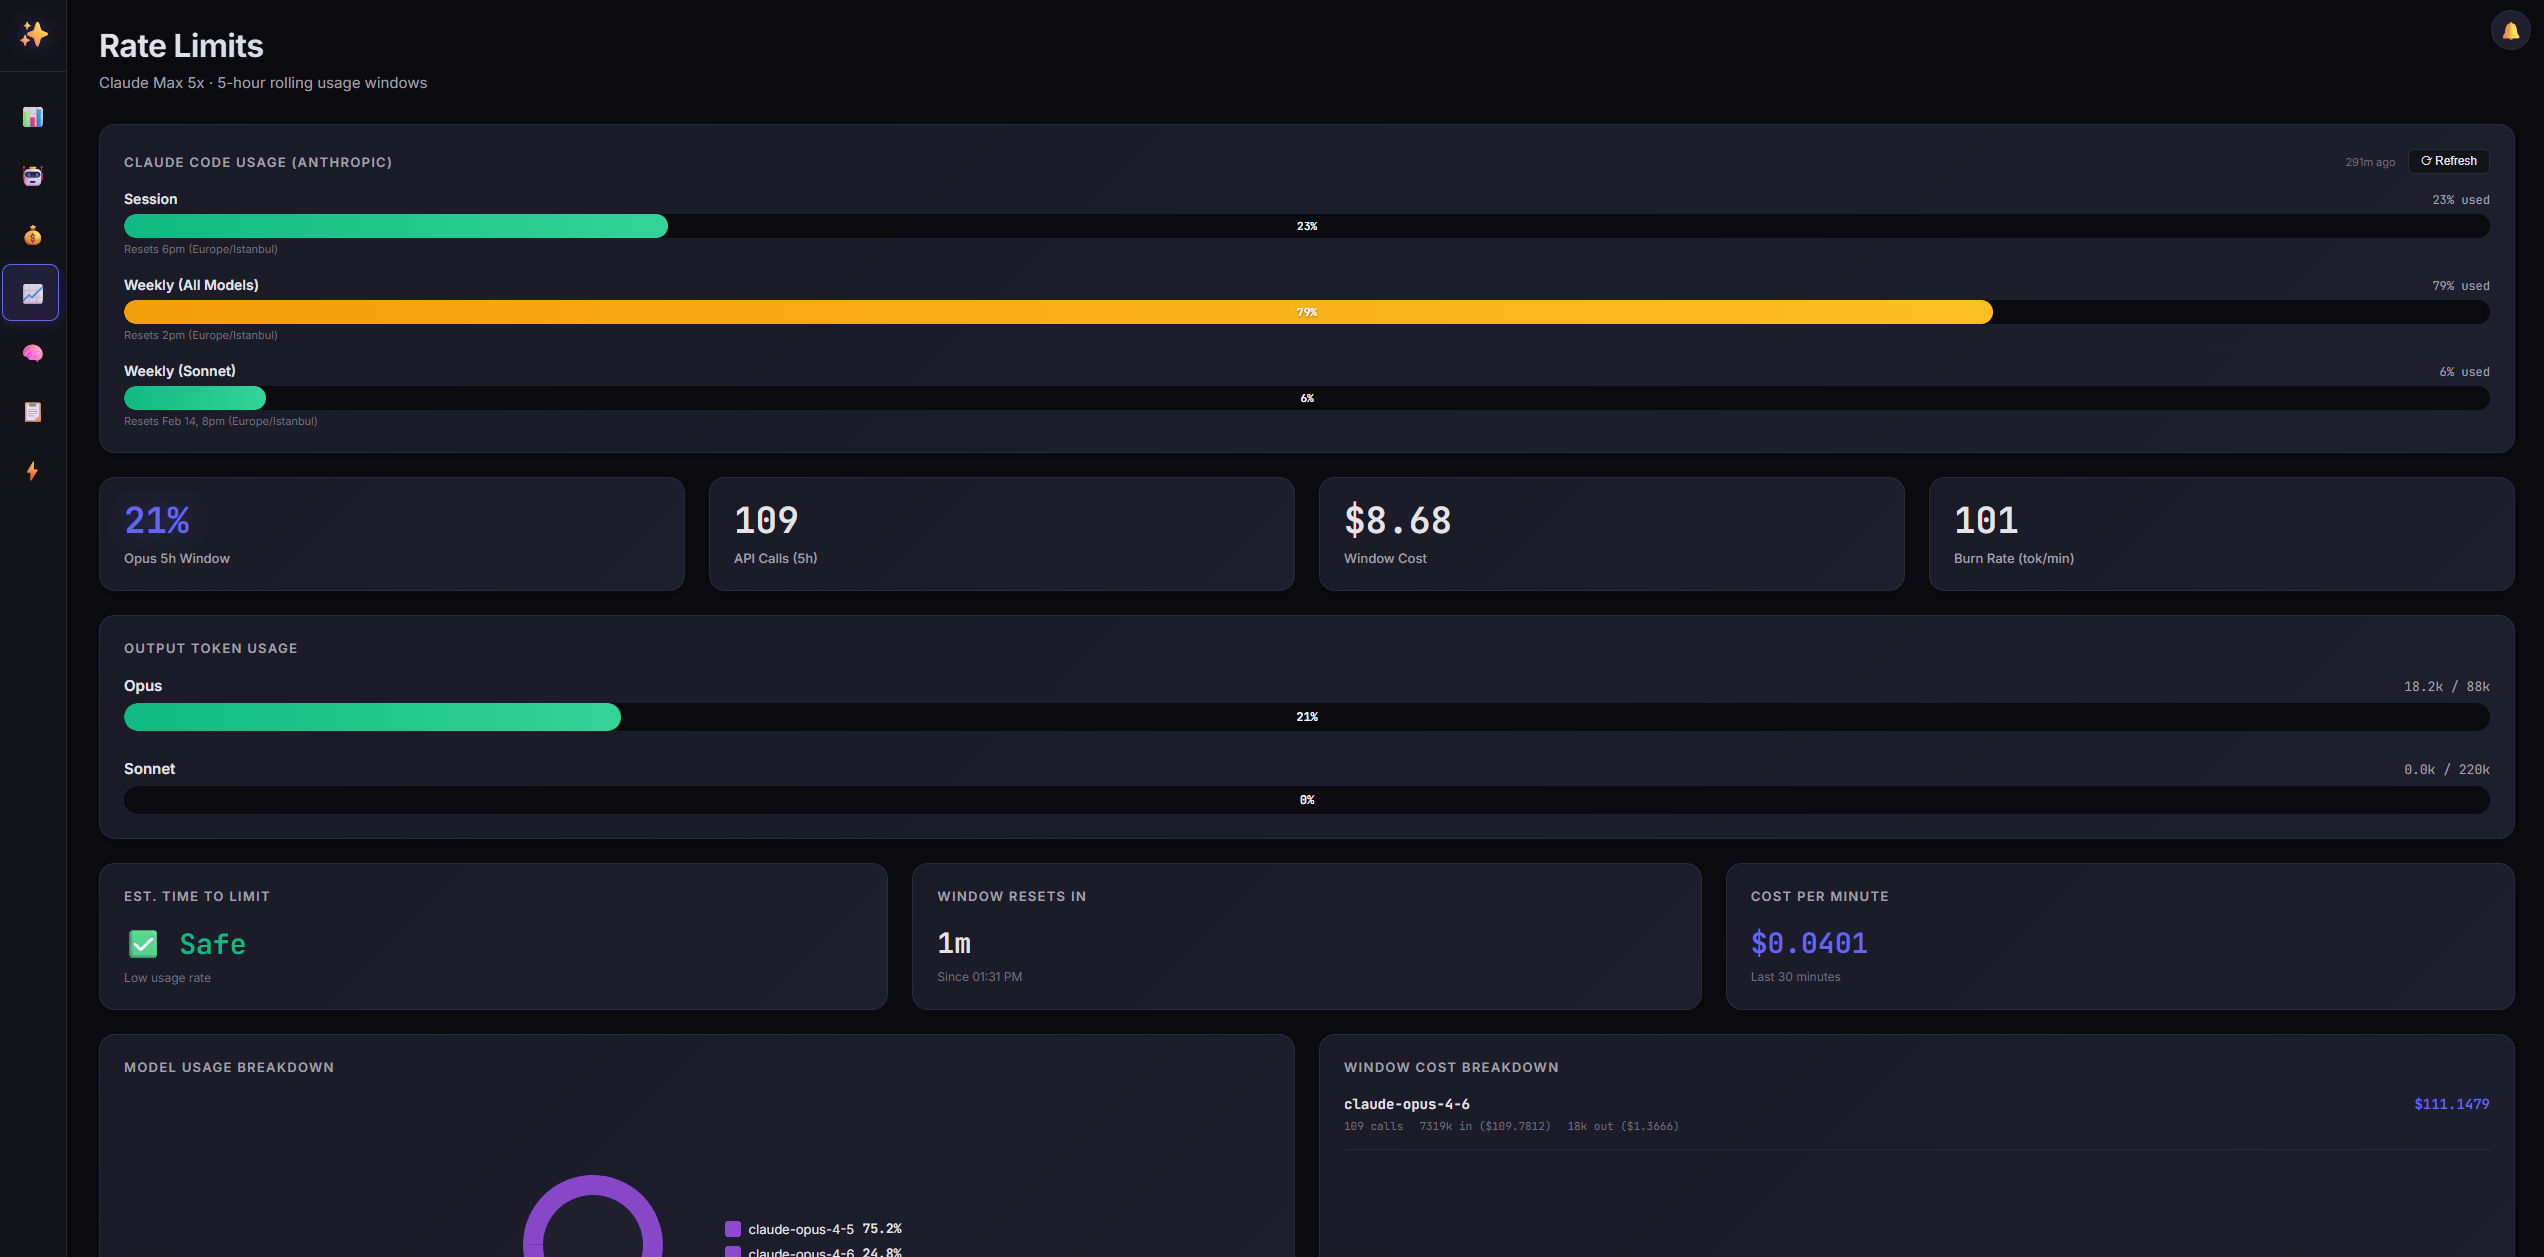 tugcantopaloglu/openclaw-dashboard
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
 horizon3ai/cve-2022-22972
Proof-of-concept exploit for CVE-2022-22972 that bypasses authentication in VMware Workspace ONE, vIDM, and vRealize Automation 7.6 via Host header…
 iomoath/sharpspray
Active Directory password spraying tool. Auto fetches user list and avoids potential lockouts.
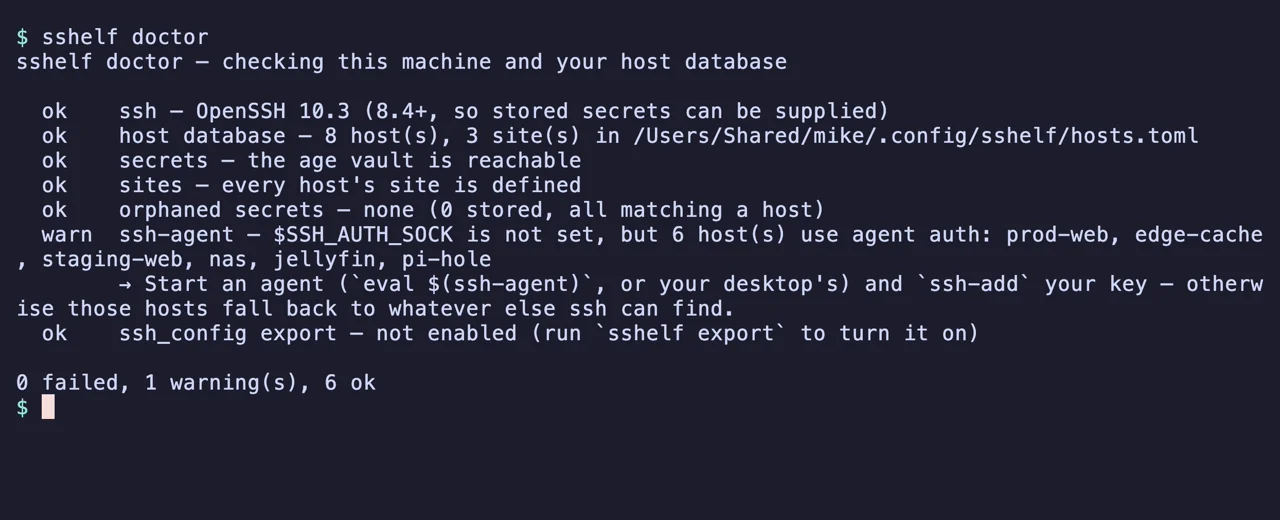 max-rh/sshelf
Fast terminal UI for your SSH hosts: fuzzy-search and connect in two keystrokes, dual-pane SFTP file transfer, and background port forwarding. Keeps…
 jmalinen/hostap
Clone of w1.fi hostap.git - NOTE: This is not the main development location and pull requests for this repository are ignored. See the upstream…
 faceless0x7/cve-2026-89013
Python exploit for CVE-2026-89013, an unauthenticated Dolibarr hashp authorization bypass enabling arbitrary file read, with check, list, hunt, read,…
 d-raco/cve-2024-31964
Proof-of-concept exploit for CVE-2024-31964, a temporary authentication bypass in Mitel 6900w Series SIP phones allowing unauthenticated POST…
 elizeuopain/exploit-cve-2024-9513-netadmin-iam-allows-user-enumeration-in-active-directory
Proof-of-concept exploit for CVE-2024-9513 targeting user enumeration in NetAdmin IAM via HTTP POST request to…
 gluxon/cve-2018-13257
Proof-of-concept exploit for CVE-2018-13257 demonstrating CAS host header spoofing in Blackboard Learn to hijack user sessions via a malicious…
 ex-cal1bur/cve-2026-44596
YAMCS yamcs-core < 5.12.7 lacks rate limiting on POST /auth/token. An unauthenticated attacker can perform unlimited brute-force attempts against any…
 g0w6y/cve-2026-21994
Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…
 vanlam2001/csrf_casdoor
Proof-of-concept CSRF exploit for Casdoor's `/api/set-password` endpoint (CVE-2023-34927), enabling unauthorized password changes via cross-site POST…
 randomrobbiebf/postgres-bruteforcer
This tool takes a list of default creds and tests it against a postgresql server and logs any that work and the databases it has access to.