
fyp
 talha1112/fyp
Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
authenticationexploitationnetwork-security+4
talha1112/fypDesktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
 skynoxk/cve-2025-40554
CVE-2025-40554 Exploitation
 livehybrid/poc-cribl-rce
CVE-2019-11076 - Cribl UI 1.5.0 allows remote attackers to run arbitrary commands via an unauthenticated web request
 optionalctf/ssoh-no
User enumeration and password spraying tool for testing Azure AD
 hashicorp/vault
A tool for secrets management, encryption as a service, and privileged access management
 authelia/authelia
The Single Sign-On Multi-Factor portal for web apps. OpenID Certified™ and Post-Quantum Cryptography Ready.
 ly4k/certipy
Tool for Active Directory Certificate Services enumeration and abuse
 dafthack/mfasweep
A tool for checking if MFA is enabled on multiple Microsoft Services
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 owasp/igoat
OWASP iGoat - A Learning Tool for iOS App Pentesting and Security by Swaroop Yermalkar
 cyberark/ketshash
A little tool for detecting suspicious privileged NTLM connections, in particular Pass-The-Hash attack, based on event viewer logs.
 jnqpblc/sharpspray
C# tool for automated password spraying attacks against Active Directory users via LDAP, with configurable delays and password lists, designed for…
 nccgroup/carnivore
Tool for assessing on-premises Microsoft servers authentication such as ADFS, Skype, Exchange, and RDWeb
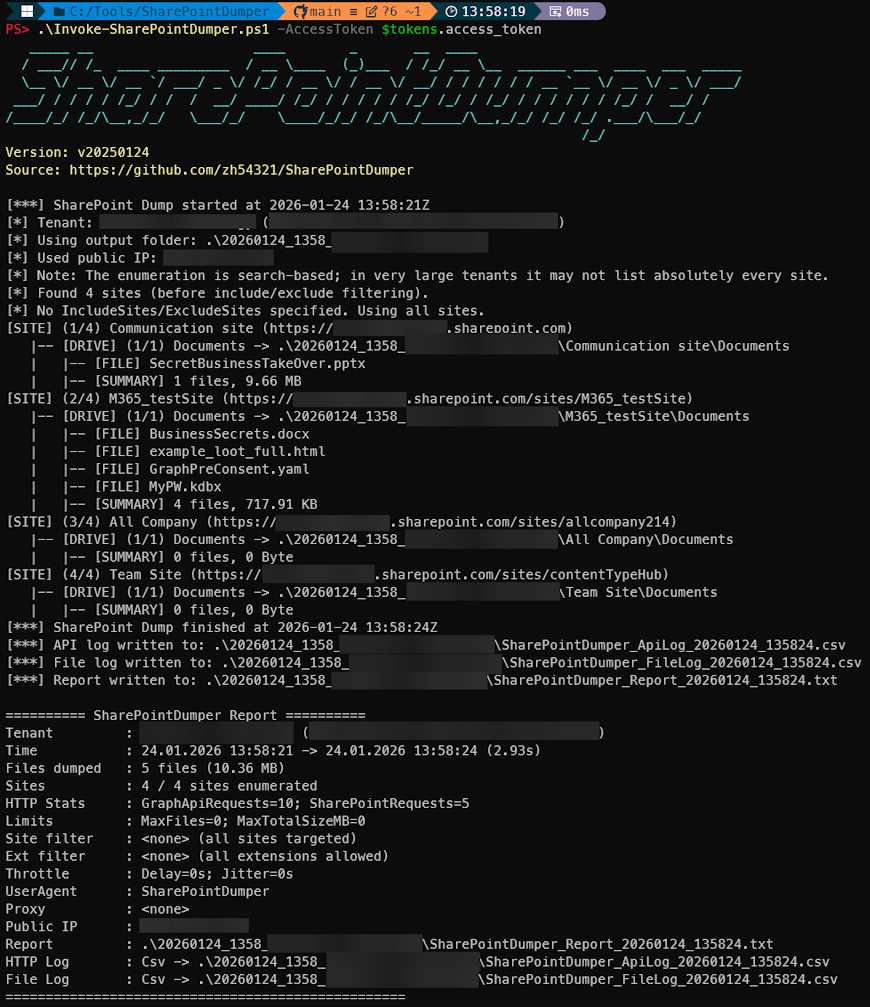 zh54321/sharepointdumper
PowerShell SharePoint extraction + auditing tool for red/blue/purple teams. Enumerates all SharePoint sites/drives a user can access via Microsoft…
 praetorian-inc/ntlmrecon
A tool for performing light brute-forcing of HTTP servers to identify commonly accessible NTLM authentication endpoints.
 kagantua/cpanelwhm-authbypass
Go-based scanner and exploit tool for CVE-2026-41940, an authentication bypass in cPanel/WHM. Supports batch scanning, token leakage, and…
 n4nj0/cve-2020-35590
Brute-force tool for WordPress Plugin Limit Login Attempts Reloaded >=2.13.0 - Login Limit Bypass (CVE-2020-35590)