
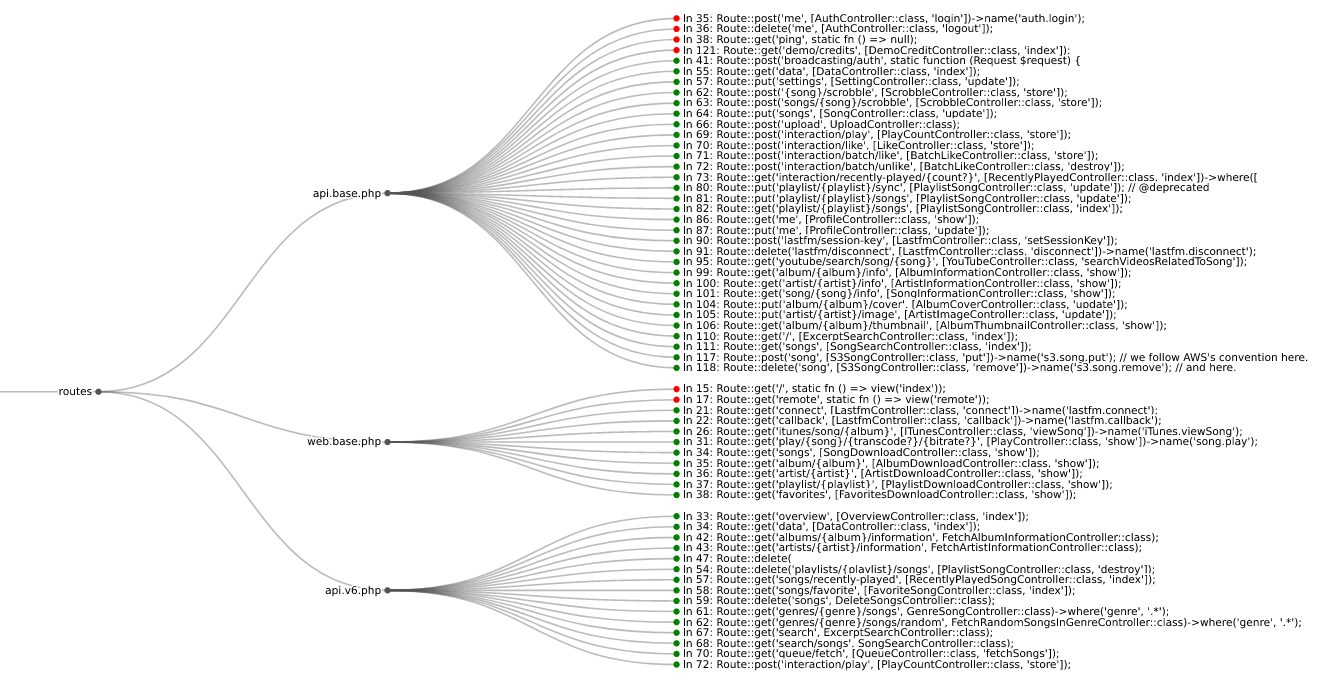
route-detect
 mschwager/route-detect
Find authentication (authn) and authorization (authz) security bugs in web application routes.
authenticationstatic-analysisvulnerability-analysis+1
280
mschwager/route-detectFind authentication (authn) and authorization (authz) security bugs in web application routes.
 debajyoti0-0/cve-2026-60206
Technical analysis and Proof-of-Concept for CVE-2026-60206, a critical Oracle WebLogic Server SAML authentication bypass vulnerability.
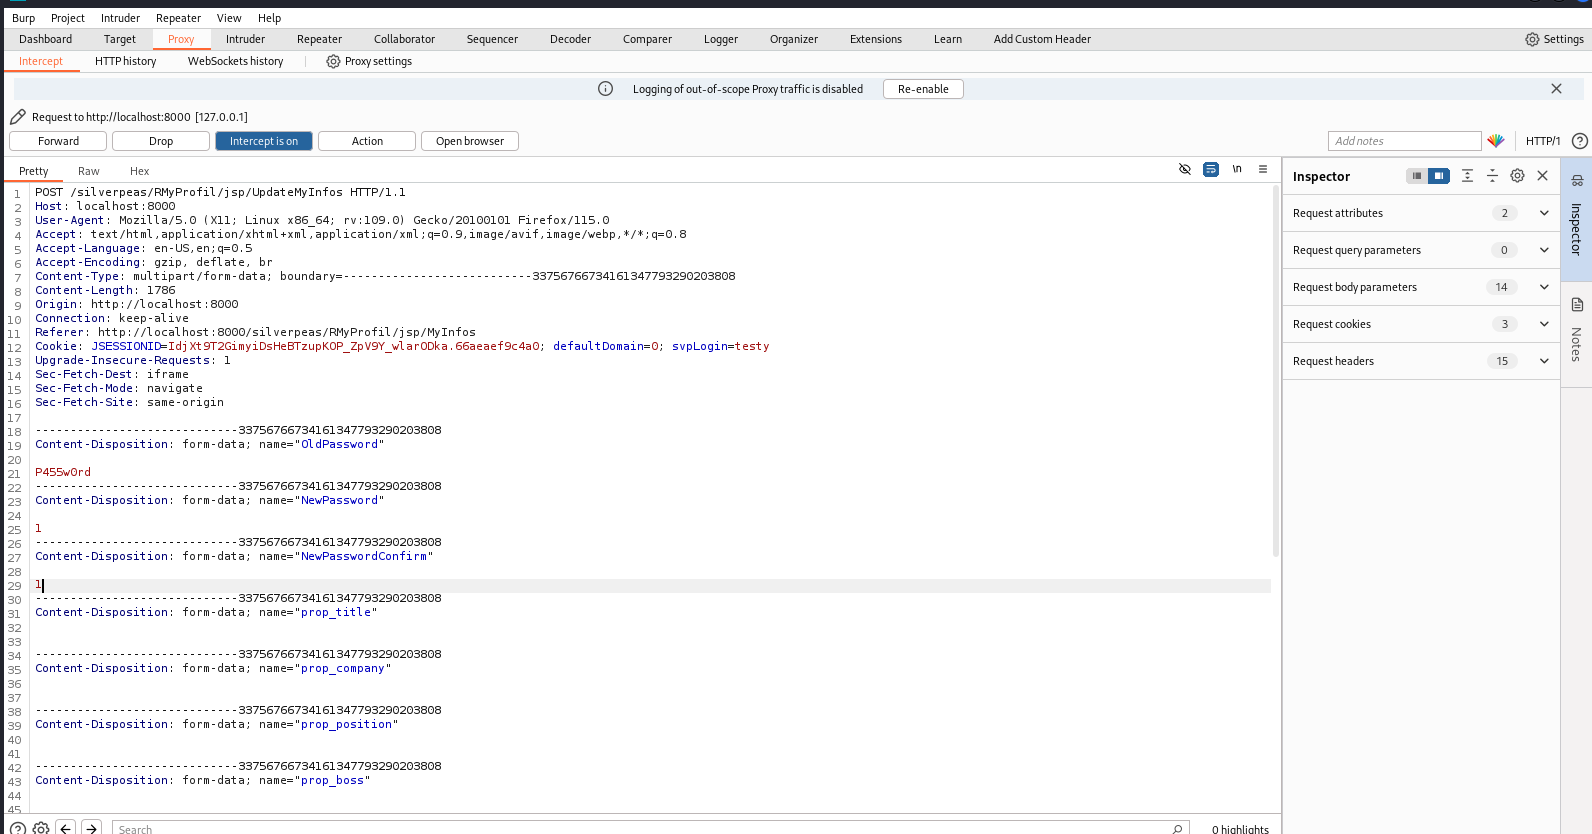 njmbb8/cve-2024-42850
An issue in Silverpeas v6.4.2 and lower allows for the bypassing of password complexity requirements.
 ev3rpalestine/0xmiddleware
CVE-2025-29927: Next.js Middleware Exploit
 stefandorresteijn/cve-2021-39409
Admin account registration in Online Student Rate System
 jet-pentest/cve-2021-3130
Proof-of-concept for CVE-2021-3130: demonstrates credential exposure via HTML obfuscation bypass in Open-AudIT up to 4.0.2, revealing SSH, SNMP, and…
 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 ylianst/meshcentral
A complete web-based remote monitoring and management web site. Once setup you can install agents and perform remote desktop session to devices on…

 initroot/cve-2022-23342
Proof-of-concept for Active Directory username enumeration vulnerability in Hyland OnBase via login endpoint response differences, enabling…
 karammahmad/cve-2021-40113
CVE documentation repository detailing unauthenticated remote vulnerabilities in Cisco Catalyst PON Series Switches ONT, including default credential…
 anir0y/sonicwall-audit-toolkit
SonicWall security audit toolkit with vulnerable CTF lab (CVE-2021-20038, CVE-2024-53704)
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
 asterisk/asterisk
The official Asterisk Project repository.
 microsoft/windowsprotocoltestsuites
⭐⭐ Join us at SNIA SDC for the SMB3 IO Lab (September 28 - October 1, 2026), see upcoming Interoperability Events
 tugcantopaloglu/openclaw-dashboard
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
 sigstore/root-signing
Maintains the TUF repository that securely delivers the Sigstore trust root (trusted_root.json) to clients, using keyholder threshold signing, KMS…
