
CVE-2026-44338-Lab
 rootdirective-sec/cve-2026-44338-lab
Docker-based lab demonstrating CVE-2026-44338 authentication bypass in PraisonAI's legacy Flask API. Includes vulnerable and patched services with…
authenticationeducationlabs-practice+3
rootdirective-sec/cve-2026-44338-labDocker-based lab demonstrating CVE-2026-44338 authentication bypass in PraisonAI's legacy Flask API. Includes vulnerable and patched services with…
 cyberharsh/libssh-server-cve-2018-10933
Proof-of-concept exploit for CVE-2018-10933, demonstrating SSH authentication bypass via MSG_USERAUTH_SUCCESS injection. Includes Docker setup and…
 hunt-benito/the-token-was-a-row-number-cve-2026-67602-phpipam-rest-api-authentication-bypass
Exploit and PoC for CVE-2026-67602, an authentication bypass in phpIPAM REST API via object-cache key collision, including a logic-level PoC and…
 savsch/poc_cve-2019-0217
Proof-of-concept exploit for CVE-2019-0217, a race condition in Apache HTTP Server's mod_auth_digest allowing authentication bypass. Includes…
 trackflaw/cve-2024-10924-wordpress-docker
Vulnerable docker container for Really Simple Security (Free, Pro, and Pro Multisite) 9.0.0 – 9.1.1.1 – Authentication Bypass CVE-2023-50164
 mdvpat/cve-2026-55957-poc
Reproducible Docker lab for the Apache Tomcat JNDIRealm GSSAPI authentication bypass
 0xdaeras/flowise-cve-2025-58434-chain-59528
FlowiseAI CVE-2025-58434 & CVE-2025-59528 exploit PoC, demonstrating unauthenticated ATO via reset token leakage, followed by authenticated RCE.…
 gman0x00/keycloak-cve-2026-18963
PoC, Dockerfile playground and root cause from patch diff analysis.
 hunt3r850/cve-2024-10924-wordpress-docker
Dockerized exploit environment for CVE-2024-10924, an authentication bypass in WordPress Really Simple Security plugin (versions 9.0.0-9.1.1.1)…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 dinosn/cve-2026-82329-jfrog-artifactory
Reproducible Docker lab and Python PoC for CVE-2026-82329, an unauthenticated auth-bypass in JFrog Artifactory leading to admin takeover, with…
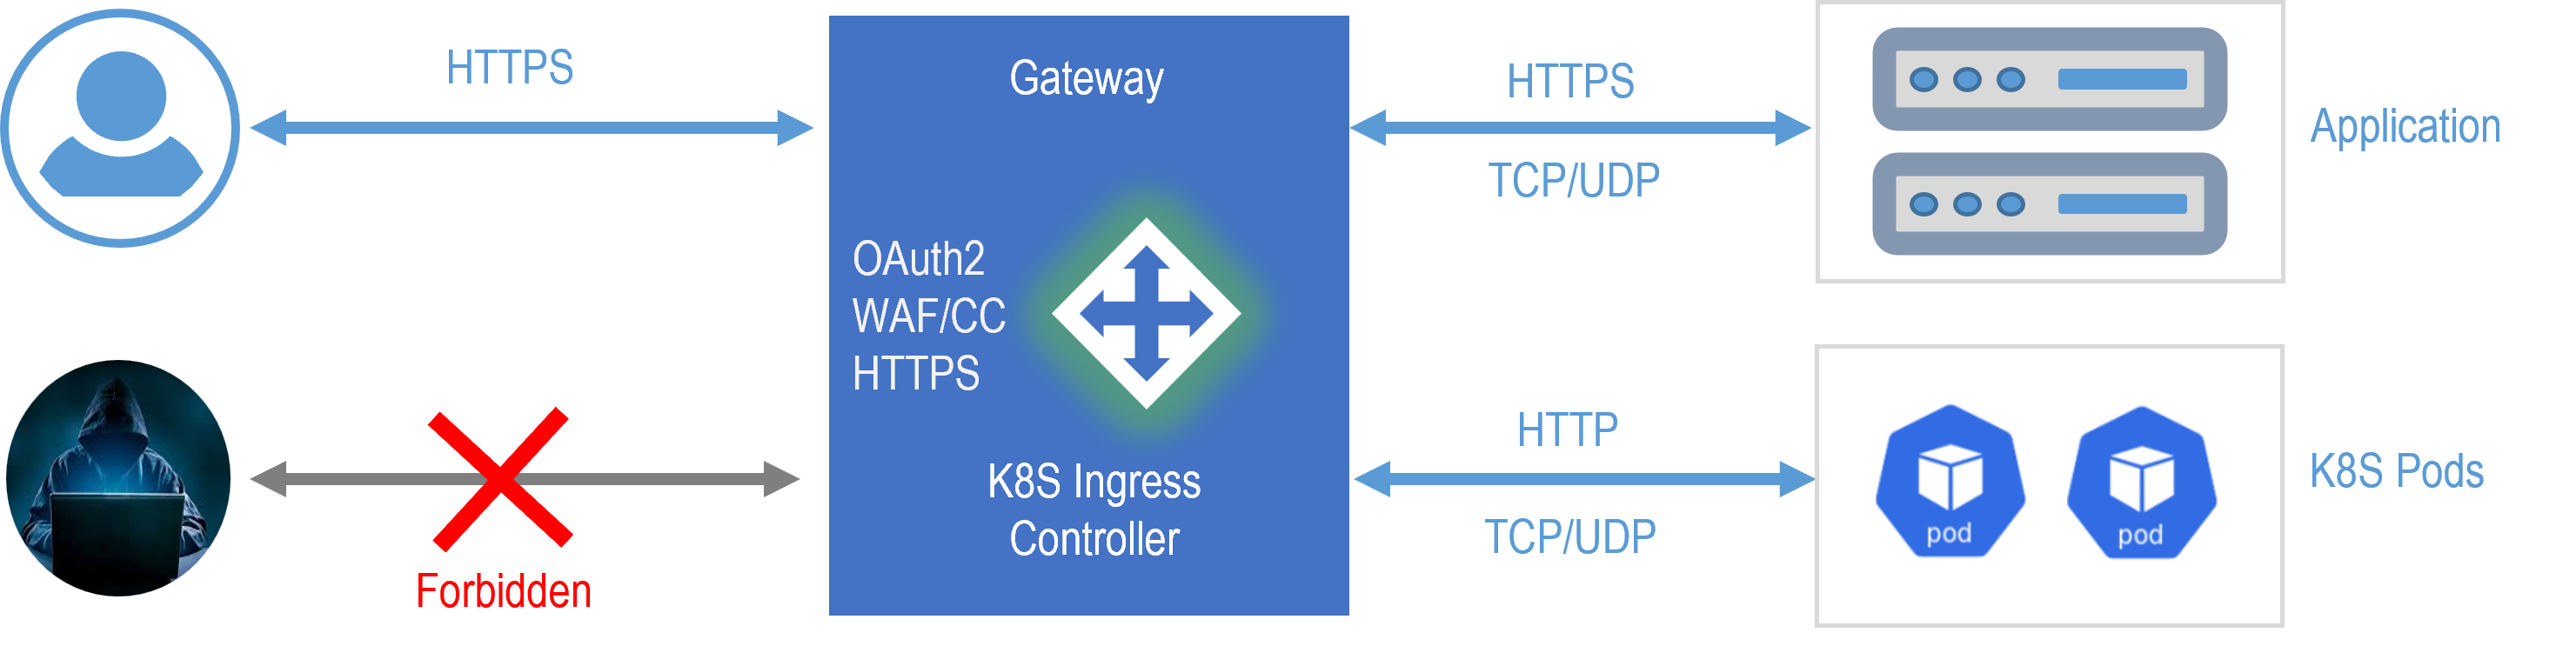 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 hackerhouse-opensource/cve-2018-10933
Docker-based CVE-2018-10933 libssh authentication bypass exploit with patched client for testing SSH server vulnerabilities and unauthorized access…
 twwd/cve-2023-0264
A small PoC for the Keycloak vulnerability CVE-2023-0264
 oscerd/cve-2026-66908
Proof-of-concept reproducer for Apache Camel JWT authentication bypass (CVE-2026-66908) demonstrating missing iss/aud validation in…
 zyn3rgy/ldaprelayscan
Check for LDAP protections regarding the relay of NTLM authentication
 horkimhab/cve-2026-psa-2026-00043-1
Proof-of-concept exploit for an unauthenticated root authentication bypass in Proxmox VE 7.0-8.0.3, intended for authorized security testing and…
 azureadtrent/cve-2026-52824
Technical analysis and PoC of CVE-2026-52824: default APP_SECRET in the Kimai Docker image enabling unauthenticated login link forgery. Affects <=…