
CVE-2023-27524
 horizon3ai/cve-2023-27524
Basic PoC for CVE-2023-27524: Insecure Default Configuration in Apache Superset
authenticationexploitationmisconfiguration+3
horizon3ai/cve-2023-27524Basic PoC for CVE-2023-27524: Insecure Default Configuration in Apache Superset
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
 ayewo/fortios-ldap-mitm-poc-cve-2019-5591
The default configuration of LDAP on FortiOS v6.0.x to v6.2.0 does not check server identity for LDAP/S leading to MITM attacks. This PoC demos full…
 mailcow/mailcow-dockerized
Dockerized mail server suite with Postfix, Dovecot, Rspamd, and ClamAV. Provides secure email hosting with integrated spam filtering, antivirus, and…
 mandiant/vcsa-hardening-tool
Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)
 george0papasotiriou/cve-2026-21018-opc-ua-authentication-bypass-via-none-security-policy
Proof-of-concept exploit for OPC UA authentication bypass using None security policy, including a simulated server to demonstrate unauthorized…
 shoucheng3/asf__james-project_cve-2022-22931_3-6-0
Modular Java mail server supporting IMAP, SMTP, POP3, and JMAP with Docker deployment, distributed architecture, and CLI management for secure…
 aa22396584/synology-nas-cli
nas: a zero-dependency Python CLI + MCP server for Synology DSM 7. One-command audit and fix for the C3RB3R / .L0CK3D ransomware campaign; hand it to…
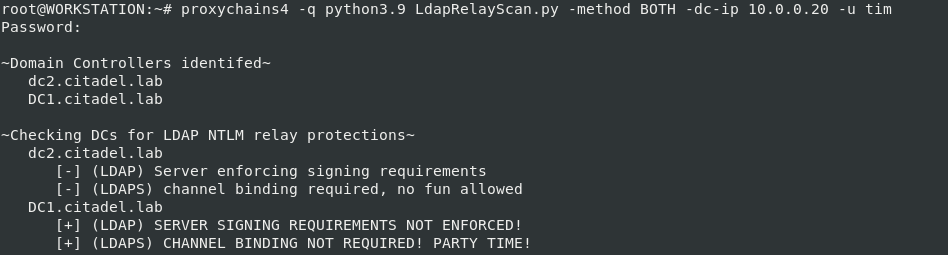 zyn3rgy/ldaprelayscan
Check for LDAP protections regarding the relay of NTLM authentication
 dev-sec/chef-ssh-hardening
This chef cookbook provides secure ssh-client and ssh-server configurations.
 dev-sec/puppet-ssh-hardening
This puppet module provides secure ssh-client and ssh-server configurations.
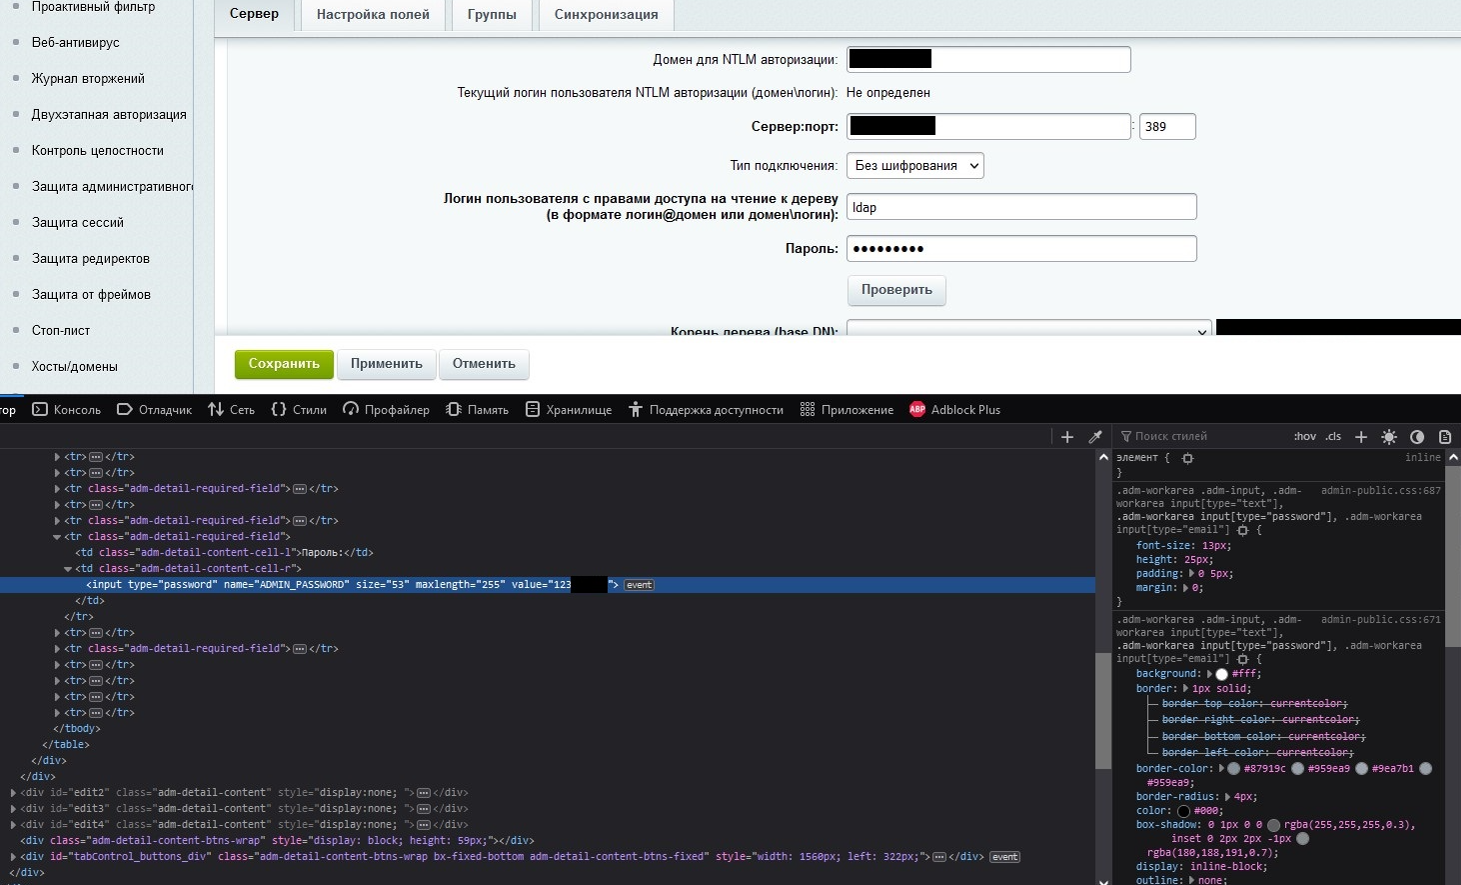 secware-ru/cve-2022-43959
Bitrix Vulnerability CVE-2022-43959
 oscerd/cve-2026-40022
Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths